

firmware
 brucedevices/firmware
Predatory ESP32 Firmware
bluetooth-securityembedded-systems-securityexploitation+9
brucedevices/firmwarePredatory ESP32 Firmware
 jenish-sojitra/jsanalyzer
Burp Suite extension for JavaScript static analysis: extracts API endpoints, URLs, secrets, and emails with noise filtering for web security testing.
 0xdevrel/easyscan
Python-based web security scanner that analyzes HTTP headers, SSL/TLS, DNS records, and common misconfigurations to generate a scored security report…
 zilbonn/owasp-wstg-rag
OWASP Web Security Testing Guide RAG system with ChromaDB, MCP for Claude Code
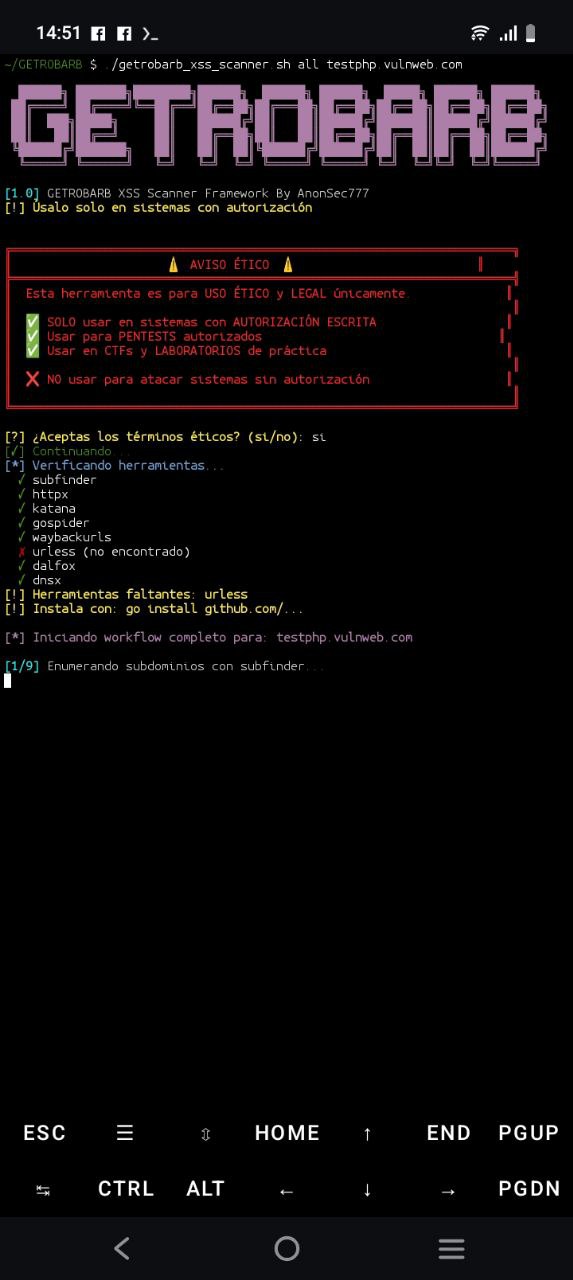 hackingteamoficial/getrobarb
Automated reconnaissance and XSS detection framework integrating subfinder, httpx, katana, gospider, waybackurls, and dalfox into a 9-stage pipeline…
 mitsu-bis/security-portfolio
Security portfolio of original responsible-disclosure findings, CTF and lab write-ups, methodology notes, and purpose-built pentest tooling covering…
 foxvr-sudo/bugbounty-arsenal-resources
Checklists and templates for bug bounty programs. MIT licensed.
 roycampos/cve-2025-29927
CVE-2025-29927 Exploit Checker
 shenril/sitadel
Web Application Security Scanner
 foxvr-sudo/bug-bounty-arsenal-v.3
Full-stack platform for authorized web application security scanning with a detector-based engine, async Celery workers, and a React dashboard for…
 taksec/google-dorks-bug-bounty
A list of Google Dorks for Bug Bounty, Web Application Security, and Pentesting
 spinkham/skipfish
Web application security scanner created by lcamtuf for google - Unofficial Mirror
 yunemse48/403bypasser
Automates HTTP 403 access control bypass techniques using header manipulation, path obfuscation, and HTTP method conversion for web application…
 zigoo0/webpwn3r
WebPwn3r - Web Applications Security Scanner.
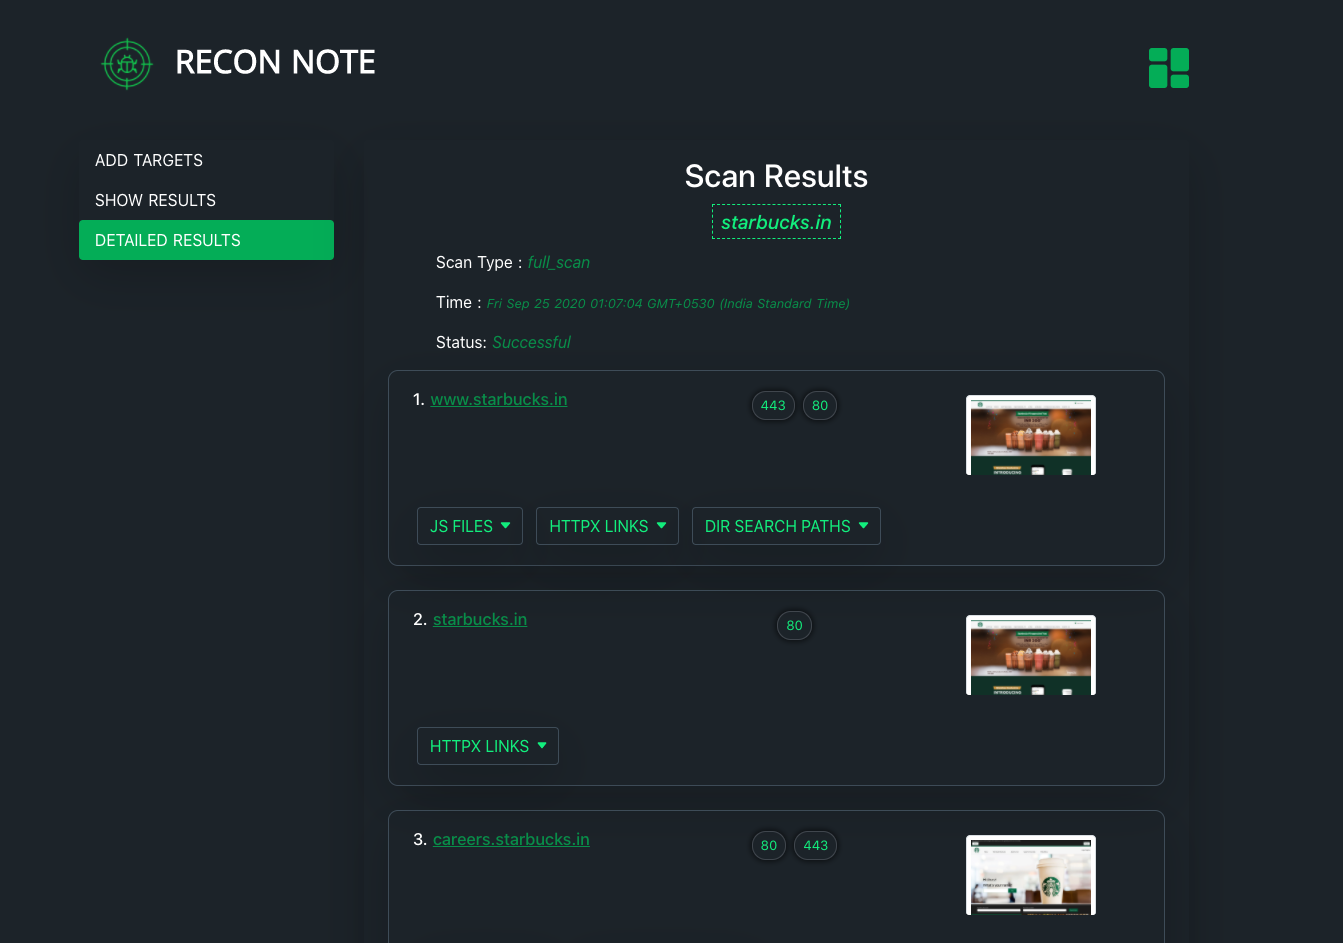 0xdekster/reconnote
Web Application Security Automation Framework which recons the target for various assets to maximize the attack surface for security professionals &…
 yalcinyolalan/wssat
WEB SERVICE SECURITY ASSESSMENT TOOL
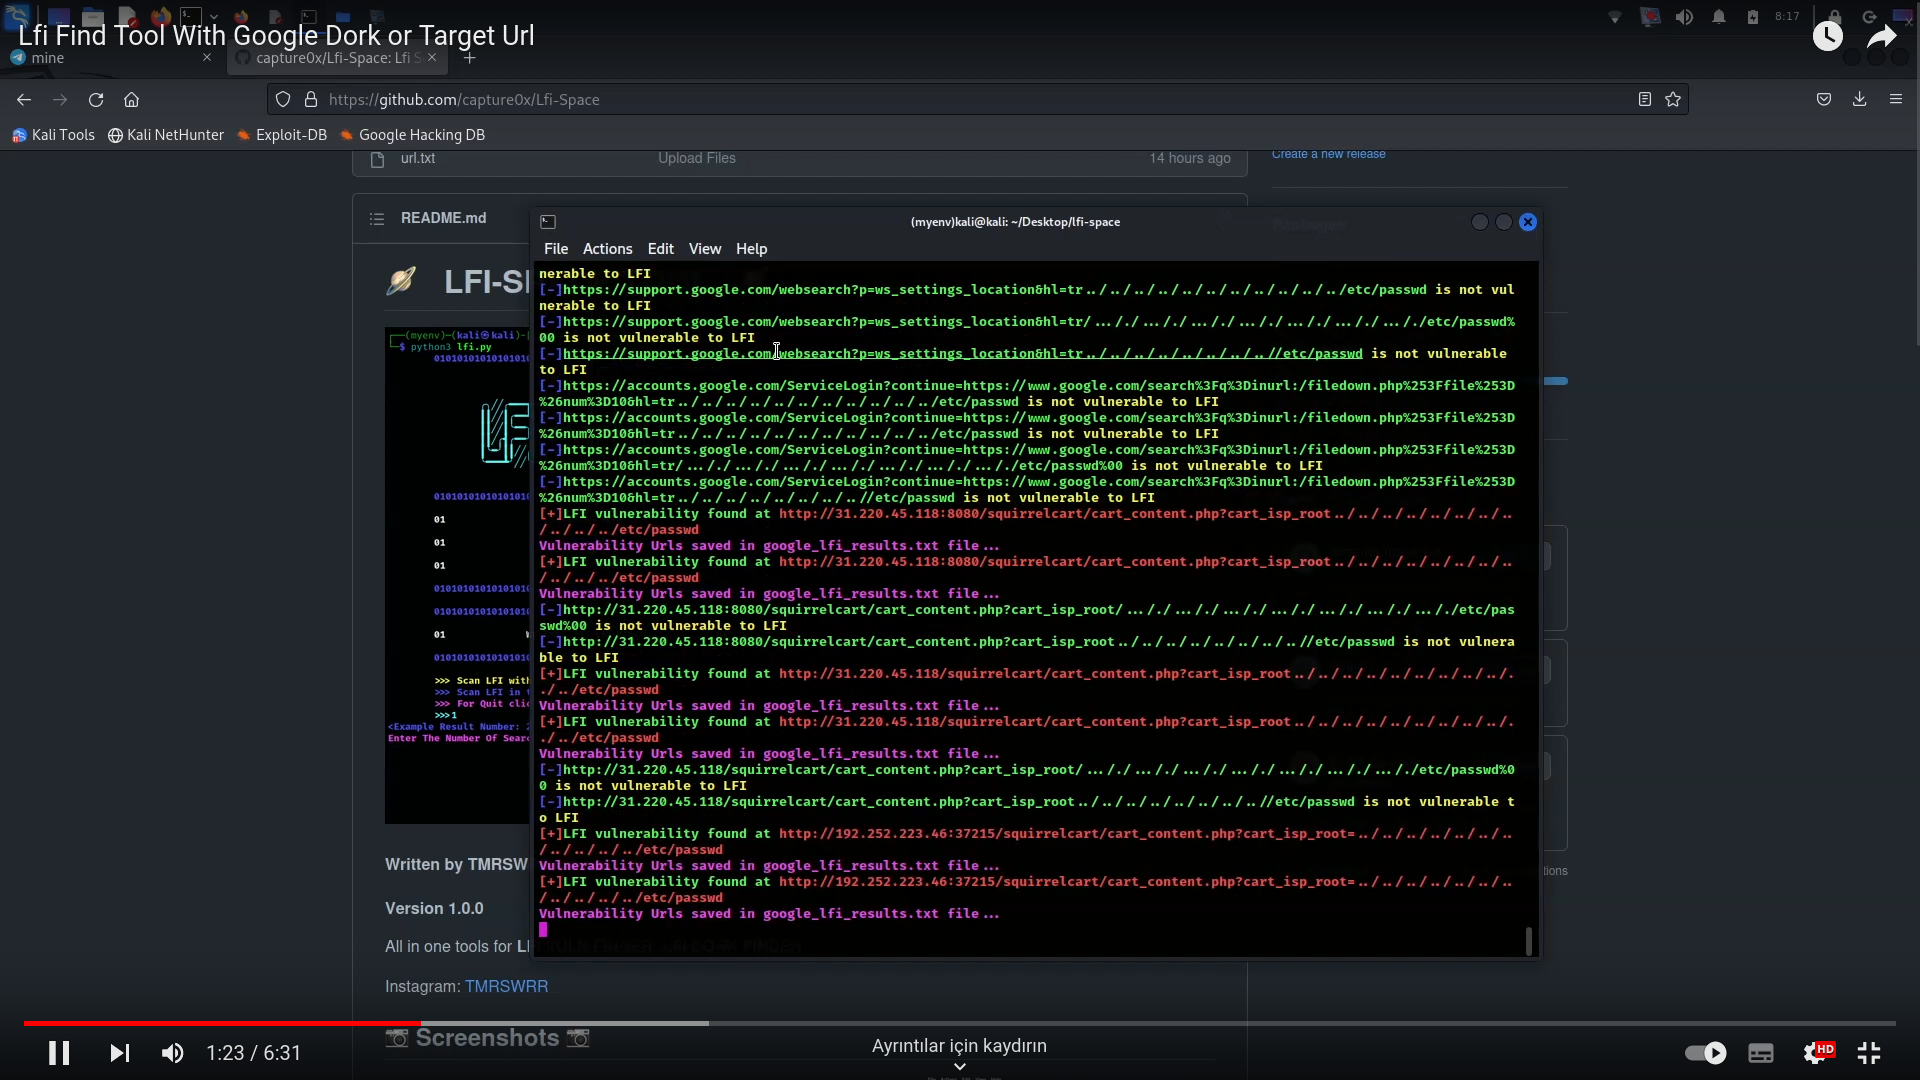 capture0x/lfi-space
Automated Local File Inclusion (LFI) vulnerability scanner with Google Dork search and targeted URL scan modes for web application security testing.
 matank001/moxy
Moxy is an open-source DAST tool designed for modern web application security testing. It provides an easy-to-use interface with agentic capabilities…