
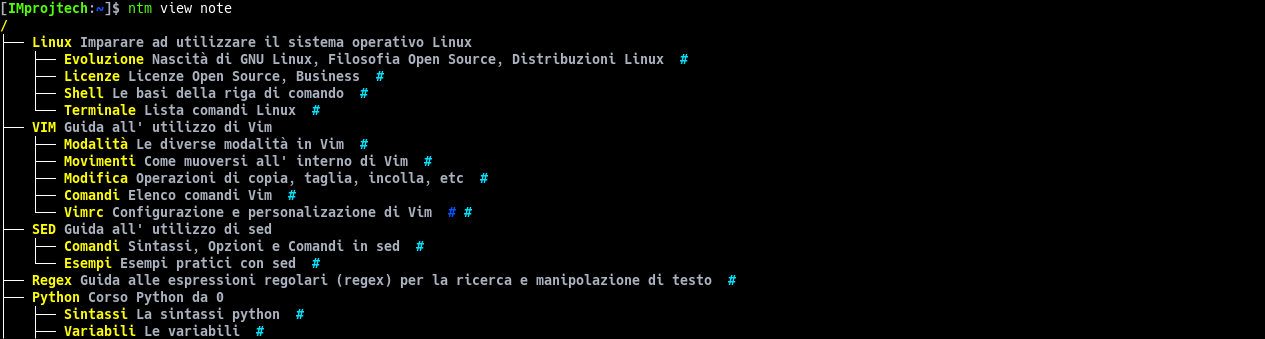
NotaMy
 improjtech/notamy
Terminal-based note manager with hierarchical tagging and file linking
educationinformation-gatheringpenetration-testing+3
improjtech/notamyTerminal-based note manager with hierarchical tagging and file linking
 lautarovculic/frida-ipa-extract
Robust Frida-based tool to dump decrypted iOS apps as .ipa from a jailbroken device supports App Store, sideloaded and system.
 0xdsm/apepe
Extracts app settings, permissions, deeplinks, and SSL pinning bypass suggestions from Android APK files via static analysis of AndroidManifest.xml,…
 projectdiscovery/httpx
Fast, multi-probe HTTP toolkit for reconnaissance and information gathering. Probes TLS, CSP, headers, tech stack, and CDN. Supports matchers,…
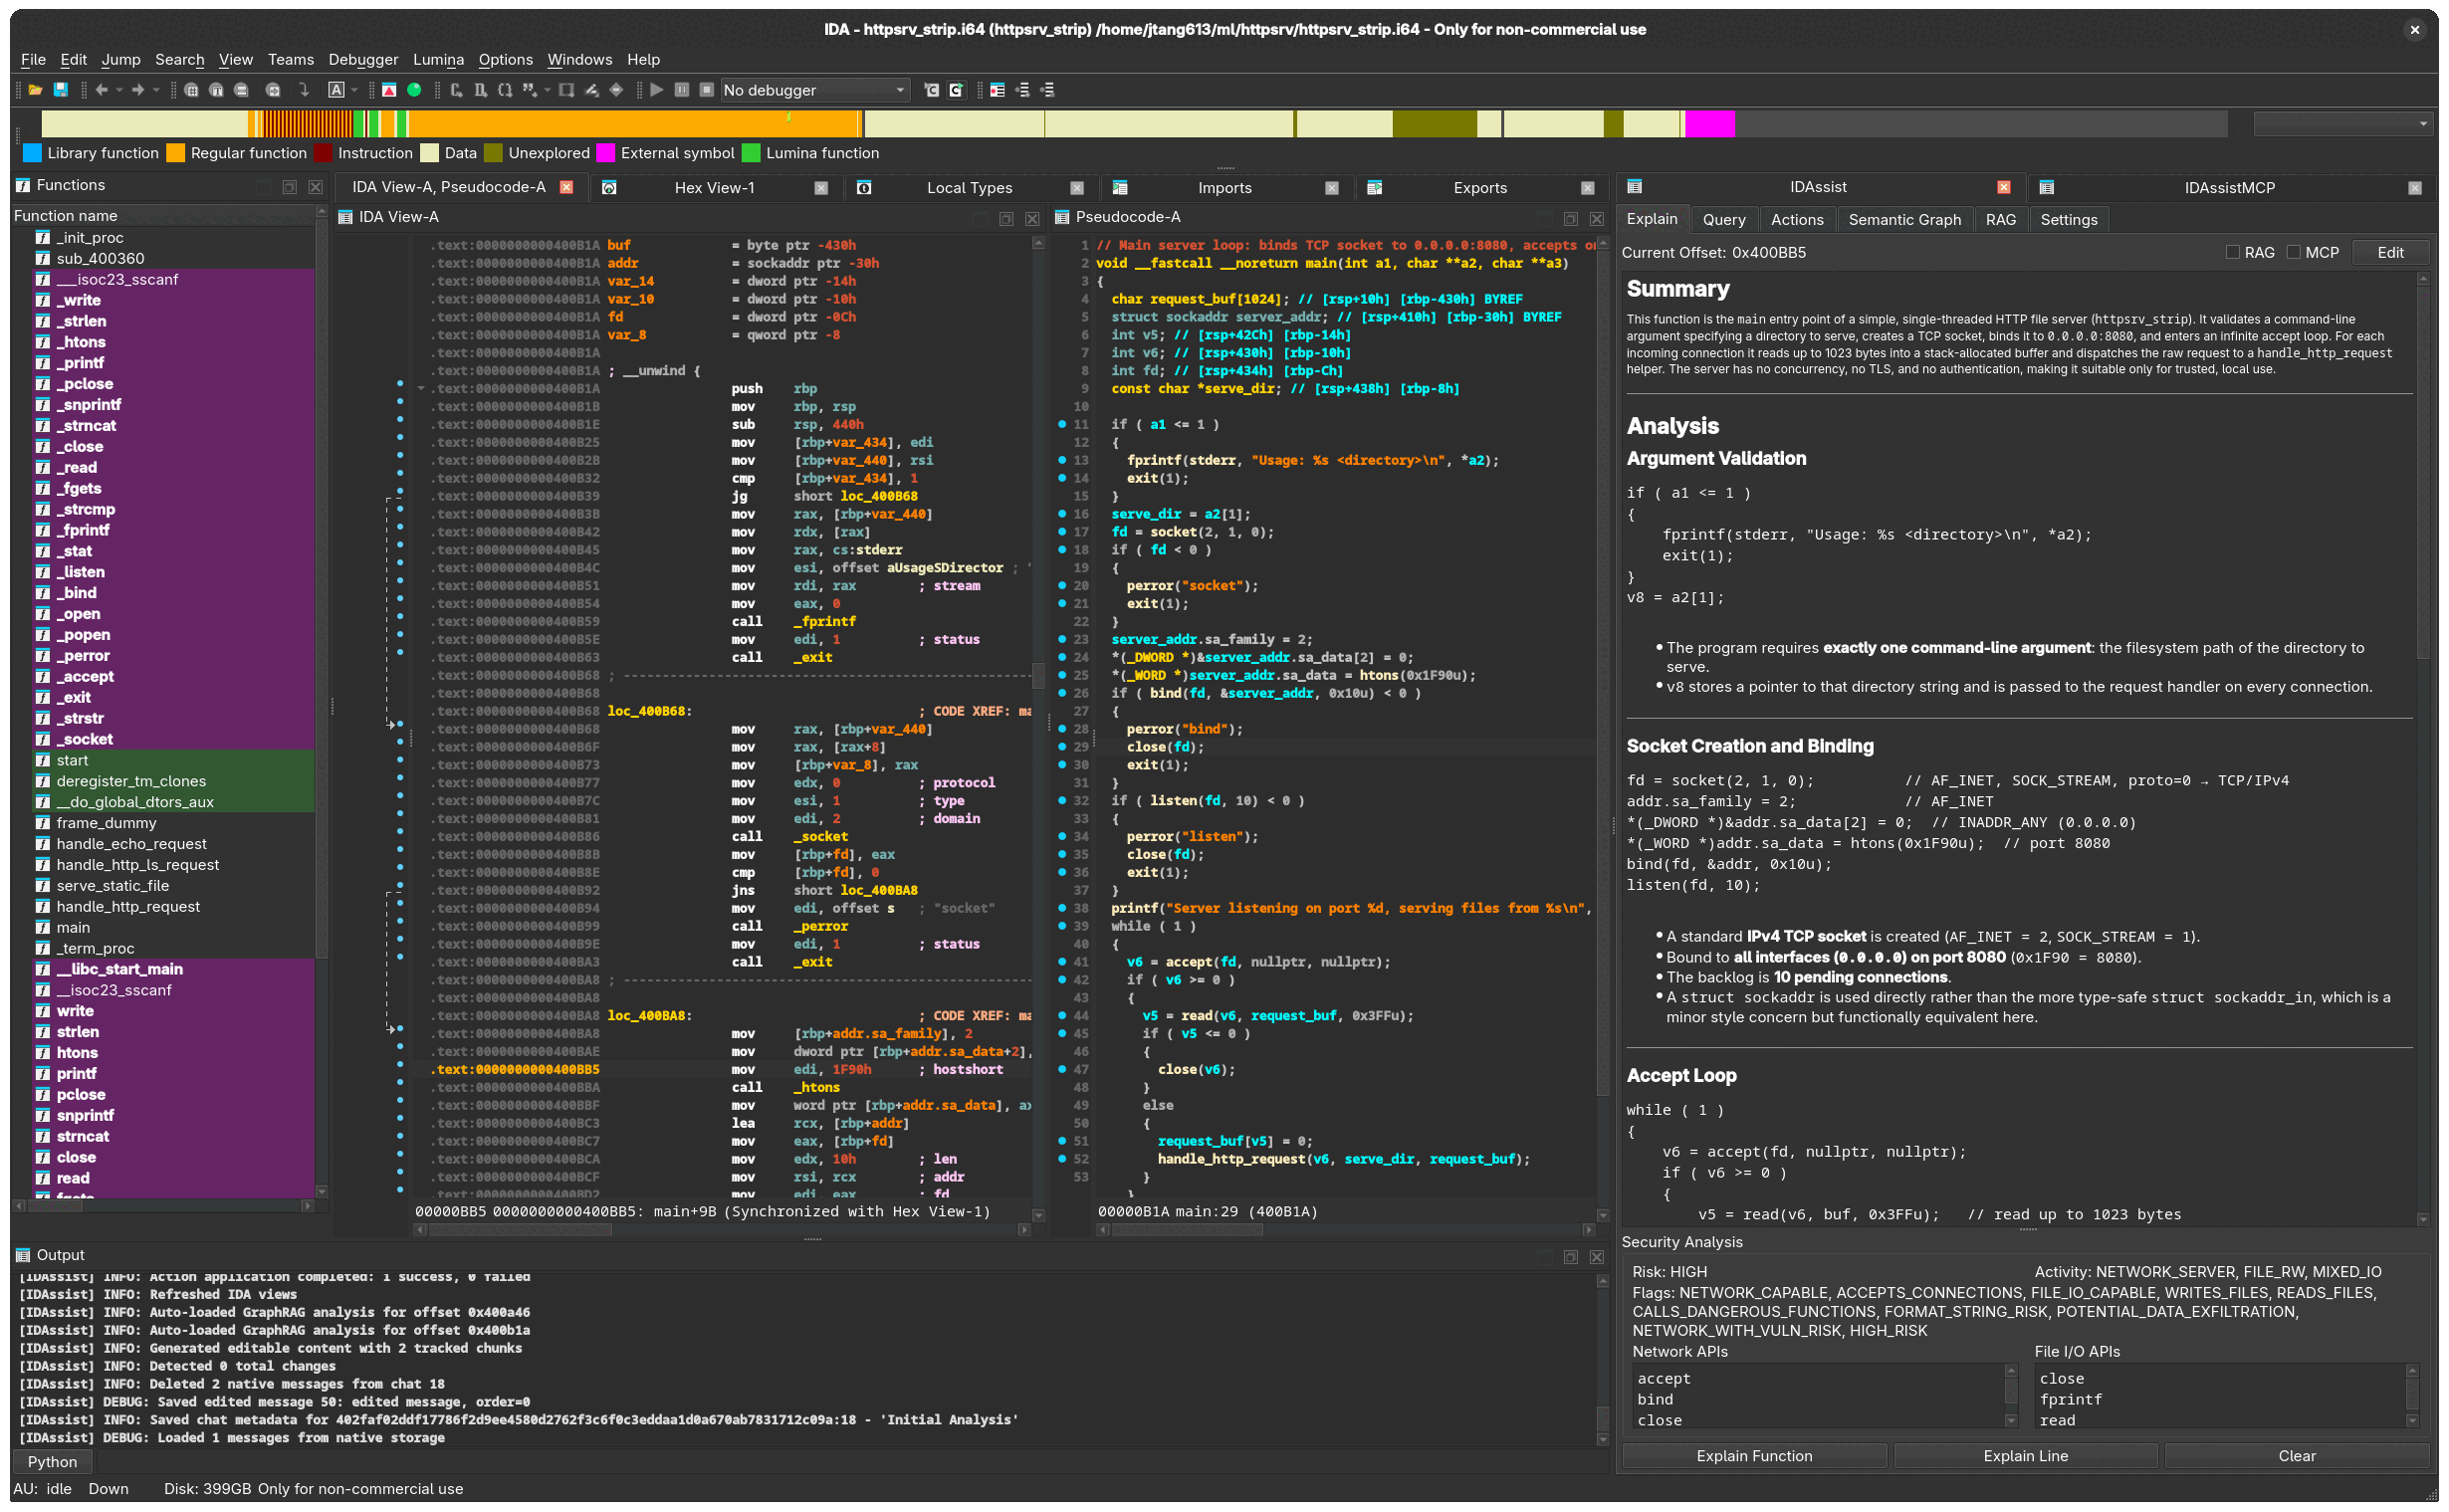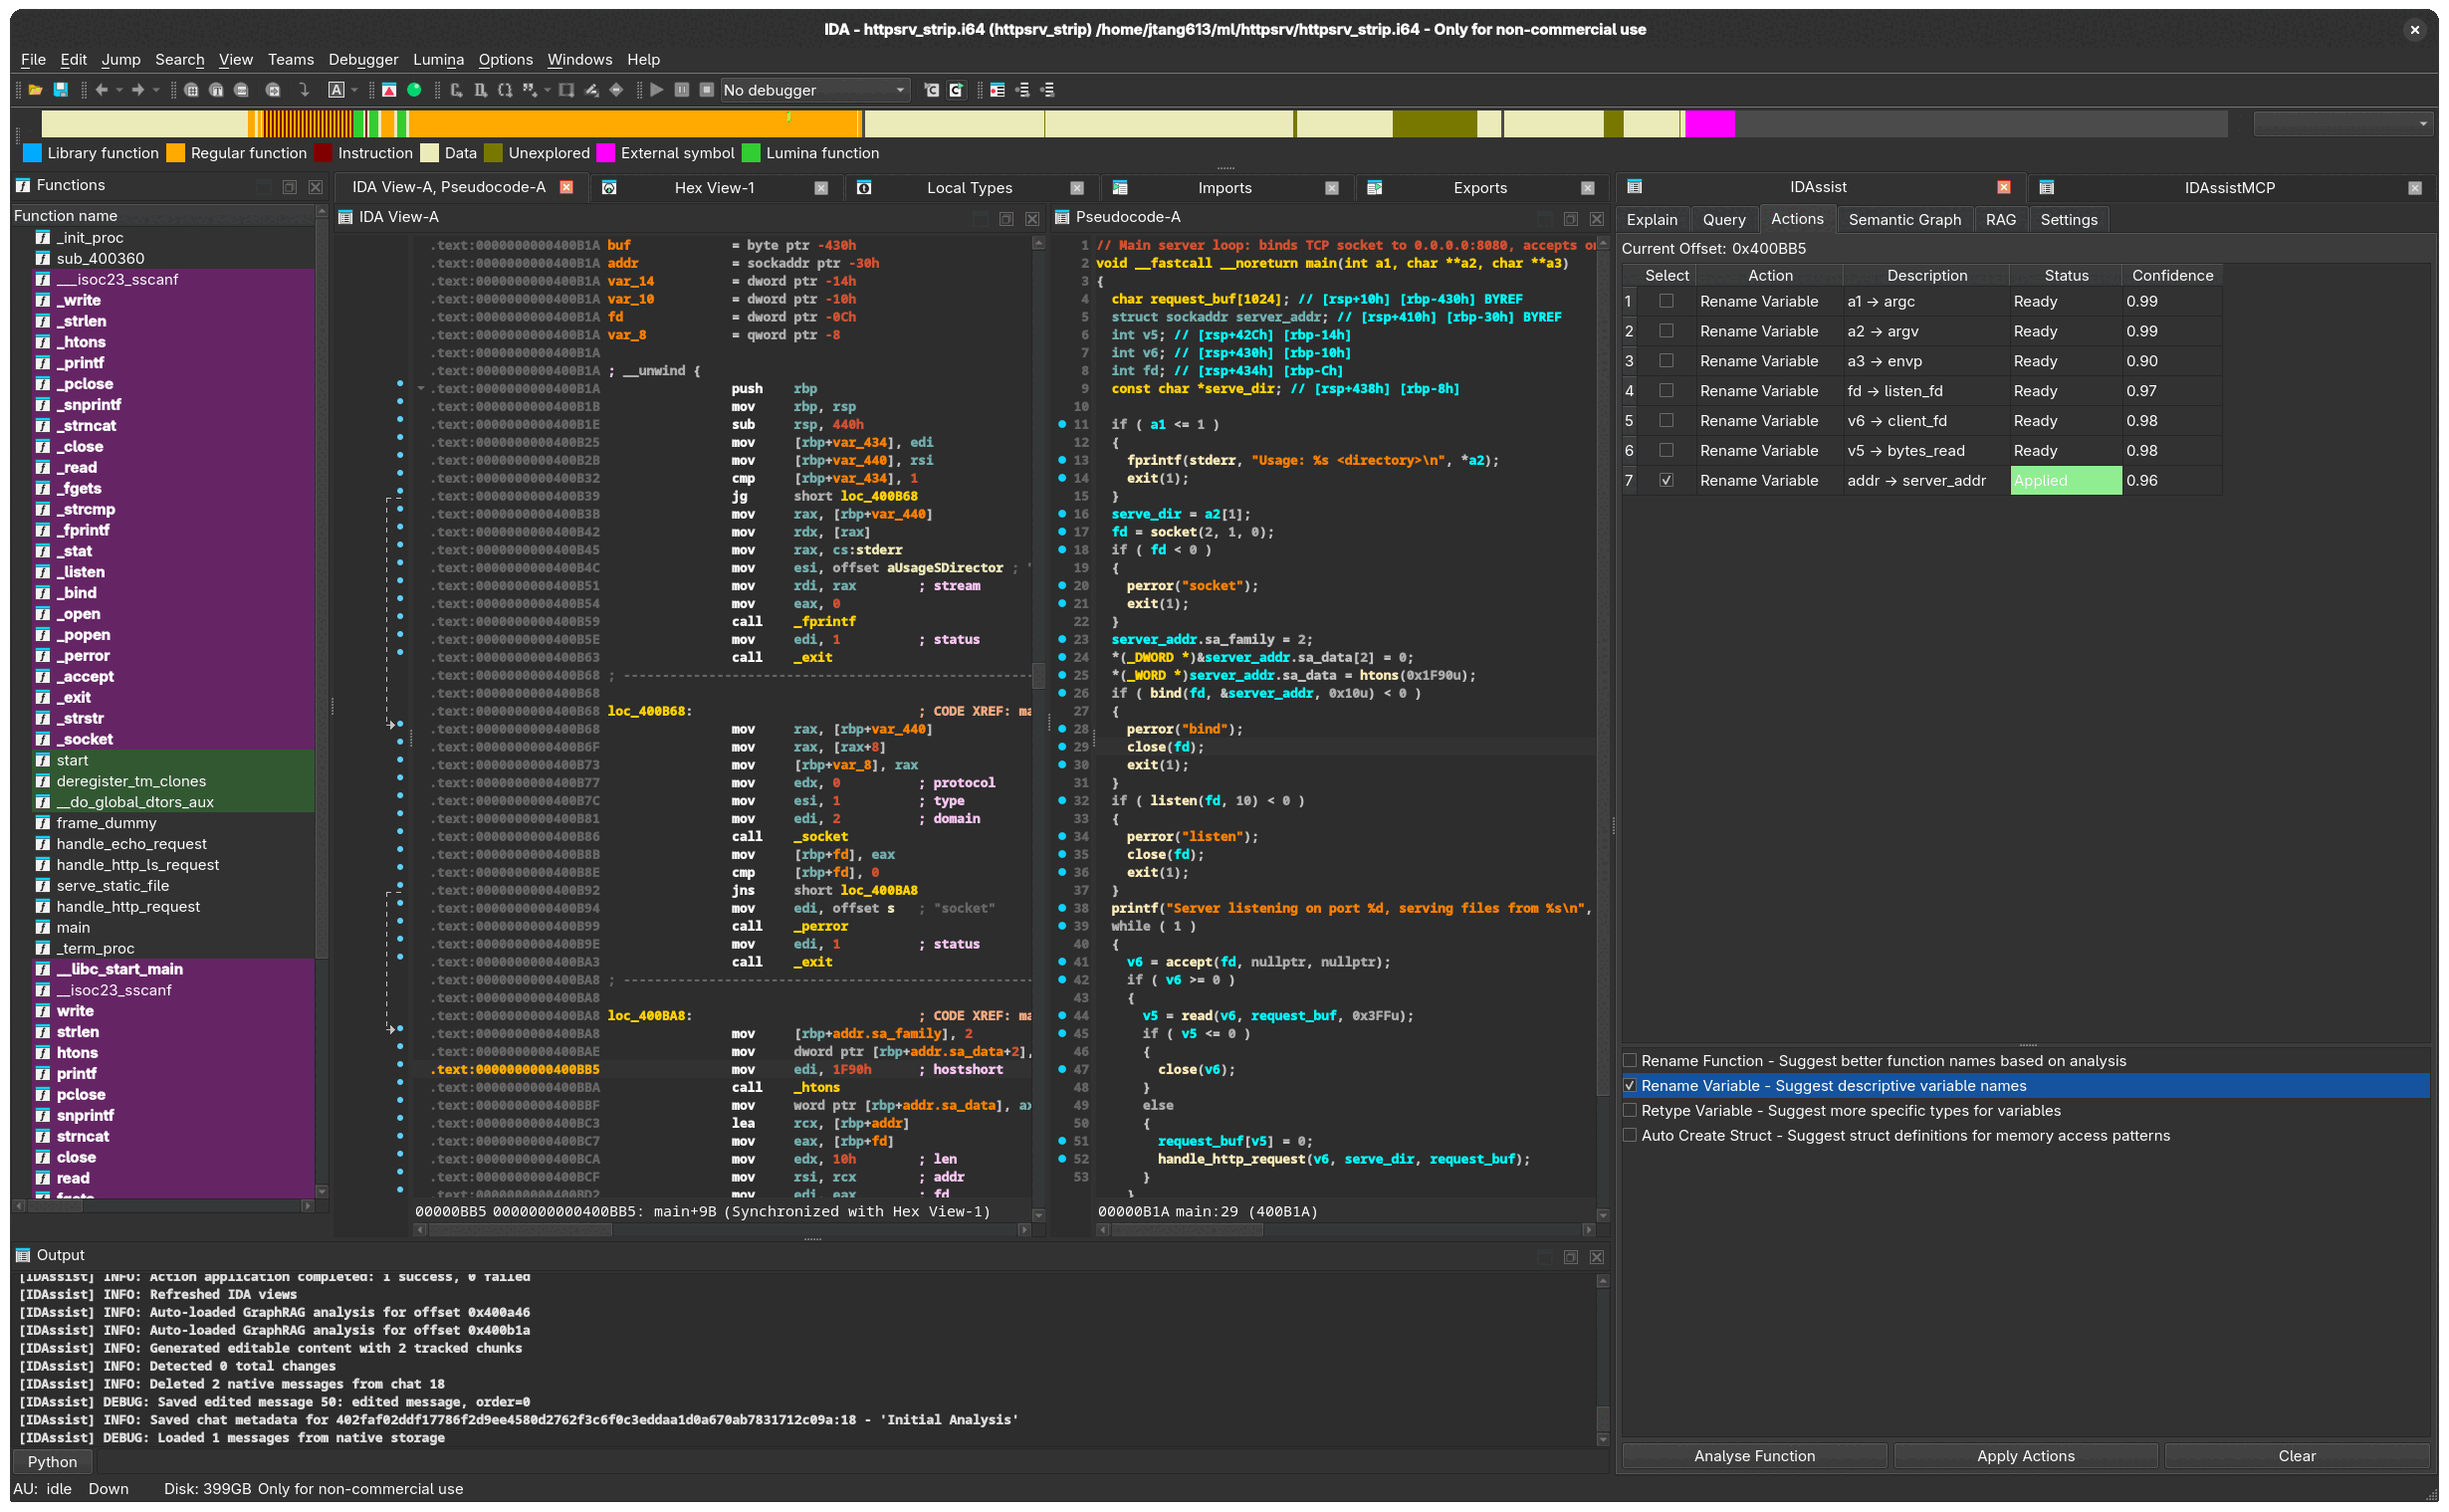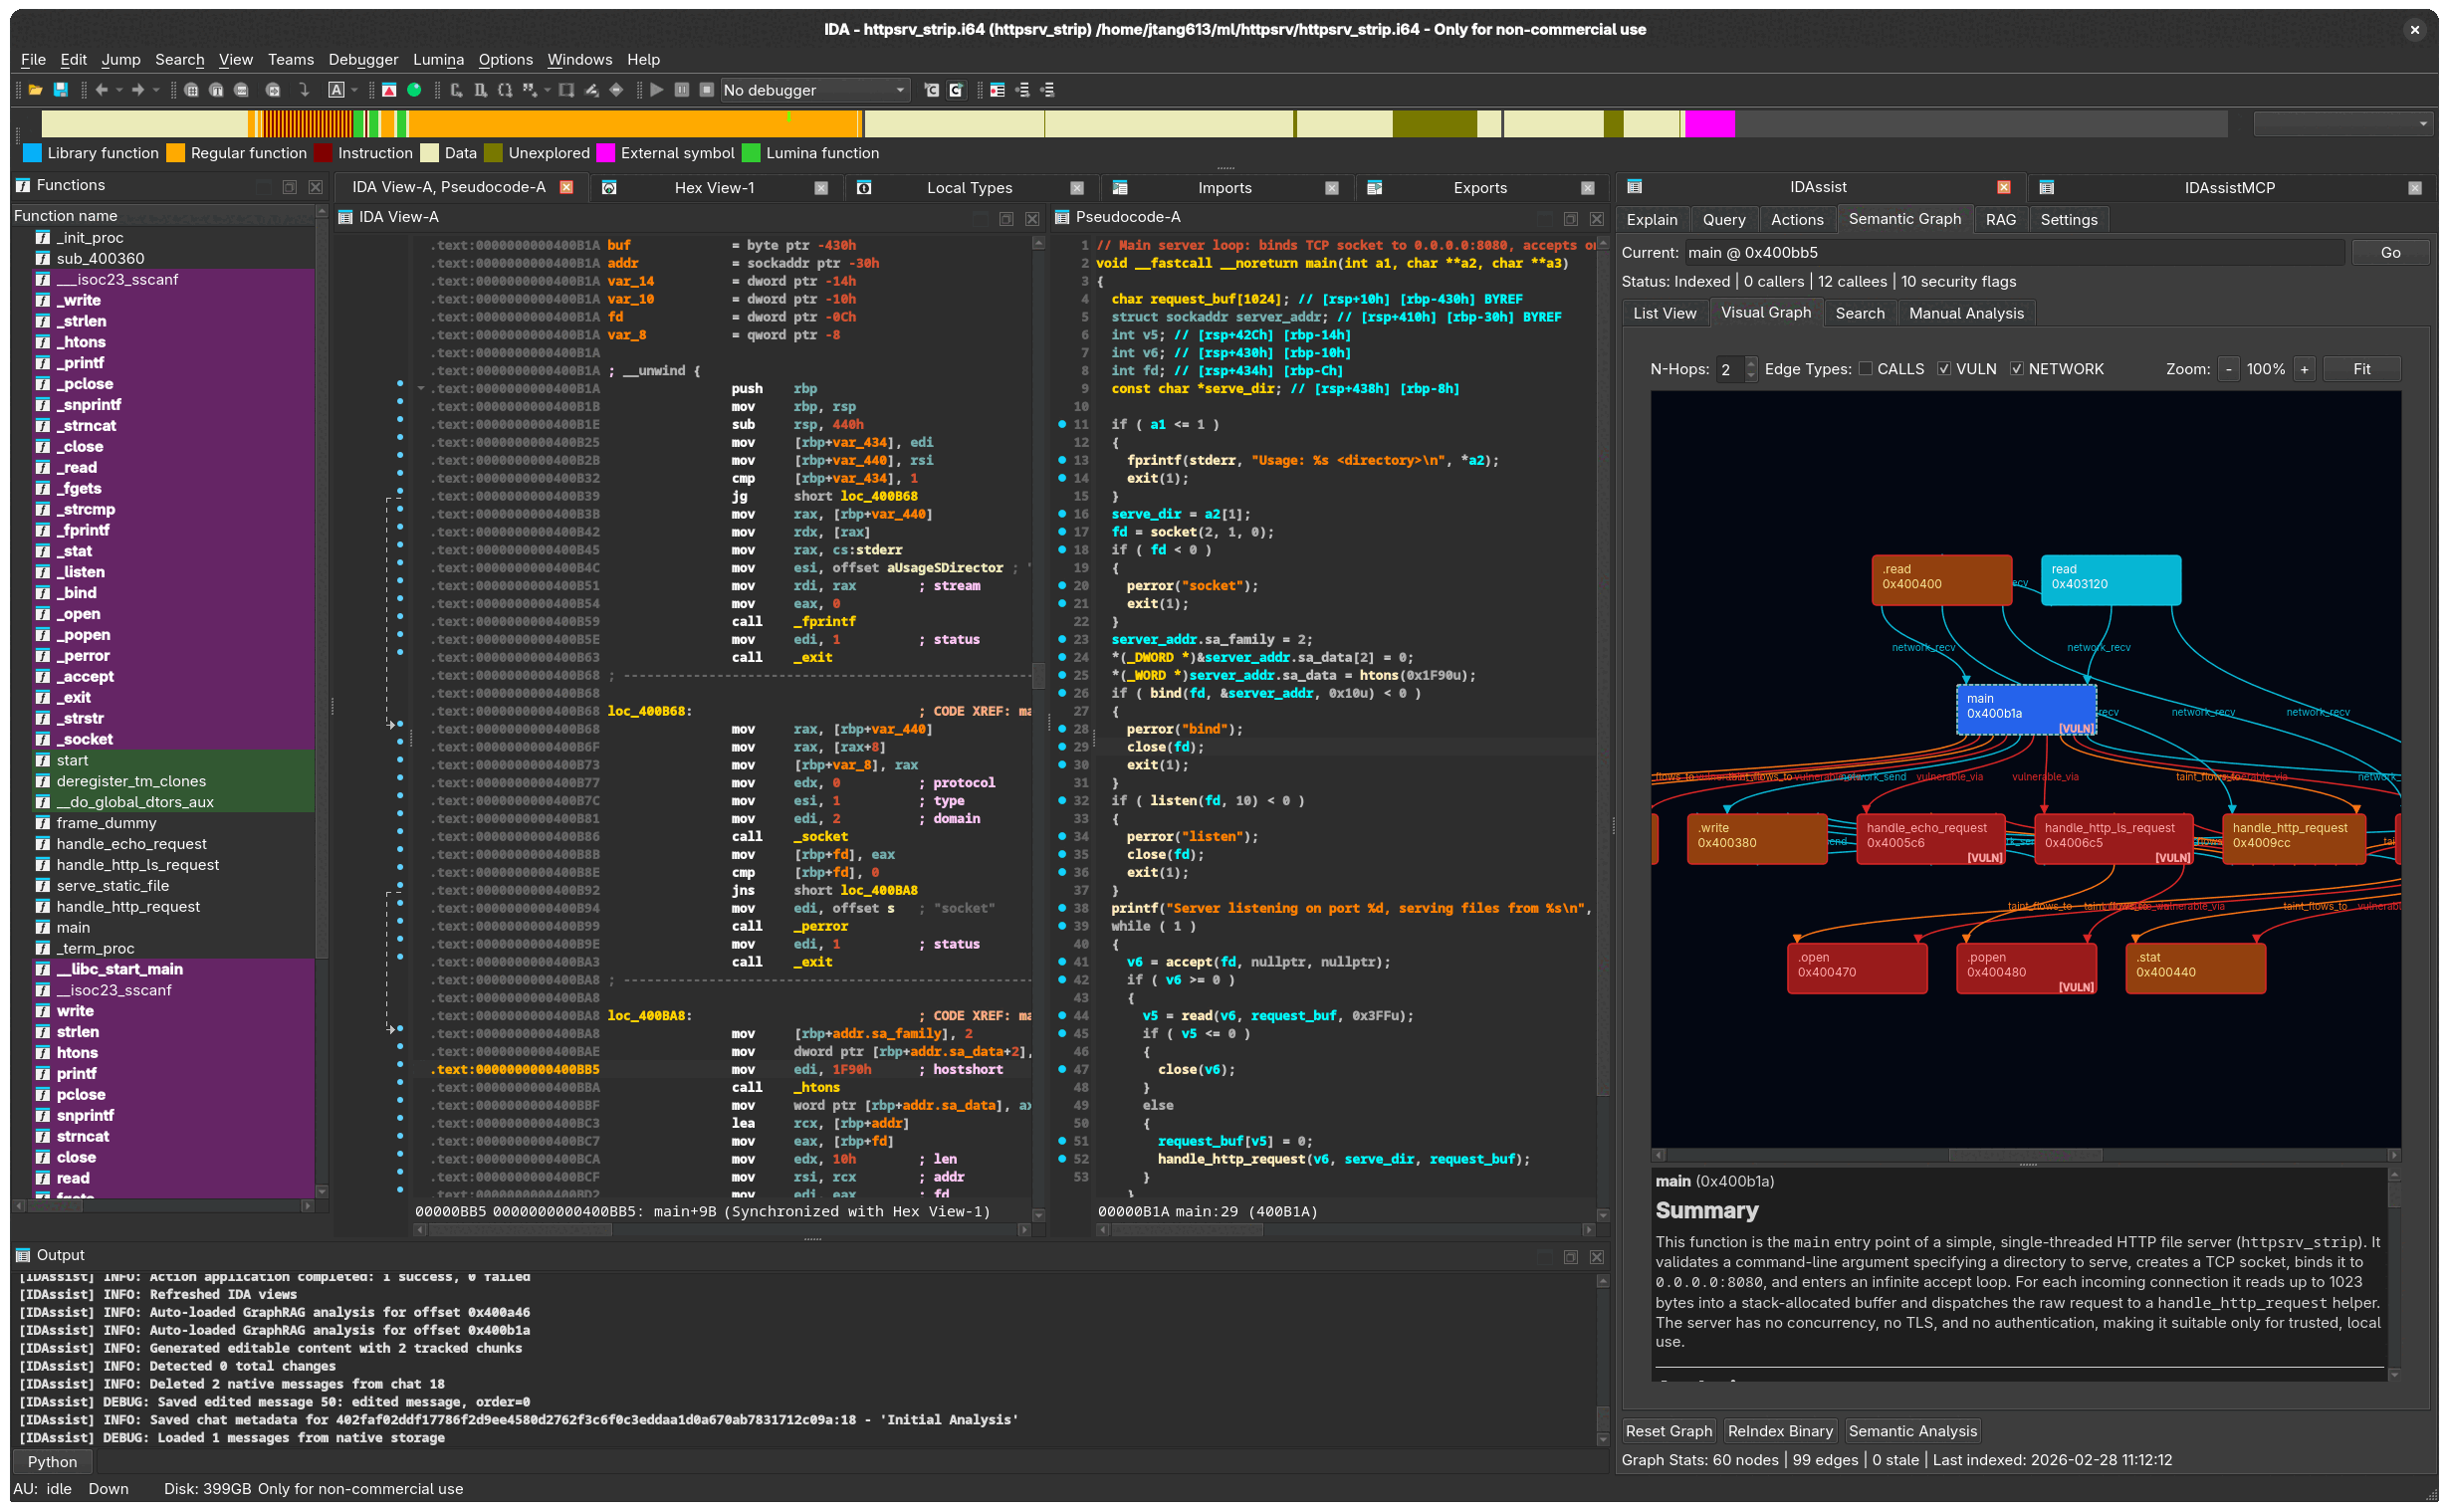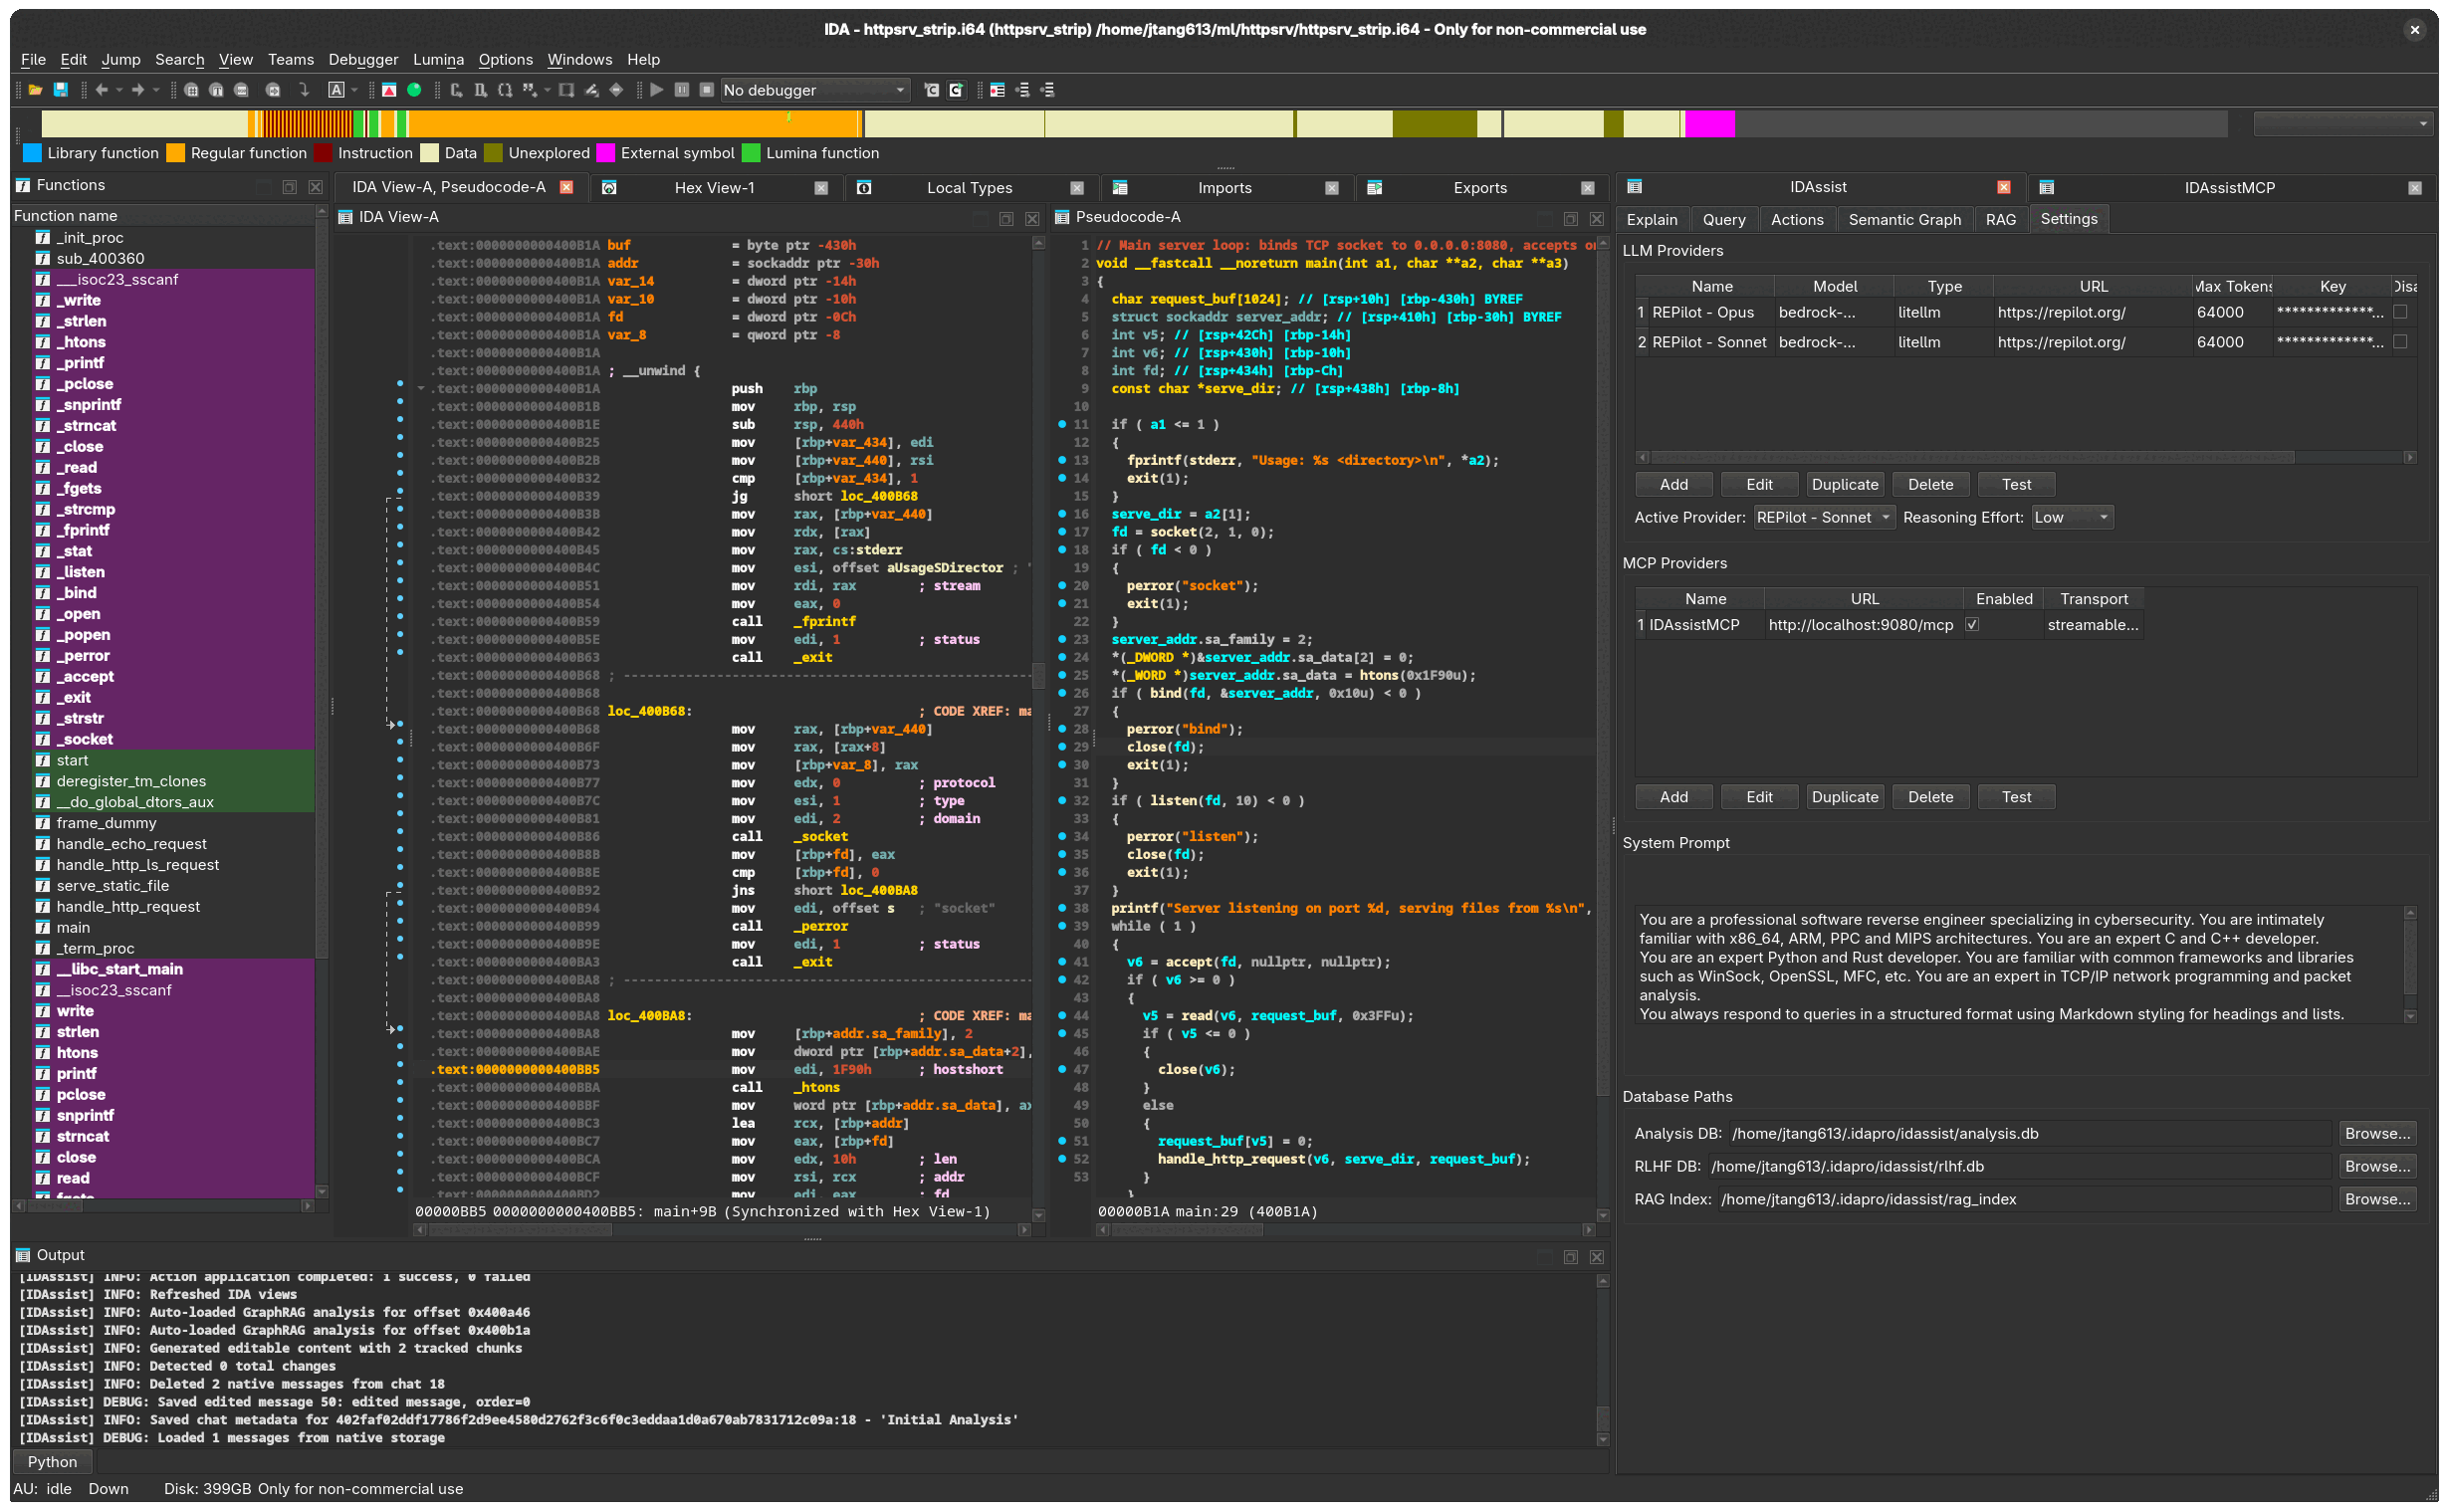 symgraph/idassist
AI-Powered Reverse Engineering Plugin for IDA Pro
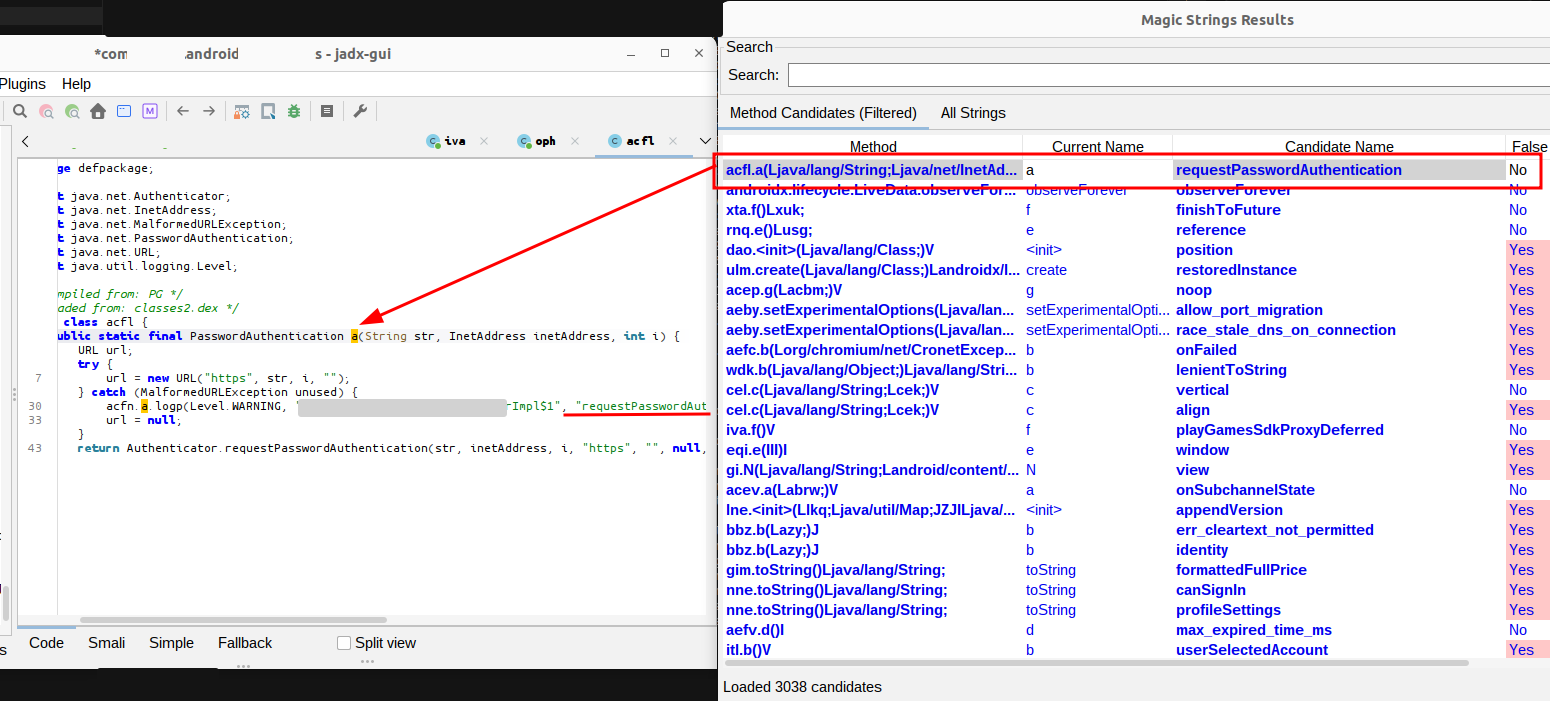 0rshemesh/jadx-magic-strings
JADX plugin that extracts method names, class references, and source file paths from string constants found in DEX files and decompiled Android code.

 majd/ipatool
Command-line tool that allows you to search for iOS, iPadOS, tvOS, visionOS, and macOS apps on the App Store, and download .ipa or macOS .pkg app…
 ravss/bluetooth-crash-cve-2017-0785
Exploit script for CVE-2017-0785 that crashes the Bluetooth module on Android 4.0+ devices by sending crafted SDP search requests, causing…
 0x1ca3/adbnet
A tool that allows you to search for vulnerable android devices across the world and exploit them.
 dwisiswant0/findom-xss
A fast DOM based XSS vulnerability scanner with simplicity.
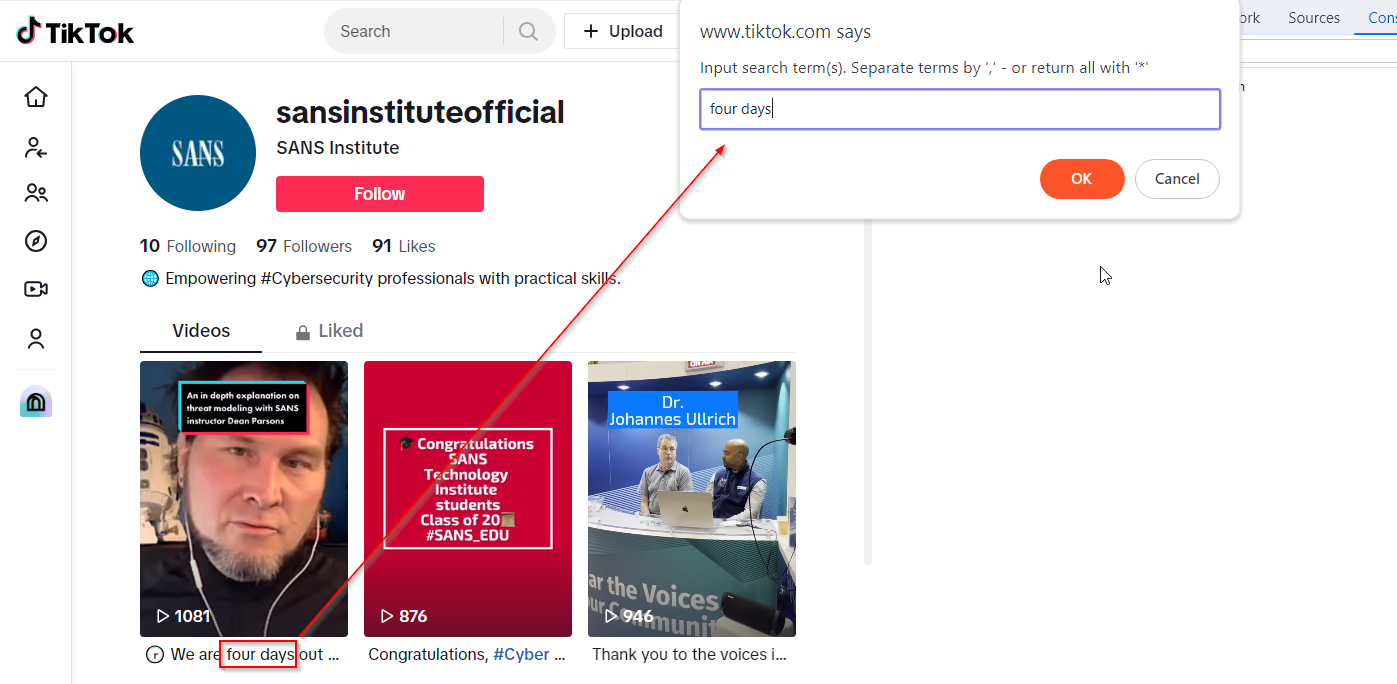 janhalendk/react
A OSINT project that explores how to dump data from React
 gonzosint/gvision
Reverse image search tool using Google Cloud Vision API to detect landmarks, web entities, and geolocation data from images for OSINT investigations.
 blackfan/bfscan
Tool for finding URLs, paths, secrets and generating raw HTTP requests and OpenApi specifications from config files and annotations used in JAR / WAR…

 epi052/feroxbuster
A fast, simple, recursive content discovery tool written in Rust.
 nightbringer21/fridump
Cross-platform memory dumper using Frida to extract accessible memory from iOS, Android, and Windows applications for forensic analysis and…
 frida/frida
Main repo for hosting release binaries