
CVE-2021-39165
 w0rty/cve-2021-39165
Github repository which contains a functional exploit for CVE-2021-39165
exploitationinformation-gatheringpenetration-testing+2
21
w0rty/cve-2021-39165Github repository which contains a functional exploit for CVE-2021-39165
 c0ff33b34n/cve-2021-38314
Python exploit for CVE-2021-38314 targeting unauthenticated sensitive information disclosure in WordPress Gutenberg Template Library & Redux…
 blu3ming/poc-cve-2021-41773
Python exploit for CVE-2021-41773 - Apache HTTP Server 2.4.49 Path Traversal vulnerability
 nanxsec/exploitapache
exploit para a CVE-2021-41773:Path Traversal cgi-bin
 magicrc/cve-2021-29447
PoC for CVE-2021-29447
 dorkerdevil/cve-2021-33564
Argument Injection in Dragonfly Ruby Gem exploit (backup)
 mlr0p/cve-2021-33564
Argument Injection in Dragonfly Ruby Gem
 srvaccount/cve-2021-26855-poc
PoC exploit code for CVE-2021-26855
 madexploits/laravel-debug-checker
CVE-2021-3129 Exploit Checker By ./MrMad
 chrisync/cve-scanner
CVE-2021-42287/CVE-2021-42278/OTHER Scanner & Exploiter.
 suljov/grafana-lfi-exploit
Updated exploit script for the CVE-2021-43798
 horizon3ai/proxyshell
Proof of Concept for CVE-2021-34473, CVE-2021-34523, and CVE-2021-31207
 tea-on/cve-2021-29447-authenticated-xxe-wordpress-5.6-5.7
POC to exploit WordPress 5.6-5.7 (PHP 8+) Authenticated XXE Injection.
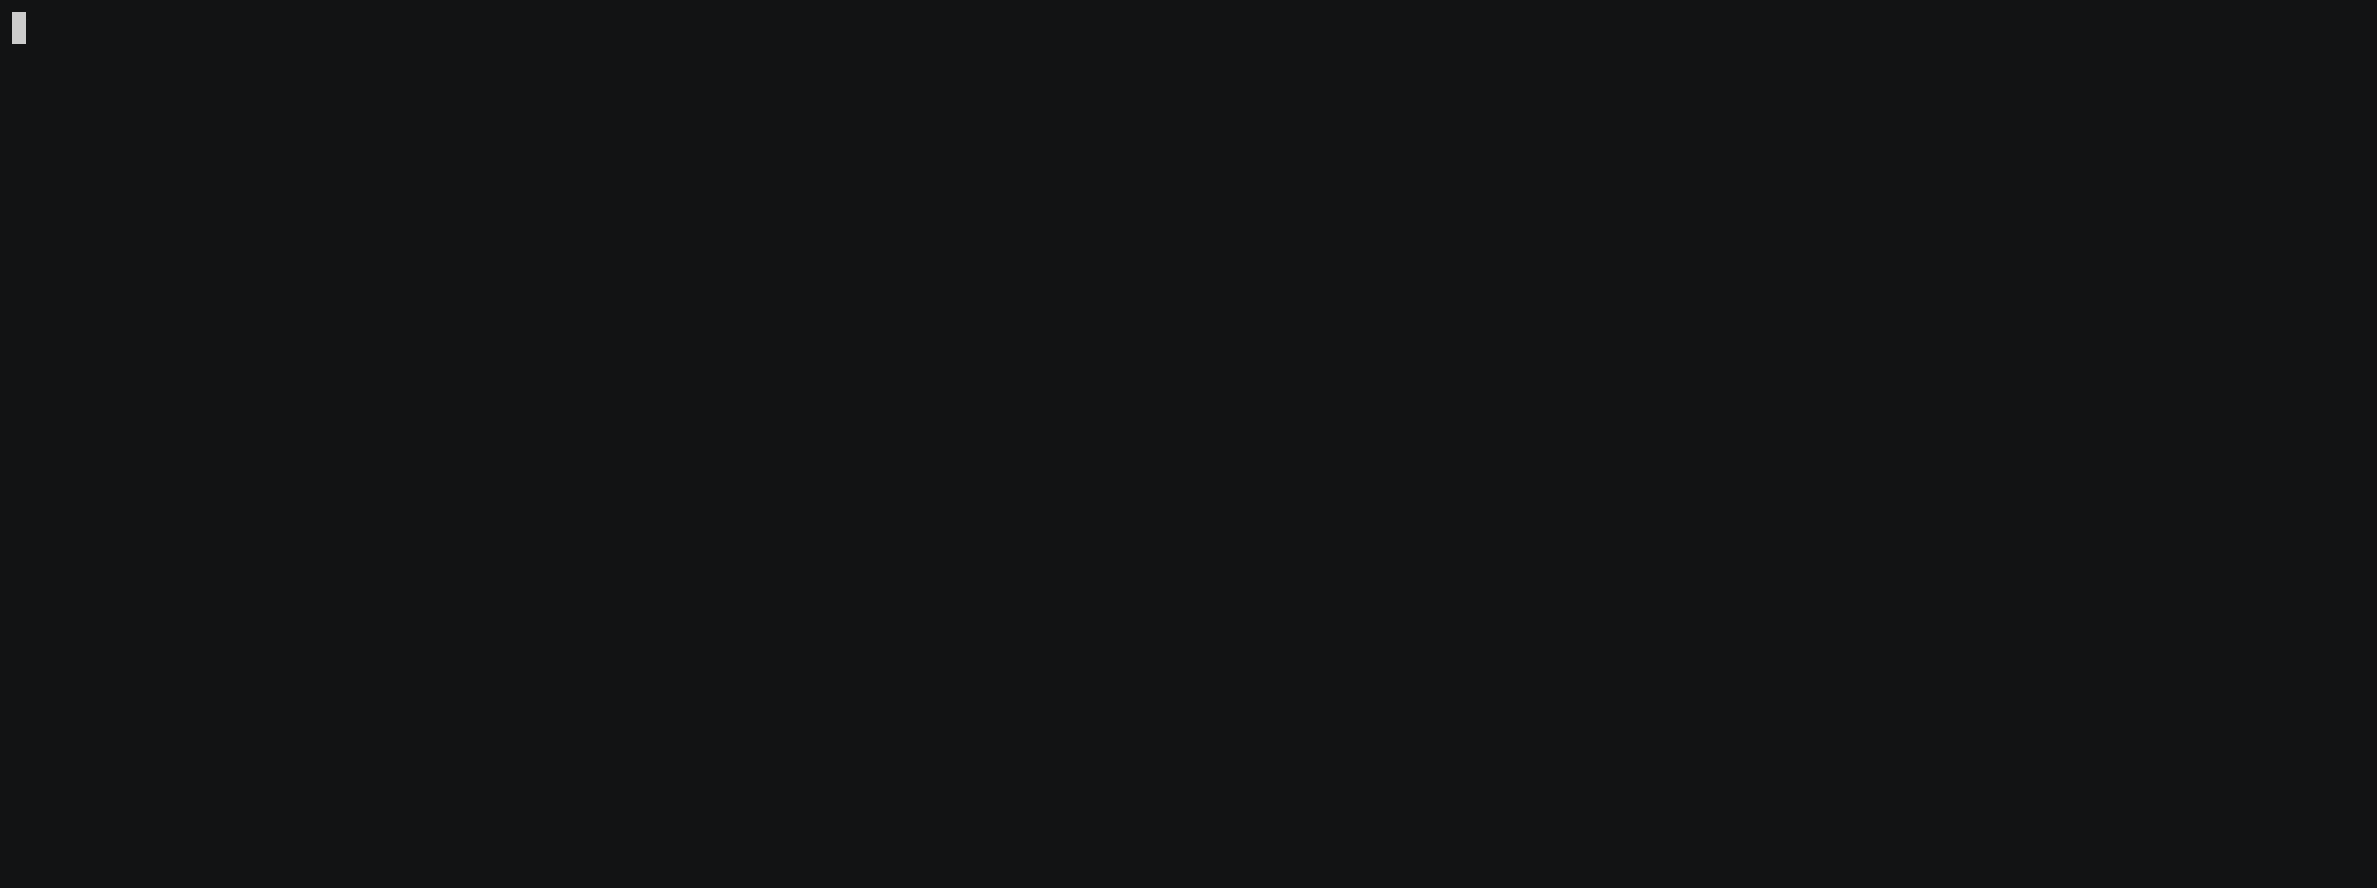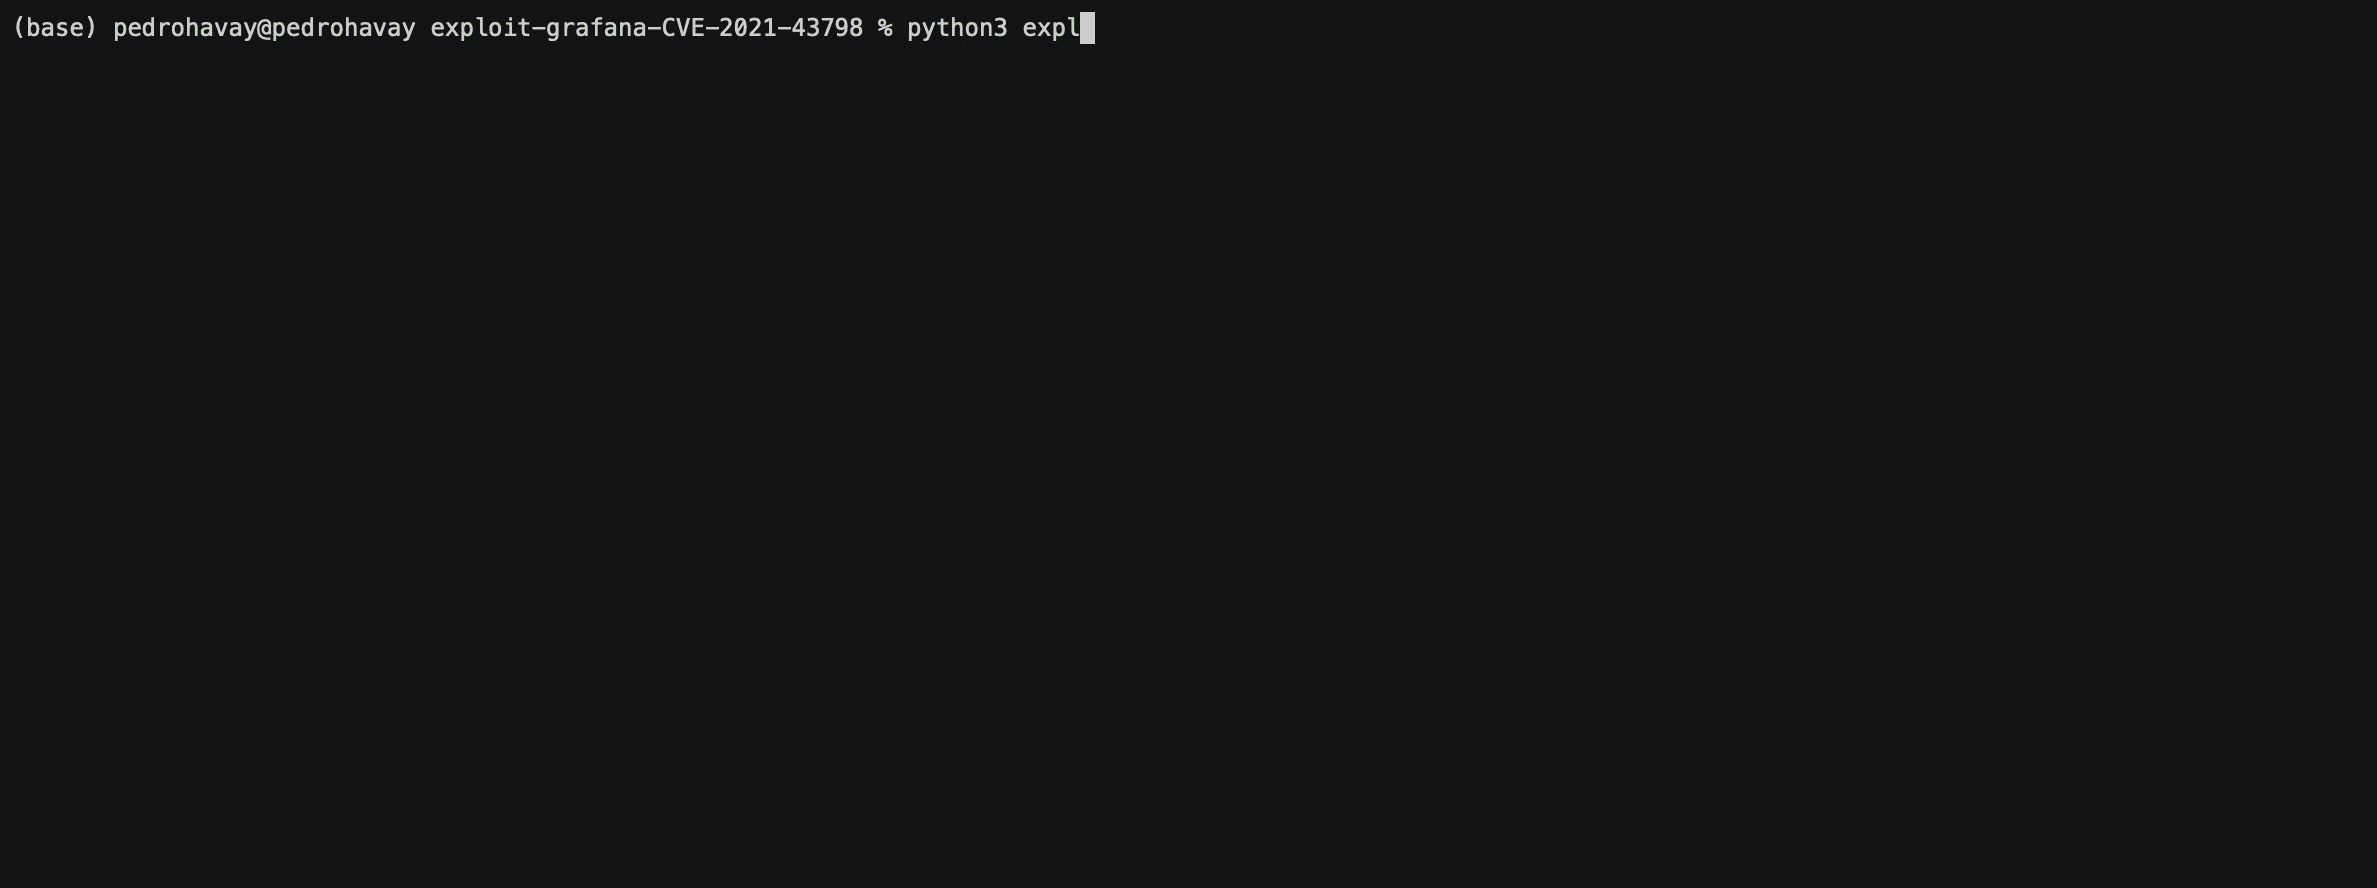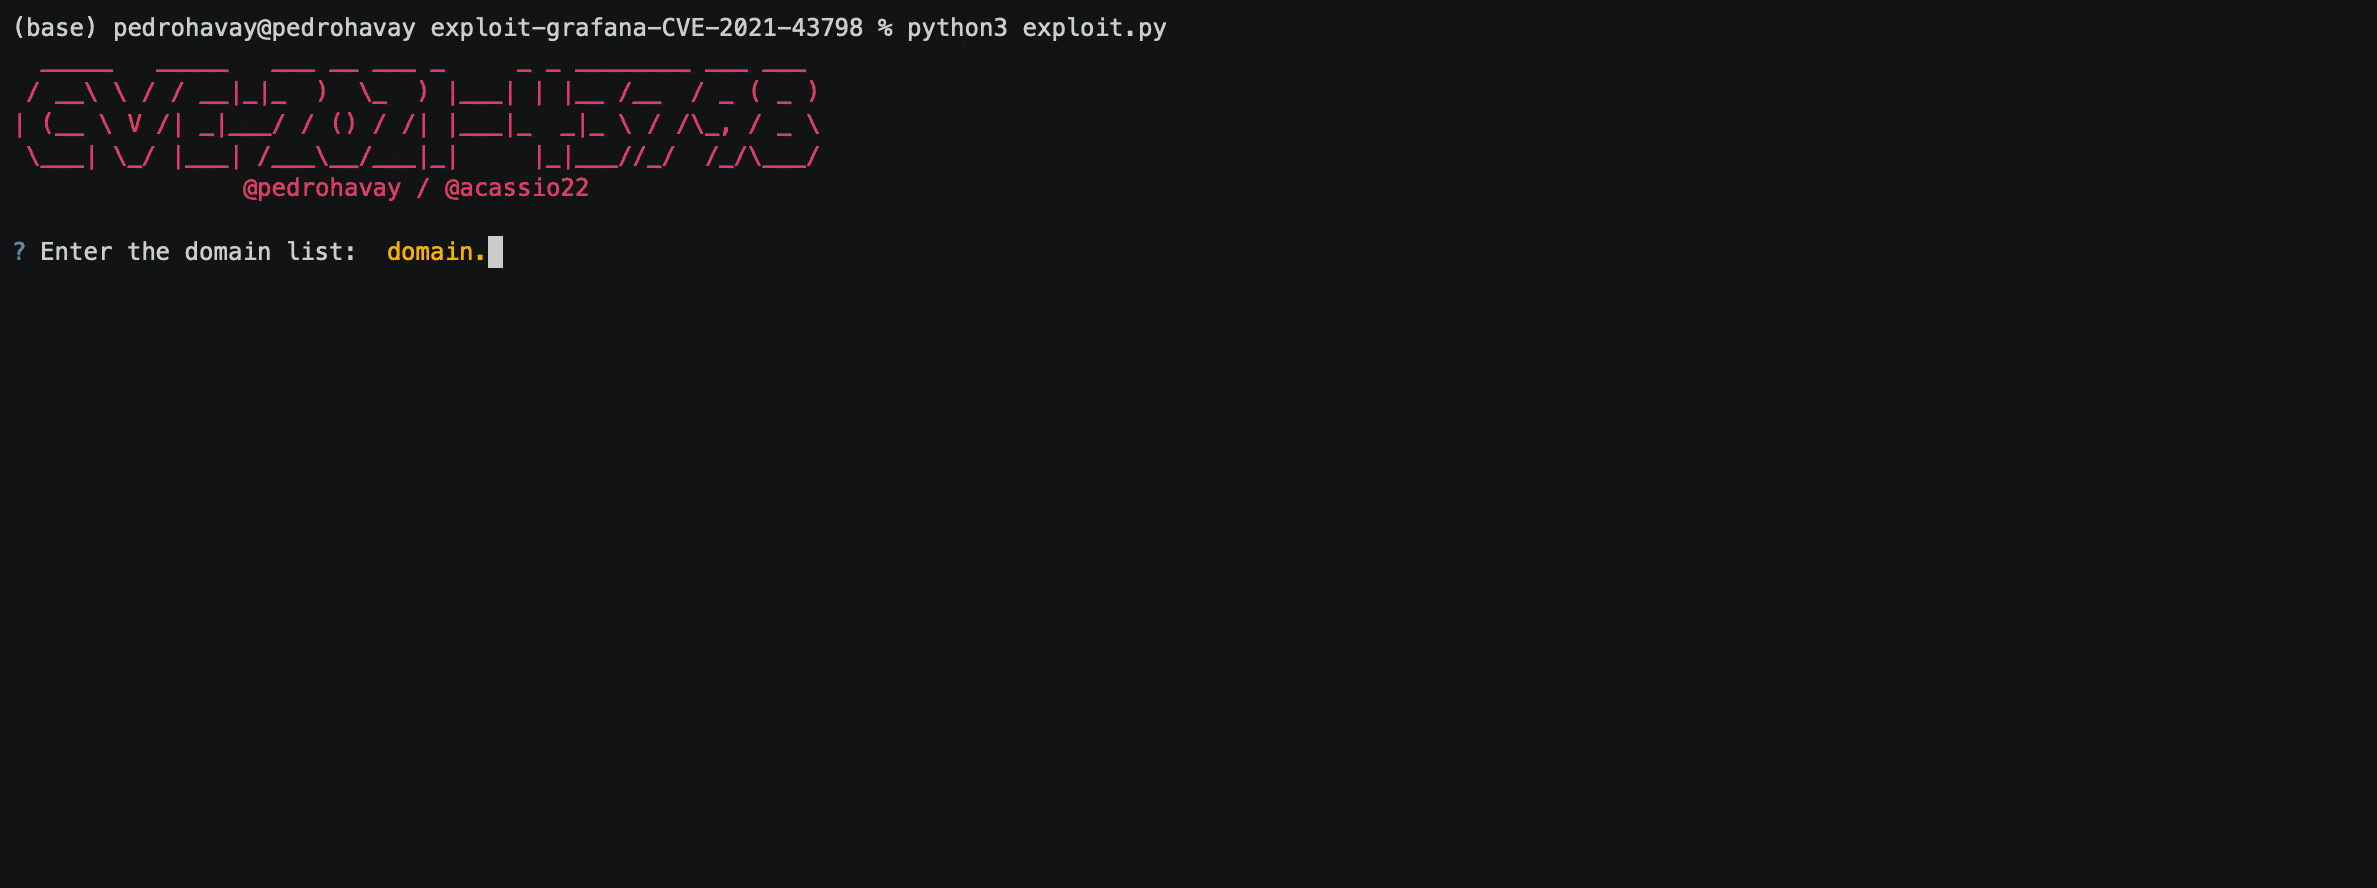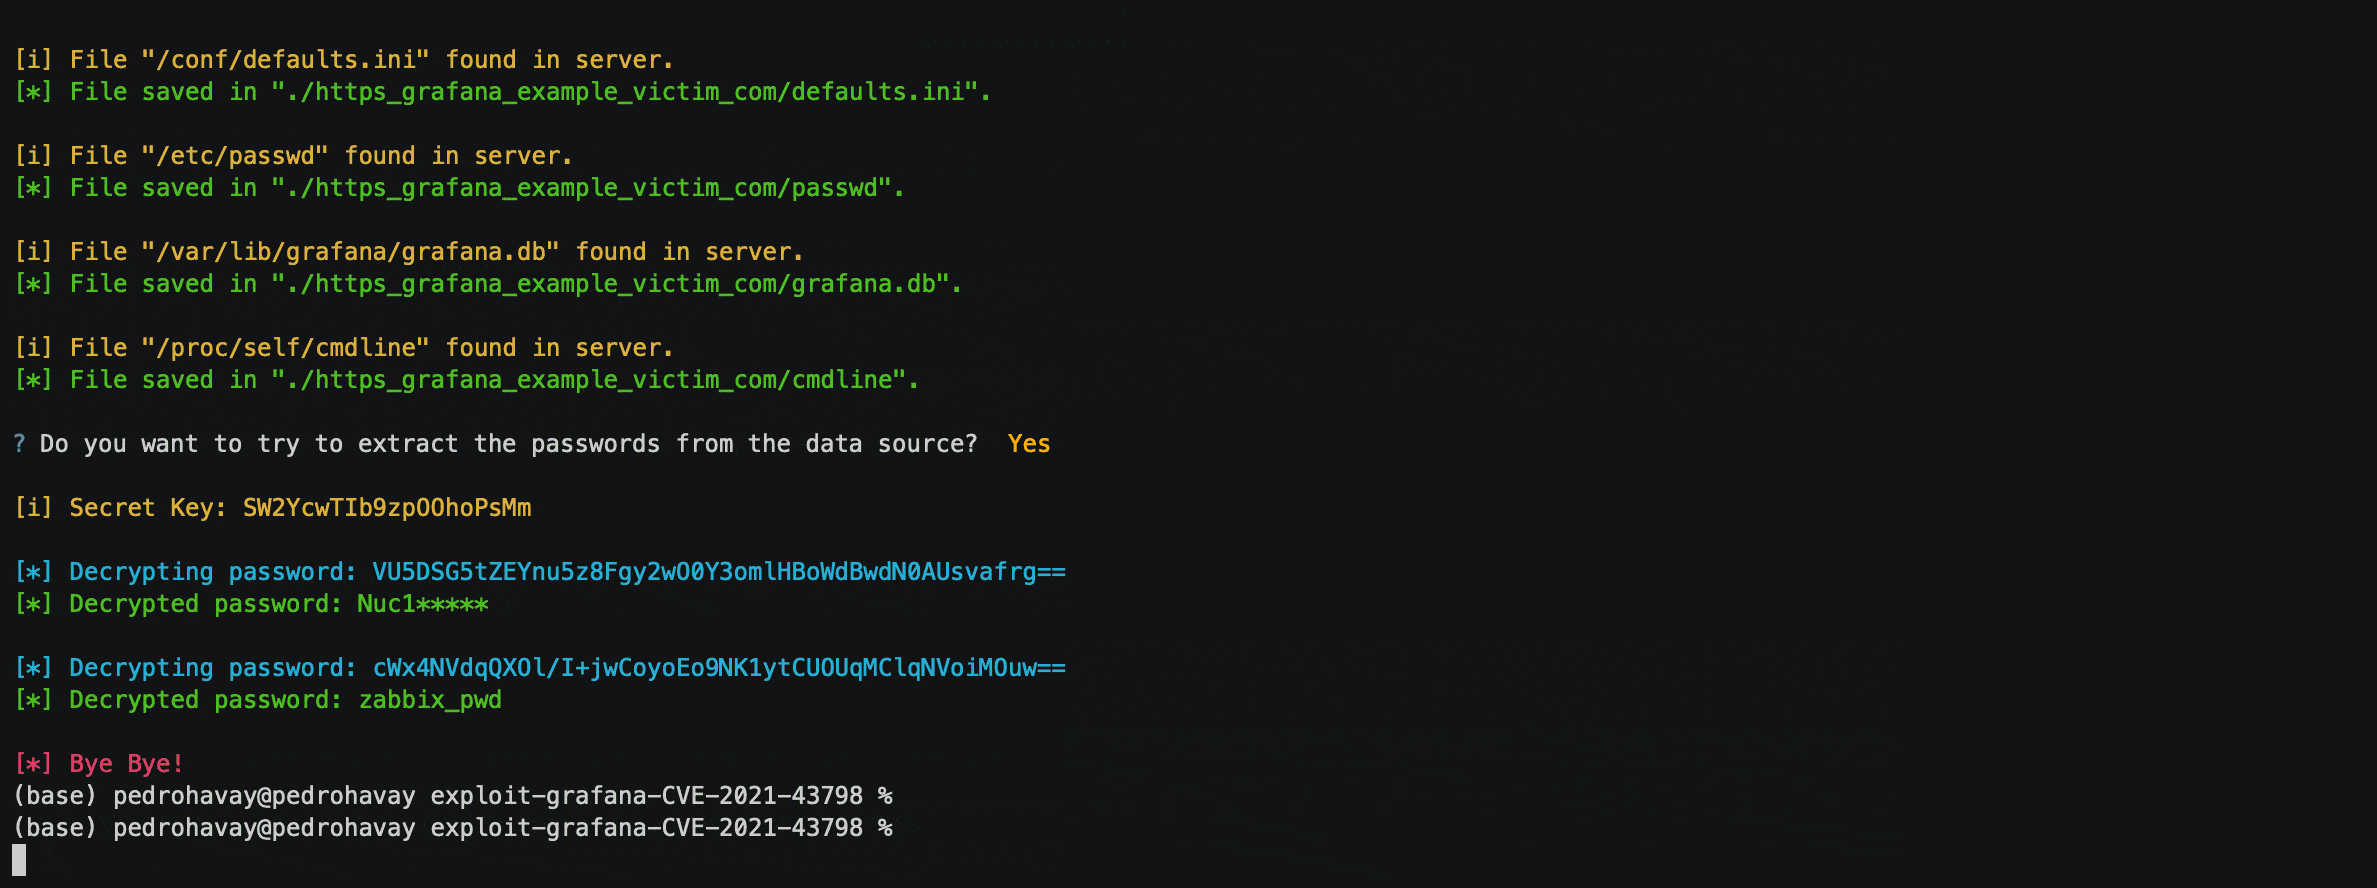 pedrohavay/exploit-grafana-cve-2021-43798
This is a proof-of-concept exploit for Grafana's Unauthorized Arbitrary File Read Vulnerability (CVE-2021-43798).
 dmitri131313/cve-2012-1823-exploit-for-https-user-password-web
CVE-2012-1823 exploit for https user password website.
 kh4sh3i/proxylogon
Exploit chain for CVE-2021-26855 and CVE-2021-27065 targeting Microsoft Exchange Server, enabling authentication bypass and remote code execution via…
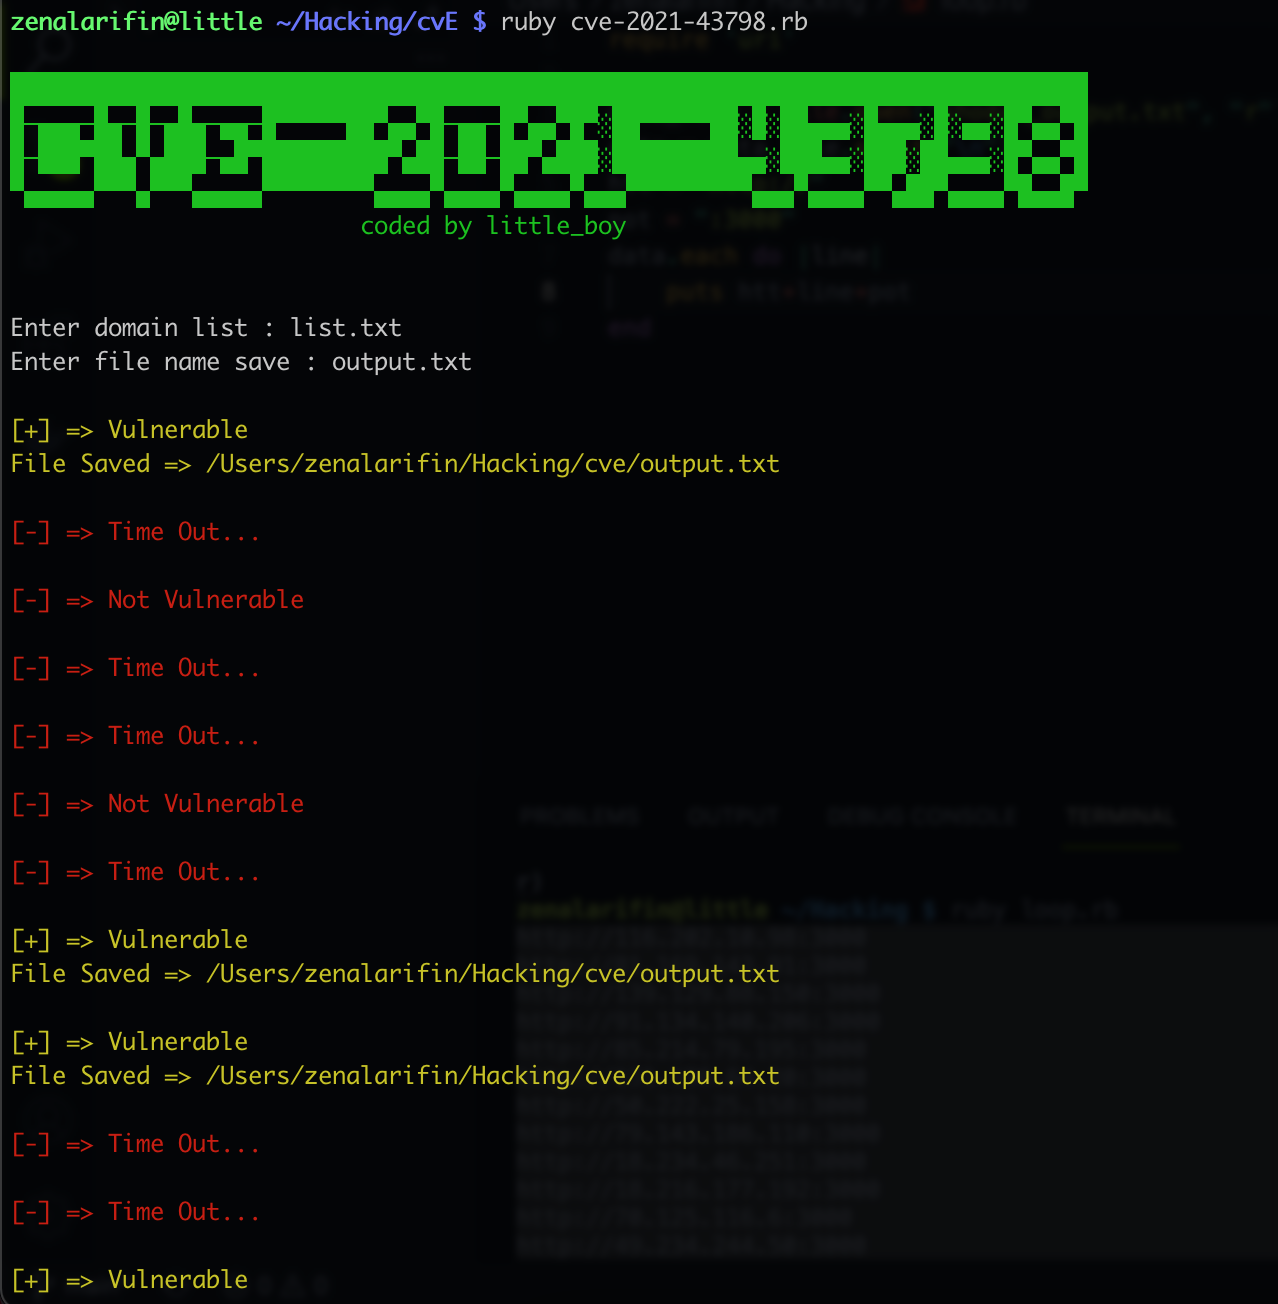 z3n70/cve-2021-43798
Simple program for exploit grafana
 mauricelambert/cve-2021-41773
Multi-language exploit and detection scripts for CVE-2021-41773, enabling remote code execution and local file disclosure on vulnerable Apache…