
BugBountyScanner
 chvancooten/bugbountyscanner
A Bash script and Docker image for Bug Bounty reconnaissance. Intended for headless use.
crawlerinformation-gatheringpenetration-testing+5
924
chvancooten/bugbountyscannerA Bash script and Docker image for Bug Bounty reconnaissance. Intended for headless use.
 cyberblackhole/domain-to-webapp
Bash script that enumerates subdomains via Subfinder, resolves IPs, and identifies live web applications hosted on a domain for reconnaissance and…
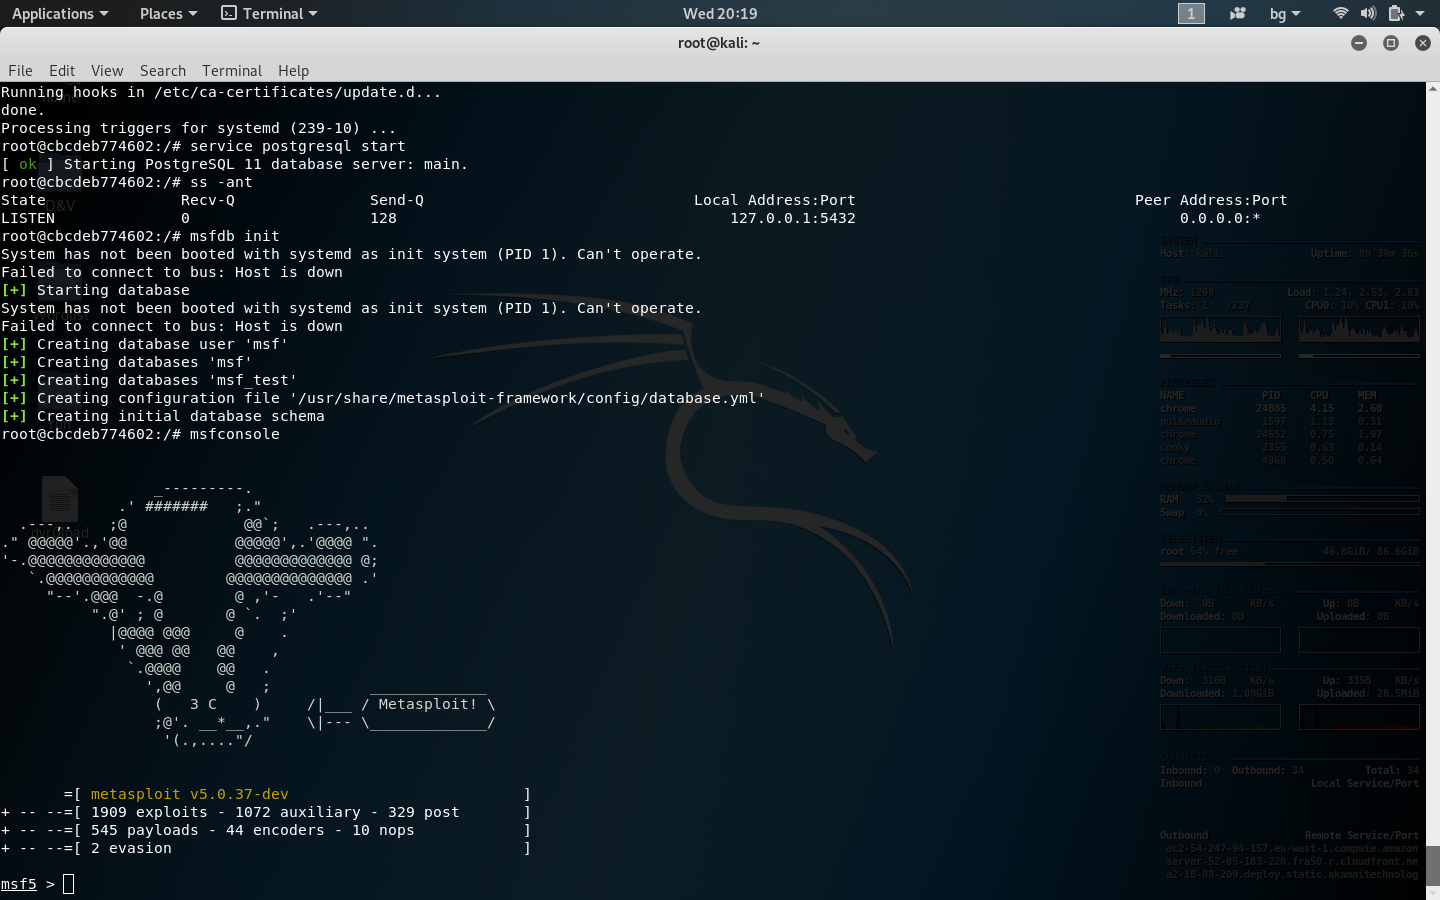 nu11secur1ty/kali-linux-docker
kali-linux-docker
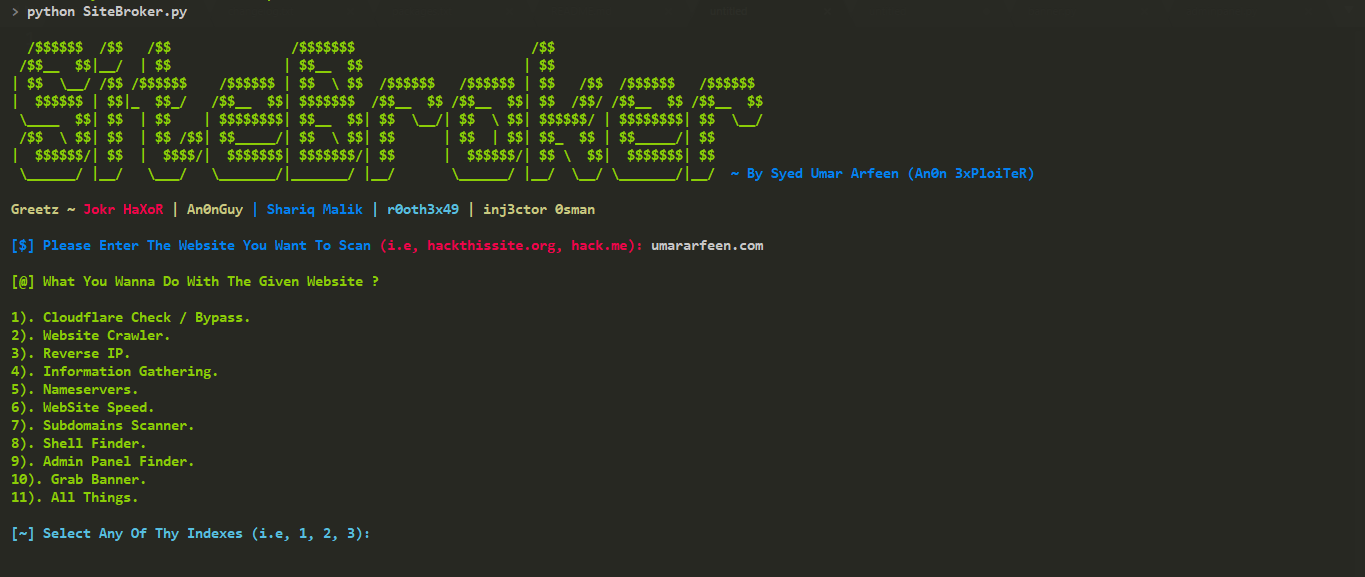 anon-exploiter/sitebroker
A cross-platform python based utility for information gathering and penetration testing automation!
 tuxotron/asn-search
Extract ASN information about a given company
 nccgroup/go-pillage-registries
Pentester-focused Docker registry tool to enumerate and pull images
 milesrichardson/docker-onion-nmap
Scan .onion hidden services with nmap using Tor, proxychains and dnsmasq in a minimal alpine Docker container.
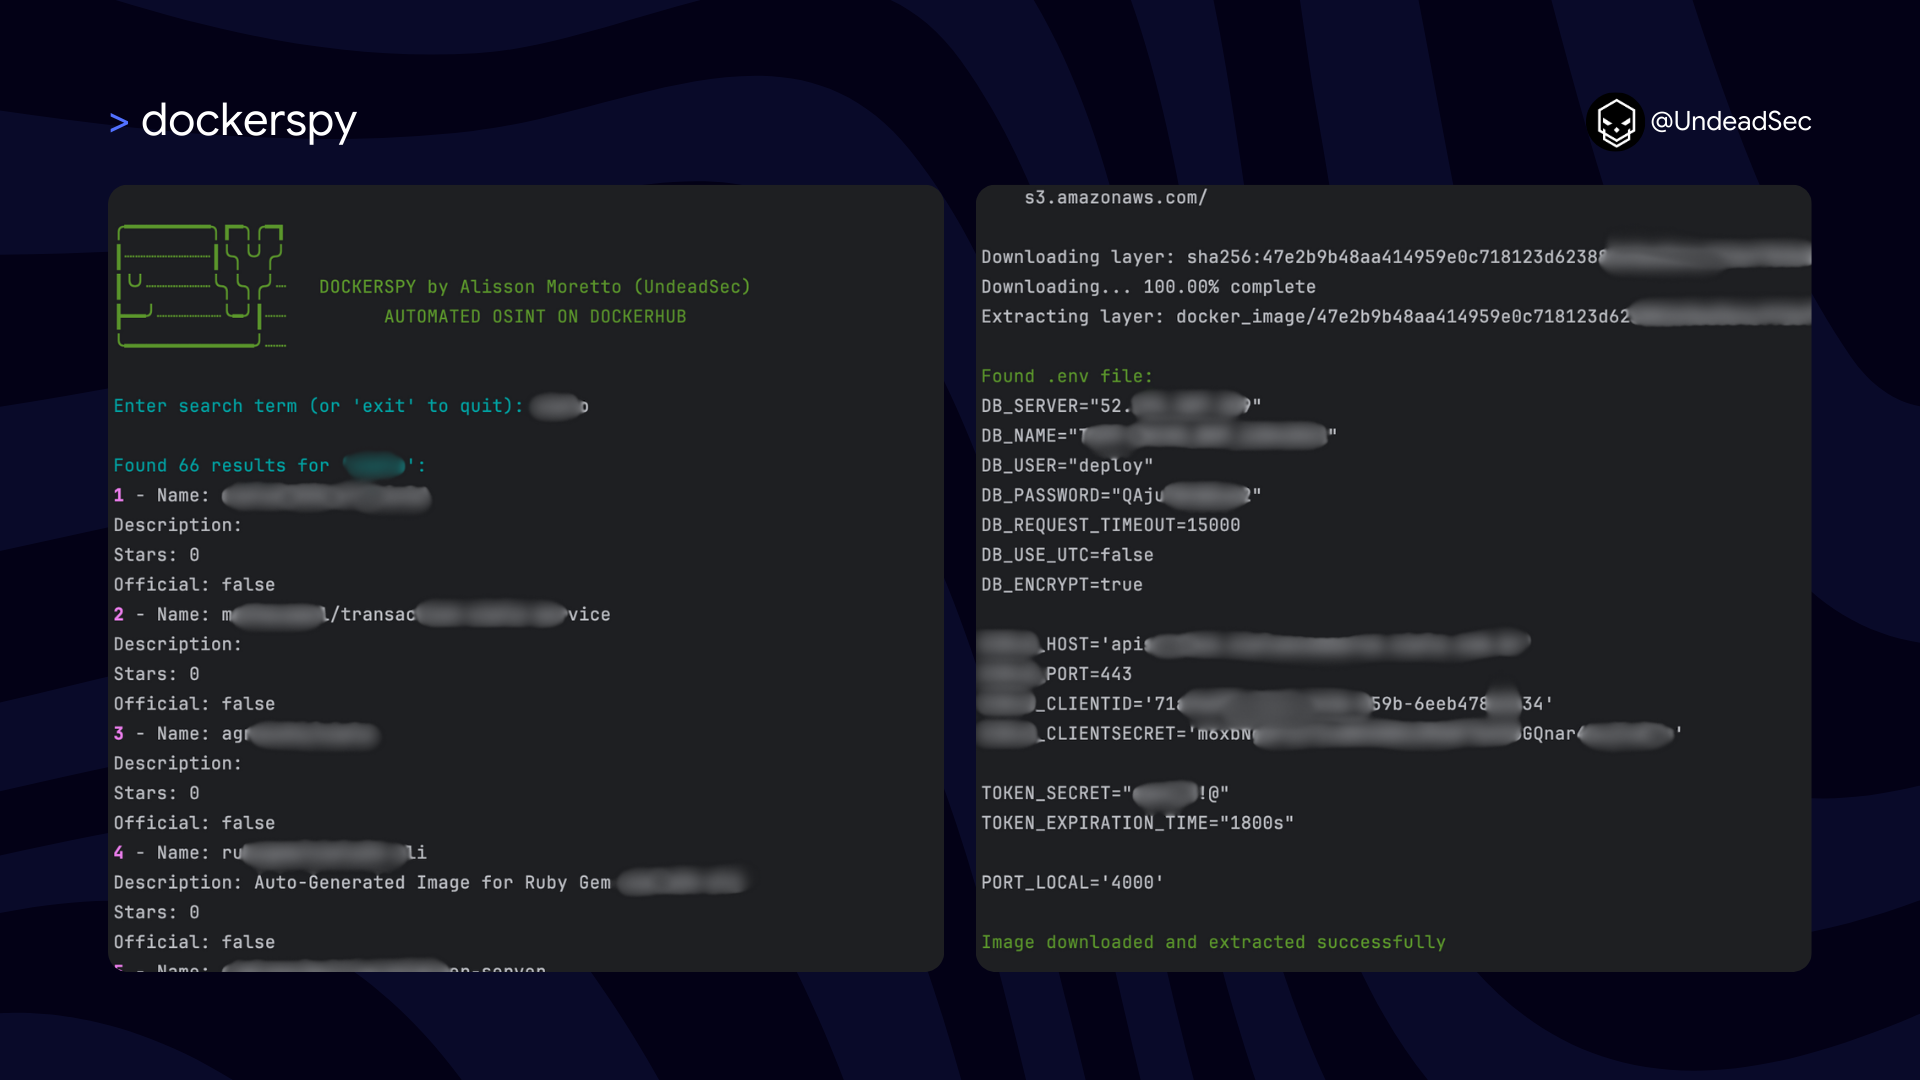 undeadsec/dockerspy
Scans Docker Hub images using regex patterns to extract exposed secrets, private keys, and authentication tokens for security auditing and incident…
 himazawa/bento
Bento Toolkit is a minimal fedora-based container for penetration tests and CTF with the sweet addition of GUI applications.
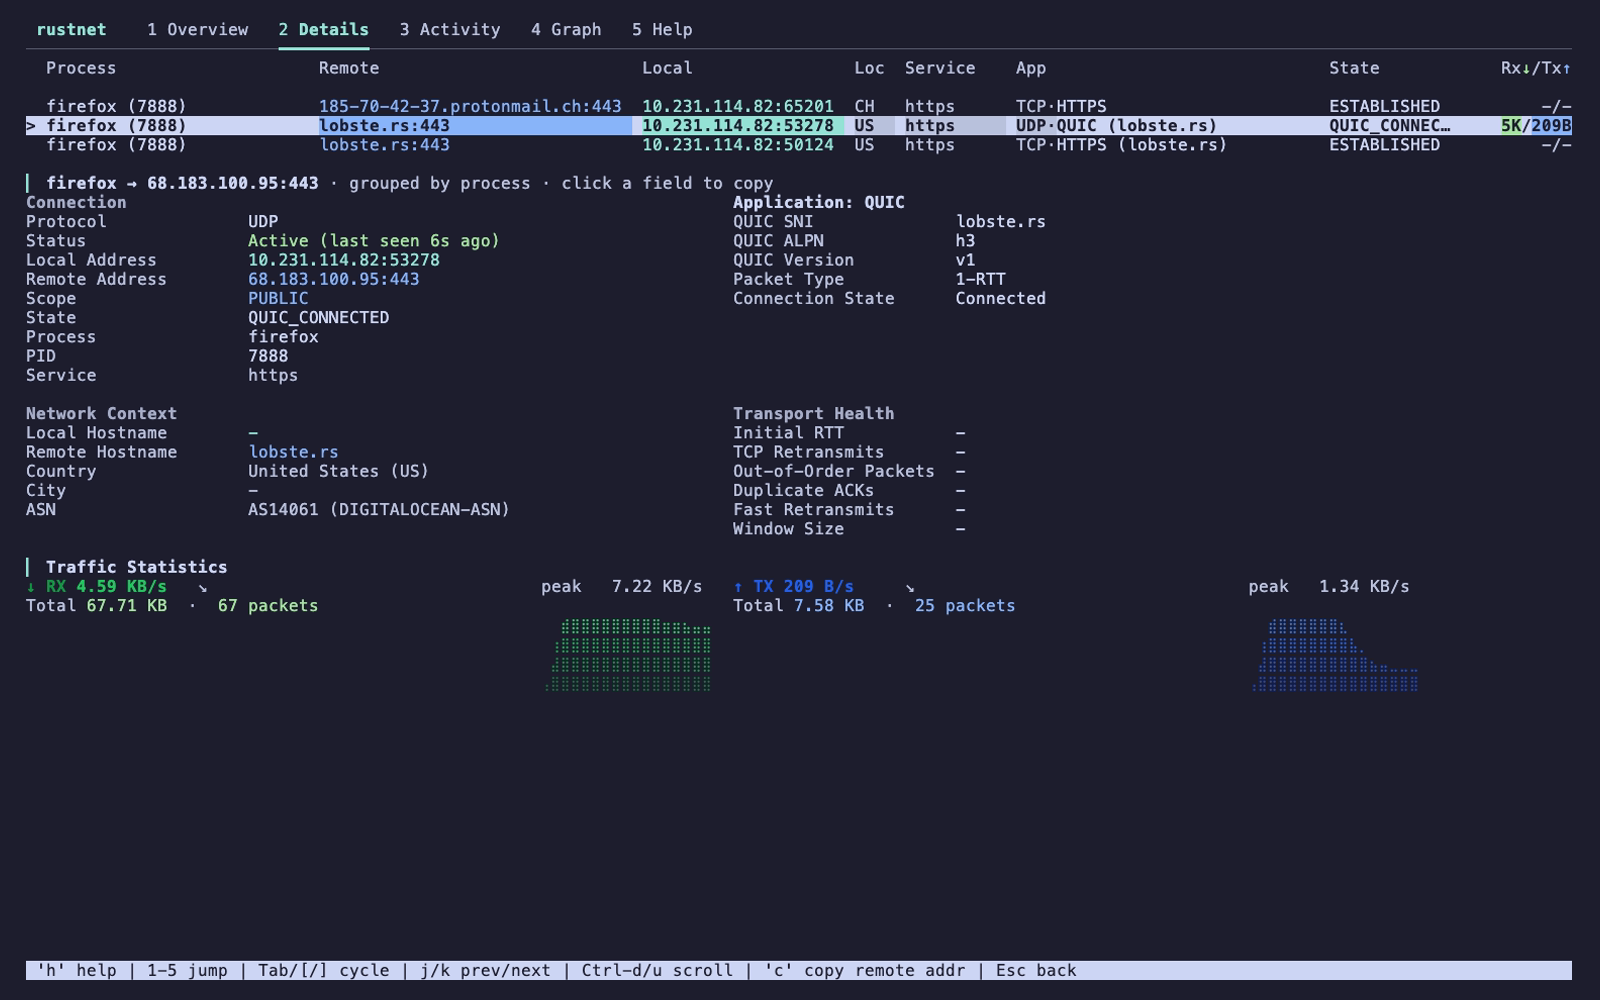 domcyrus/rustnet
Per-process network monitoring for your terminal with deep packet inspection. Cross-platform, sandboxed.
 professionallyevil/harpoon
A collection of scripts, and tips and tricks for hacking k8s clusters and containers.
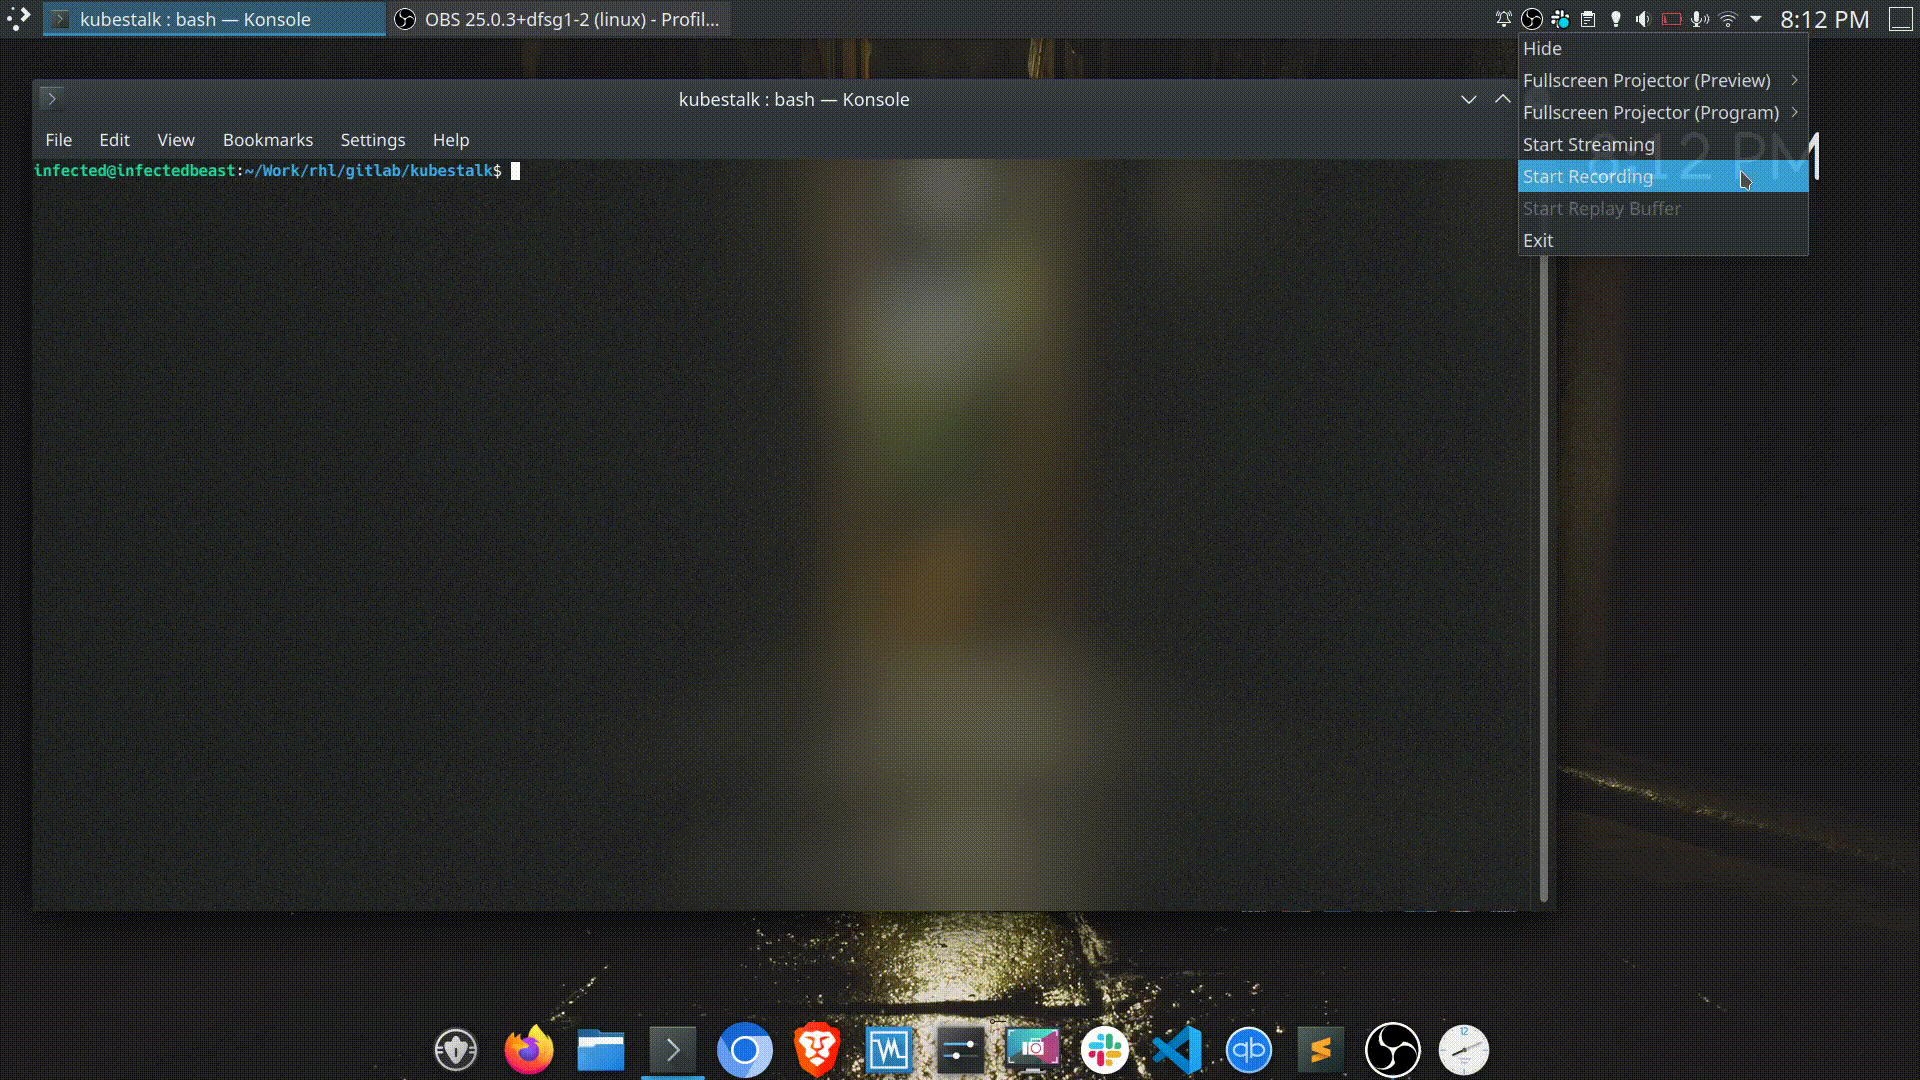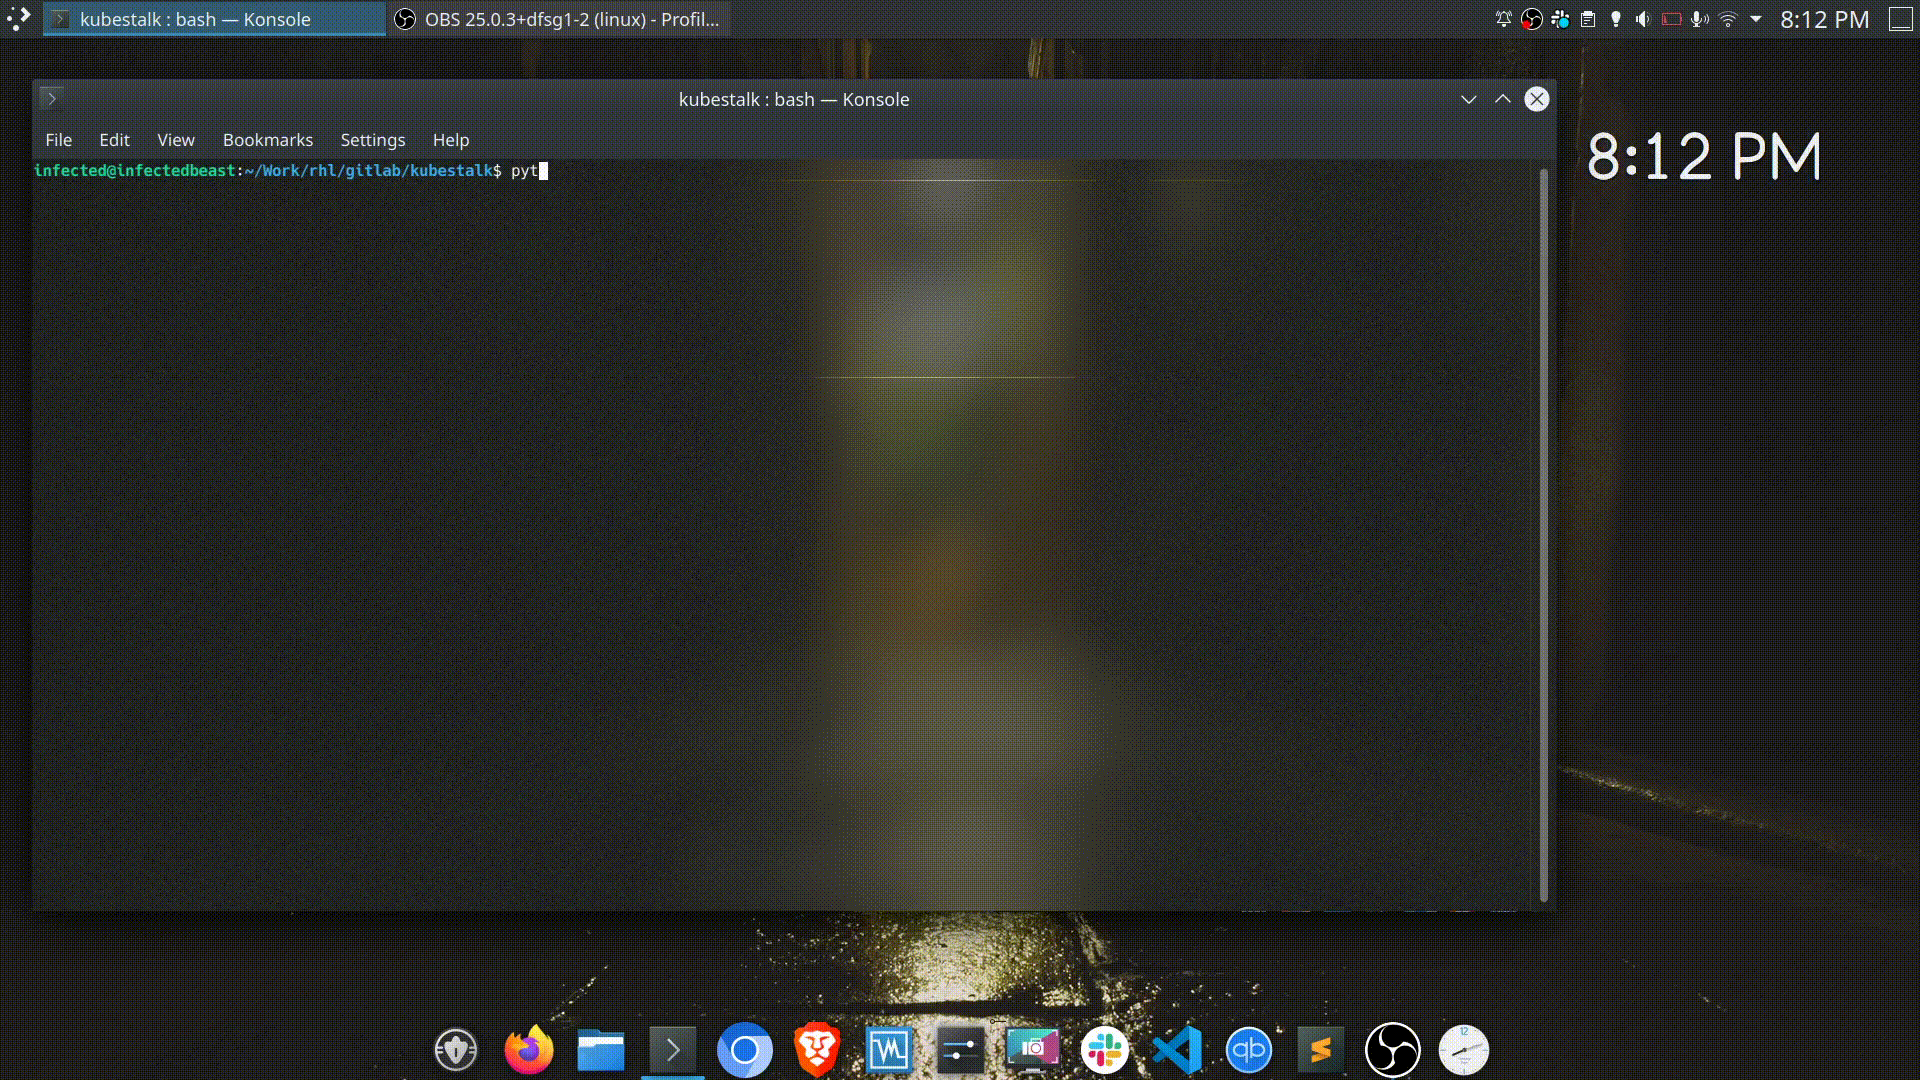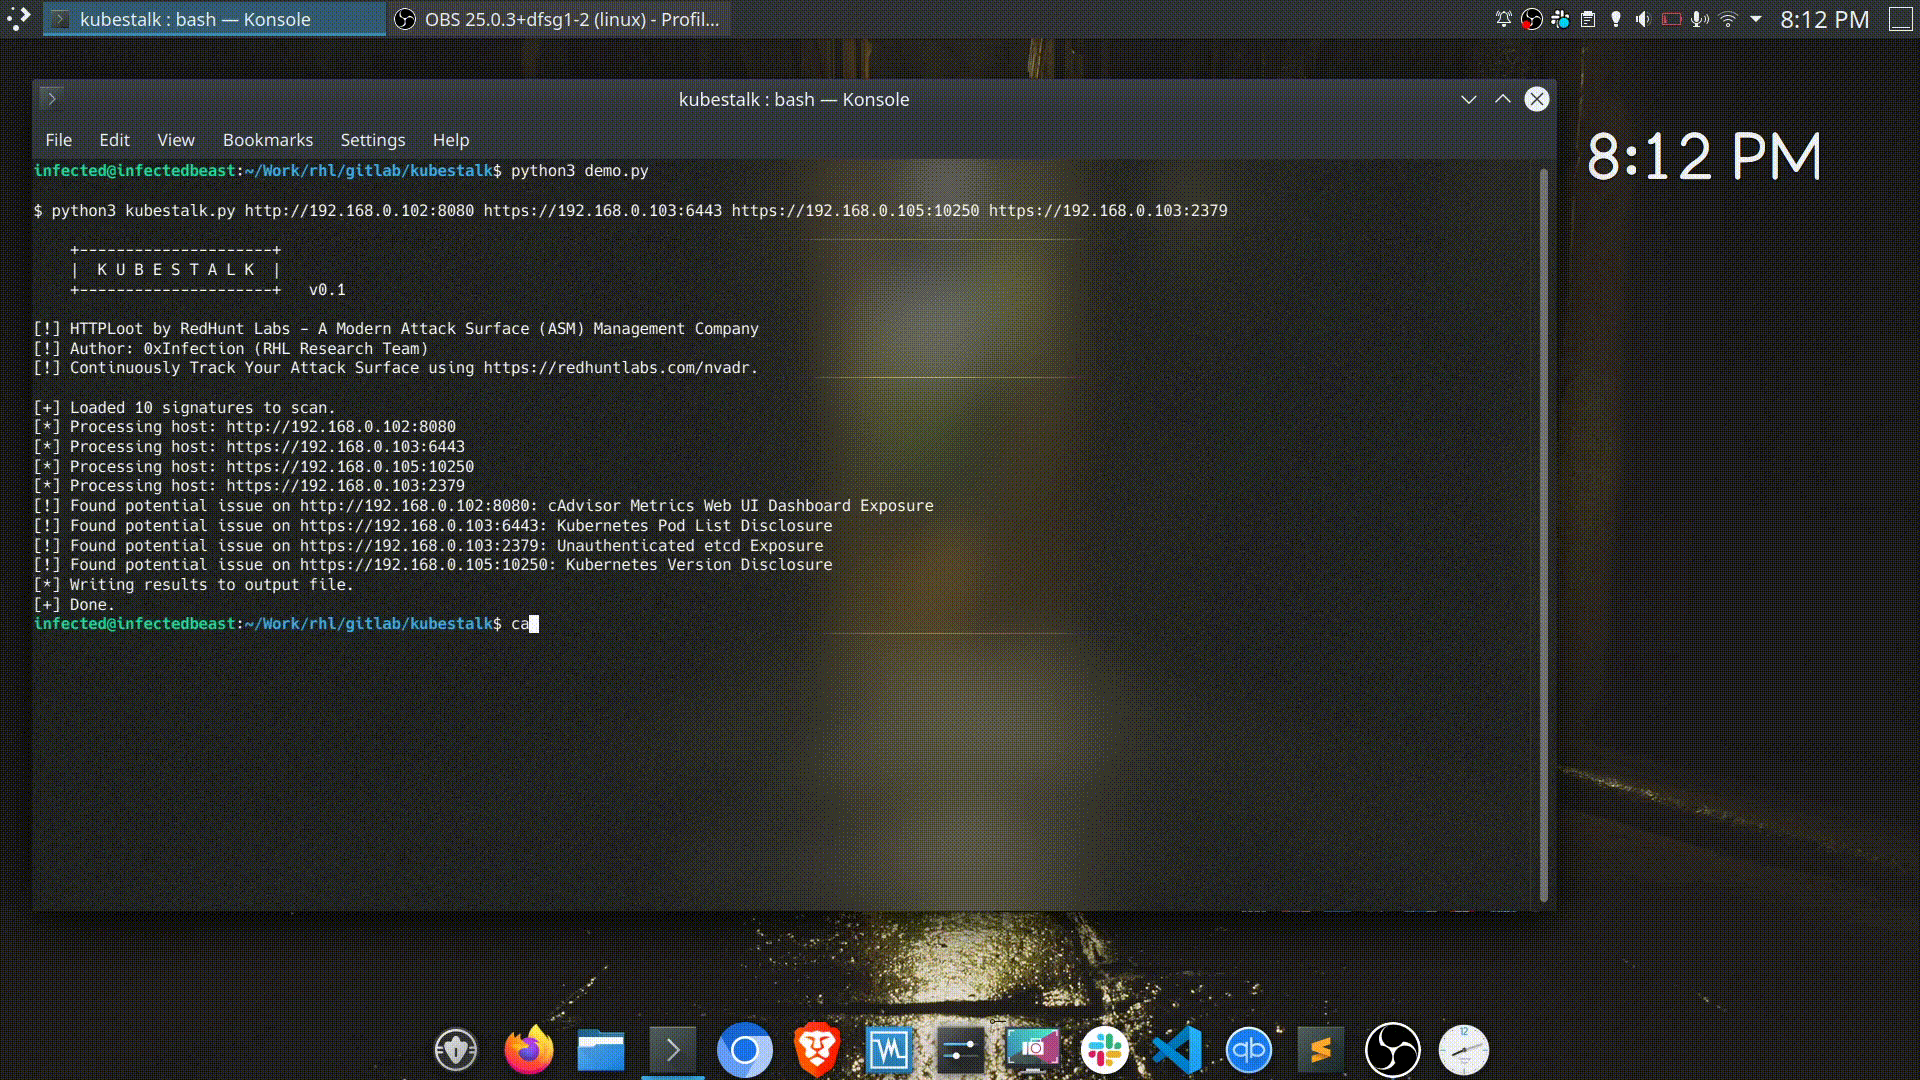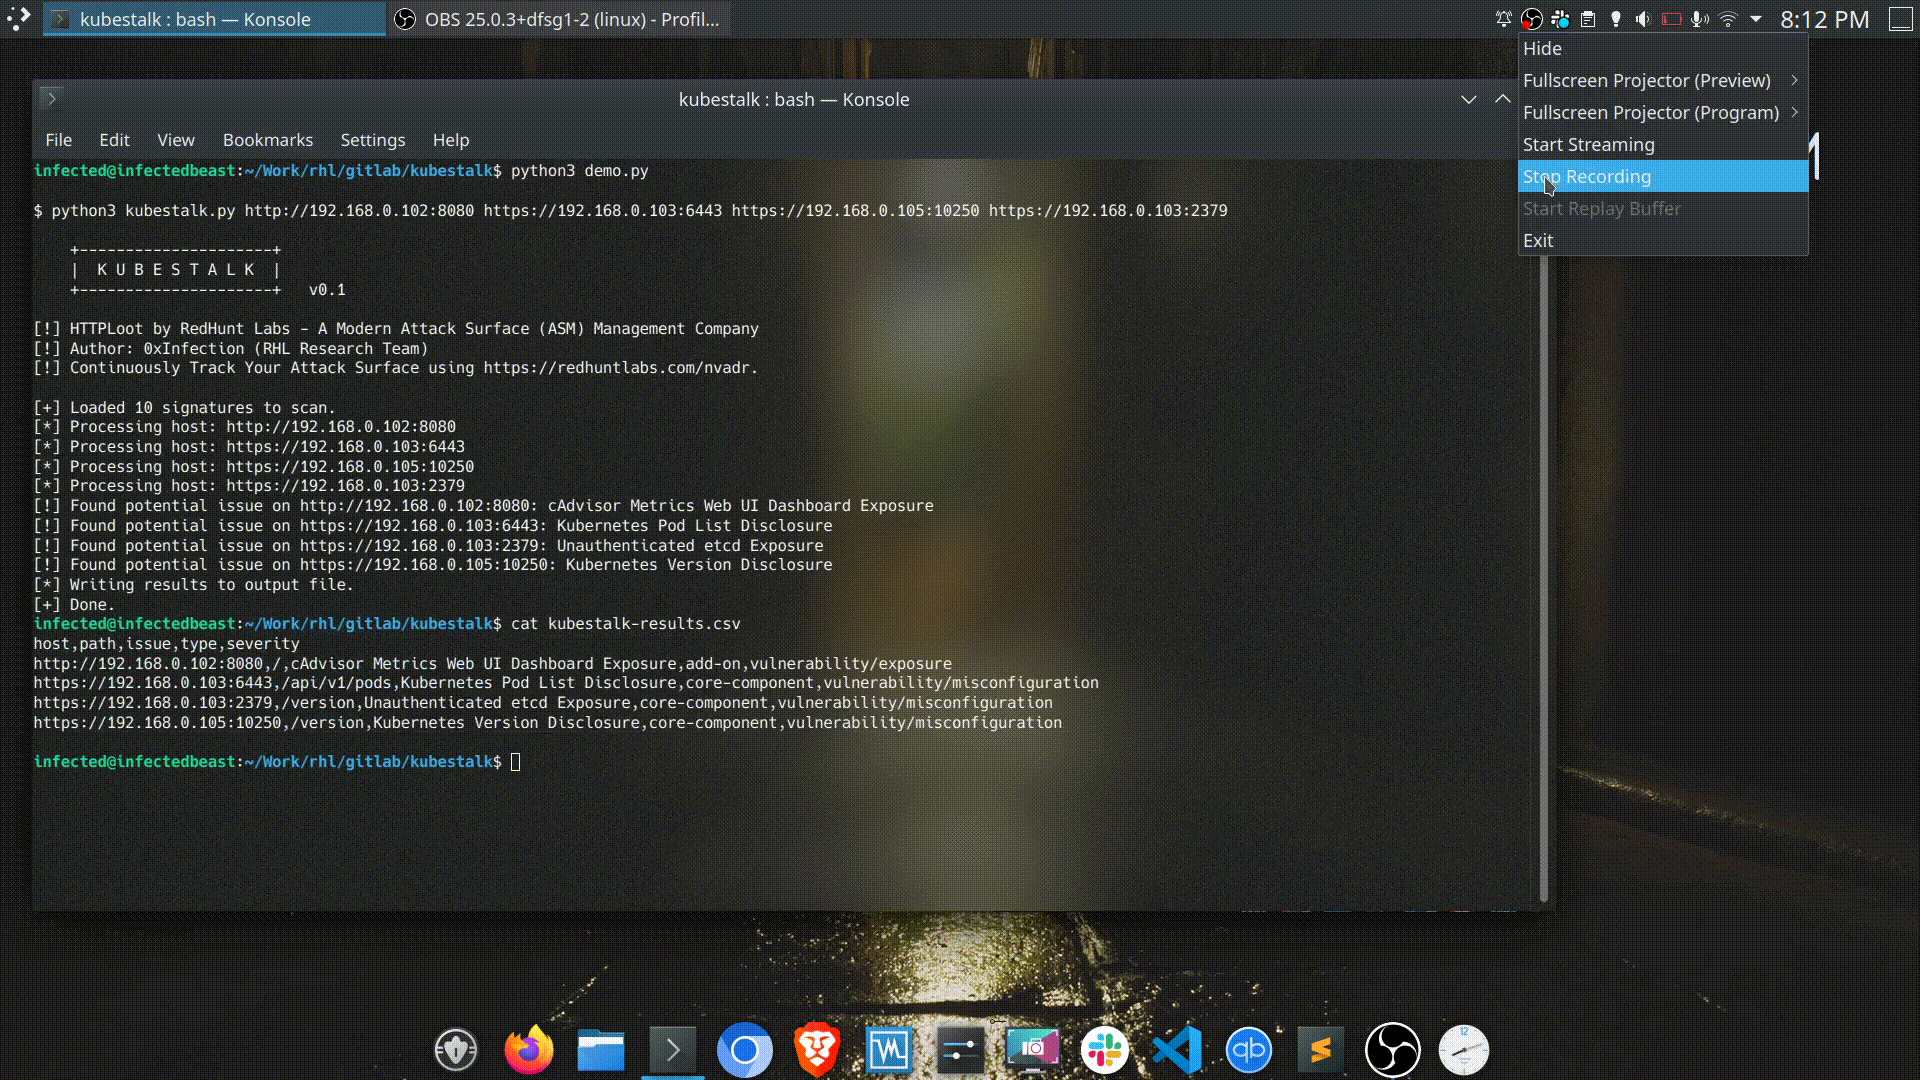 redhuntlabs/kubestalk
Black-box Kubernetes attack surface discovery tool that probes for unsecured clusters, exposed dashboards, and misconfigurations using…
 k8scout/k8scout
Drop a single binary into a compromised Kubernetes pod and instantly map every realistic attack path to cluster-admin, node escape, secret theft,…
 loresuso/psc
the ps utility, with an eBPF twist and container context
 lijiejie/log4j2_vul_local_scanner
Log4j 漏洞本地检测脚本。 Scan all java processes on your host to check whether it's affected by log4j2 remote code execution vulnerability (CVE-2021-45046)
 404tk/cve-2022-46463
harbor unauthorized detection
 tabbysable/poc-2020-8558
Information about Kubernetes CVE-2020-8558, including proof of concept exploit.
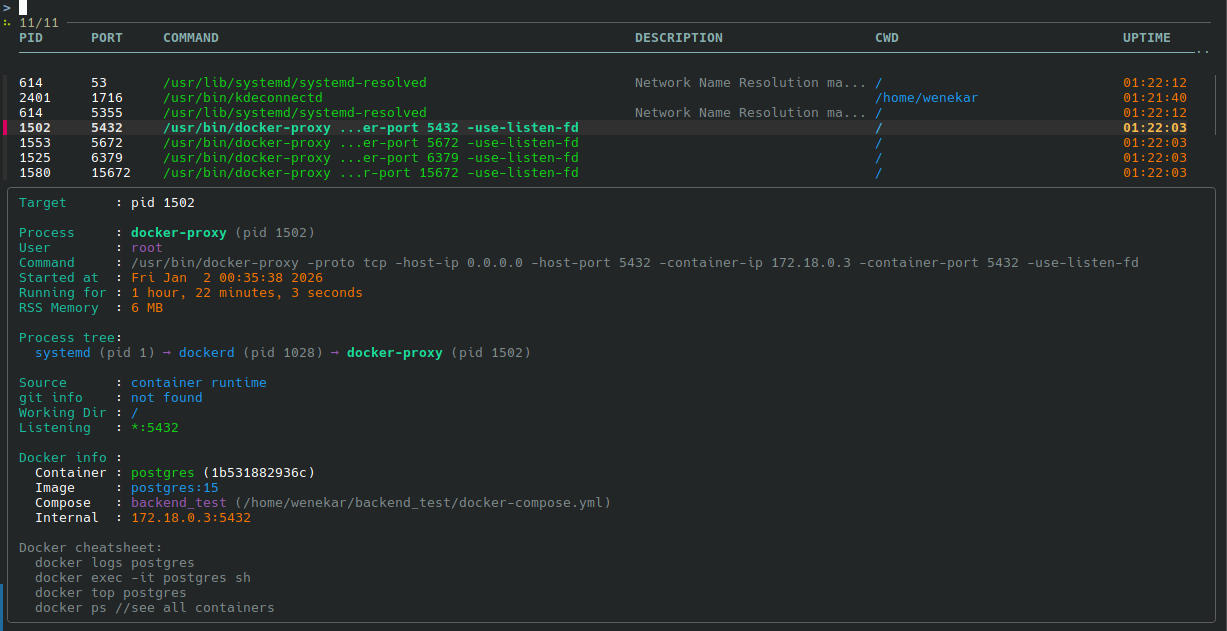 wenekar/procinfo
Get process information straight from bash, minimal dependencies.