

CVE-2023-22515-Scan
 erikwynter/cve-2023-22515-scan
Scanner for CVE-2023-22515 - Broken Access Control Vulnerability in Atlassian Confluence
exploitationinformation-gatheringpenetration-testing+3
80
erikwynter/cve-2023-22515-scanScanner for CVE-2023-22515 - Broken Access Control Vulnerability in Atlassian Confluence
 certitude-consulting/cve-2025-25599
Proof of Concept for CVE-2025-25599
 oligocybersecurity/cve-2023-43654
Demo for CVE-2023-43654 - Remote Code Execution in PyTorch TorchServe
 d0rb/cve-2023-49103
Proof-of-concept exploit for CVE-2023-49103, an unauthenticated information disclosure vulnerability in ownCloud Graph API, leaking environment…
 ma111e/melody
Melody is a transparent internet sensor built for threat intelligence. Supports custom tagging rules and vulnerable application simulation.
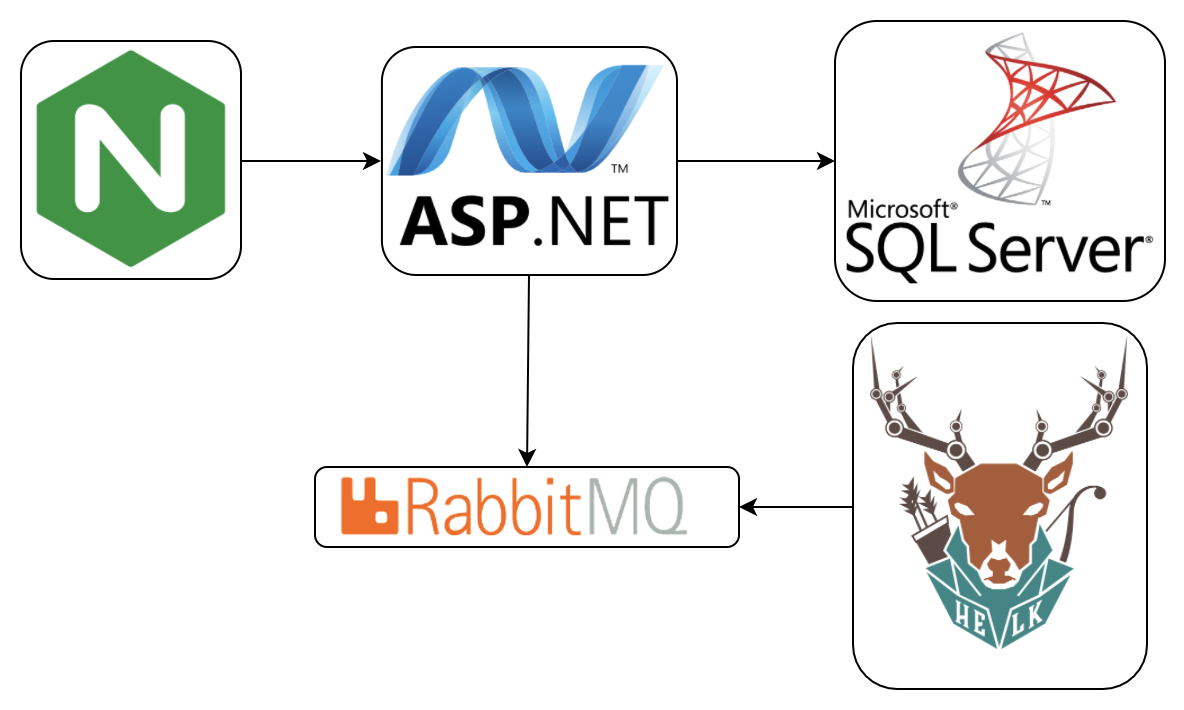 invoke-ir/ace
Automated, Collection, and Enrichment Platform
 cveproject/cvelistv5
CVE cache of the official CVE List in CVE JSON 5 format
 ghostmanager/ghostwriter
The SpecterOps project management and reporting engine
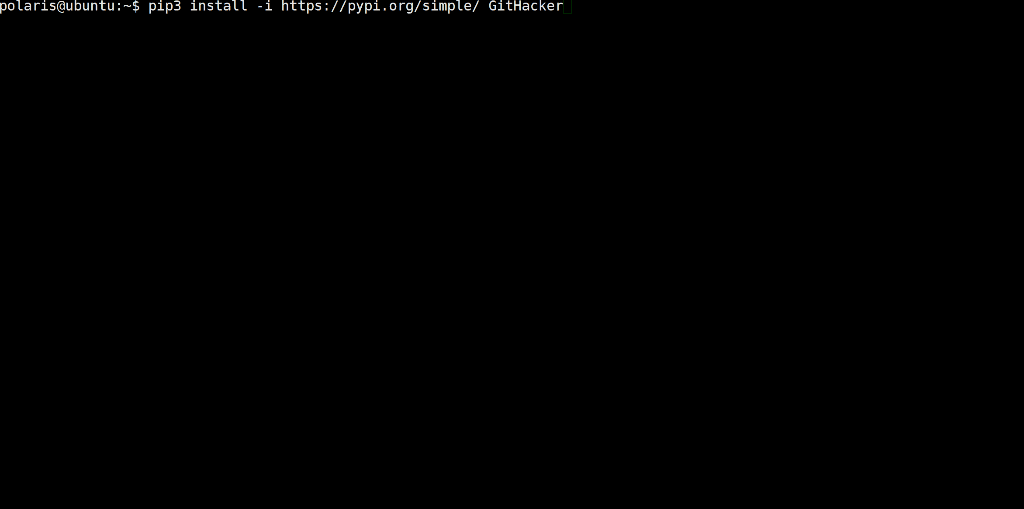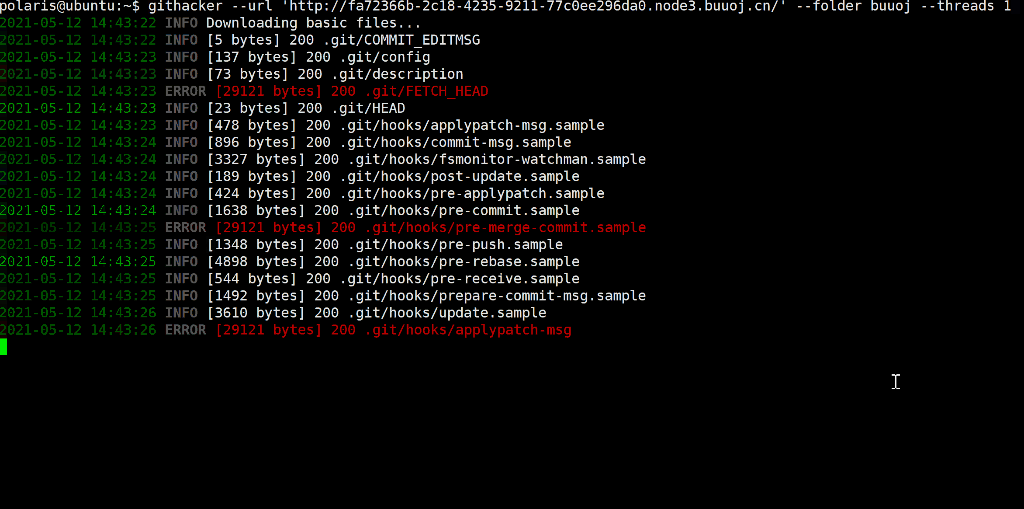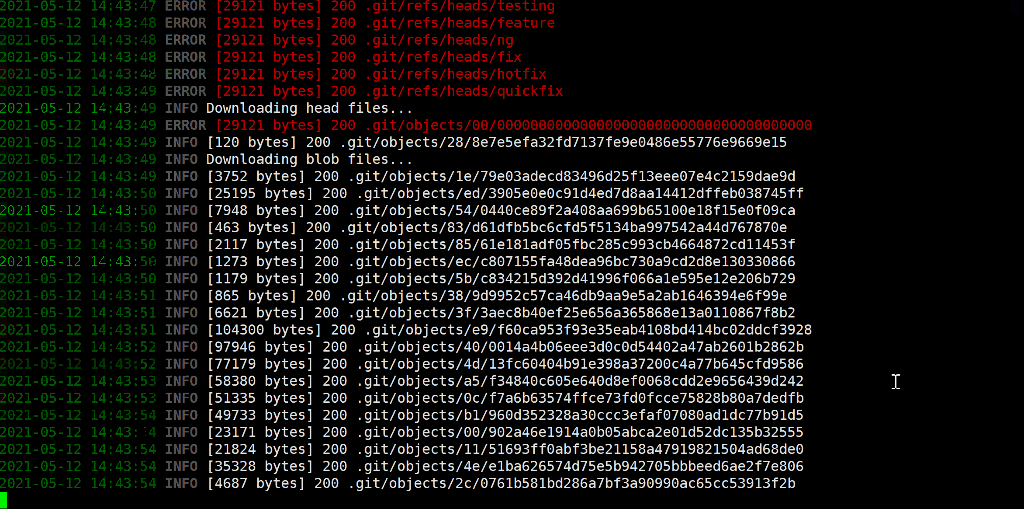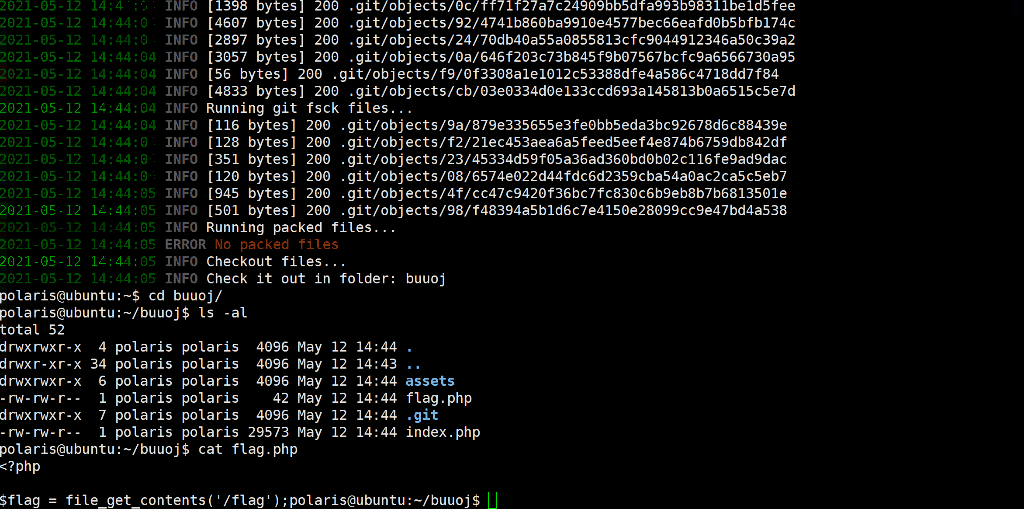 wangyihang/githacker
🕷️ A `.git` folder exploiting tool that is able to restore the entire Git repository, including stash, common branches and common tags.
 ivanglinkin/fast-google-dorks-scan
The OSINT project, the main idea of which is to collect all the possible Google dorks search combinations and to find the information about the…
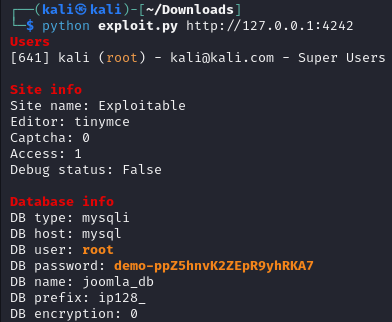 fernando-olv/joomla-cve-2023-23752
This Python implementation serves an educational purpose by demonstrating the exploitation of CVE-2023-23752. The code provides insight into the…
 mrtuxx/socialpwned
SocialPwned is an OSINT tool that allows to get the emails, from a target, published in social networks such as Instagram, Linkedin and Twitter to…
 evilsocket/dnssearch
A subdomain enumeration tool.
 punk-security/smbeagle
SMBeagle - Fileshare auditing tool.
 algosecure/pollenisator
Collaborative pentest tool with highly customizable tools
 vulnmachines/oracle-weblogic-cve-2022-21371
Oracle WebLogic CVE-2022-21371