
CVE-2023-08-21-exploit
 amirzargham/cve-2023-08-21-exploit
Axigen < 10.3.3.47, 10.2.3.12 - Reflected XSS
data-exfiltrationexploitationinformation-gathering+3
1
amirzargham/cve-2023-08-21-exploitAxigen < 10.3.3.47, 10.2.3.12 - Reflected XSS
 yobing1/cve-2023-40924
SolarView vuln
 arpsyndicate/cve-scores
Aggregates EPSS and VEDAS scores for CVEs, providing exploit prediction and vulnerability prevalence data from open-source intelligence for threat…
 sakthivel10q/cve-2025-14847
🛠 Exploit the CVE-2025-14847 vulnerability in MongoDB to disclose sensitive heap memory using a Python script that analyzes responses for new leaked…
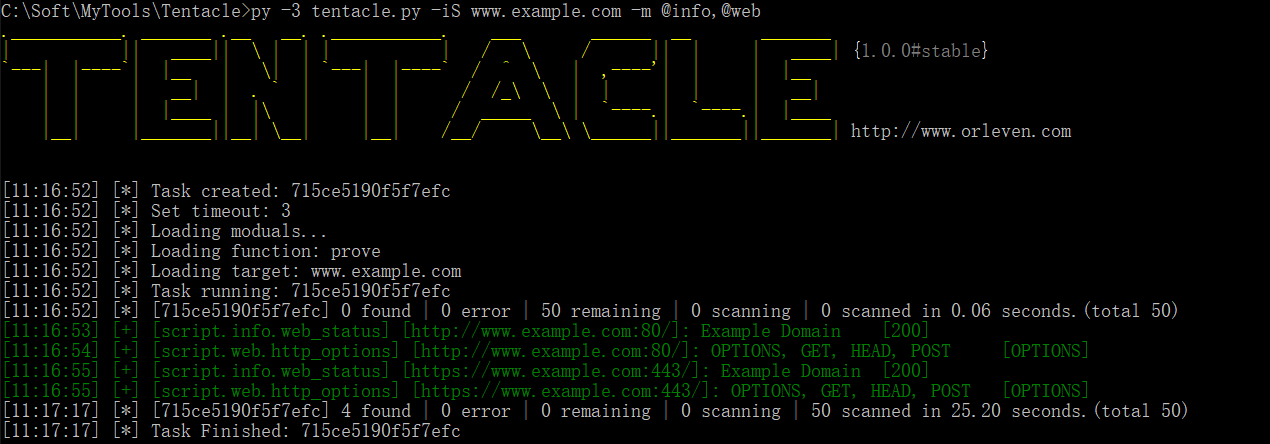 orleven/tentacle
Tentacle is a POC vulnerability verification and exploit framework. It supports free extension of exploits and uses POC scripts. It supports calls to…
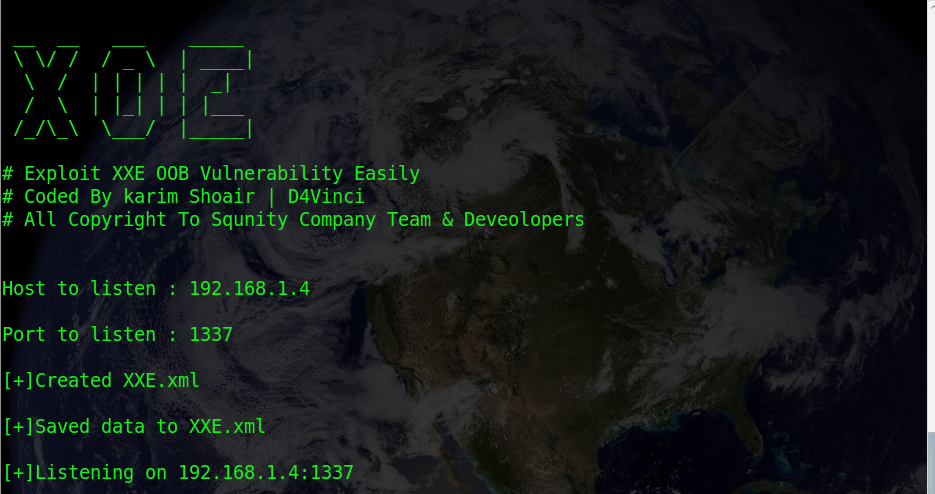 d4vinci/xoe
Exploit XXE Out-Of-Band Vulnerability Easily
 sh4den/cve-2025-52488
This exploit targets a vulnerability in DNN (formerly DotNetNuke) versions 6.0.0 to before 10.0.1 that allows attackers to disclose NTLM hashes…
 gmh5225/cve-2025-6554-2
Exploit for CVE-2025-6554 vulnerability with proof-of-concept code for security testing and vulnerability verification.
 mdunfjeld/cve-2025-59886
Exploit for CVE-2025-59886 vulnerability, providing proof-of-concept code for security testing and vulnerability verification.
 kinghacker353/cve-2025-55184
Exploit for CVE-2025-55184 vulnerability with Python-based scanning and exploitation capabilities for penetration testing and security assessment.
 sherlocksecurity/cve-2025-55182-exploit-scanner
Python-based scanner for CVE-2025-55182, designed to detect and exploit the specific vulnerability in target systems for security assessment.
 pog-frog/cve-2022-44268
Generates malicious PNG files to exploit ImageMagick LFI vulnerability (CVE-2022-44268) for arbitrary file read, with extraction script for…
 rhynorater/cve-2018-15473-exploit
Exploit written in Python for CVE-2018-15473 with threading and export formats
 rvzsec/cve-2023-40028
CVE-2023-40028 PoC Exploit
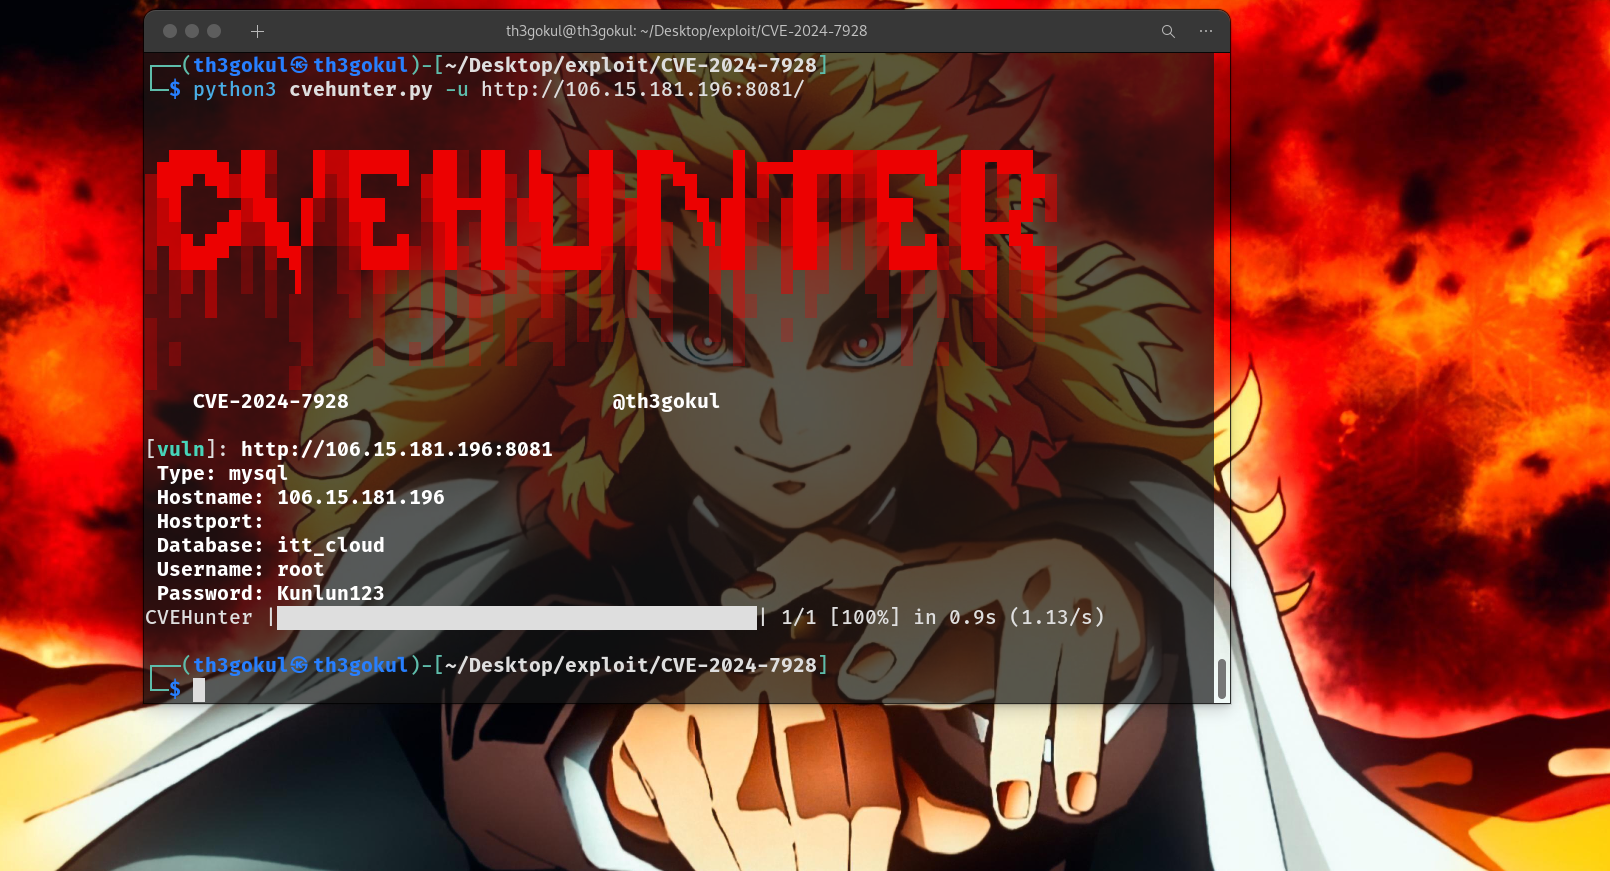 th3gokul/cve-2024-7928
CVE-2024-7928: FastAdmin < V1.3.4.20220530 Arbitrary File Reading Vulnerability
 alissonfaoli/cve-2023-23752
Joomla Unauthenticated Information Disclosure (CVE-2023-23752) exploit
 blu3ming/poc-cve-2021-41773
Python exploit for CVE-2021-41773 - Apache HTTP Server 2.4.49 Path Traversal vulnerability
 gmh5225/cve-2022-24716
Arbitrary File Disclosure Vulnerability in Icinga Web 2 <2.8.6, <2.9.6, <2.10