

CVE-2020-17519
 murataydemir/cve-2020-17519
[CVE-2020-17519] Apache Flink RESTful API Arbitrary File Read
exploitationexploit-frameworksinformation-gathering+3
8
murataydemir/cve-2020-17519[CVE-2020-17519] Apache Flink RESTful API Arbitrary File Read
 zeop-cybersec/citrix_adc_netscaler_lfi
This Metasploit-Framework module can be use to help companies to check the last Citrix vulnerability CVE-2020-8193, CVE-2020-8195 and CVE-2020-8196…
 zhzyker/exphub
Exphub[漏洞利用脚本库] 包括Webloigc、Struts2、Tomcat、Nexus、Solr、Jboss、Drupal的漏洞利用脚本,最新添加CVE-2020-14882、CVE-2020-11444、CVE-2020-10204、CVE-2020-10199、CVE-2020-1938…
 vulnerscom/getsploit
Search and download public exploits from the Vulners database — online, or fully offline from a local SQLite FTS5 index.
 moham3driahi/xattacker
X Attacker Tool ☣ Website Vulnerability Scanner & Auto Exploiter
 s3cur3th1ssh1t/powersharppack
PowerShell wrapper bundling 50+ C# offensive security tools for post-exploitation, privilege escalation, credential dumping, lateral movement, and…
 1n3/findsploit
Find exploits in local and online databases instantly
 gyoisamurai/gyoithon
GyoiThon is a growing penetration test tool using Machine Learning.

 arpsyndicate/puncia
Panthera(P.)uncia - Official CLI utility for Subdomain Center & Exploit Observer.
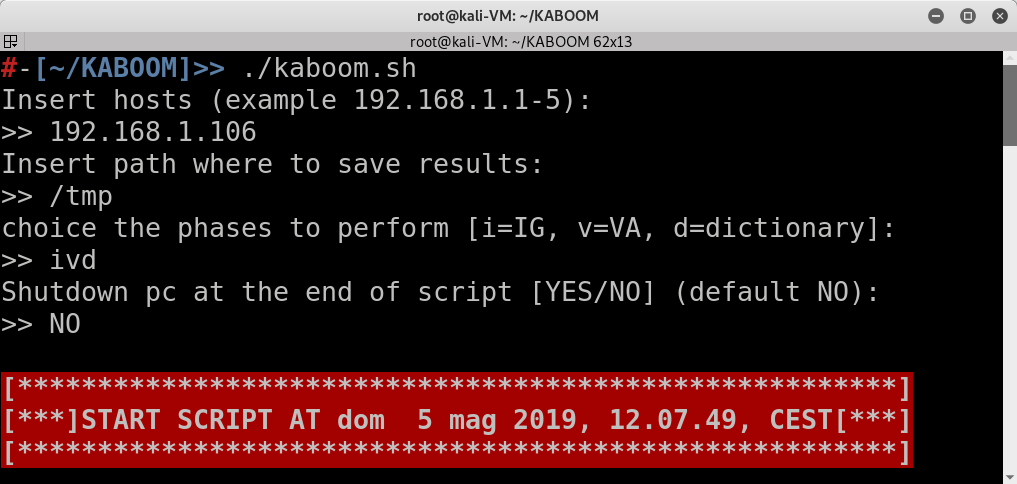 leviathan36/kaboom
A tool to automate penetration tests
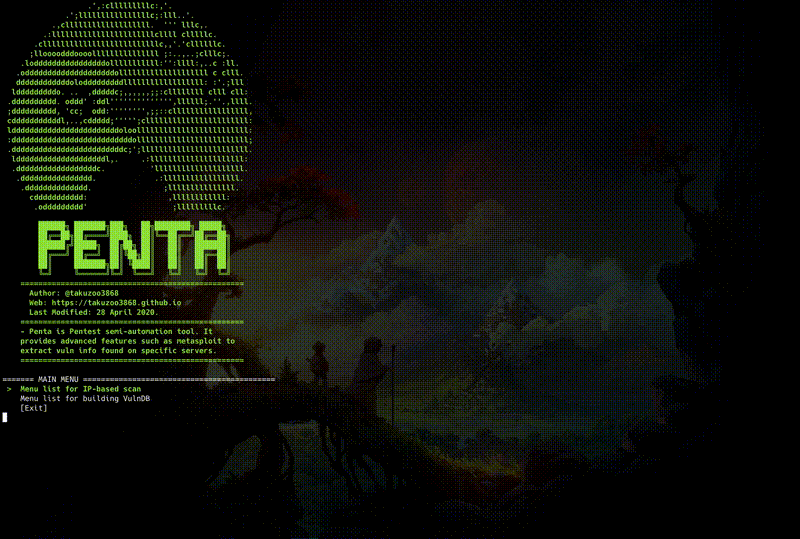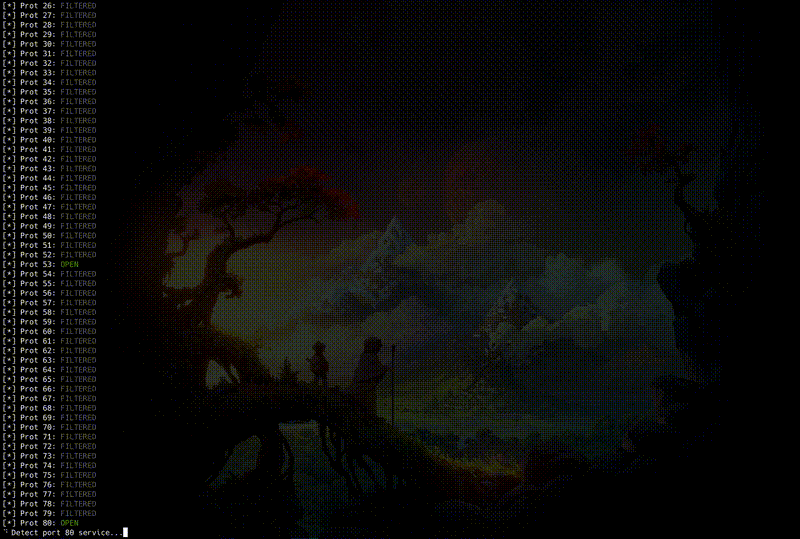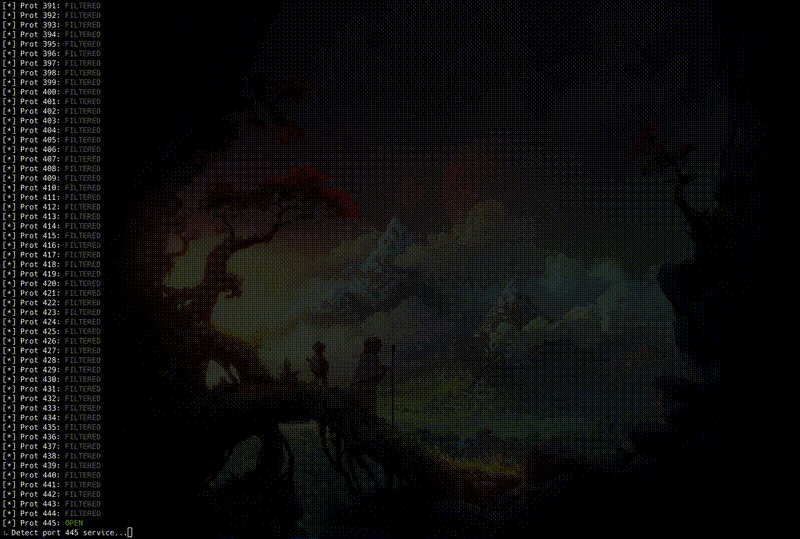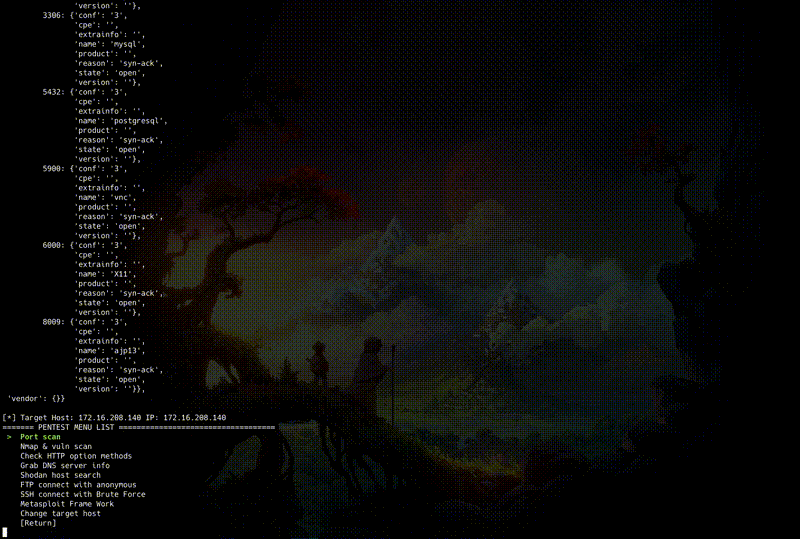 takuzoo3868/penta
Open source all-in-one CLI tool to semi-automate pentesting.
 msd0pe-1/cve-maker
CLI tool to search CVEs and exploits from NIST, ExploitDB, and GitHub databases. Supports exploit compilation detection and lists latest critical…
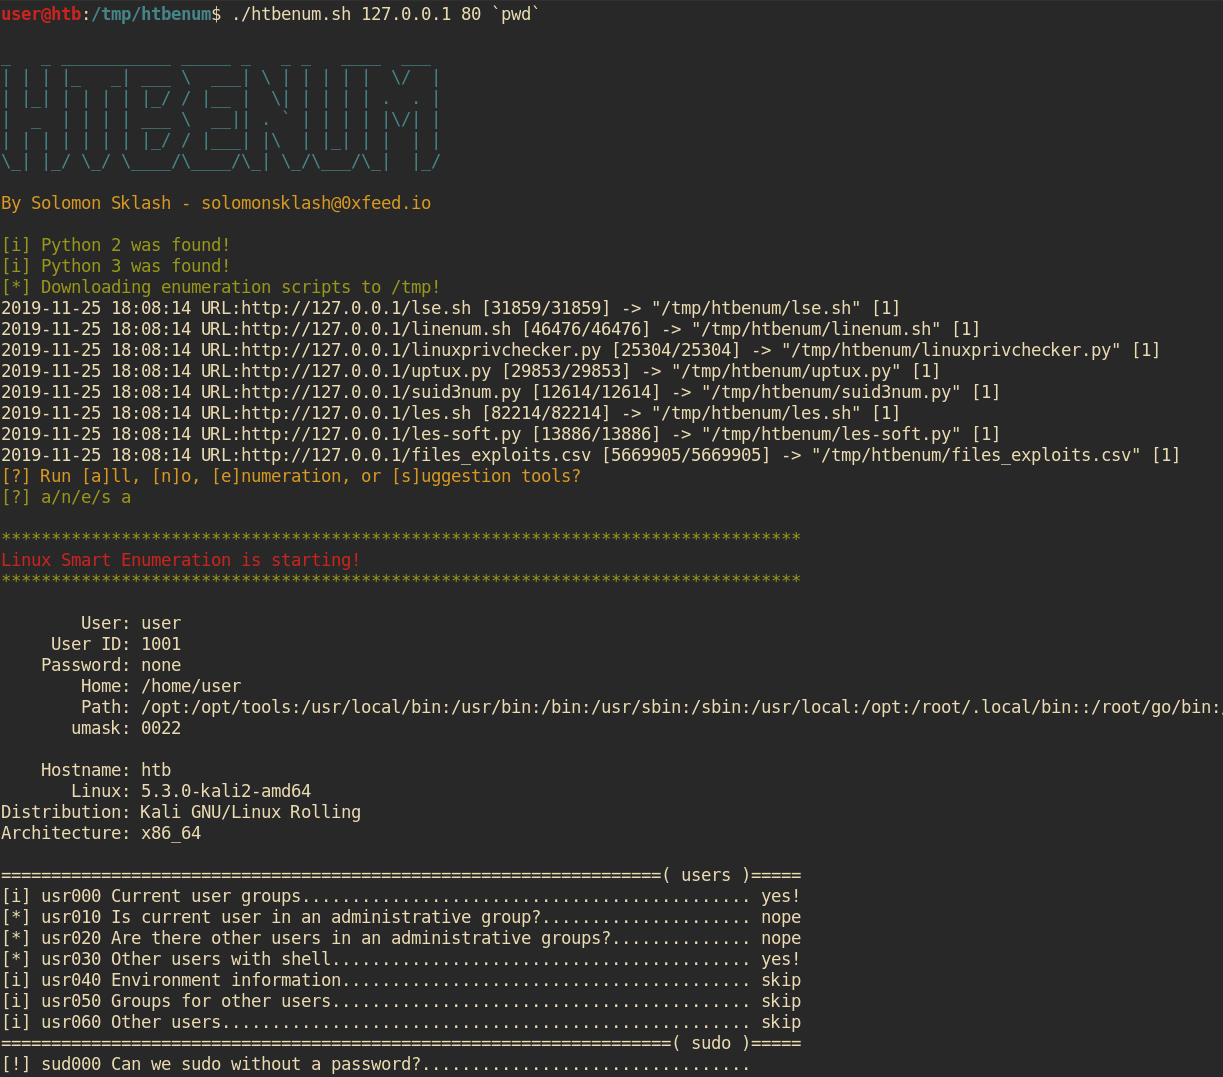 solomonsklash/htbenum
A Linux enumeration script for Hack The Box
 nvisosecurity/pycobalthound
pyCobaltHound is an Aggressor script extension for Cobalt Strike which aims to provide a deep integration between Cobalt Strike and Bloodhound.
 nicolas-carolo/houndsploit
An advanced graphical search engine for Exploit-DB
 shizzz477/msploitego
Pentesting suite for Maltego based on data in a Metasploit database