Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
33 results
react2shell-burp preview

react2shell-burp

GitHubj0lt-github/react2shell-burp

Burp Suite extension for detecting CVE-2025-55182 (React2Shell) unsafe deserialization vulnerability. Features safe digest check, PoC redirect mode,…

exploitationinformation-gatheringpenetration-testing+4
1
2 months ago
mongobleedburp preview

mongobleedburp

GitHubj0lt-github/mongobleedburp

Burp Suite extension to detect CVE-2025-14847 (MongoBleed) via manual leak tests from a dedicated UI tab.

data-exfiltrationexploitationinformation-gathering+3
2 months ago
ParaForge preview

ParaForge

GitHubanof-cyber/paraforge

A BurpSuite extension to create a custom word-list of endpoint and parameters for enumeration and fuzzing

fuzzinginformation-gatheringpenetration-testing+1
1423 years ago
rep-chrome preview

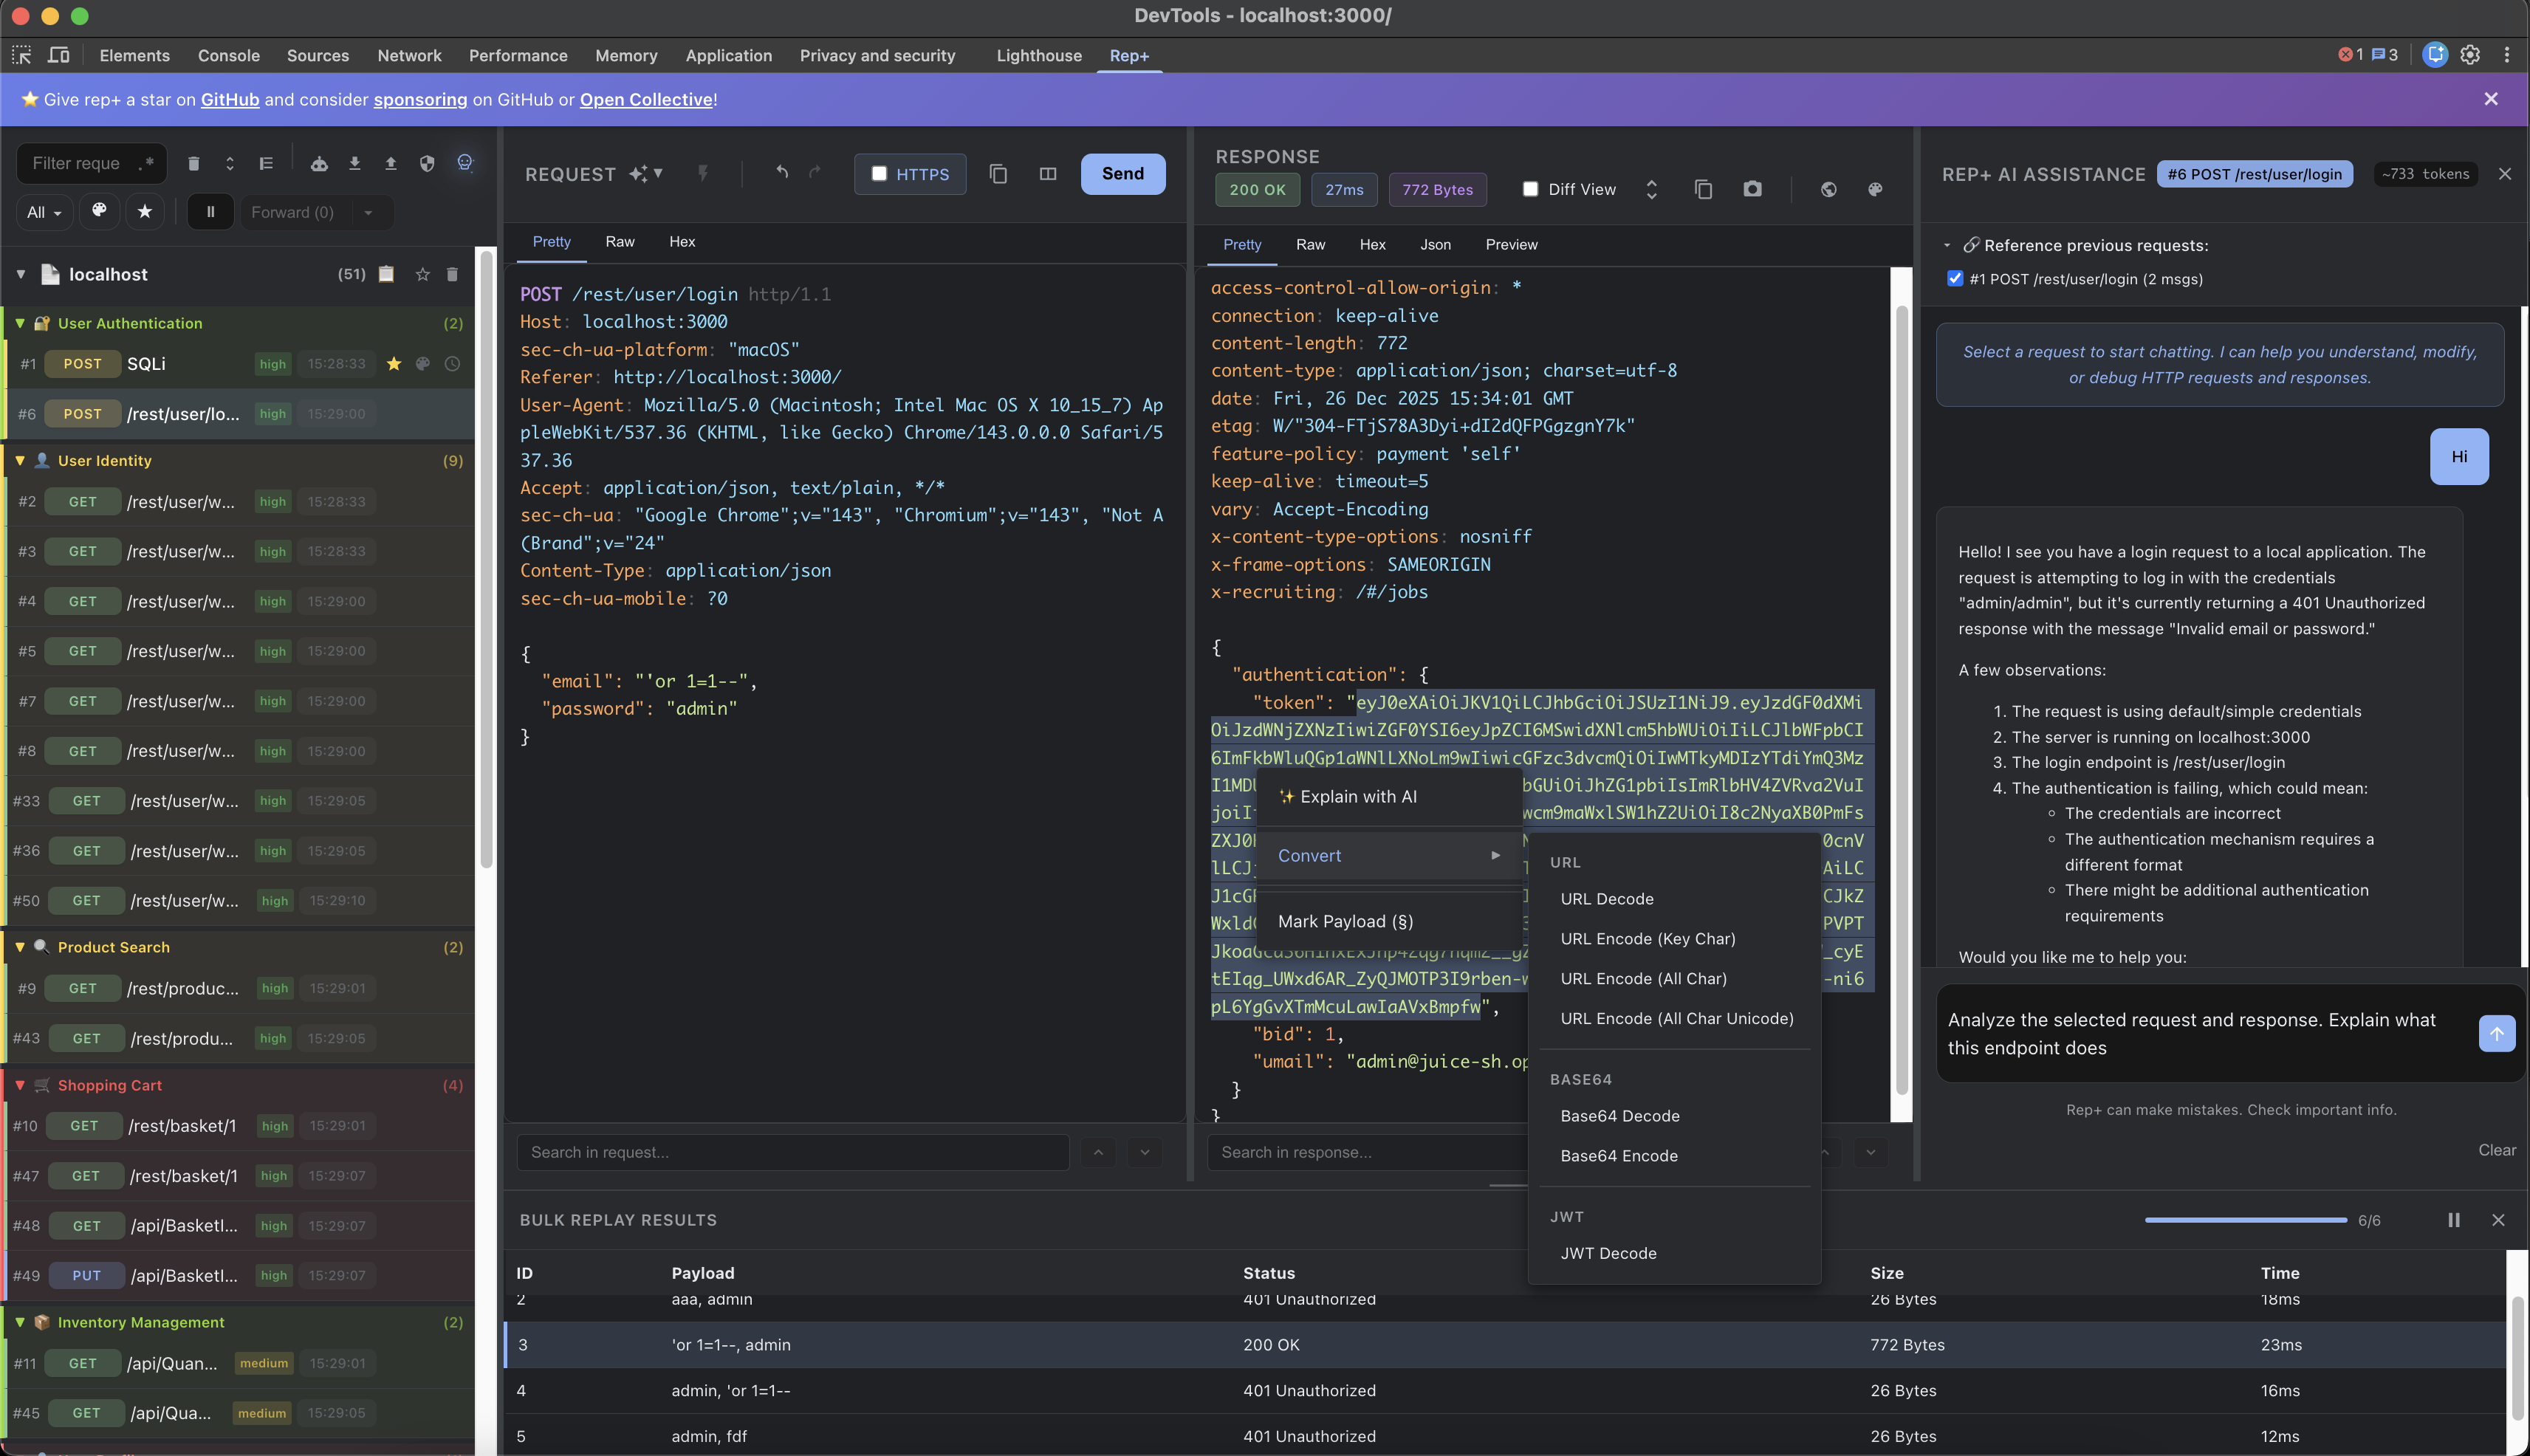
rep-chrome

GitHubrepplus/rep-chrome

rep+ — Burp-style HTTP Repeater for Chrome DevTools with built‑in AI to explain requests and suggest attacks

ai-securityapi-security-testingfuzzing+6
1.6k8 months ago
JS-Tap preview

JS-Tap

GitHubhoodoer/js-tap

JavaScript beacons and C2 to be used for XSS payload or post exploitation implants on webapp servers or desktop software to monitor users and…

command-and-controldata-exfiltrationinformation-gathering+8
4772 months ago
neo preview

neo

GitHub4ier/neo

Turn any web app into an API. Chrome extension captures browser traffic, auto-generates schemas, lets AI replay APIs directly. No official API needed.

ai-securityapi-securitycrawler+8
7565 months ago
XnlReveal preview

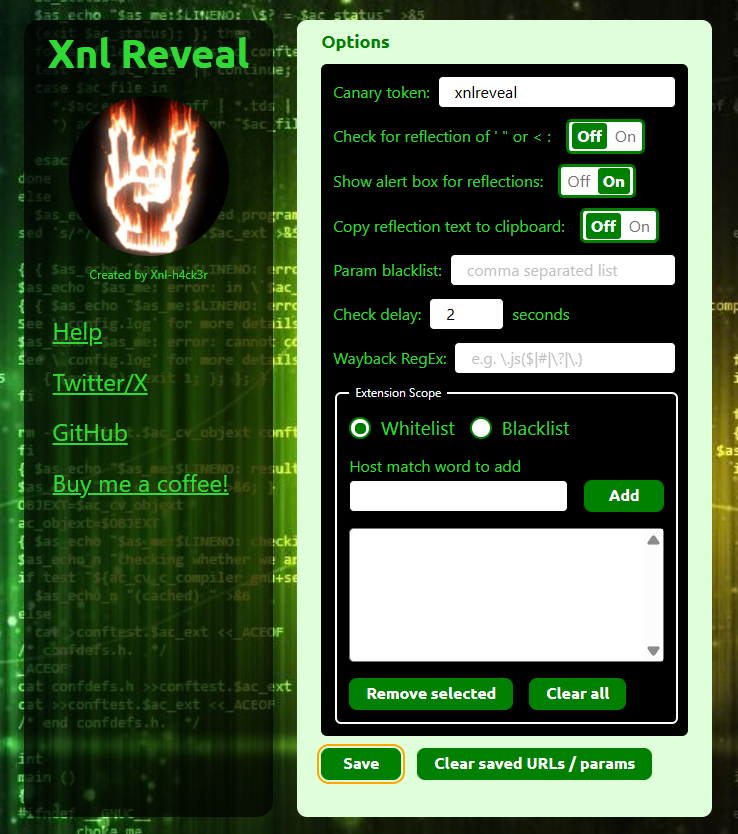
XnlReveal

GitHubxnl-h4ck3r/xnlreveal

A Chrome/Firefox browser extension to show alerts for reflected query params, show Wayback archive links for the current path, show hidden elements…

information-gatheringosintpenetration-testing+3
4545 months ago
posta preview

posta

GitHubbenso-io/posta

Browser extension for tracking, inspecting, and exploiting cross-document postMessage vulnerabilities with replay and cross-origin exploit simulation…

information-gatheringpenetration-testingweb-application-exploitation+1
3093 years ago
extloader preview

extloader

GitHubsynacktiv/extloader

A chromium extension exploitation toolkit

exploitationinformation-gatheringpenetration-testing+4
2711 months ago
CVE-2025-55182-Exploiter preview

CVE-2025-55182-Exploiter

GitHubalfazhossain/cve-2025-55182-exploiter

CVE-2025-55182-Exploiter Google Chrome Extension. nextjs vulnerability #nextjscve

exploitationinformation-gatheringpenetration-testing+3
49 months ago
CVE-2026-66491 preview

CVE-2026-66491

GitHubtoanln-cov/cve-2026-66491

The Joomla extension PhocaCommander is vulnerable to Path Traversal in the getSource function - CVSS 8.2

exploitationinformation-gatheringpenetration-testing+3
1 month ago
CVE-2024-5736 preview

CVE-2024-5736

GitHubafine-com/cve-2024-5736

AdmirorFrames Joomla! Extension < 5.0 - Server-Side Request Forgery

information-gatheringpenetration-testingvulnerability-analysis+2
2 years ago
CVE-2026-56096 preview

CVE-2026-56096

GitHubyairhinkis/cve-2026-56096

Proof of concept and technical write-up for CVE-2026-56096, a blind Solr query injection in TYPO3 EXT:solr enabling unauthenticated field enumeration…

exploitationinformation-gatheringpapers-research+3
9 days ago
CVE-2023-50072 preview

CVE-2023-50072

GitHubahrixia/cve-2023-50072

A stored cross-site scripting (XSS) vulnerability exists in OpenKM version 7.1.40.

exploitationinformation-gatheringpenetration-testing+2
42 years ago
CVE-2026-65891 preview

CVE-2026-65891

GitHubmurrez/cve-2026-65891

CVE-2026-65891 PoC — Joomla Content Editor file rename vulnerability (auth required, fixed in JCE 2.20.2)

exploitationinformation-gatheringpenetration-testing+4
1 month ago
Previous12Next