
XSS2Shell
 g0d150ne/xss2shell
Exploits WordPress pre-auth XSS (CVE-2026-64638) to achieve remote code execution, installing an AES-encrypted backdoor webshell with persistence,…
command-and-controlexploitationinformation-gathering+6
2
g0d150ne/xss2shellExploits WordPress pre-auth XSS (CVE-2026-64638) to achieve remote code execution, installing an AES-encrypted backdoor webshell with persistence,…
 mohammad-008/rsfiles-cve-2026-57827
Unauthenticated File Upload → RCE PoC for CVE-2026-57827 (RSFiles! Joomla < 1.17.12). Authorized security research use only.
 shinthink/cve-2026-57827
CVE-2026-57827 — RSFiles! Joomla Component Unauthenticated File Upload RCE. Split-controller upload bypass. CVSS 9.8 | CWE-434 | com_rsfiles < 1.17.12
 nxploited/cve-2026-10818
WPForms Pro <= 1.10.1.1 - Unauthenticated Arbitrary File Write via Chunked Upload Init/Finalize Ordering
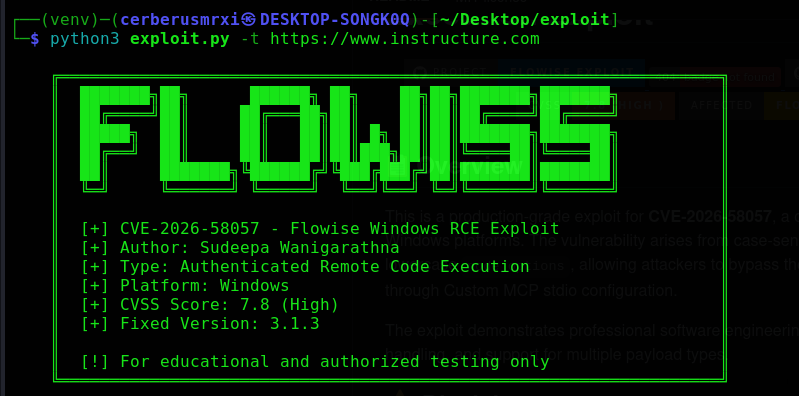 cerberusmrxi/flowise-cve-2026-58057-exploit
Flowise Windows RCE exploit for CVE-2026-58057. Bypasses environment variable validation via case-sensitive flaw. Uses node_options to inject…
 shinthink/cve-2026-14894
Super Forms Unauthenticated File Upload RCE | CVSS 9.8
 madexploits/ninja-form-exploit
CVE-2026-0740
 0xdenis77/cve-2026-56291
Mendeteksi versi (passive detection) & Exploitation CVE POC
 caterscam/cve-2026-5524-poc
Mass exploit toolkit for CVE-2026-5524, an unauthenticated file upload RCE in Divi Form Builder. Features multi-threaded scanning, WAF bypass…
 iicaicai/cve-2026-5524-poc
Python mass-exploit toolkit for CVE-2026-5524, an unauthenticated file upload RCE in the WordPress Divi Form Builder plugin, with webshell upload and…
 ayiezola/cve-2026-48908
Unauthenticated RCE PoC for CVE-2026-48908 SP Page Builder (Joomla) arbitrary file upload and remote code execution exploit with mass scaning…
 xmyronn/cve-2026-11344-rce
Unauthenticated remote code execution exploit for Vehicle Management System in PHP via unrestricted file upload in newdriver.php and newvehicle.php,…
 groppoxx/cve-2023-2825-poc
PoC for CVE-2023-2825: automated GitLab 16.0.0 arbitrary file read via nested public groups, project upload traversal, reusable upload paths, and…
 pescada-dev/cve-2025-61506
Unrestricted File Upload DoS Vulnerability discovered in MediaCrush thru 1.0.1(CVE-2025-61506)
 nxgn-kd01/smartermail-cve-scanner
CVE-2025-52691 Scanner - Detects vulnerable SmarterMail installations (CVSS 10.0 RCE)
 abrewer251/cve-2020-1938_ghostcat-poc
Apache Tomcat AJP Ghostcat (CVE-2020-1938) exploit tool for file disclosure with multi-target scanning, custom wordlists, and upload point detection…
 amirqusairy99/wordpress-file-upload-4.24.11---unauthenticated-path-traversal
Python-based tool to detect and exploit arbitrary file read vulnerability in WordPress WP File Upload plugin (<=4.24.11), enabling unauthenticated…
