

feroxbuster
 epi052/feroxbuster
A fast, simple, recursive content discovery tool written in Rust.
api-securityapi-security-testingcrawler+8
epi052/feroxbusterA fast, simple, recursive content discovery tool written in Rust.
 redteambrasil/cve-2020-24029
Detailed disclosure of an unauthenticated password change vulnerability in ForLogic Qualiex v1 and v3, enabling remote privilege escalation and…
 coolkiee/cve-2019-9053
Python exploit for CVE-2019-9053 targeting SQL injection in CMS Made Simple, enabling automated time-based blind injection and credential extraction.
 jeanback1/cve-2019-9053-exploit
Automated exploit for CVE-2019-9053, a time-based blind SQL injection in CMS Made Simple ≤2.2.9. Extracts admin credentials (username, email,…
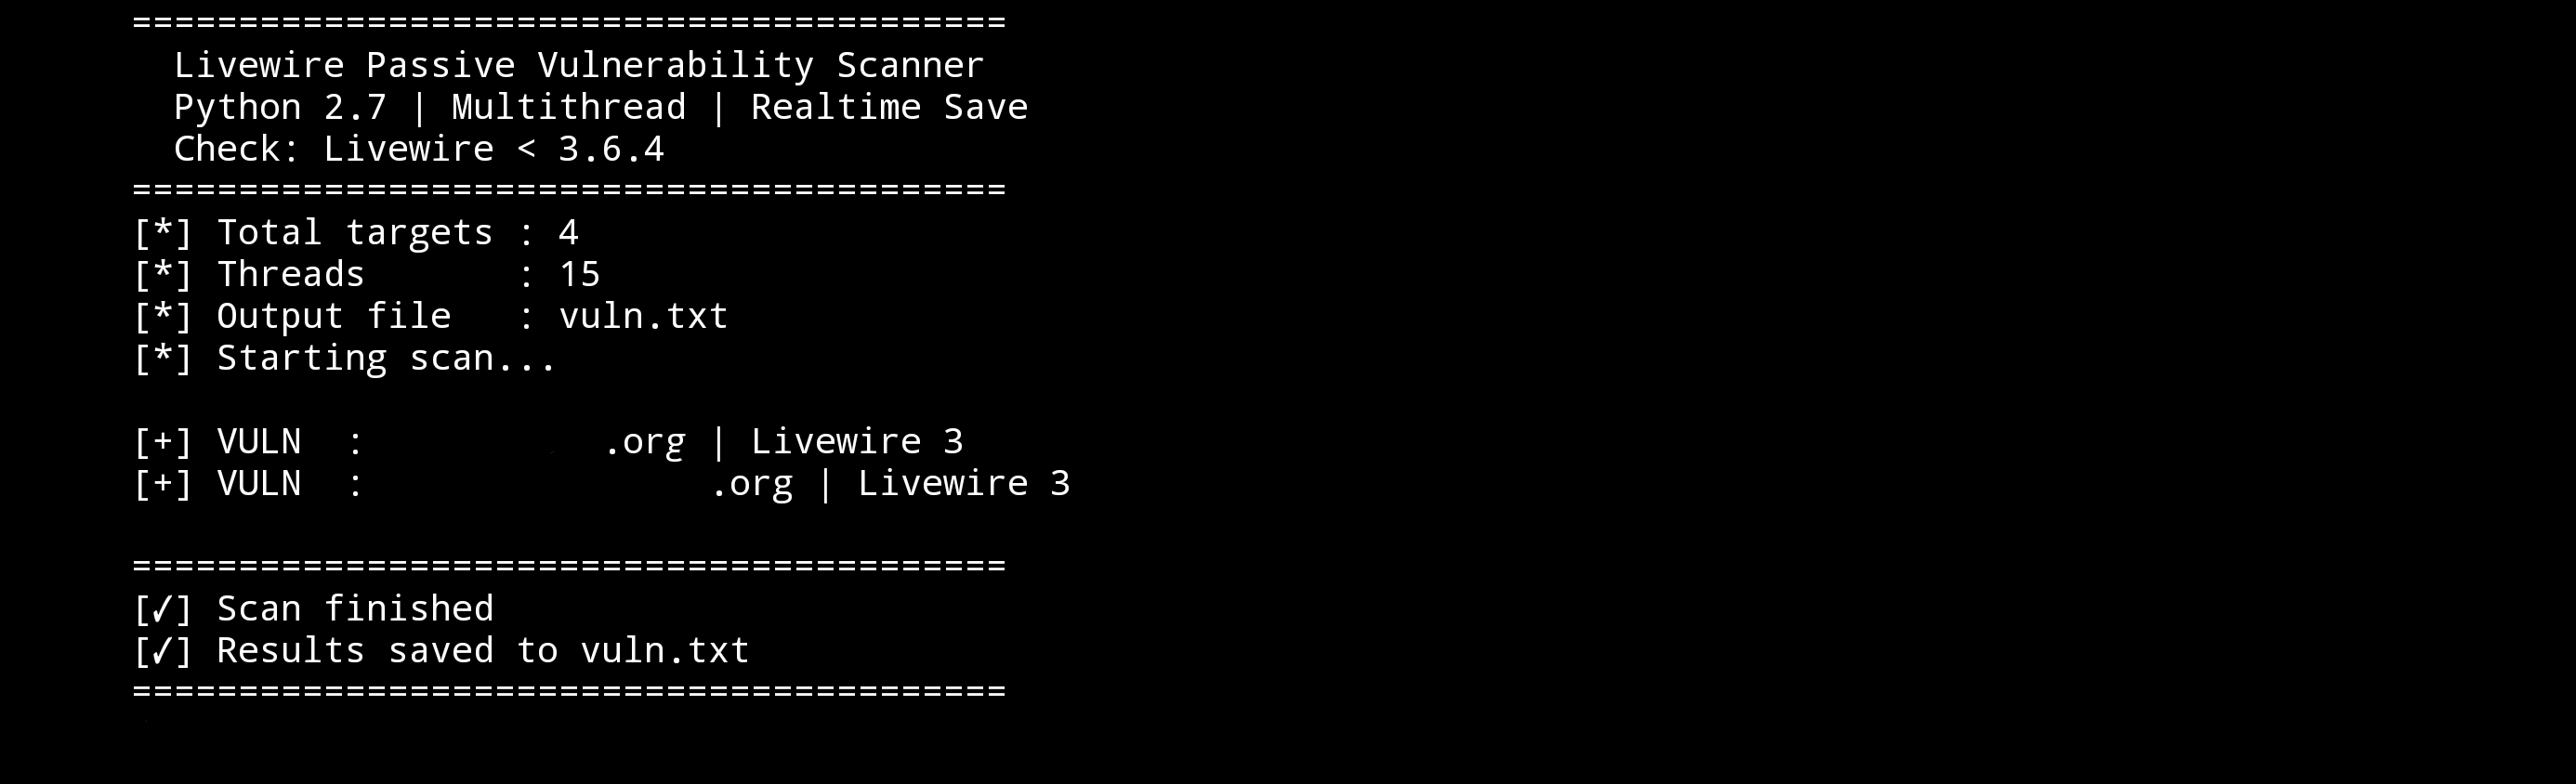 jenderal92/livewire-vuln-scanner
Simple scanner to detect vulnerable Livewire installations.
 v4rr10r/cve-2019-9053
CMS Made Simple CVE-2019-9053 Exploit (Python 3)
 jyothsna-git007/cms-made-simple-2.2.10---sql-injection
Google Dork-based scanner for detecting CVE-2019-9053 SQL injection in CMS Made Simple < 2.2.10. Designed for security auditing and patch…
 killukeren/-cve-2019-9053
Python exploit script for CVE-2019-9053 targeting CMS Simple. Automates vulnerability exploitation and information gathering for penetration testing…
 nxploited/cve-2025-53580
WordPress Simple Business Directory Pro Plugin < 15.6.9 is vulnerable to a high priority Privilege Escalation
 caybermods/cve-2026-22812-poc
Python tool to check and exploit CVE-2026-22812 in OpenCode, supporting command execution, file read, and multi-target scanning on ports 4095-4100.
 jmehta10/cve-2025-66470
A fast, simple scanner for detecting CVE-2025-66470 - XSS vulnerability in NiceGUI's ui.interactive_image component.
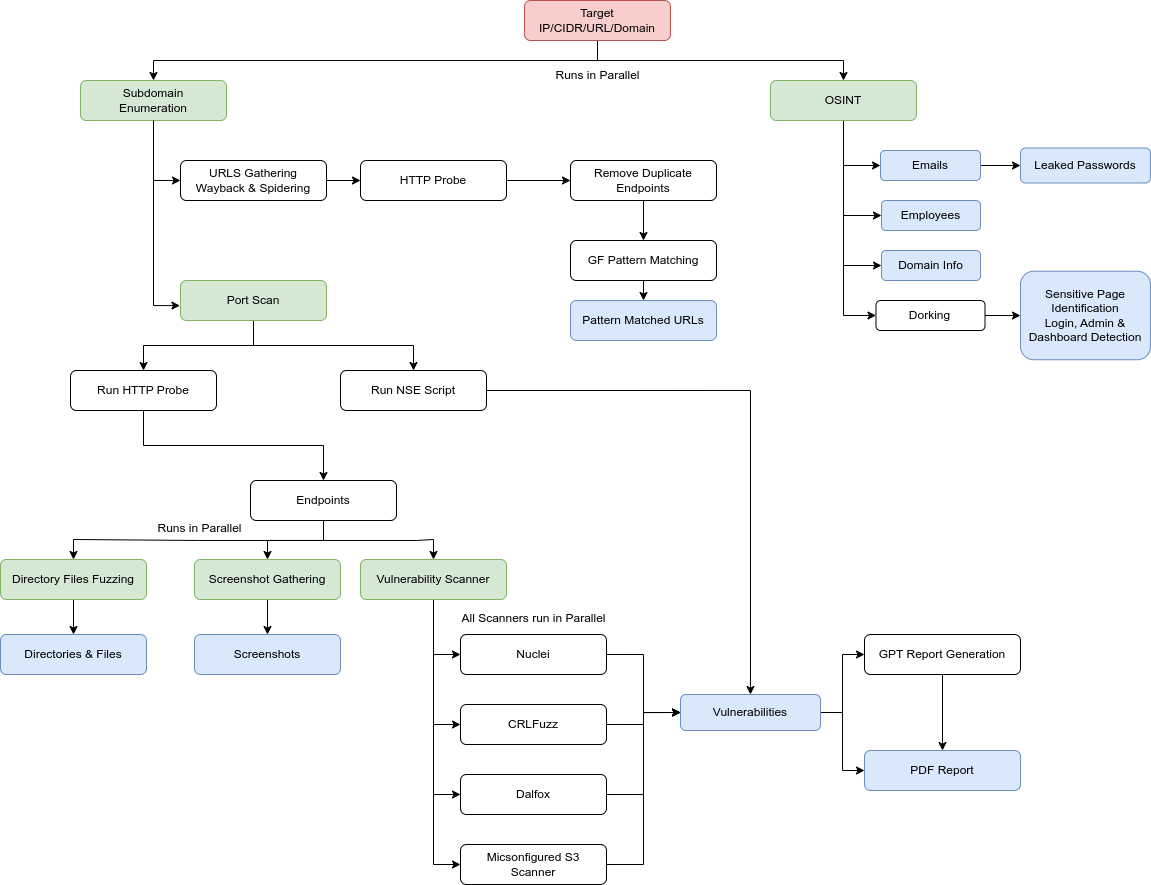 yogeshojha/rengine
reNgine is an automated reconnaissance framework for web applications with a focus on highly configurable streamlined recon process via Engines,…
 6h4ack/cve-2025-12101-checker
Simple Python PoC to check Citrix NetScaler ADC/Gateway for CVE-2025-12101 reflected XSS on /cgi/logout using a crafted SAMLResponse + RelayState…
 hlc23/cve-2024-5932-web-ui
Python-based exploit for CVE-2024-5932 targeting a web UI vulnerability. Provides a simple script to demonstrate and test the security flaw.
 artemy-ccrsky/cve-2024-39211
User Enumeration vulnerability in Kaiten (workflow management system)
 kalidas-7/cve-2019-9053
Unauthenticated time-based blind SQL injection exploit for CMS Made Simple <= 2.2.9. Extracts admin credentials and optionally cracks password hashes…
 x3rx3ssec/cve-2022-0169
CVE-2022-0169 - WordPress Photo Gallery SQLi PoC
 ademto/wordpress-cve-2024-10924-pentest
Penetration testing report and exploit for CVE-2024-10924, a 2FA bypass in Really Simple SSL, including reconnaissance, exploitation, and remediation…