

EntraTrace
 bert-janp/entratrace
Defensive research tool that documents observable API endpoints and user agents of offensive tooling targeting Microsoft Entra ID, supporting…
authenticationcloud-securitydefensive-tools+5
122
bert-janp/entratraceDefensive research tool that documents observable API endpoints and user agents of offensive tooling targeting Microsoft Entra ID, supporting…
 n3rada/mssqland
In-target C# post-exploitation and exploitation tool for Microsoft SQL Server (MS SQL / MSSQL) traversing linked-server chains of any depth with…
 bitsadmin/wesng
Windows Exploit Suggester - Next Generation
 microsoft/msticpy
Microsoft Threat Intelligence Security Tools
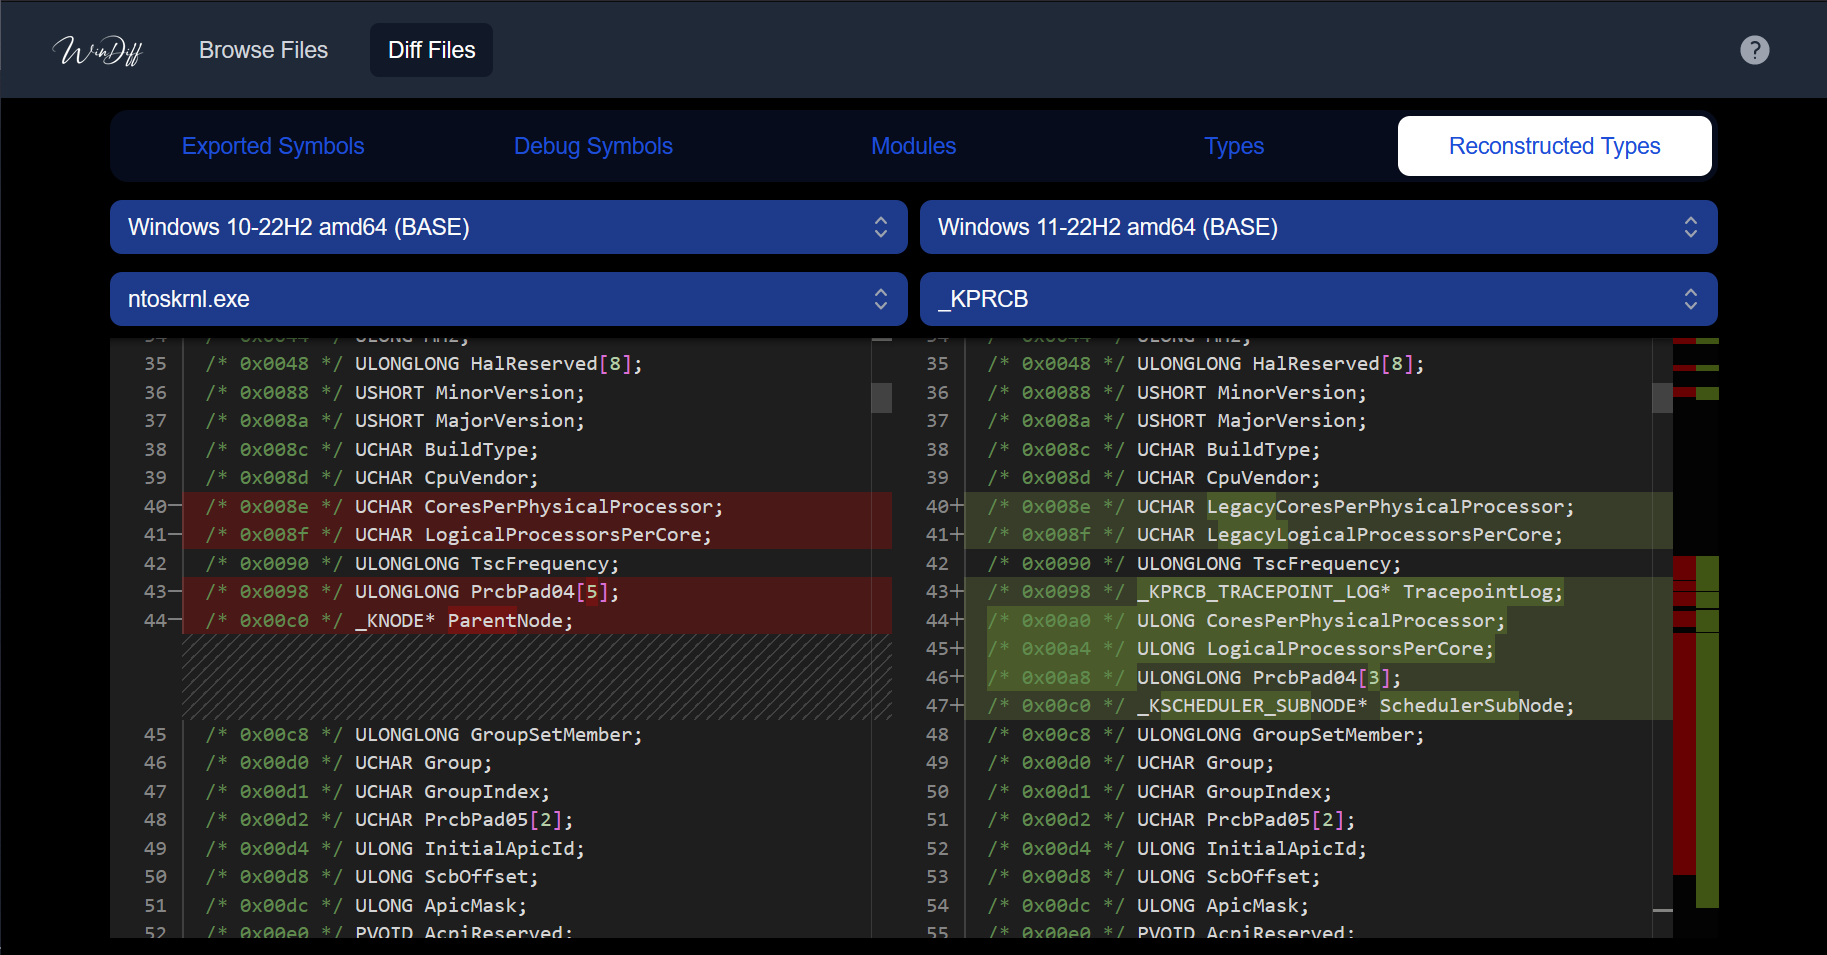 ergrelet/windiff
Tool that allows comparing symbol, type and syscall information of Microsoft Windows binaries across different versions of the OS, using a Web UI…
 garrettfoster13/sccmhunter
Post-exploitation tool for identifying, profiling, and attacking Microsoft SCCM assets within Active Directory domains, streamlining credential…
 a2awais/threat-hunting
Curated collection of threat hunting and detection queries for CrowdStrike Falcon (CQL) and Microsoft Defender XDR (KQL), mapped to MITRE ATT&CK…
 blacklanternsecurity/offensive-azure
Collection of offensive tools targeting Microsoft Azure
 mr-un1k0d3r/azureredops
Azure RedOps is a offensive security toolkit for assessing the security posture of Microsoft Entra ID
 dfir-orc/dfir-orc
Forensics artefact collection tool for systems running Microsoft Windows
 redbyte1337/credspy
Entra ID user enumeration and auth method discovery via the public GetCredentialType API
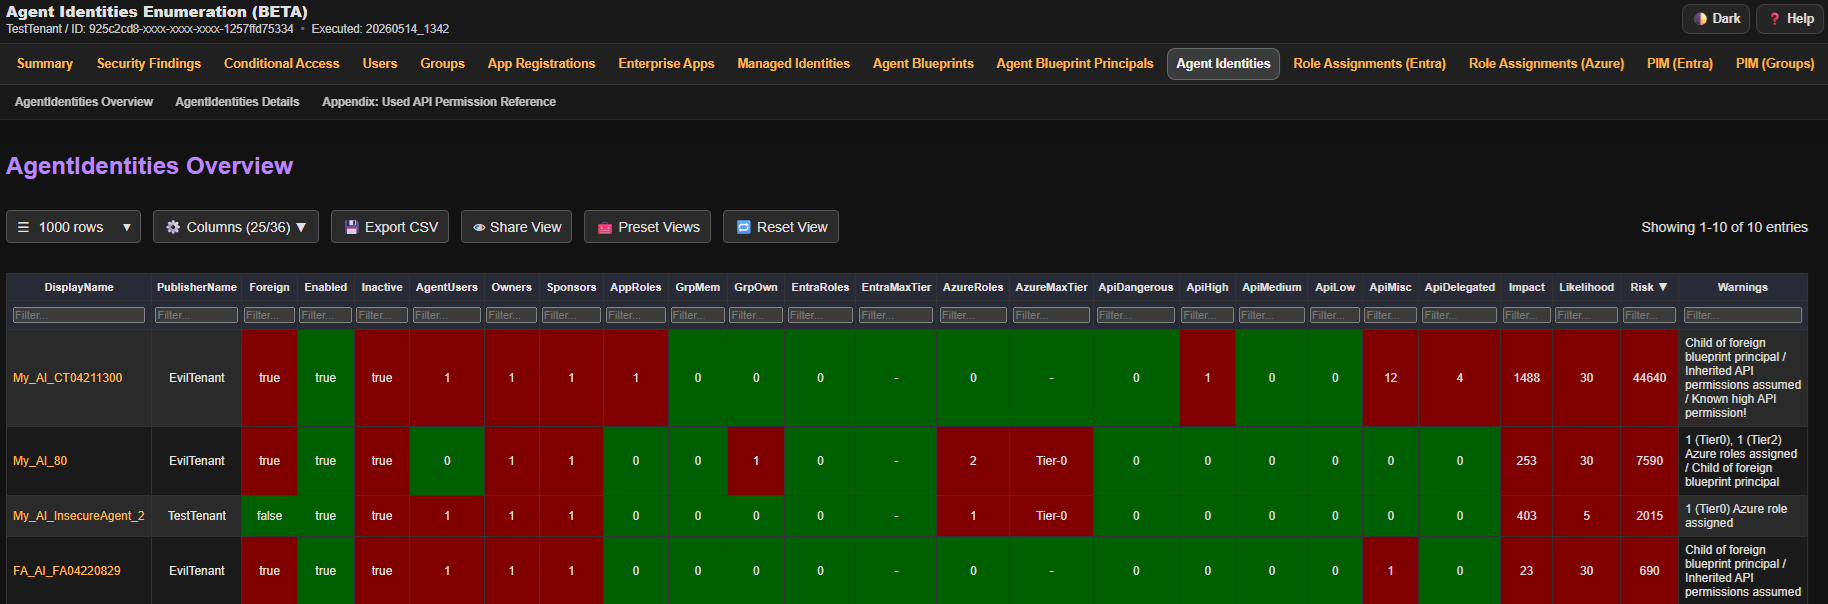 compasssecurity/entrafalcon
A lightweight PowerShell tool for assessing the security posture of Microsoft Entra ID environments. It helps identify privileged objects, risky…
 hac01/azure-pentesting-suite
Go toolkit for authorized Azure security assessments: enumerates subscriptions and resources, audits misconfigurations, and attacks public Blob…
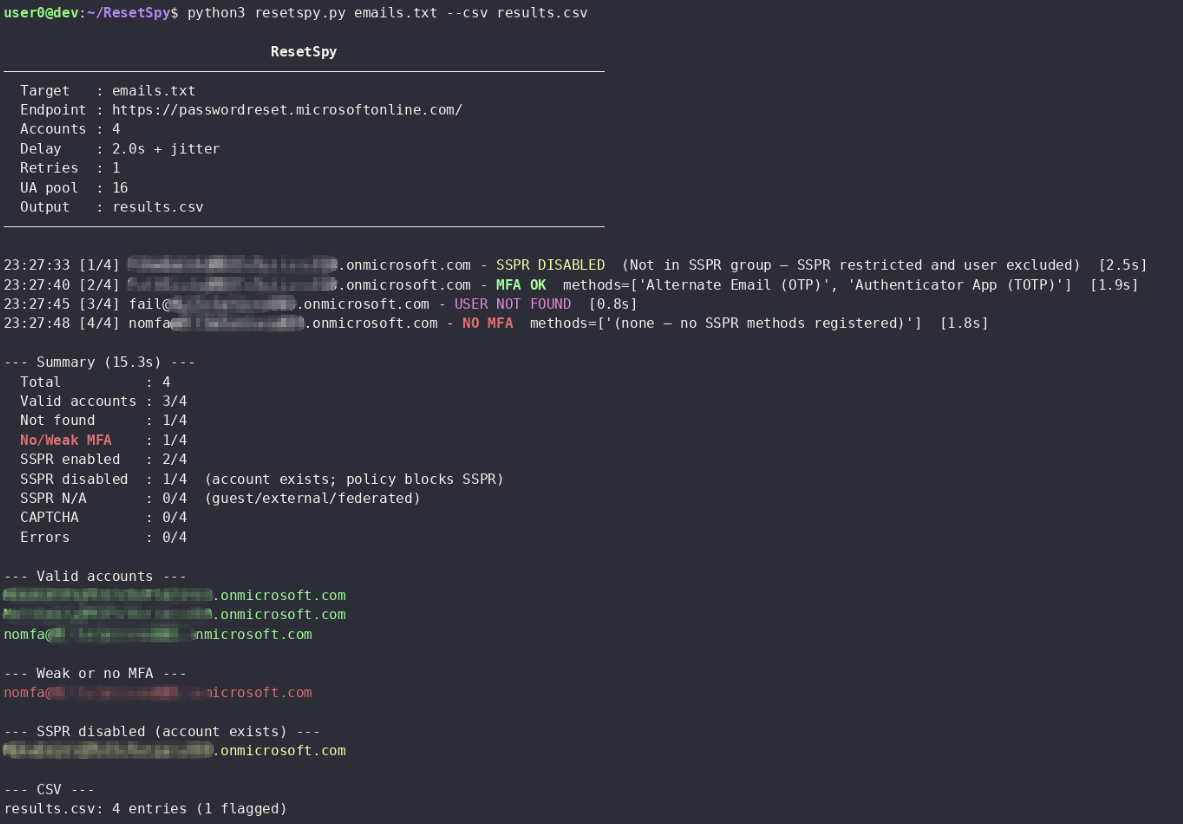 mlcsec/resetspy
Enumerate user accounts and registered authentication methods via the Microsoft Self-Service Password Reset (SSPR) portal
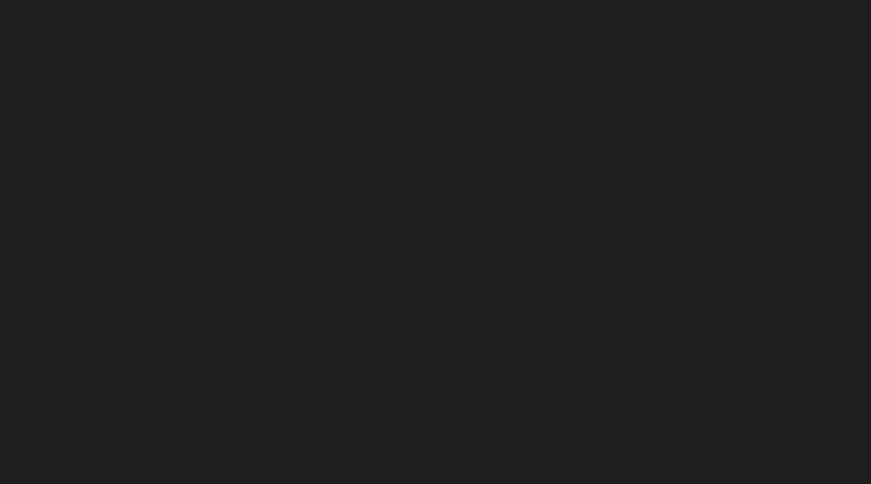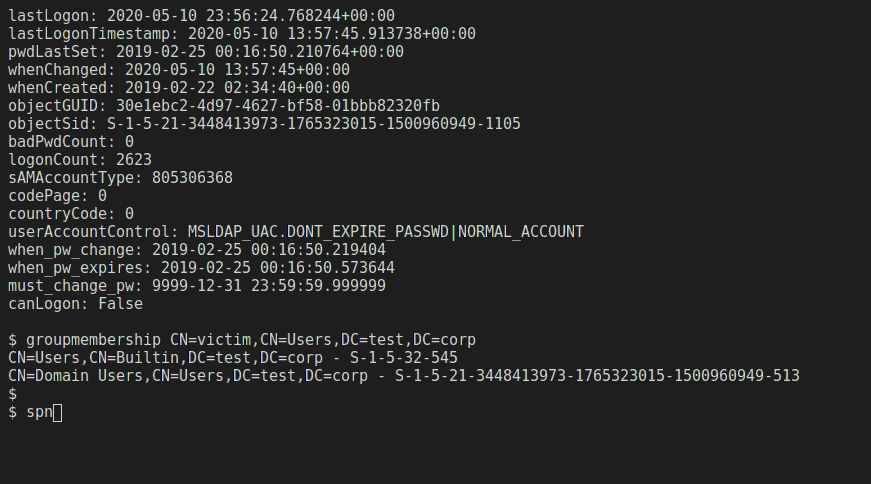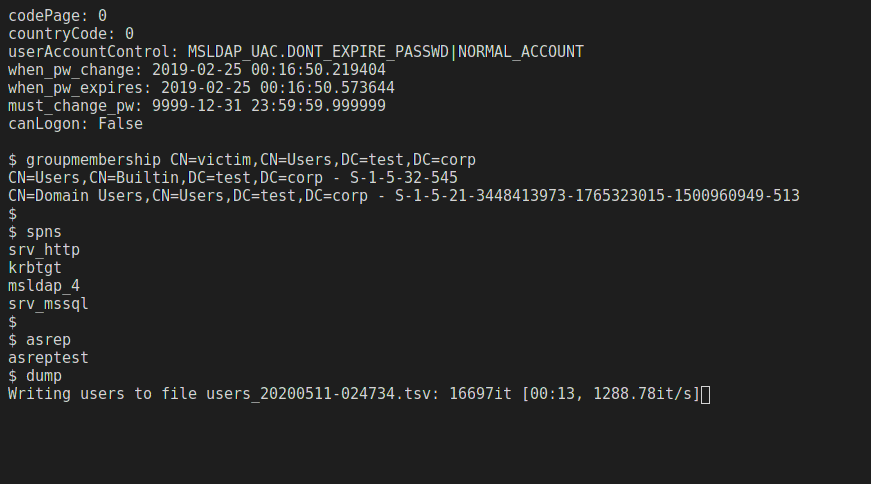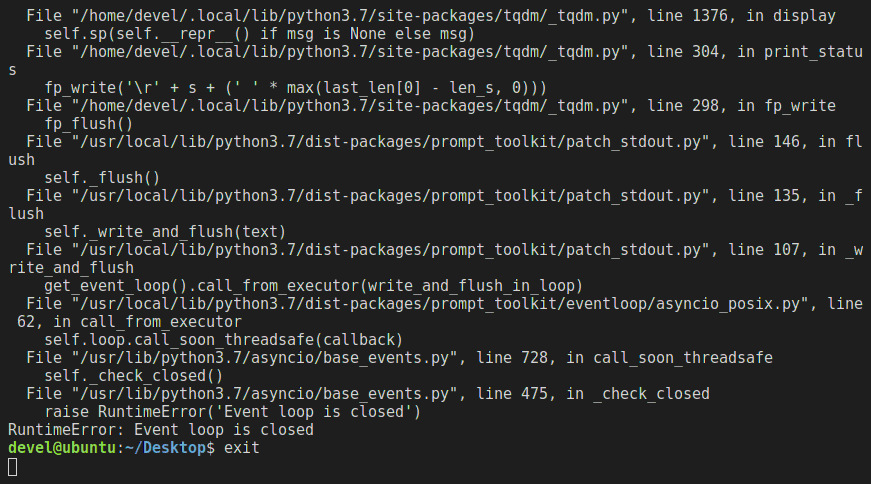 skelsec/msldap
Python library for auditing Microsoft Active Directory via LDAP, supporting NTLM, Kerberos, SSPI authentication, channel binding, encryption, and…
 virologi-info/mssharepoint-scanner
A scanner for CVE-2026-55040 and CVE-2026-63520, designed to determine whether the server is affected by these two CVEs.
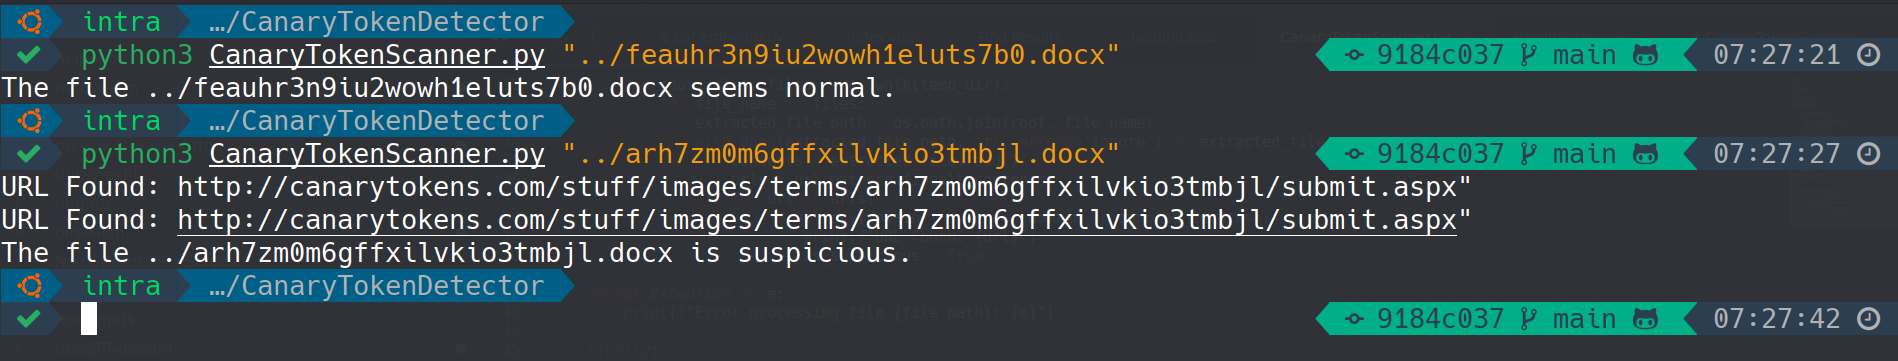 0xnslabs/canarytokenscanner
Detects CanaryTokens in Office docs and PDFs (docx, xlsx, pptx, pdf) without triggering alerts
 sfewer-r7/cve-2026-55040
Proof-of-concept exploit for Microsoft SharePoint CVE-2026-55040 that forges JWT tokens, bypasses authentication, auto-discovers metadata, and…