
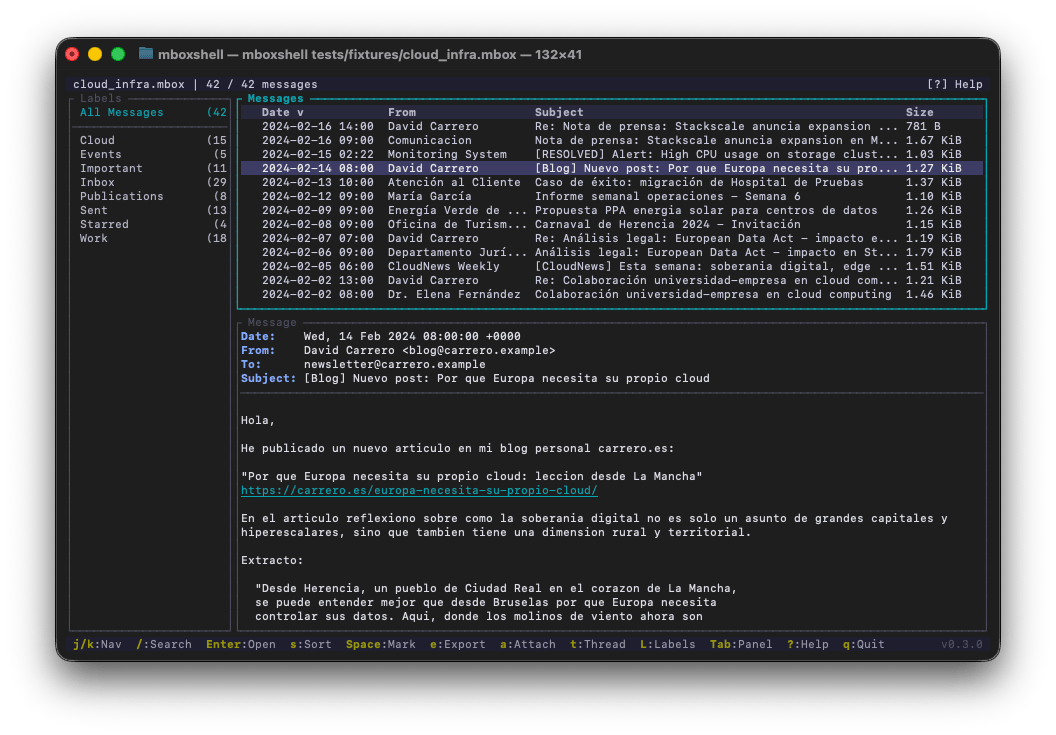
mboxshell
 dcarrero/mboxshell
mboxShell. Fast terminal viewer for MBOX files of any size. Open, search and export emails from Gmail Takeout backups (50GB+) without loading them…
data-recoverydigital-forensicsemail-security+4
dcarrero/mboxshellmboxShell. Fast terminal viewer for MBOX files of any size. Open, search and export emails from Gmail Takeout backups (50GB+) without loading them…
 kashyapghodasara/public_exploit-1--wordpress-cve-2021-29447
CVE-2021-29447 is an authenticated XML External Entity (XXE) vulnerability in WordPress
 anirbala98/cve-2025-57231
Python PoC exploit for CVE-2025-57231, an unauthenticated path traversal in Docmost < 0.22.0 that reads arbitrary files via the avatar endpoint.
 nsonaniya2010/subdomainizer
A tool to find subdomains and interesting things hidden inside, external Javascript files of page, folder, and Github.
 solivaquaant/cve-2026-85706
Proof-of-concept and reproduction lab for CVE-2026-85706, an unauthenticated path-traversal file read in GitLab CE/EE repository commits and files…
 mhtsec/cve-2026-85706
Python PoC for CVE-2026-85706, an unauthenticated path traversal in GitLab CE/EE Repository Commits API that leaks arbitrary local files via a…
 squeeze440/zotlit-poc
PoC — attachment import copies files from unapproved local paths in ZotLit (GHSA-4qh7-66xv-h329, CVE-2026-87000, CVSS 5.5).
 login-securite/donpapi
Automated remote credential dumper for Windows environments, extracting DPAPI secrets, browser credentials, certificates, and configuration files…
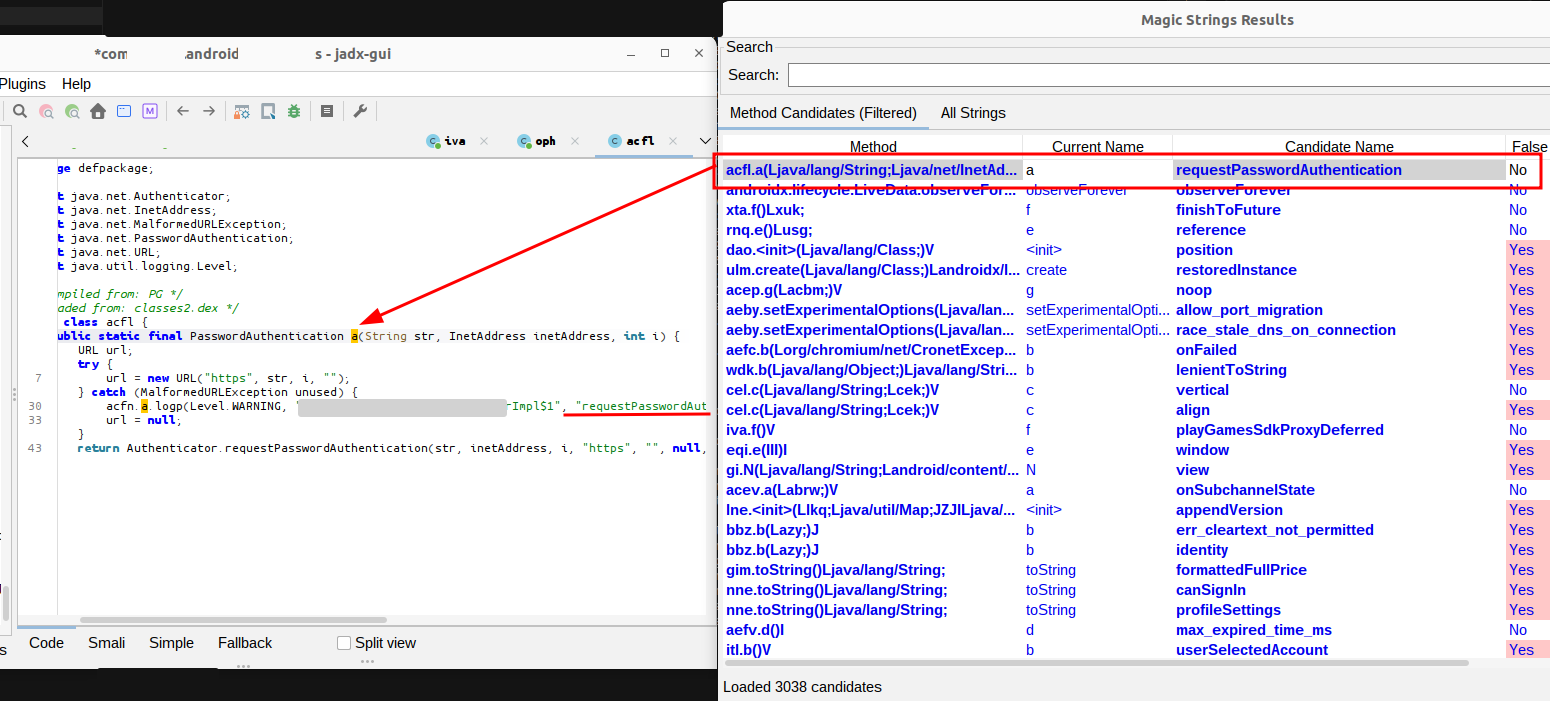 0rshemesh/jadx-magic-strings
JADX plugin that extracts method names, class references, and source file paths from string constants found in DEX files and decompiled Android code.
 0xterror/cve-2023-22047-oracle-peoplesoft-lfi
CVE-2023-22047 is a critical unauthenticated Local File Inclusion (LFI) vulnerability in Oracle PeopleSoft Enterprise PeopleTools. This exploit…
 0xterror/cve-2023-22047---oracle-peoplesoft-lfi
CVE-2023-22047 is a critical unauthenticated Local File Inclusion (LFI) vulnerability in Oracle PeopleSoft Enterprise PeopleTools. This exploit…
 sh4den/cve-2026-21858
Proof of Concept: CVE-2026-21858 is vulnerability on n8n where unauthenticated remote attackers can access sensitive files.
 jfs-jfs/cve-2026-37070
Proof-of-concept exploit for CVE-2026-37070: an authenticated attacker can read arbitrary uploaded files in Veno File Manager 4.4.9 via a crafted GET…
 webbreacher/obsidian-osint-templates
These templates are suggestions of how the Obsidian notetaking tool can be used during an OSINT investigation. The example data in those files should…
 doany1/cve-2026-24849
Proof-of-concept exploit for CVE-2026-24849, an authenticated path-traversal arbitrary file read in OpenEMR's EtherFax module. Reads server files…
 asbawy/graftraverse-cve-2021-43798
CVE-2021-43798 MiNi Exploitation Framework
 overspace-labs/caa
BurpSuite plugin for HTTP packet analysis and fuzzing dictionary generation. Extracts parameters, paths, and files from requests, counts frequency,…