
HijackLibs
 wietze/hijacklibs
Project for tracking publicly disclosed DLL Hijacking opportunities.
curated-resourceseducationinformation-gathering+3
wietze/hijacklibsProject for tracking publicly disclosed DLL Hijacking opportunities.
 ivancabrera02/whfb-pincapture
Captures Windows Hello PINs at entry by injecting a DLL into LogonUI.exe that sets a CPU hardware breakpoint on NgcSerializeConvenienceCredential,…
 outflanknl/c2-tool-collection
A collection of tools which integrate with Cobalt Strike (and possibly other C2 frameworks) through BOF and reflective DLL loading techniques.
 daddycocoaman/azbelt
AAD related enumeration in Nim
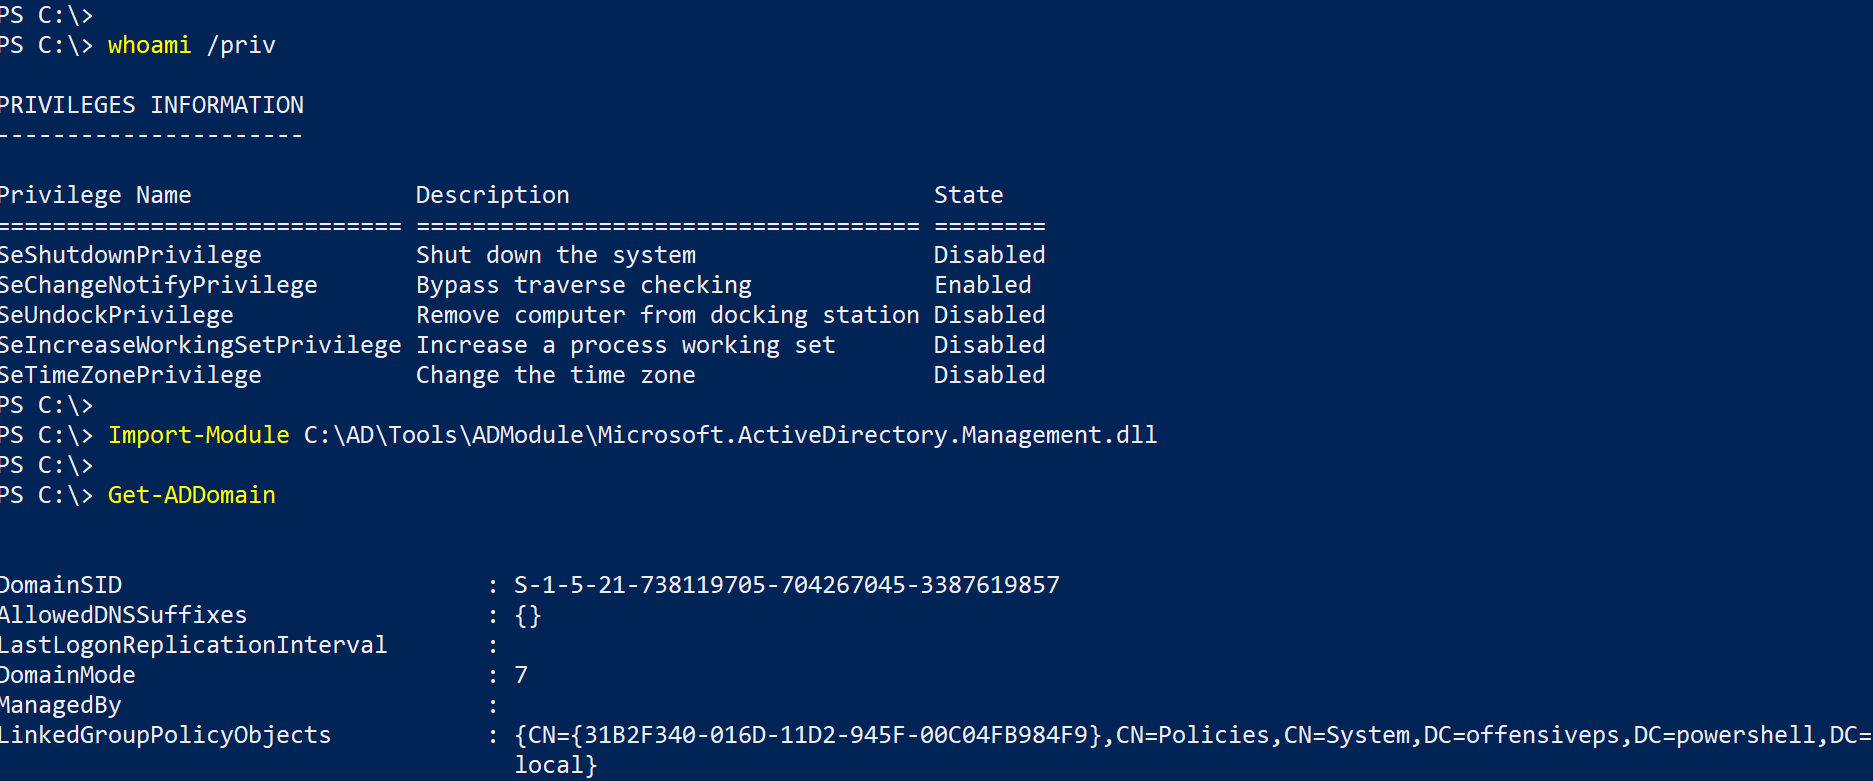 samratashok/admodule
Microsoft signed ActiveDirectory PowerShell module