
HackBrowserData
 moond4rk/hackbrowserdata
Extract and decrypt browser data, supporting multiple data types, runnable on various operating systems (macOS, Windows, Linux).
data-exfiltrationdigital-forensicsencryption-decryption-tools+4
14.5k
moond4rk/hackbrowserdataExtract and decrypt browser data, supporting multiple data types, runnable on various operating systems (macOS, Windows, Linux).
 alan-baigorria/dscanner
DScanner es una herramienta en bash que automatiza la fase de reconocimiento en auditorías de seguridad web, integrando múltiples utilidades (dig,…
 87achrafg-stack/cve-2026-48907
Exploits CVE-2025-9209 in WordPress by querying /wp-json/wp/v2/users, harvesting user keys, tokens, and cookies, bypassing Defender/Imunify360, and…
 heisenbergh4x/cve-2008-1930
CVE-2008-1930 is a critical improper authentication vulnerability affecting the core cookie integrity mechanism in WordPress version 2.5. It allows…
 maldev-academy/dumpbrowsersecrets
Extracts browser-stored data such as refresh tokens, cookies, saved credentials, credit cards, autofill entries, browsing history, and bookmarks from…
 undeadsec/socialfish
Modern dynamic phishing toolkit for authorized red team exercises. Clones login pages, captures credentials, cookies, and 2FA codes with a live…
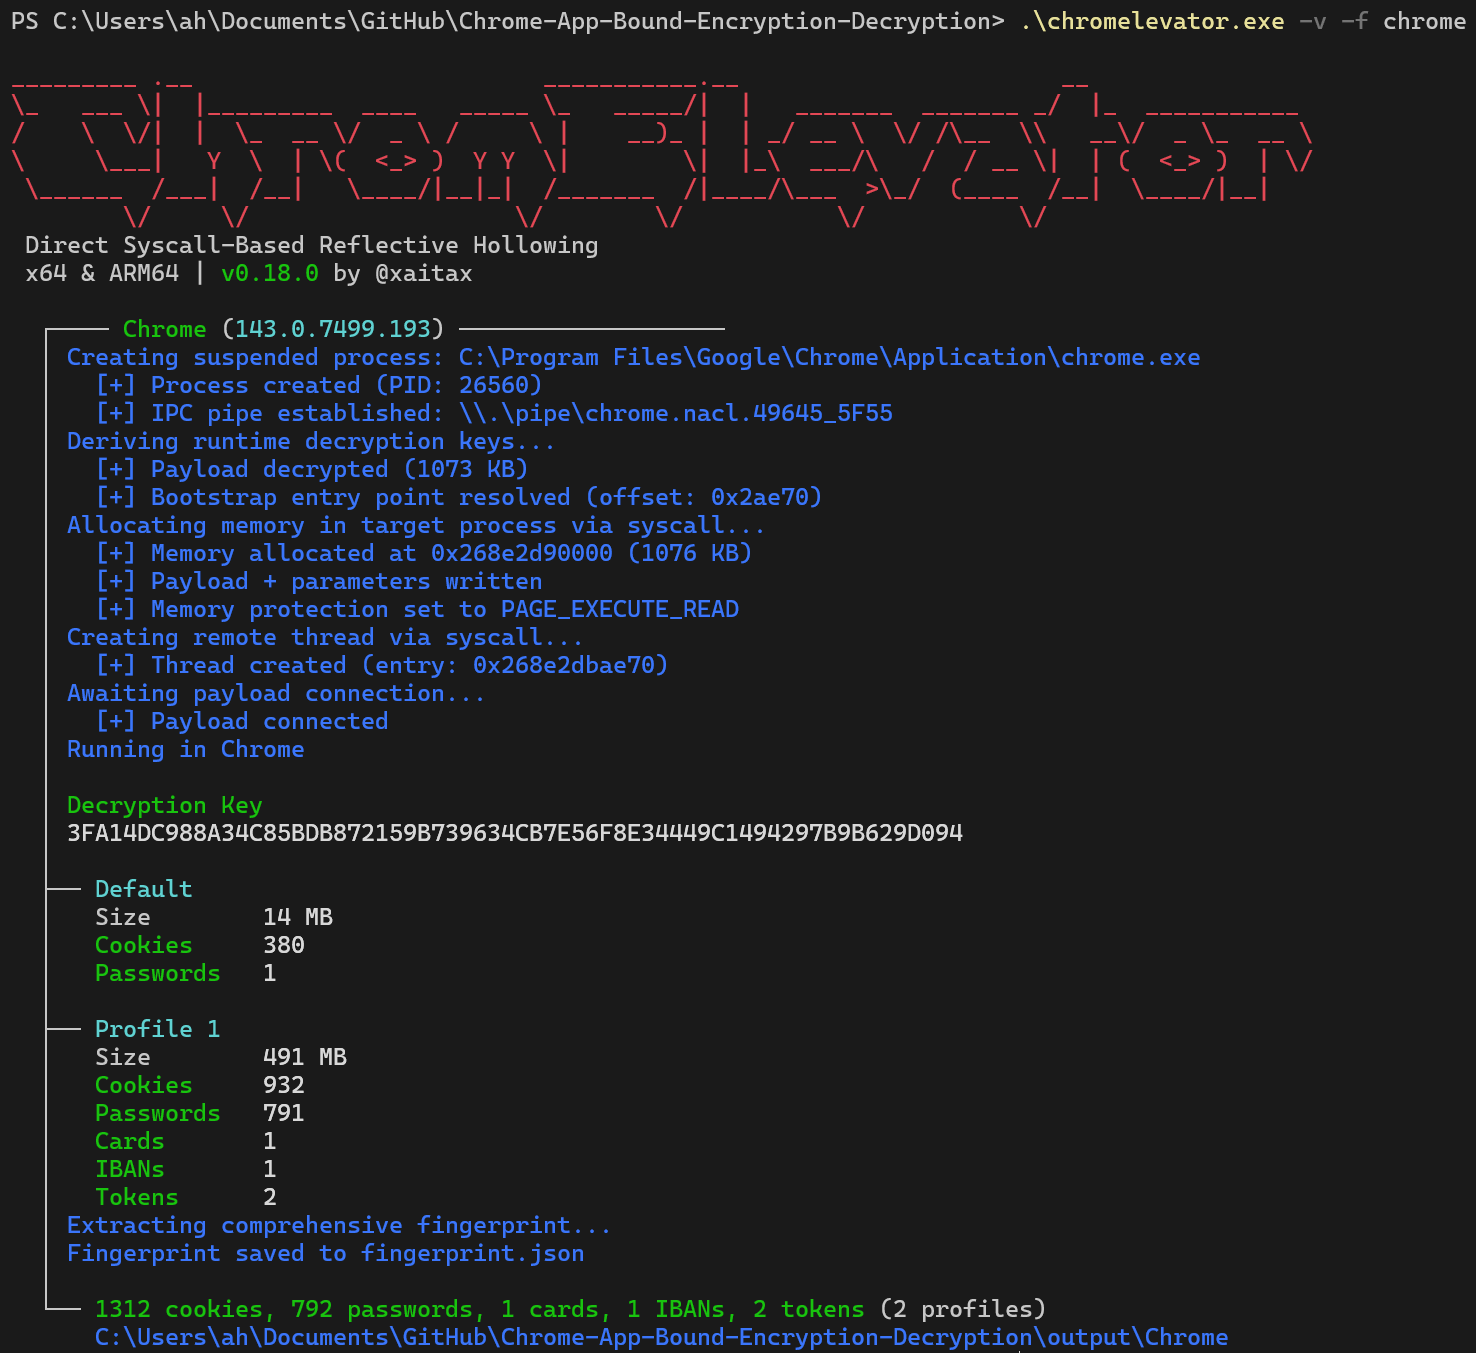 xaitax/chrome-app-bound-encryption-decryption
Bypass Chromium's App-Bound Encryption via Direct Syscall-based Reflective Process Hollowing. Extract cookies, passwords, payment methods & tokens…
 maldev-academy/dumpchromesecrets
Extract data from modern Chrome versions, including refresh tokens, cookies, saved credentials, autofill data, browsing history, and bookmarks
 d0rb/rusttlsx
🦀 Stealth HTTP client for Rust . mimics real browser TLS fingerprints for undetectable requests. Fast, type-safe, and built for precision networking.
 cybertechajju/cve-2025-5755
Asynchronous scanner and exploit tool for CVE-2025-5777 (CitrixBleed 2). Detects memory leaks in NetScaler ADC/Gateway, parses sensitive data like…
 godbadtry/cve-2025-26159
Go-based exploit script for CVE-2025-26159 that decodes, filters, and extracts cookies from Laravel applications via stored XSS payload injection.
 joelgmsec/evilnovnc
Real-time phishing platform that bypasses 2FA via a live noVNC browser session, capturing cookies, saved passwords, browsing history, and downloaded…
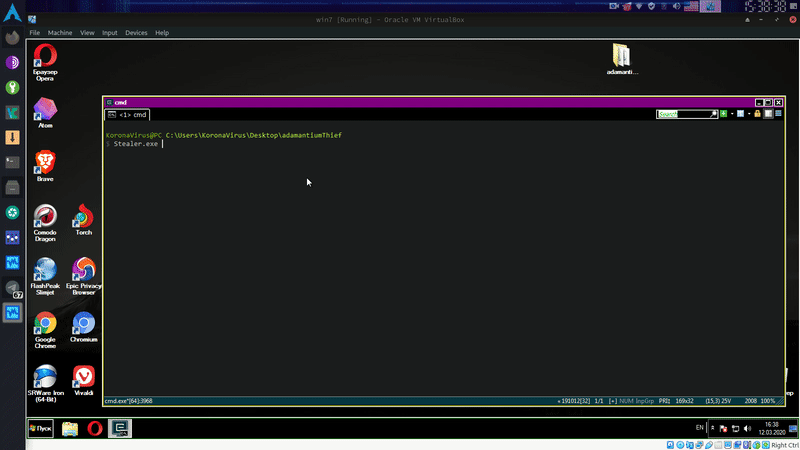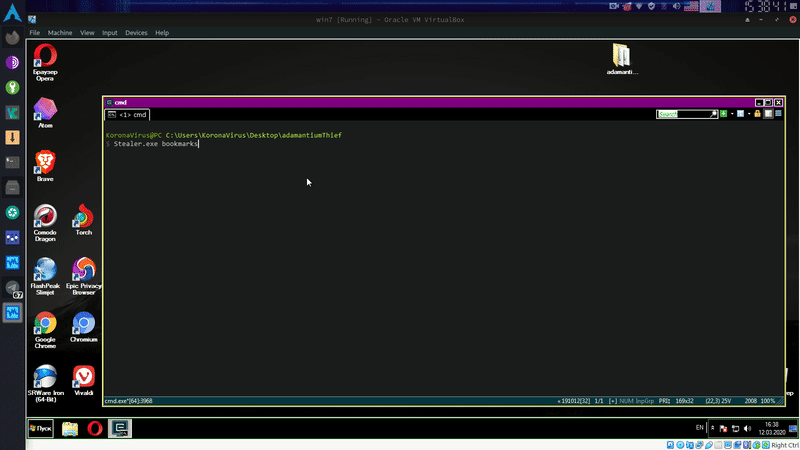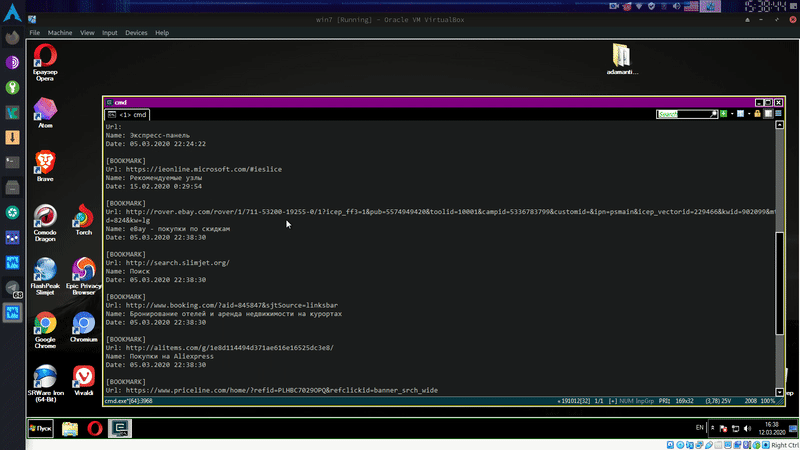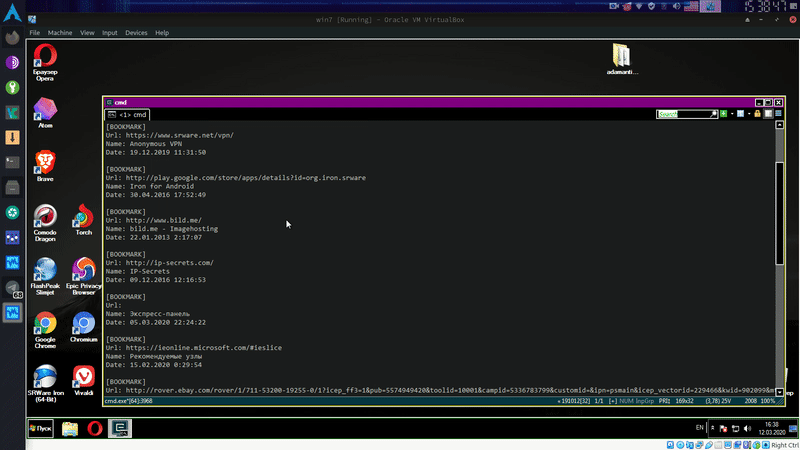 limerboy/adamantium-thief
:key: (THIS CODE IS OUTDATED FOR NEW CHROME VERSIONS) Decrypt chromium based browsers passwords, cookies, credit cards, history, bookmarks, autofill.…
 geniuszly/cve-2024-44000
is a PoC tool designed to exploit insecurely exposed debug logs from WordPress sites and extract session cookies
 rotarydrone/globalunprotect
Decrypt GlobalProtect configuration and cookie files.
 baroi-ai/cve-2024-42658
CVE-2024-42658 An issue in wishnet Nepstech Wifi Router NTPL-XPON1GFEVN v1.0 allows a remote attacker to obtain sensitive information via the cookies…
 jansen-c-moreira/cve-2024-40508
OpenPetra v.2023.02 CVE-2024-40508
 ahrixia/cve-2023-45542
mooSocial v3.1.8 is vulnerable to cross-site scripting on search function.