
CVE-2021-42013
 mauricelambert/cve-2021-42013
Detects and exploits Apache CVE-2021-42013 for remote code execution and local file disclosure via Nmap, Python, and Ruby scripts.
exploitationinformation-gatheringpenetration-testing+3
1
mauricelambert/cve-2021-42013Detects and exploits Apache CVE-2021-42013 for remote code execution and local file disclosure via Nmap, Python, and Ruby scripts.
 mauricelambert/cve-2021-41773
Multi-language exploit and detection scripts for CVE-2021-41773, enabling remote code execution and local file disclosure on vulnerable Apache…
 hackspeak/cve-2026-66066
CVE-2026-66066 (KindaRails2Shell) PoC - Rails Active Storage/libvips arbitrary file read to RCE; for authorized security testing
 rapid7/recog
Pattern recognition for hosts, services, and content
 s0c5/remotepasswordwifi
Script in Ruby. Break Remote router wifi passwords.
 mpgn/cve-2019-5418
CVE-2019-5418 - File Content Disclosure on Ruby on Rails
 z3n70/cve-2021-41277
simple program for exploit metabase
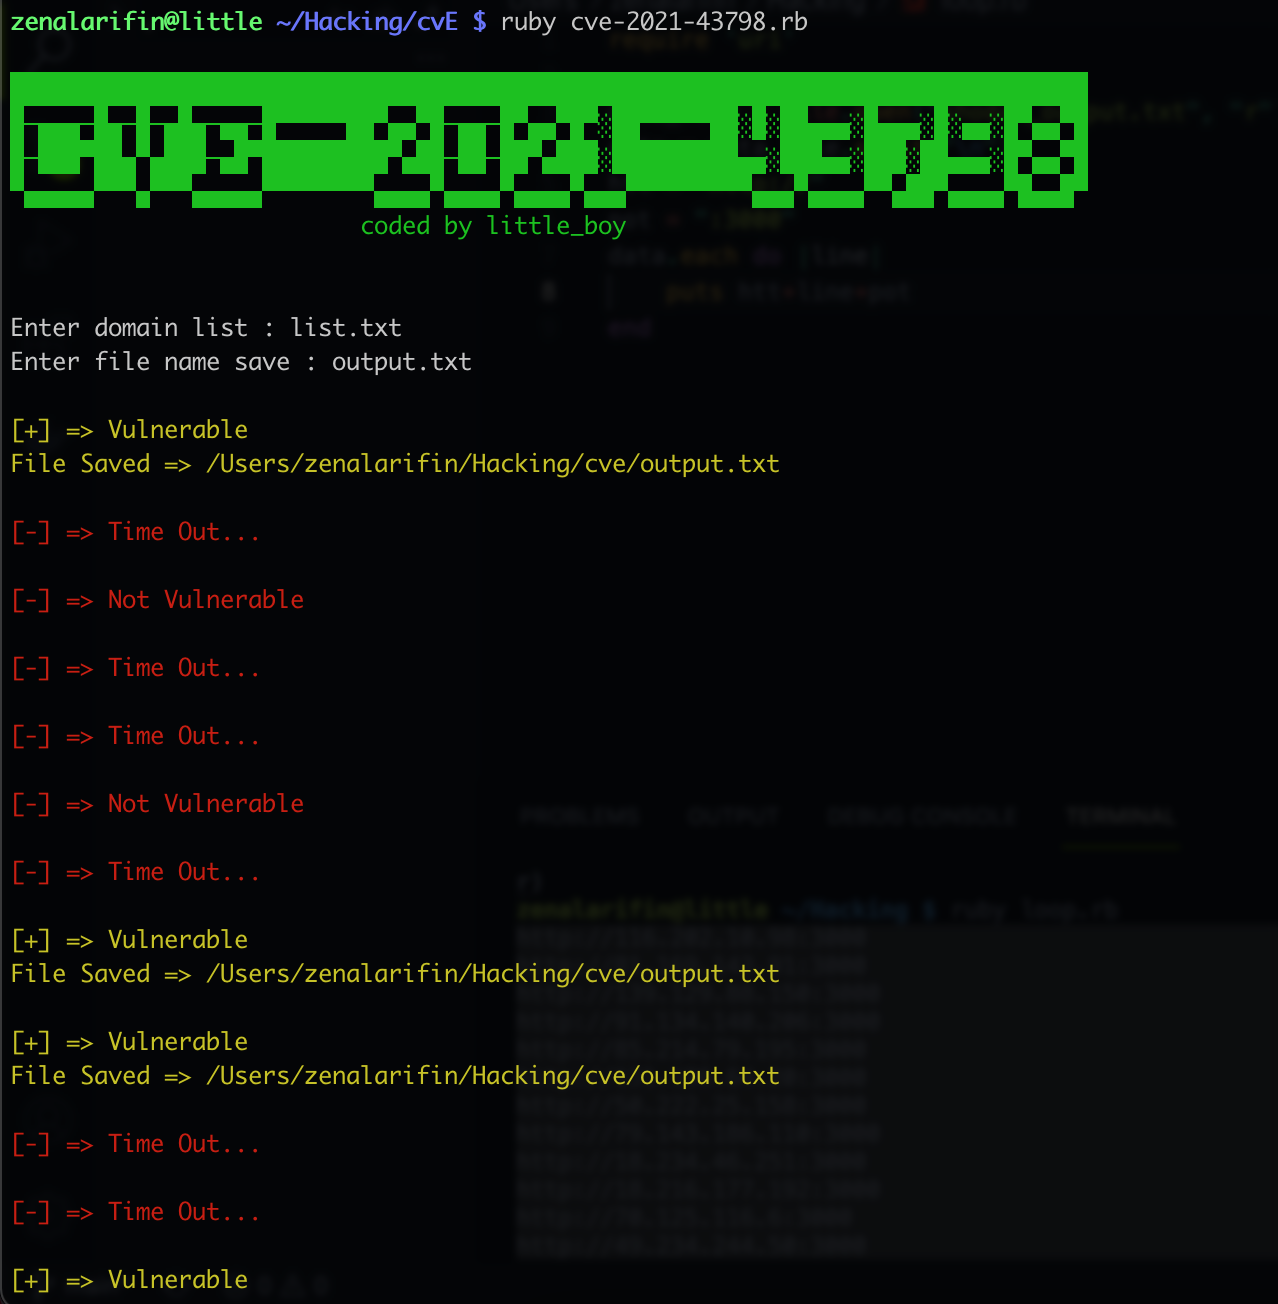 z3n70/cve-2021-43798
Simple program for exploit grafana
 omaratallahh/cve-2023-23138
short view of ruby on rails properties misconfiguration
 svaltheim/cve-2023-23752
Python exploit for Joomla! v4.2.8 unauthenticated information disclosure vulnerability (CVE-2023-23752). Extracts sensitive configuration data from…
 sakthivel10q/cve-2025-14847
🛠 Exploit the CVE-2025-14847 vulnerability in MongoDB to disclose sensitive heap memory using a Python script that analyzes responses for new leaked…
 mlr0p/cve-2021-33564
Argument Injection in Dragonfly Ruby Gem
 omarkurt/cve-2014-0130
cve-2014-0130 rails directory traversal vuln
 urbanadventurer/whatweb
Next generation web scanner
 dorkerdevil/cve-2021-33564
Argument Injection in Dragonfly Ruby Gem exploit (backup)
 brompwnie/cve-2019-5418-scanner
A multi-threaded Golang scanner to identify Ruby endpoints vulnerable to CVE-2019-5418
 advaitpathak21/cve-2024-46987
Exploit created using Python
 0xsauby/yasuo
A ruby script that scans for vulnerable & exploitable 3rd-party web applications on a network