
Public_Exploit-1--Wordpress-CVE-2021-29447
 kashyapghodasara/public_exploit-1--wordpress-cve-2021-29447
CVE-2021-29447 is an authenticated XML External Entity (XXE) vulnerability in WordPress
exploitationinformation-gatheringpenetration-testing+3
kashyapghodasara/public_exploit-1--wordpress-cve-2021-29447CVE-2021-29447 is an authenticated XML External Entity (XXE) vulnerability in WordPress
 anirbala98/cve-2025-57231
Python PoC exploit for CVE-2025-57231, an unauthenticated path traversal in Docmost < 0.22.0 that reads arbitrary files via the avatar endpoint.
 solivaquaant/cve-2026-85706
Proof-of-concept and reproduction lab for CVE-2026-85706, an unauthenticated path-traversal file read in GitLab CE/EE repository commits and files…
 mhtsec/cve-2026-85706
Python PoC for CVE-2026-85706, an unauthenticated path traversal in GitLab CE/EE Repository Commits API that leaks arbitrary local files via a…
 squeeze440/zotlit-poc
PoC — attachment import copies files from unapproved local paths in ZotLit (GHSA-4qh7-66xv-h329, CVE-2026-87000, CVSS 5.5).
 yasindce1998/grafana-cve-2021-43798
This repository contains files for reproducing the vulnerability.
 risuxx/cve-2023-51127
Discloses CVE-2023-51127, a directory traversal vulnerability in FLIR AX8 thermal cameras allowing unauthenticated remote attackers to read arbitrary…
 qflksheep/cve-2026-29909-mrcms-vulnerability
Unauthenticated directory enumeration PoC for MRCMS V3.1.2, exploiting missing authentication in /admin/file/list.do to disclose server directory…
 padayali-jd/cve-2026-29597
Demonstrates an improper access control vulnerability in DDSN Interactive cm3 Acora CMS 10.7.1, allowing editor-privileged users to retrieve…
 mbanyamer/llama-stack-0.4.0rc3-local-cve-2026-25211
Local proof-of-concept scanner that detects plaintext database passwords in llama-stack initialization logs, using regex pattern matching to identify…
 chengling-ing/cve-2021-41277
Exploit script for CVE-2021-41277, an arbitrary file read vulnerability in Metabase, allowing unauthorized access to sensitive files.
 0xterror/cve-2023-22047---oracle-peoplesoft-lfi
CVE-2023-22047 is a critical unauthenticated Local File Inclusion (LFI) vulnerability in Oracle PeopleSoft Enterprise PeopleTools. This exploit…
 0xterror/cve-2023-22047-oracle-peoplesoft-lfi
CVE-2023-22047 is a critical unauthenticated Local File Inclusion (LFI) vulnerability in Oracle PeopleSoft Enterprise PeopleTools. This exploit…
 kc57/awesome-pentest
A list of awesome penetration testing tools and resources.
 webbreacher/obsidian-osint-templates
These templates are suggestions of how the Obsidian notetaking tool can be used during an OSINT investigation. The example data in those files should…
 badsectorlabs/sccm-http-looter
Find interesting files stored on (System Center) Configuration Manager (SCCM/CM) shares via HTTP(s)
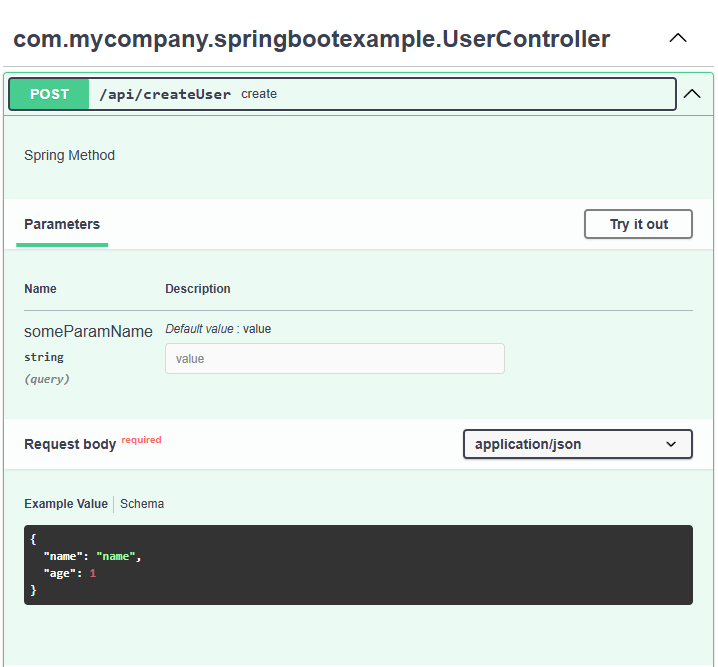 blackfan/bfscan
Tool for finding URLs, paths, secrets and generating raw HTTP requests and OpenApi specifications from config files and annotations used in JAR / WAR…
 randomrobbiebf/loot-me
Collects files and commands post-exploitation, formats them into Markdown reports, and helps find sensitive information for red team reporting.