
nextjs-scanner
 ferpalma21/nextjs-scanner
This script scans a list of URLs to detect if they are using **Next.js** and determines whether they are vulnerable to **CVE-2025-29927**. It…
exploitationfingerprint-spoofinginformation-gathering+6
2
ferpalma21/nextjs-scannerThis script scans a list of URLs to detect if they are using **Next.js** and determines whether they are vulnerable to **CVE-2025-29927**. It…
 anirbala98/cve-2025-57231
Python PoC exploit for CVE-2025-57231, an unauthenticated path traversal in Docmost < 0.22.0 that reads arbitrary files via the avatar endpoint.
 maxprog-svg/citrixbleedcve-2026-8452-2025-5777
CitrixBleed Exploit Tool - CVE-2025-5777 & CVE-2026-8452. Unauthenticated remote memory read from Citrix NetScaler ADC & Gateway. Steal admin session…
 khashayarnzk/cve-2025-10952-ml-logger-afr
PoC for CVE-2025-10952 — ml-logger unauthenticated arbitrary file read. CVSS 5.3
 e4zyy/project-cve-2025-54068
Fast Python scanner detects vulnerable Laravel Livewire v3 sites (CVE-2025-54068, CVSS 9.2). Separates risky sites into vuln.txt, safe sites into…
 netvanguard-cmd/cve-2025-11371
Proof-of-concept exploit for CVE-2025-11371, an unauthenticated Local File Inclusion in Gladinet CentreStack and TrioFox, enabling remote file…
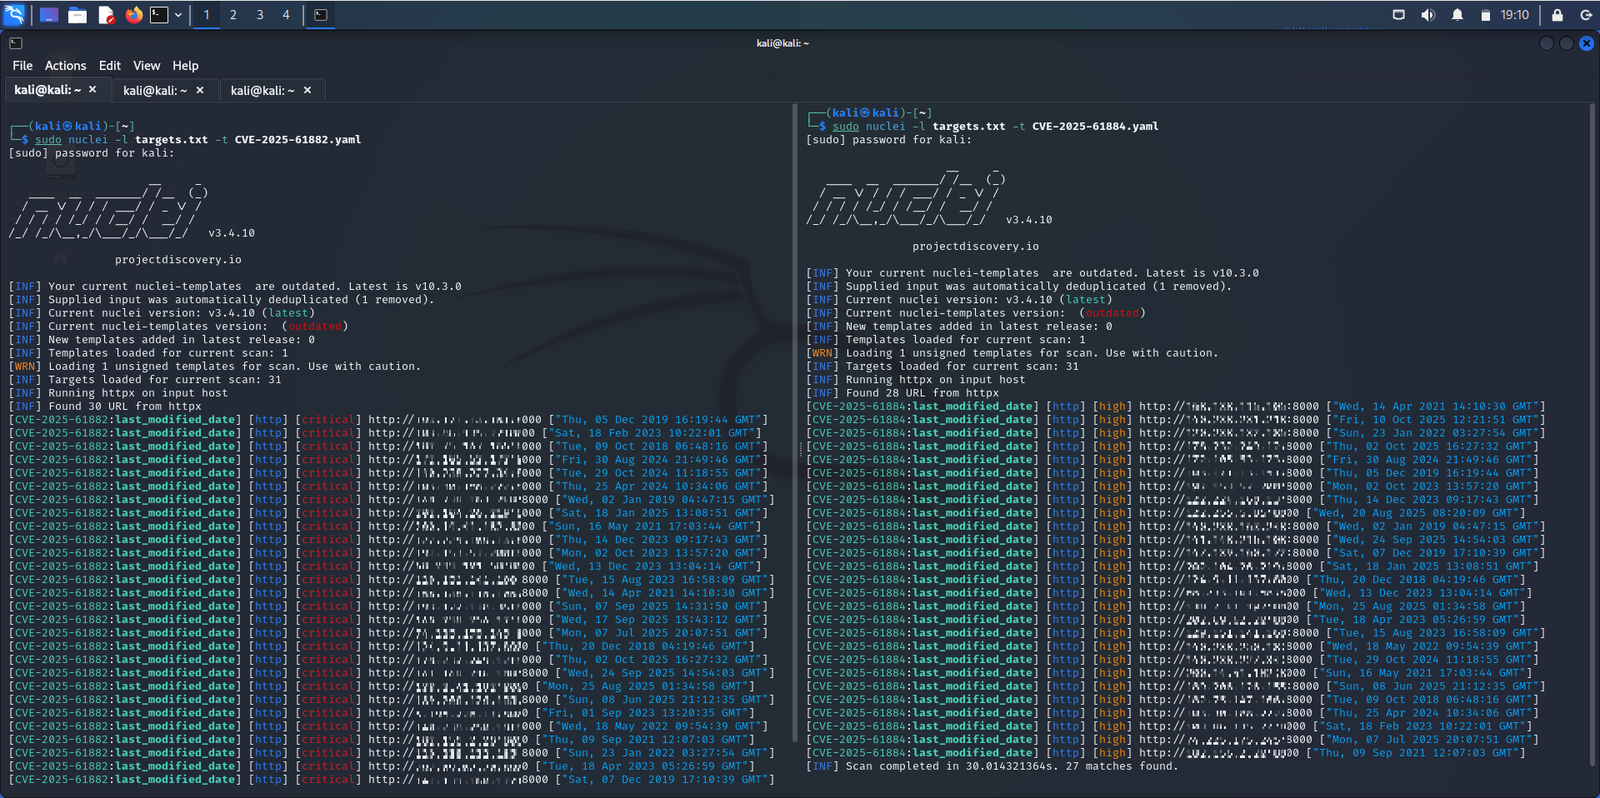 jrexploit/blackash-cve-2025-61884
Provides a detailed summary and detection guidance for CVE-2025-61884, an unauthenticated data disclosure vulnerability in Oracle E-Business Suite…
 battalionx/http-oracle-ebs-cve-2025-61882.nse
Nmap NSE script for detecting Oracle E-Business Suite CVE-2025-61882 with multi-tier checks including fingerprinting, version checks, SSRF tests, and…
 kaiisyms/cve-2025-24071
Microsoft Windows File Explorer Spoofing Vulnerability / NTLM Hash Leak
 1amunvalid/cve-2025-10951
Proof-of-concept checker for CVE-2025-10951, an unauthenticated path traversal in ml-logger, validating arbitrary file read via /glob and /stream…
 cybrly/badsuccessor
Exploits the Windows Server 2025 dMSA privilege escalation vulnerability to enumerate writable OUs, escalate to arbitrary domain users, extract…
 twappz/htb-silentium-writeup
Hack The Box - Silentium machine writeup | CVE-2025-58434, CVE-2025-59528, CVE-2025-8110
 cerberusmrxi/cve-2025-48932-invision-community-sqli-exploit
CVE-2025-48932 - Unauthenticated SQL injection exploit for Invision Community ≤ 4.7.20. Fully automated exploitation with database enumeration,…
 7h30th3r0n3/cve-2025-51586-prestashop-poc
PrestaShop AdminLogin Email Enumeration PoC - CVE-2025-51586. This repository provides an ethical Proof-of-Concept (PoC) for the PrestaShop…
 xploitgh0st/cve-2025-26794-exploit
SQL injection exploit for CVE-2025-26794 in Exim 4.98. Automated data extraction via time-based blind SQLi. For authorized penetration testing only.
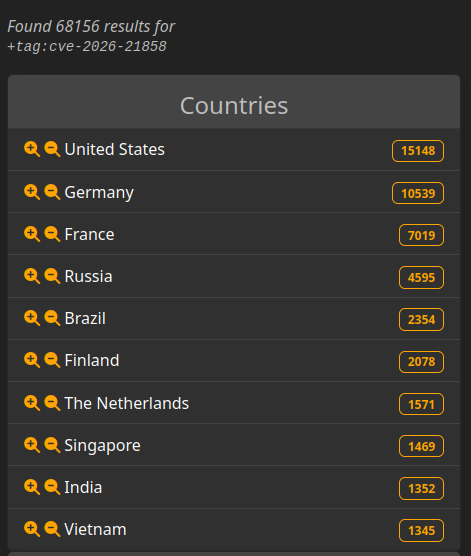 chocapikk/cve-2026-21858
n8n Ni8mare - Unauthenticated Arbitrary File Read to RCE Chain (CVSS 10.0)
 bountyyfi/azure-apim-cross-tenant-signup-bypass
Security advisory: Azure APIM Developer Portal allows cross-tenant account registration by bypassing UI signup restrictions. Reported to MSRC twice -…
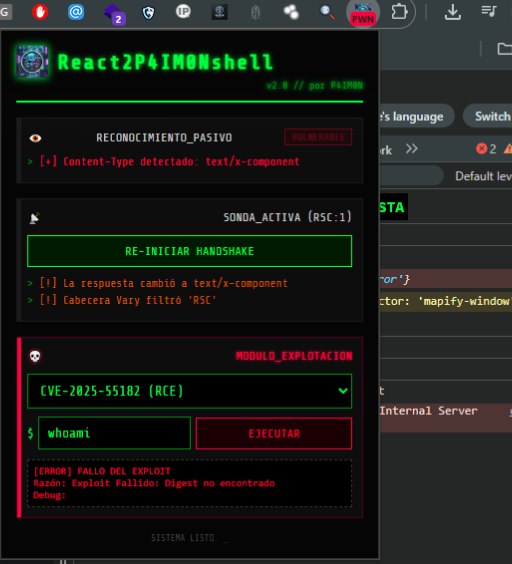 mammaninelsond/react2p4im0nshell
💥Extension Tool para Auditoría y Explotación avanzada RCE/Source Leak/Dos (CVE-2025-55182/83/84) para entornos Next.js y React Server Components…