diario-commandline-tools

CLI client for bulk DIARIO API consumption: upload PDF/Office documents, query file hashes, and automate malware analysis workflows via command-line…

CLI client for bulk DIARIO API consumption: upload PDF/Office documents, query file hashes, and automate malware analysis workflows via command-line…

Automated vulnerability scanner for Oracle WebLogic Server, detecting historical CVEs including deserialization, SSRF, and arbitrary file upload with…

Proof-of-concept exploit for CVE-2025-26319, a pre-authentication arbitrary file upload vulnerability in Flowise, enabling remote code execution.

Apache Tomcat AJP Ghostcat (CVE-2020-1938) exploit tool for file disclosure with multi-target scanning, custom wordlists, and upload point detection…

Flowise Windows RCE exploit for CVE-2026-58057. Bypasses environment variable validation via case-sensitive flaw. Uses node_options to inject…

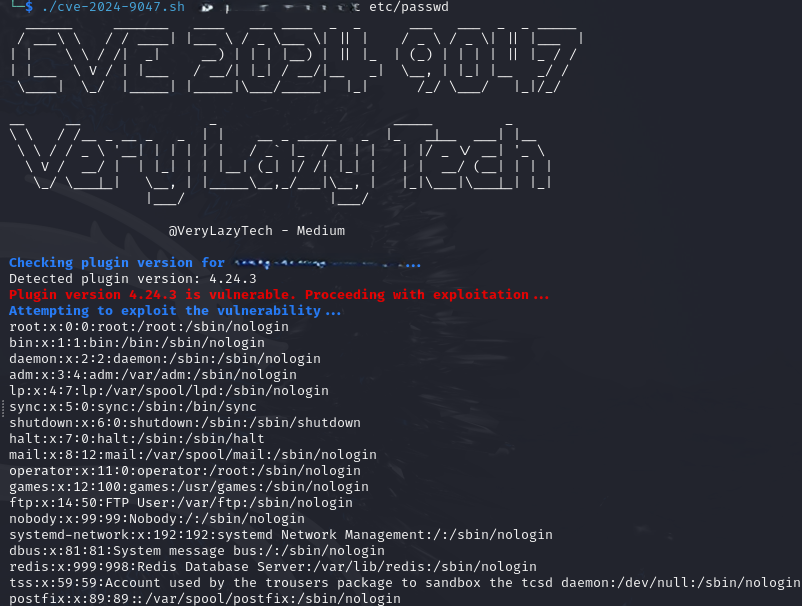
Python-based tool to detect and exploit arbitrary file read vulnerability in WordPress WP File Upload plugin (<=4.24.11), enabling unauthenticated…

Multiple exploits for Monitorr

CVE-2026-57827 — RSFiles! Joomla Component Unauthenticated File Upload RCE. Split-controller upload bypass. CVSS 9.8 | CWE-434 | com_rsfiles < 1.17.12

A tool that identifies writable web directories in Apache Tomcat via HTTP PUT method [CVE-2025-24813]

CVE-2025-24813-Scanner is a Python-based vulnerability scanner that detects Apache Tomcat servers vulnerable to CVE-2025-24813, an arbitrary file…

Exploits WordPress pre-auth XSS (CVE-2026-64638) to achieve remote code execution, installing an AES-encrypted backdoor webshell with persistence,…

Python mass-exploit toolkit for CVE-2026-5524, an unauthenticated file upload RCE in the WordPress Divi Form Builder plugin, with webshell upload and…

Unauthenticated File Upload → RCE PoC for CVE-2026-57827 (RSFiles! Joomla < 1.17.12). Authorized security research use only.

Mass exploit toolkit for CVE-2026-5524, an unauthenticated file upload RCE in Divi Form Builder. Features multi-threaded scanning, WAF bypass…

Extracts all S3 Buckets from CSP report headers and then tests for file upload vulns

Python-based exploit for CVE-2022-44268, an arbitrary file read vulnerability in ImageMagick. Poisons PNG images to read sensitive files from…

POC - WordPress File Upload plugin, in the wfu_file_downloader.php file before version <= 4.24.11