Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
368 results
conti-ransomware-writeup preview

conti-ransomware-writeup

GitHubjustjeff211/conti-ransomware-writeup

Conducted a full SOC investigation into a Conti ransomware compromise of an Exchange server using Splunk 8.2.2. Analysed 28,145 events across Windows…

digital-forensicseducationforensics+6
6 months ago
GhostTrace preview

GhostTrace

GitHubdevzinh/ghosttrace

Read-only Windows forensic scanner for software traces — persistence, execution artifacts (Prefetch, Shimcache, BAM), user activity and Ghost Tasks…

digital-forensicsforensicsincident-response+3
2 months ago
BearFTP preview
Archived

BearFTP

GitHubkolya5544/bearftp

Honeypot FTP server written in .NET Core (C#) for both Linux and Windows.

defensive-toolsincident-responseinformation-gathering+4
143 years ago
EnableWindowsLogSettings preview

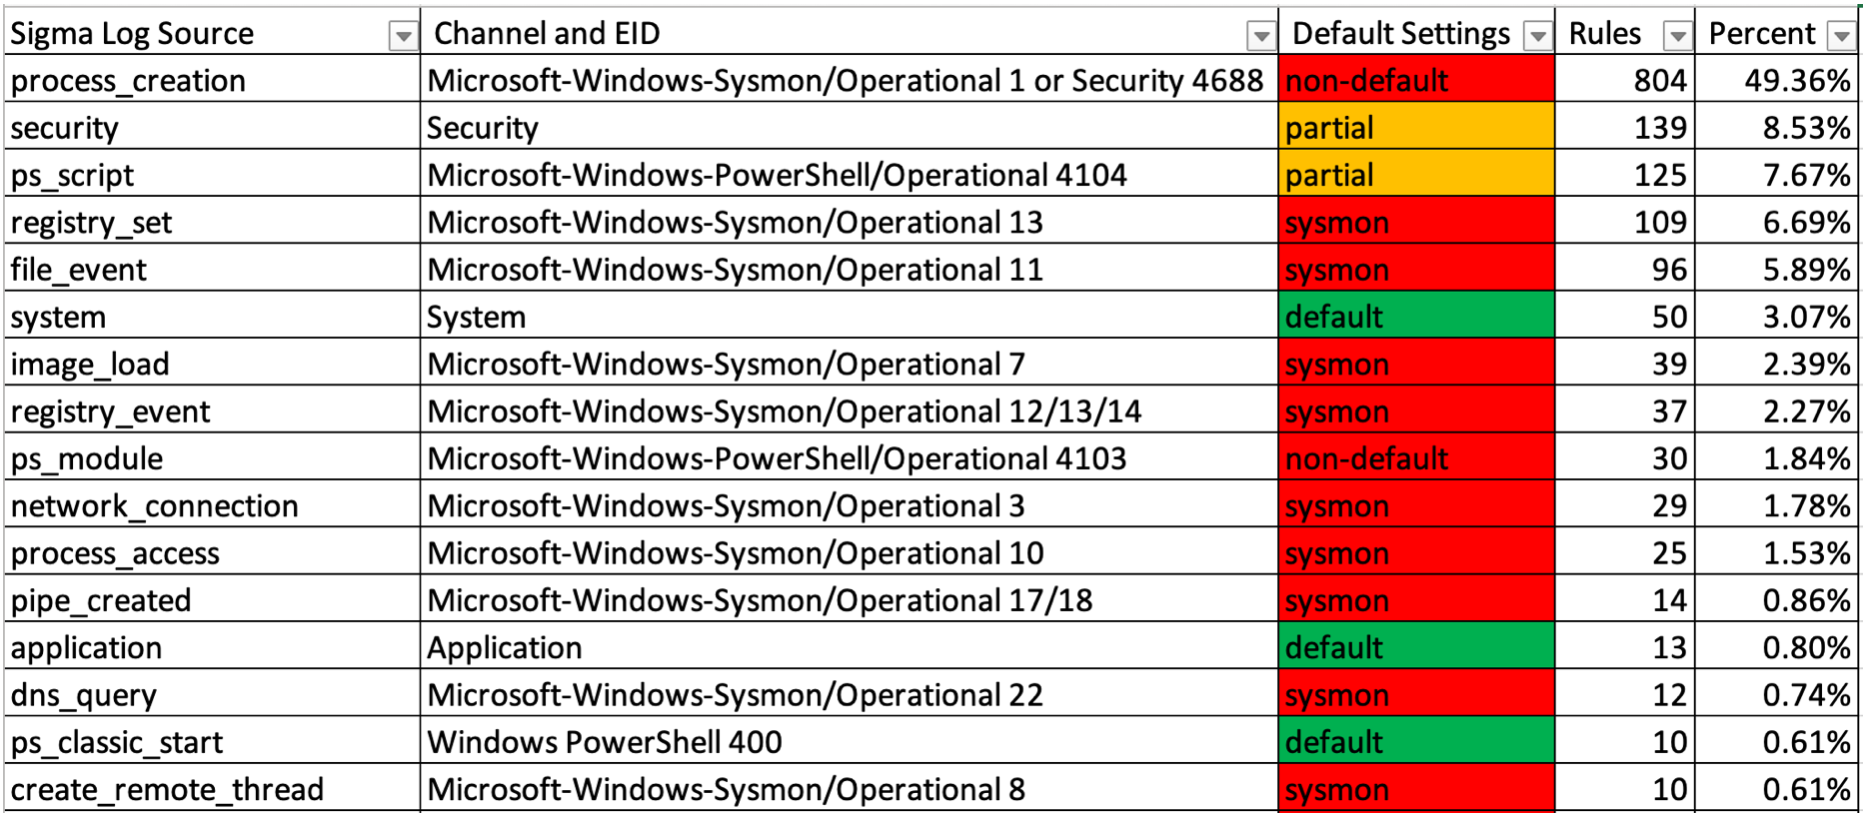
EnableWindowsLogSettings

GitHubyamato-security/enablewindowslogsettings

Documentation and scripts to properly enable Windows event logs.

configuration-auditingdefensive-toolsdigital-forensics+3
7231 year ago
Evtx_Log_Browser preview

Evtx_Log_Browser

GitHubkacos2000/evtx_log_browser

Evtx Log (xml) Browser

defensive-toolsdigital-forensicsforensics+2
603 years ago
pywintrace preview

pywintrace

GitHubfireeye/pywintrace

Python ctypes wrapper for Event Tracing for Windows (ETW) enabling session control, event capture, and custom callbacks for security monitoring and…

defensive-toolsdigital-forensicsincident-response+2
3033 years ago
LogonTracer preview

LogonTracer

GitHubjpcertcc/logontracer

Investigate malicious Windows logon by visualizing and analyzing Windows event log

ai-securitydigital-forensicsincident-response+2
3.3k2 months ago
RsWindowsThingies preview

RsWindowsThingies

GitHubforensicmatt/rswindowsthingies

Rust-based Windows forensic toolkit for real-time MFT monitoring, event log streaming, and channel enumeration, enabling live system analysis and…

digital-forensicsincident-responselog-analysis
236 years ago
PhantomFS preview

PhantomFS

GitHuballoysecuregroup/phantomfs

Windows honeypot using ProjFS to project decoy files that trigger Event Log and desktop alerts when accessed, with SMB remote session logging for…

defensive-toolsincident-responseintrusion-detection
711 month ago
attack_monitor preview

attack_monitor

GitHubyarox24/attack_monitor

Endpoint detection & Malware analysis software

defensive-toolsdynamic-analysis-sandboxingincident-response+1
2336 years ago
fleet-cve-scanner preview

fleet-cve-scanner

GitHubboostedchaos/fleet-cve-scanner

An open-source, single-script CVE scanner for RMM-managed fleets. Pure PowerShell 7 — joins your RMM software inventory against NVD, CISA KEV, EPSS…

configuration-auditingincident-responselog-analysis+3
122 months ago
BLUESPAWN preview

BLUESPAWN

GitHubion28/bluespawn

An Active Defense and EDR software to empower Blue Teams

configuration-auditingdefensive-toolsincident-response+3
1.3k6 months ago
QLOG preview

QLOG

GitHubthreathunters-io/qlog

ETW-based Windows process creation logger that enriches events with file hashes, signatures, and parent process details, outputting to Windows…

defensive-toolsforensicsincident-response+1
444 years ago
Secure-Desktop preview

Secure-Desktop

GitHubalphadelta/secure-desktop

Anti-keylogger/anti-rat application for Windows

anti-botdefensive-toolsincident-response+2
24711 years ago
Get-AppLockerEventlog preview

Get-AppLockerEventlog

GitHubromaissaadjailia/get-applockereventlog

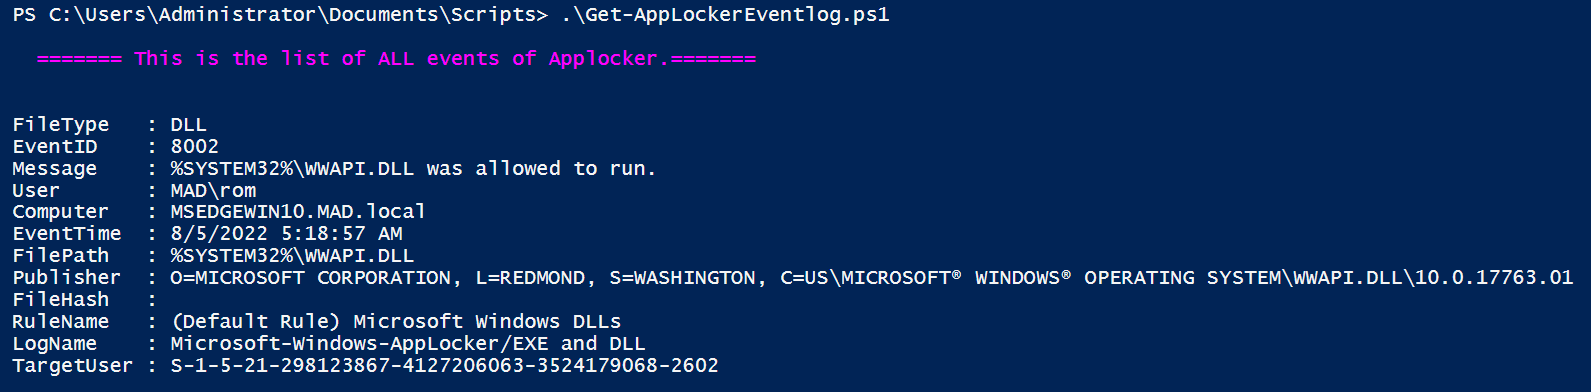
This is a repo for fetching Applocker event log by parsing the win-event log

forensicsincident-responselog-analysis+1
294 years ago
doublepulsar-detection-script preview

doublepulsar-detection-script

GitHubwithsecurelabs/doublepulsar-detection-script

A python2 script for sweeping a network to find windows systems compromised with the DOUBLEPULSAR implant.

incident-responseintrusion-detectionmalware-analysis+2
1.0k9 years ago
SuperMem preview

SuperMem

GitHubcrowdstrike/supermem

A python script developed to process Windows memory images based on triage type.

digital-forensicsforensicsincident-response+2
2682 years ago
WindowsFirewallHookDriverEnumeration preview

WindowsFirewallHookDriverEnumeration

GitHubnccgroup/windowsfirewallhookdriverenumeration

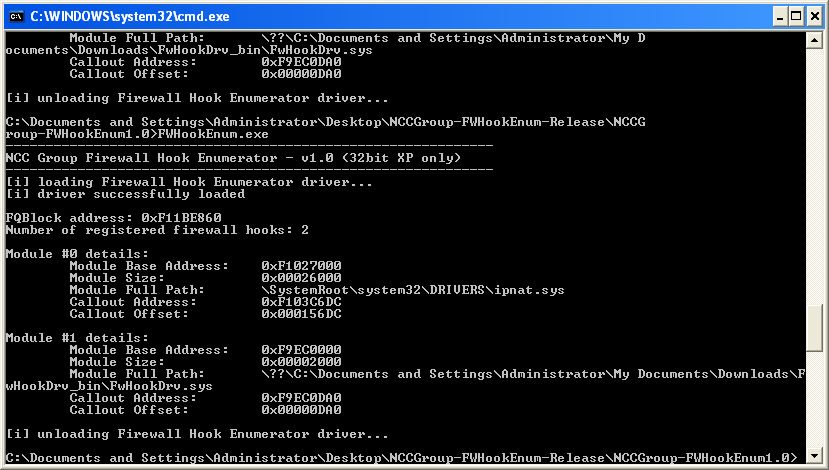
Tools to enumerate Windows Firewall Hook Drivers on Windows 2000, XP and 2003

digital-forensicsforensicsincident-response+2
2111 years ago
Previous12…21Next