CVE-2022-22965-Spring4Shell-Security-Operations-Analysis

A comprehensive Security Operations Centre (SOC) incident response simulation demonstrating threat detection, triage, analysis, and mitigation of the…

A comprehensive Security Operations Centre (SOC) incident response simulation demonstrating threat detection, triage, analysis, and mitigation of the…

Modular Bash toolkit that hardens Debian/Ubuntu systems for CyberPatriot competitions, automating account, firewall, SSH, PAM, and service hardening…

Reconciliation audit for Alliance Auth's Discord integration: finds guild members holding AA-managed roles that Auth never granted and strips or…

Tools for the Computer Incident Response Team :computer:

This package extends the Intel package to log more fields


Forensics artefact collection tool for systems running Microsoft Windows

A low to medium interaction honeypot.

A command line tool for pstree-like output on macOS with additional pid capturing capabilities

CVE-2023-34362-IOCs. More information on Deep Instinct's blog site.

Usermode detector that catches indirect syscalls. Traps Hell's Hall, Tartarus' Gate, RecycledGate, and VEH syscalls & Many more.

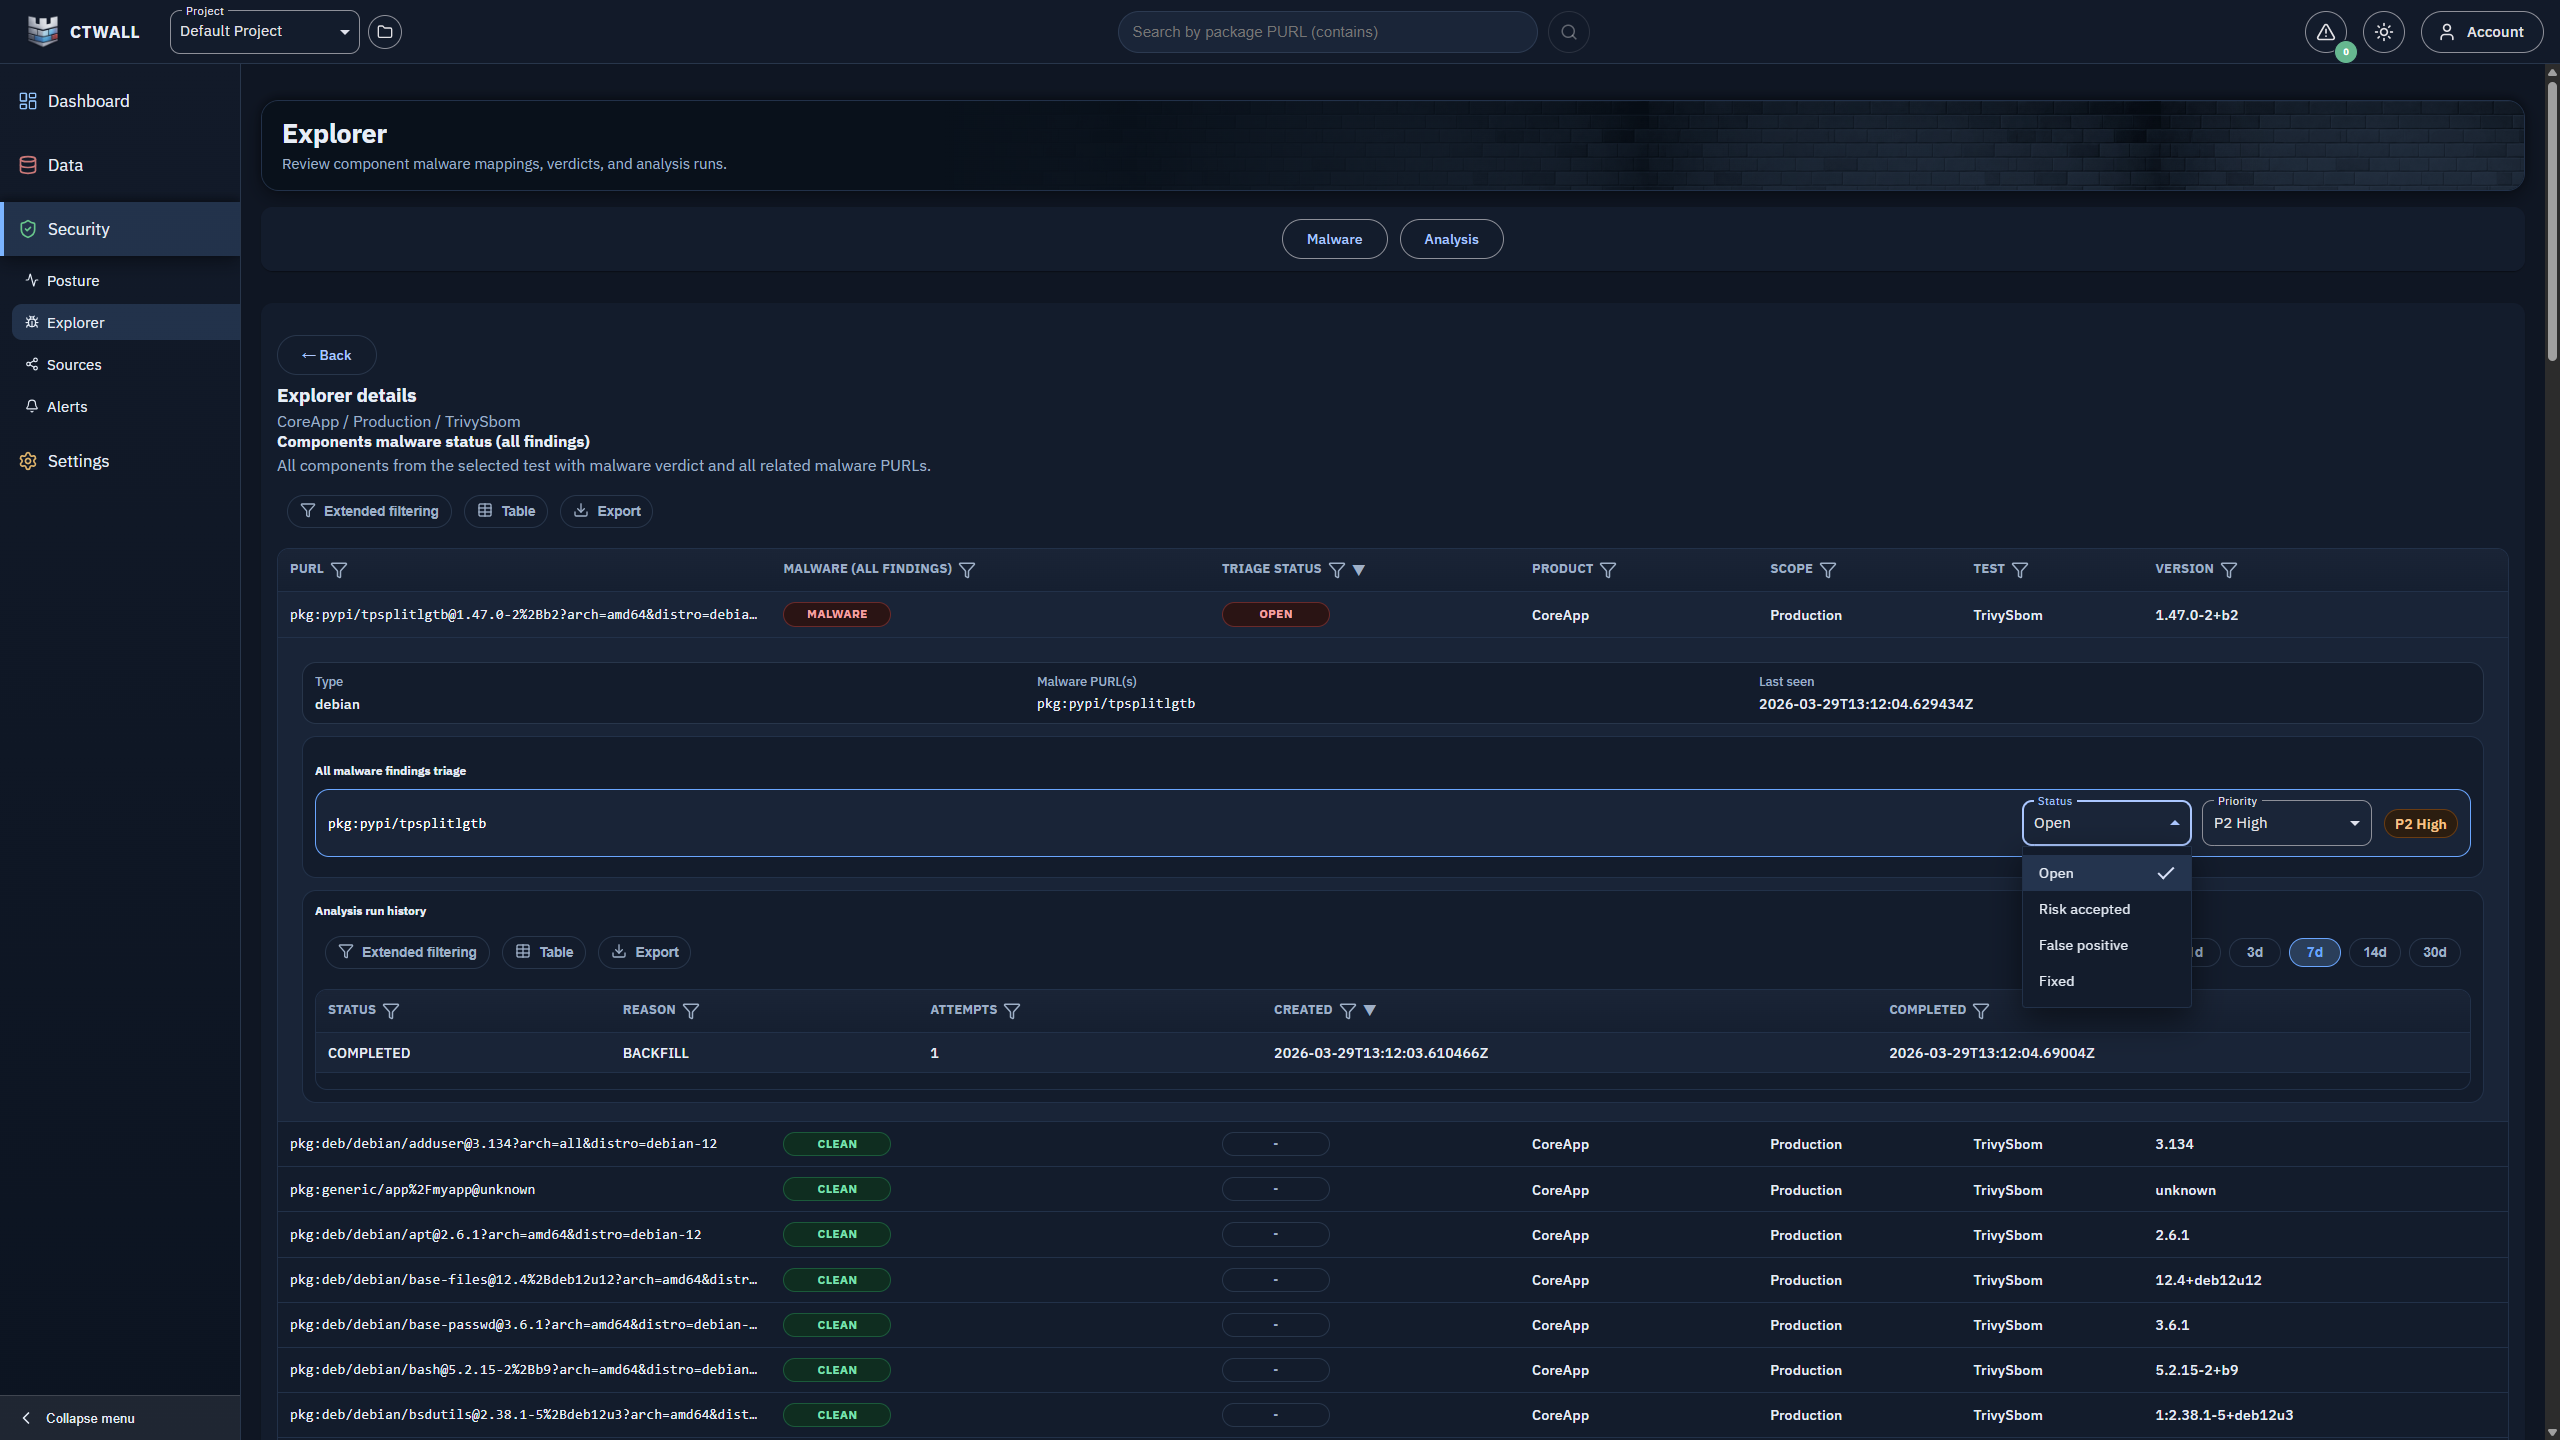
CTWall (ChainThreatWall) platform helps Security, DevOps, and Product teams make risk decisions faster by using SBOM/BOM data to identify malware in…

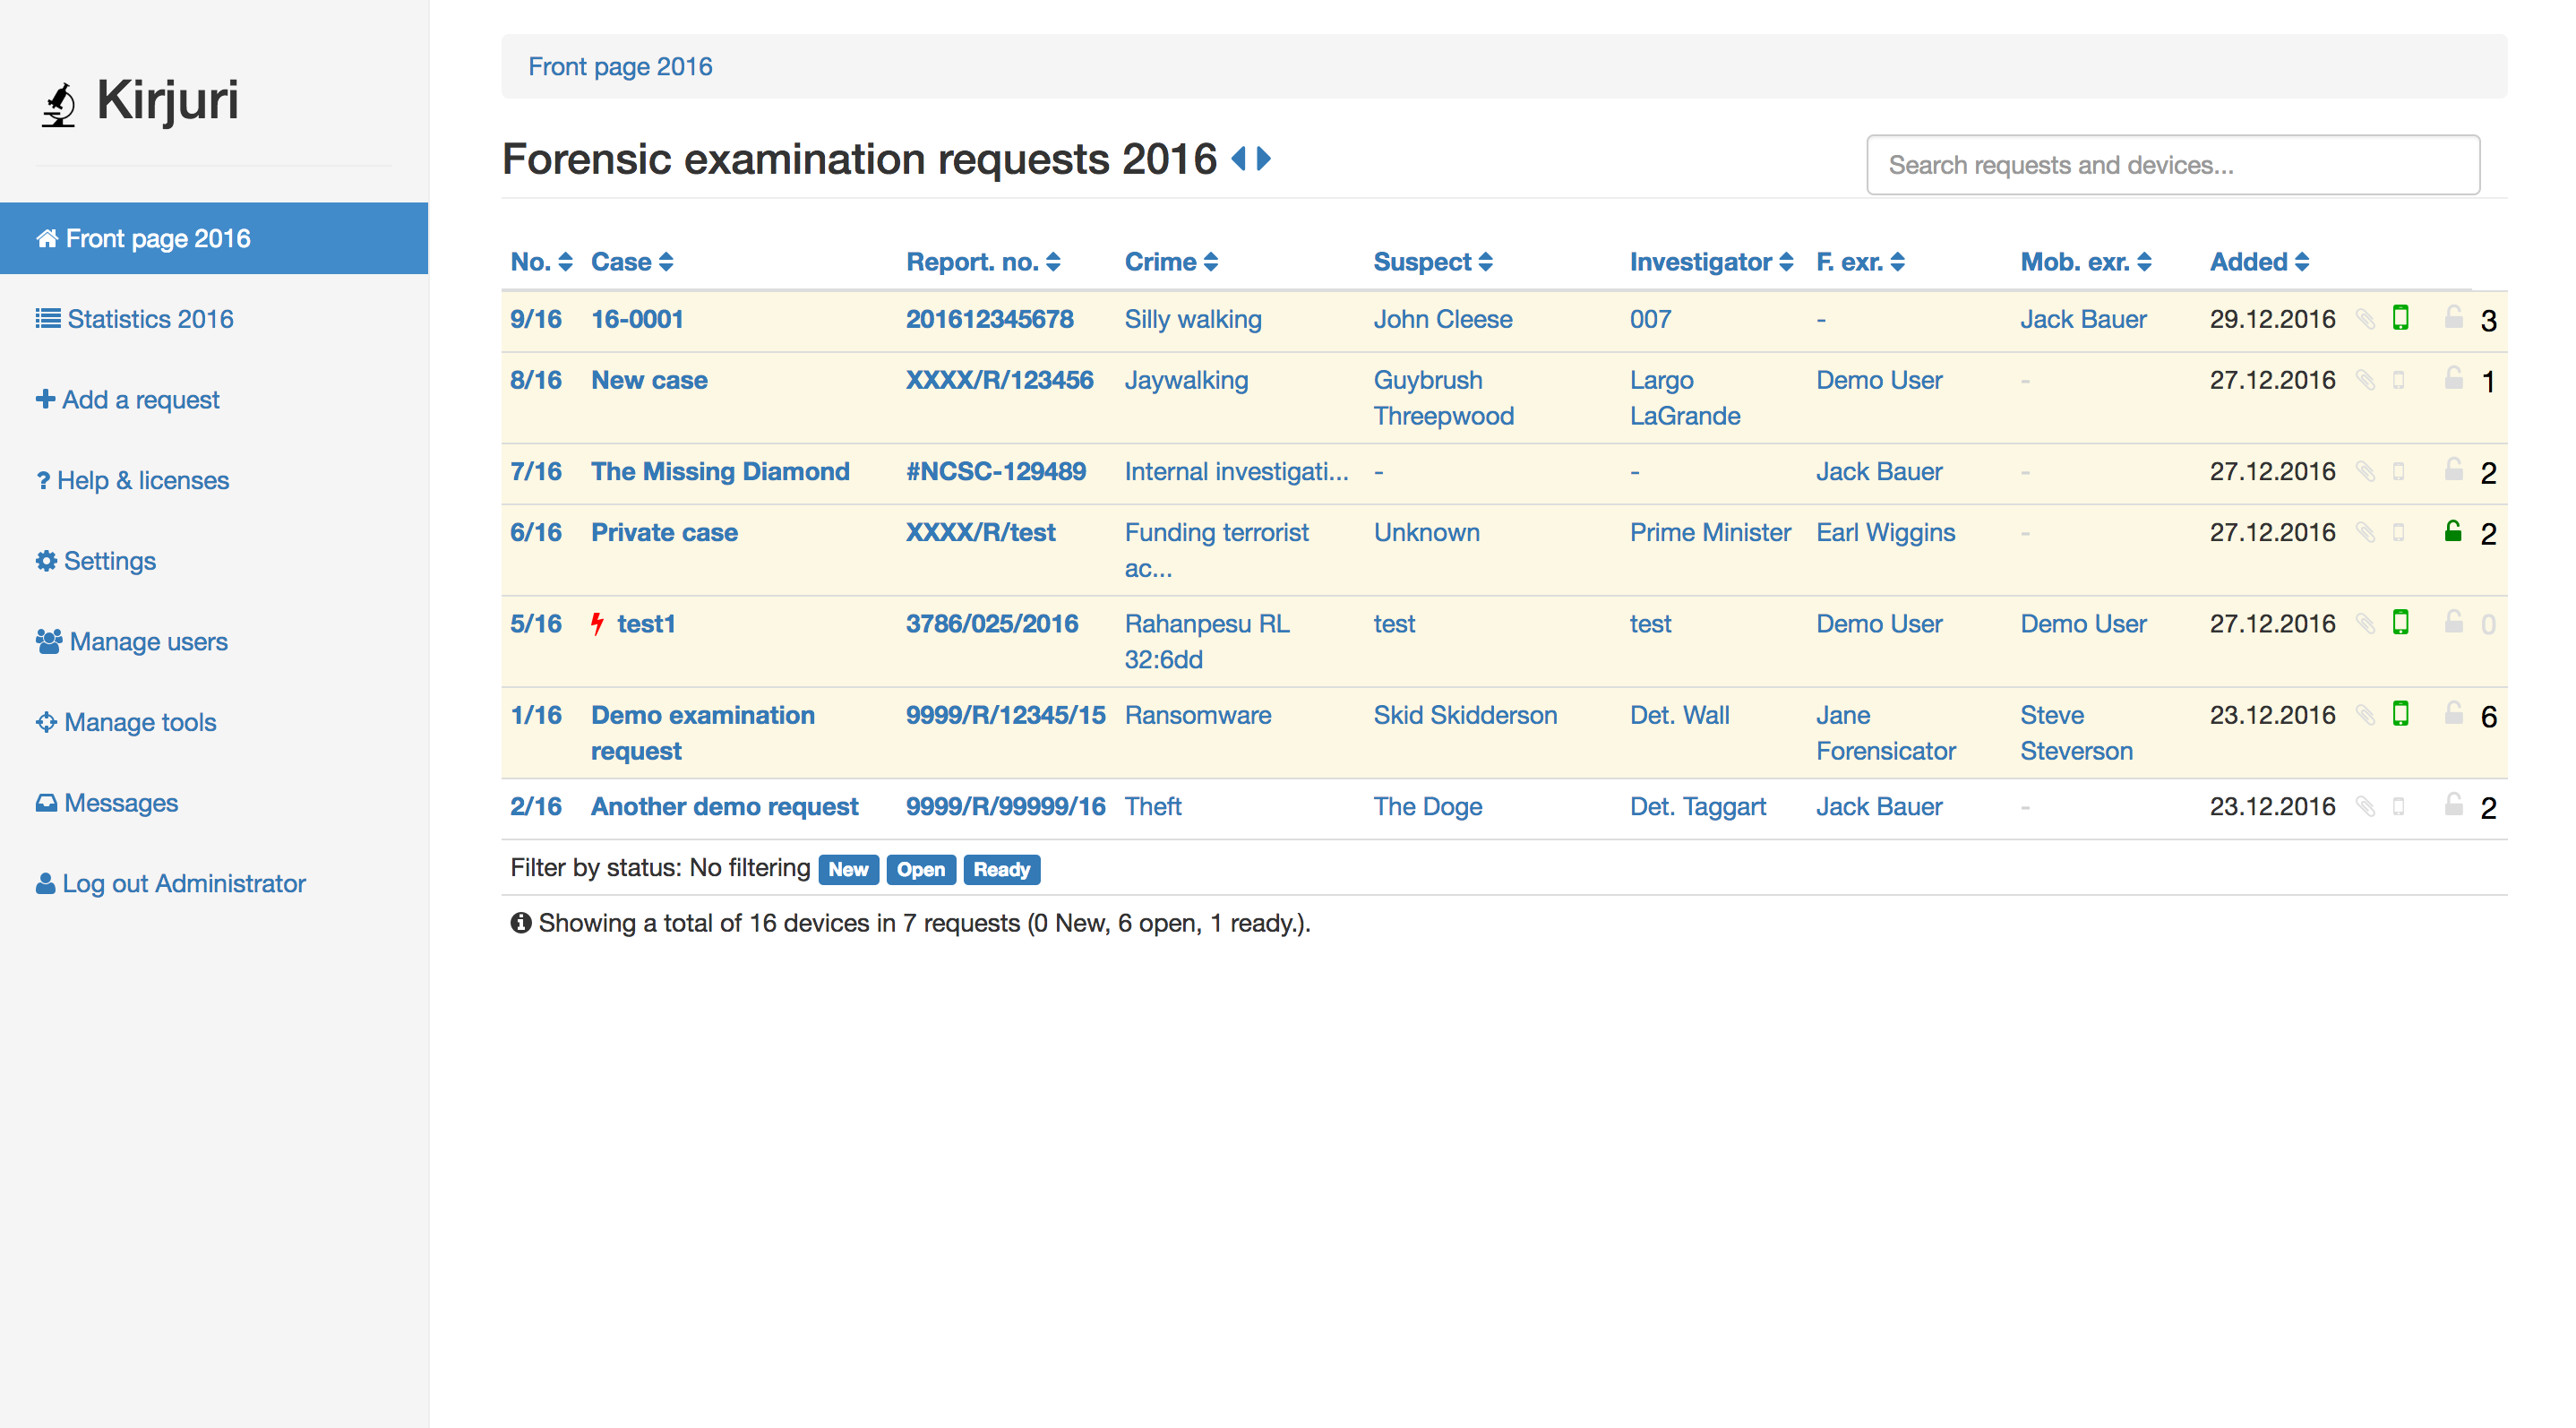
Kirjuri is a web application for managing cases and physical forensic evidence items.

Welcome to the NCC Group Threat Intelligence Alert repo, here you will find the alerts which we have raised to our customers regarding intelligence…

React2Shell, CVE-2025-55182, RCE Vulnerability: A critical breakdown of the unsafe deserialization flaw in React Server Components that enables…

A high interaction SSH honeypot

PowerShell toolkit for AMSI/Defender detection-boundary analysis and static malware triage maps byte offsets to detection triggers, plus YARA,…