
Archived
halogen
 target/halogen
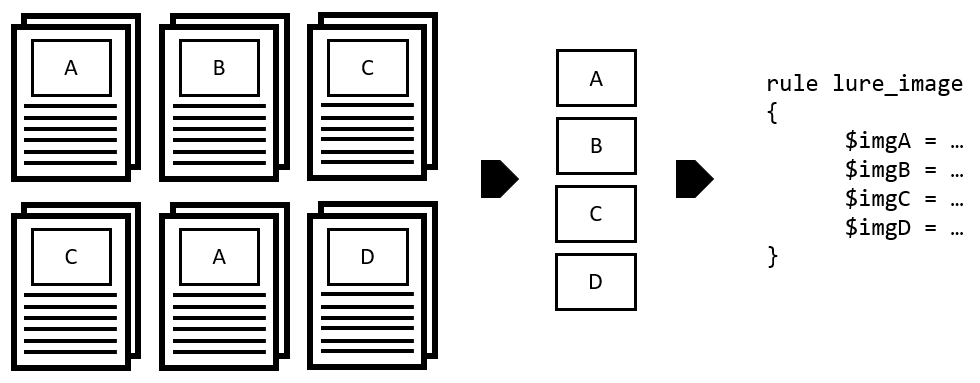
Automatically create YARA rules from malicious documents.
forensicsincident-responsemalware-analysis+2
210
 l4r1k/citrixnetscaleranalysis
🔬 Jupyter notebook to help automate some of the forensic analysis related to Citrix Netscalers compromised via CVE-2019-19781
 cado-security/rip_raw
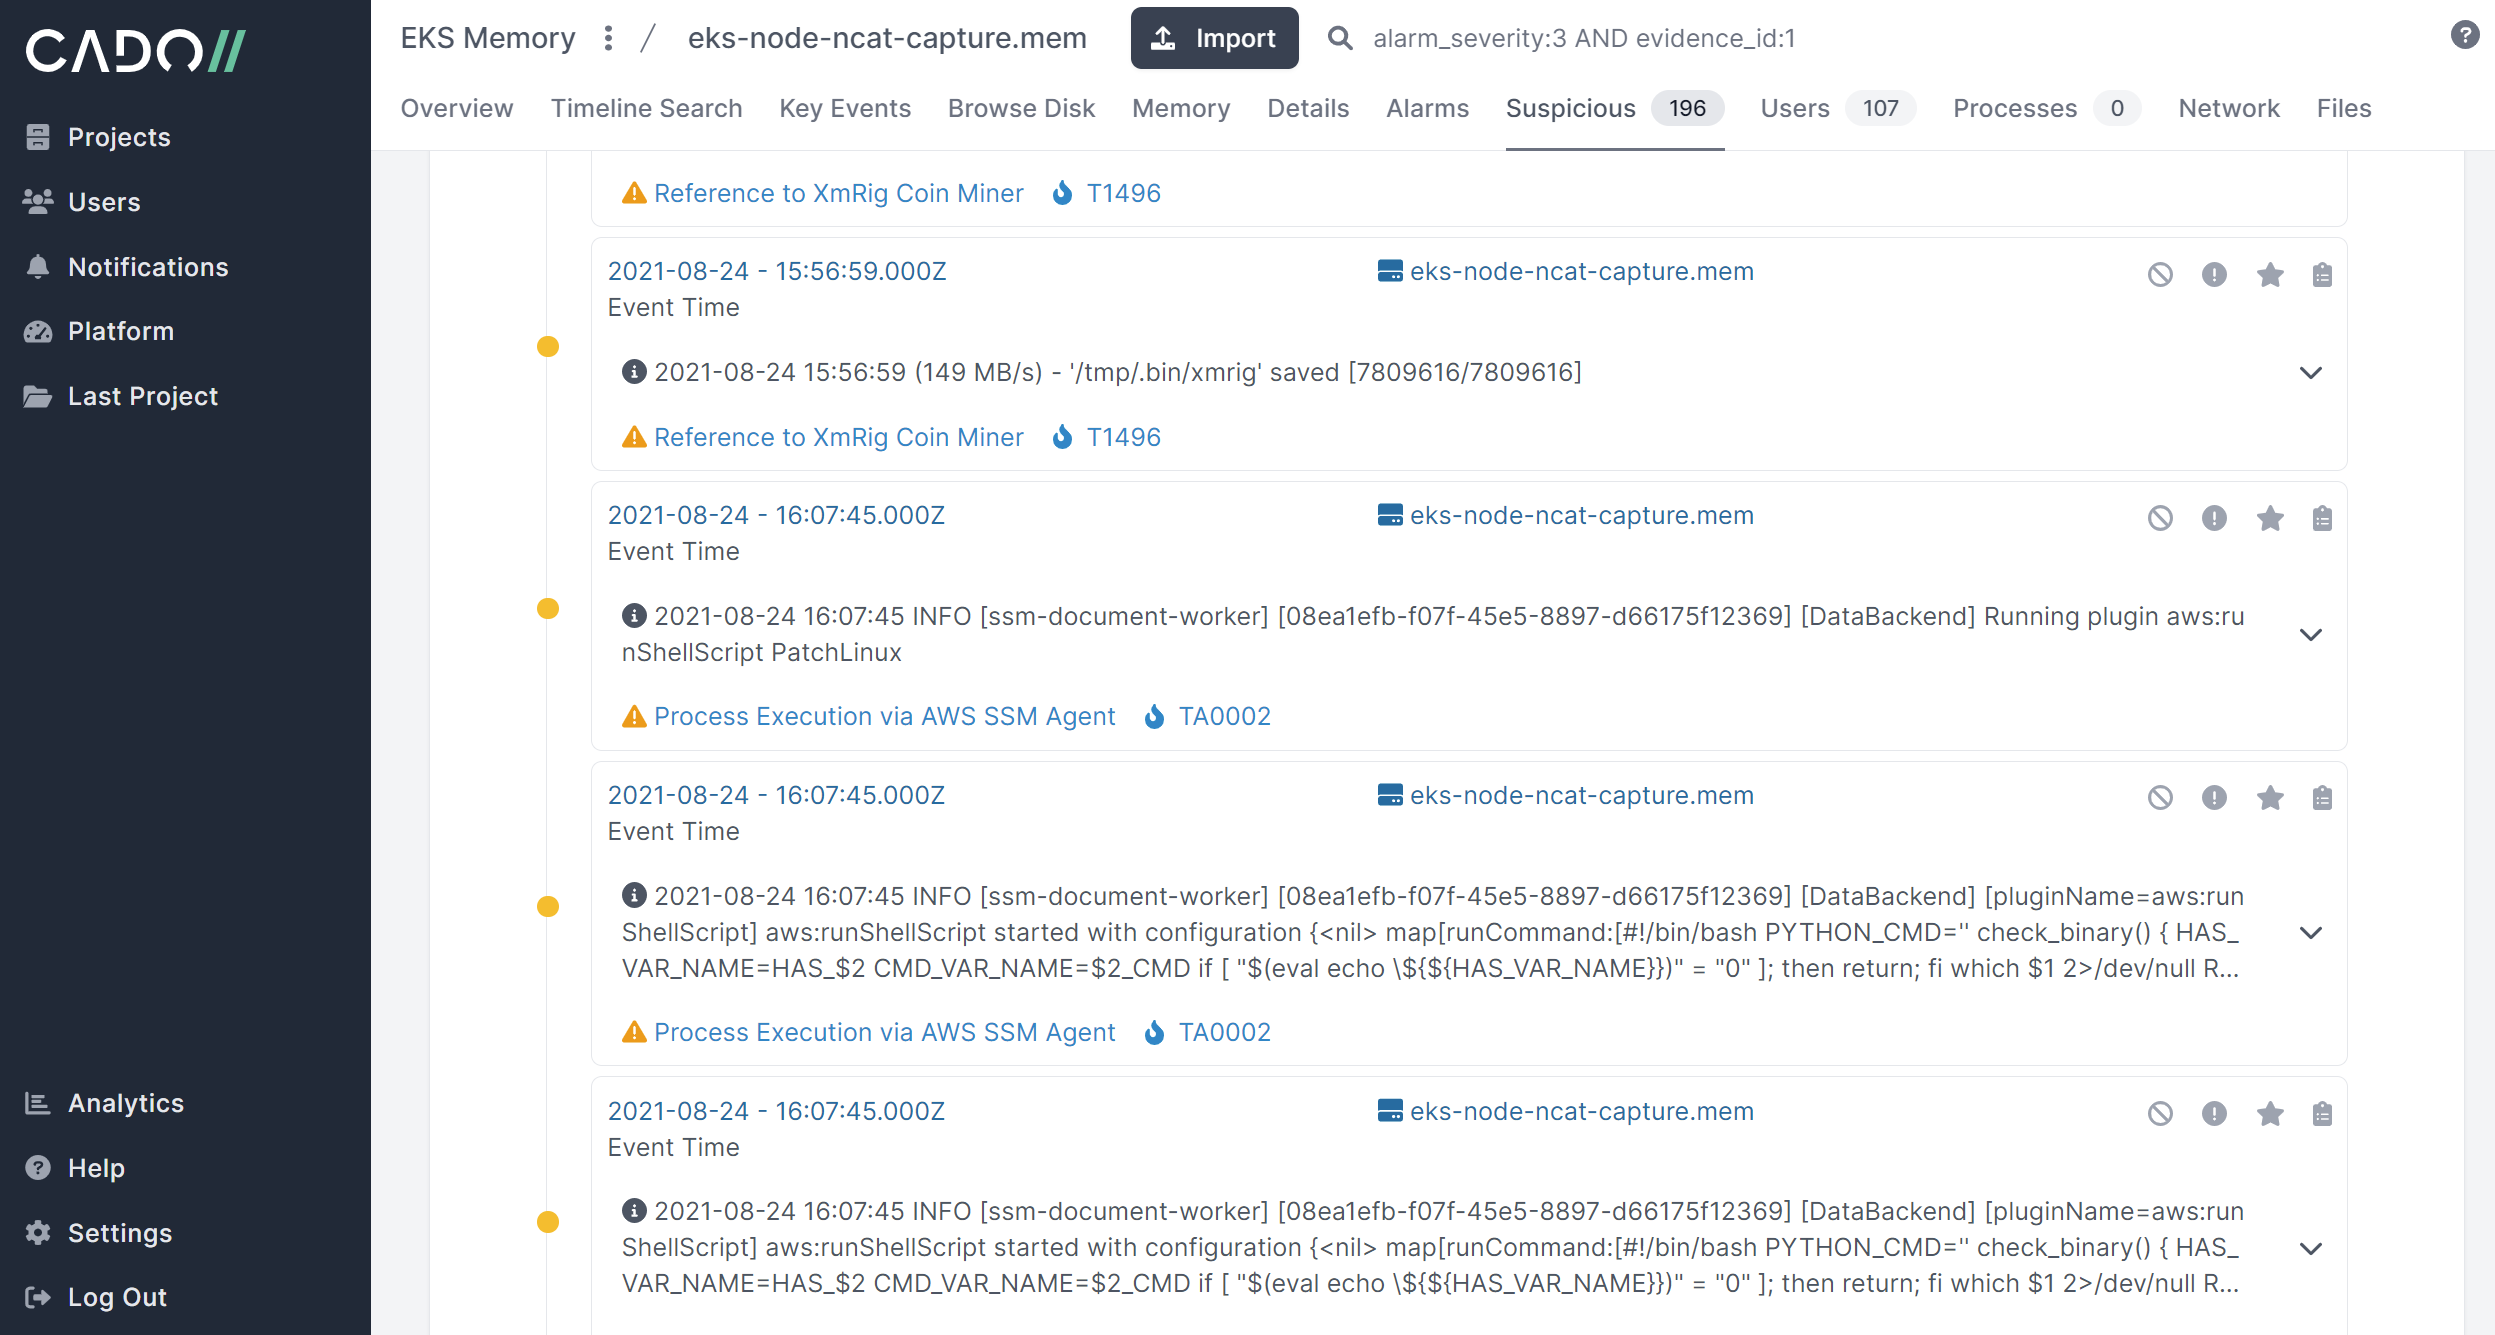
Rip Raw is a small tool to analyse the memory of compromised Linux systems.
 mvt-project/androidqf
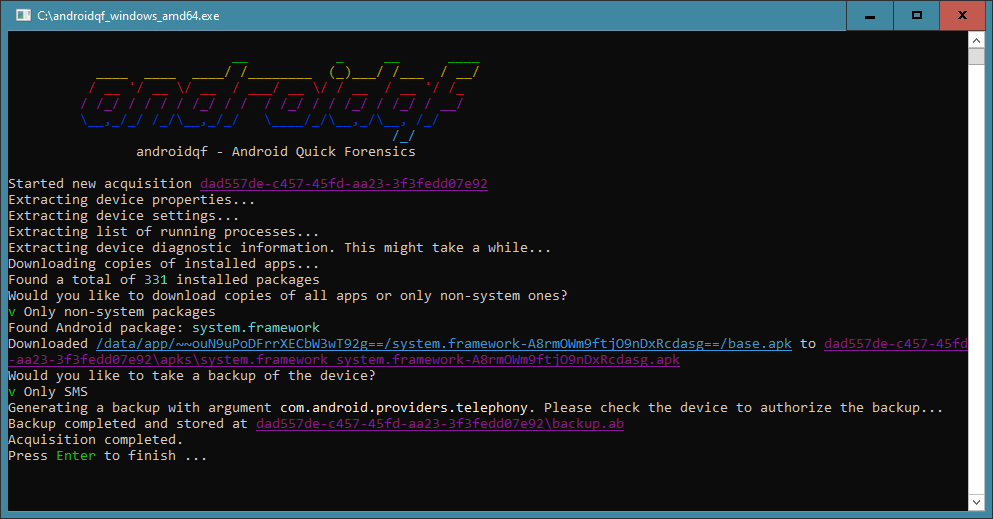
androidqf (Android Quick Forensics) helps quickly gathering forensic evidence from Android devices, in order to identify potential traces of…
 emrekybs/bluefish
Automation tool designed to simplify the analysis of PCAP (Packet Capture) files
 invictus-ir/microsoft-extractor-suite
A PowerShell module for acquisition of data from Microsoft 365 and Azure for Incident Response and Cyber Security purposes.
 cloudflare/mitmengine
A MITM (monster-in-the-middle) detection tool. Used to build MALCOLM:
 malvuln/ransomlord
RansomLord is a proof-of-concept Anti-Ransomware exploitation tool that automates the creation of PE files, used to compromise ransomware…
 yossisassi/zerologon-exploitation-check
quick'n'dirty automated checks for potential exploitation of CVE-2020-1472 (aka ZeroLogon), using leading artifects in determining an actual…
 viralmaniar/ddwpasterecon
DDWPasteRecon tool will help you identify code leak, sensitive files, plaintext passwords, password hashes. It also allow member of SOC & Blue Team…
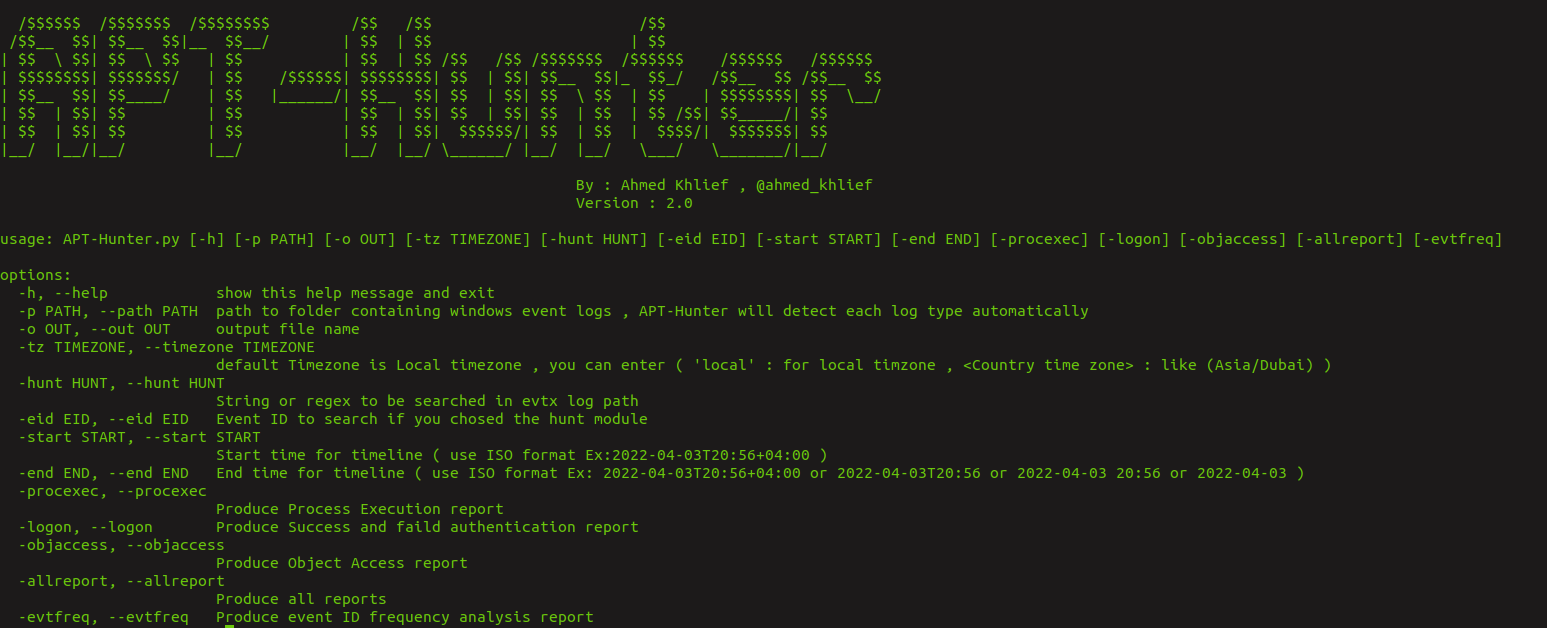 ahmedkhlief/apt-hunter
APT-Hunter is Threat Hunting tool for windows event logs which made by purple team mindset to provide detect APT movements hidden in the sea of…
 cisagov/esxiargs-recover
A tool to recover from ESXiArgs ransomware
 zeronetworks/rpcfirewall
Windows RPC firewall that audits, detects, and blocks malicious remote procedure calls to prevent lateral movement, reconnaissance, and exploitation…
 mindcrypt/stegowiper
A powerful and flexible tool to apply active attacks for disrupting stegomalware
 viralmaniar/remote-desktop-caching-
This tool allows one to recover old RDP (mstsc) session information in the form of broken PNG files. These PNG files allows Red Team member to…
 sucuri-labs/cve-2025-57819-ioc-check
This is repository contains a script to check for current IOCs listed in the freepbx forum topic of the CVE-2025-57819
 lawiet47/autoresponder
Automates incident response tasks via Carbon Black Response API: file/registry deletion, process killing, sensor isolation, binary collection, and…