
reportly
 sap8899/reportly
AzureAD/EntraID user activity reporter for blue teams. Input a suspicious user and time frame to receive a detailed report of user info, actions, and…
cloud-securityidentity-access-managementincident-response+2
96
sap8899/reportlyAzureAD/EntraID user activity reporter for blue teams. Input a suspicious user and time frame to receive a detailed report of user info, actions, and…
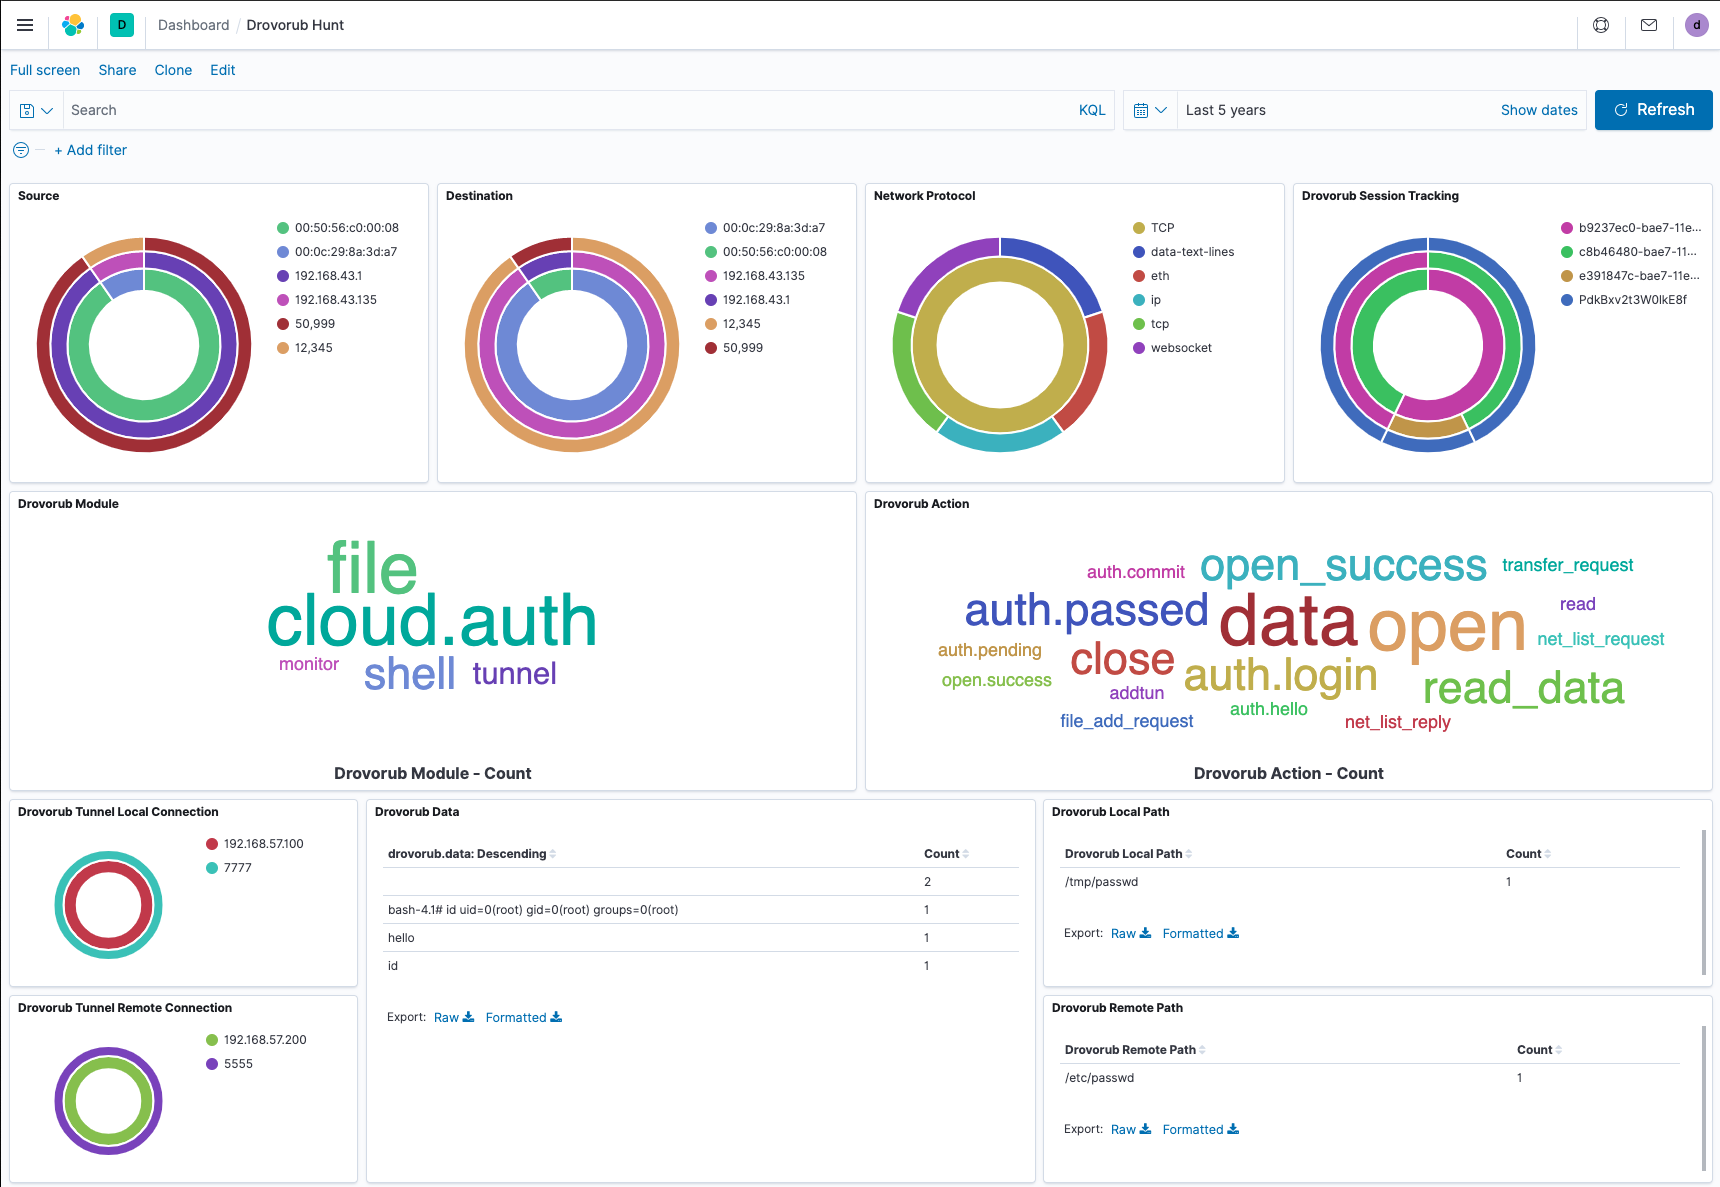 insane-forensics/drovorub-hunt
A tool to assist with network-based hunting for GRU's Drovorub malware c2
 theevidencehunter/forensix
Digital Forensics Intelligence Framework
 immersive-labs-sec/bruteratel-detectiontools
A collection of Tools and Rules for decoding Brute Ratel C4 badgers
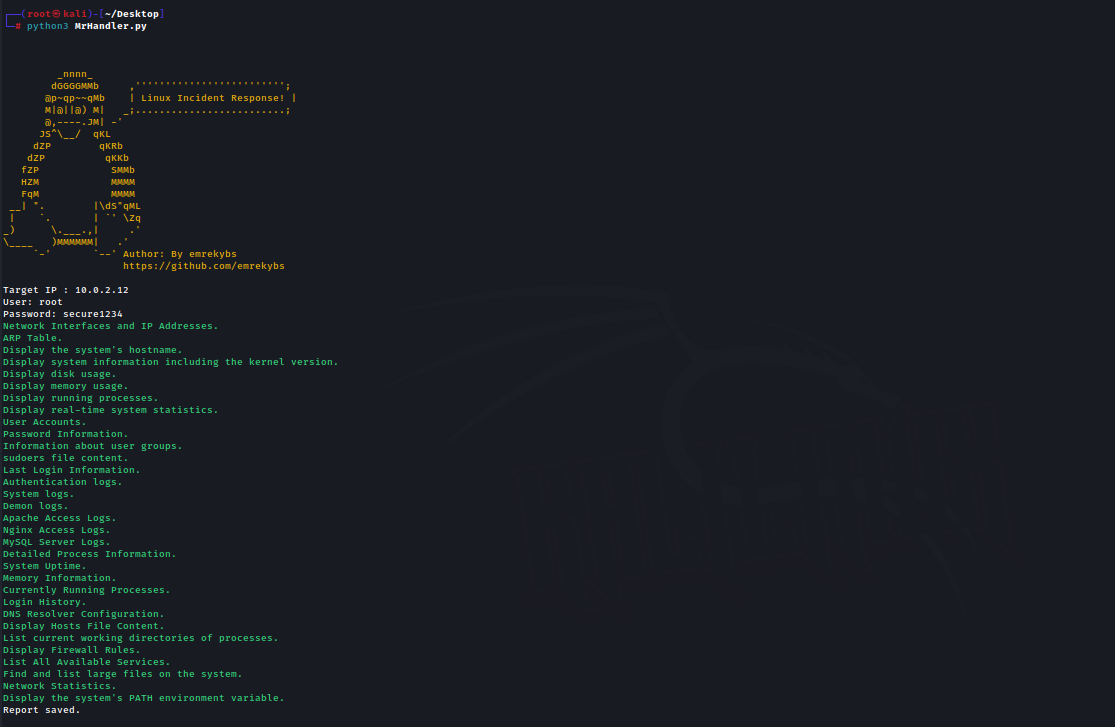 emrekybs/mrhandler
SSH-based Linux incident response tool that executes diagnostic commands to collect network configs, logs, user accounts, and processes, then…
 24owais/threat-intel-cve-2024-3094
Threat intelligence report analyzing the xz-utils backdoor vulnerability (CVE-2024-3094)