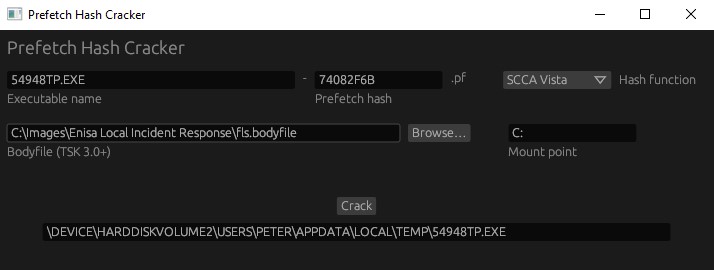
prefetch-hash-cracker

Brute-force tool that recovers full executable paths from Windows prefetch hashes using bodyfiles, supporting XP, Vista, and 2008 hash functions for…

Brute-force tool that recovers full executable paths from Windows prefetch hashes using bodyfiles, supporting XP, Vista, and 2008 hash functions for…

Active deception tool that transparently migrates attackers from real targets to honeypots during exploitation and post-exploitation, supporting…

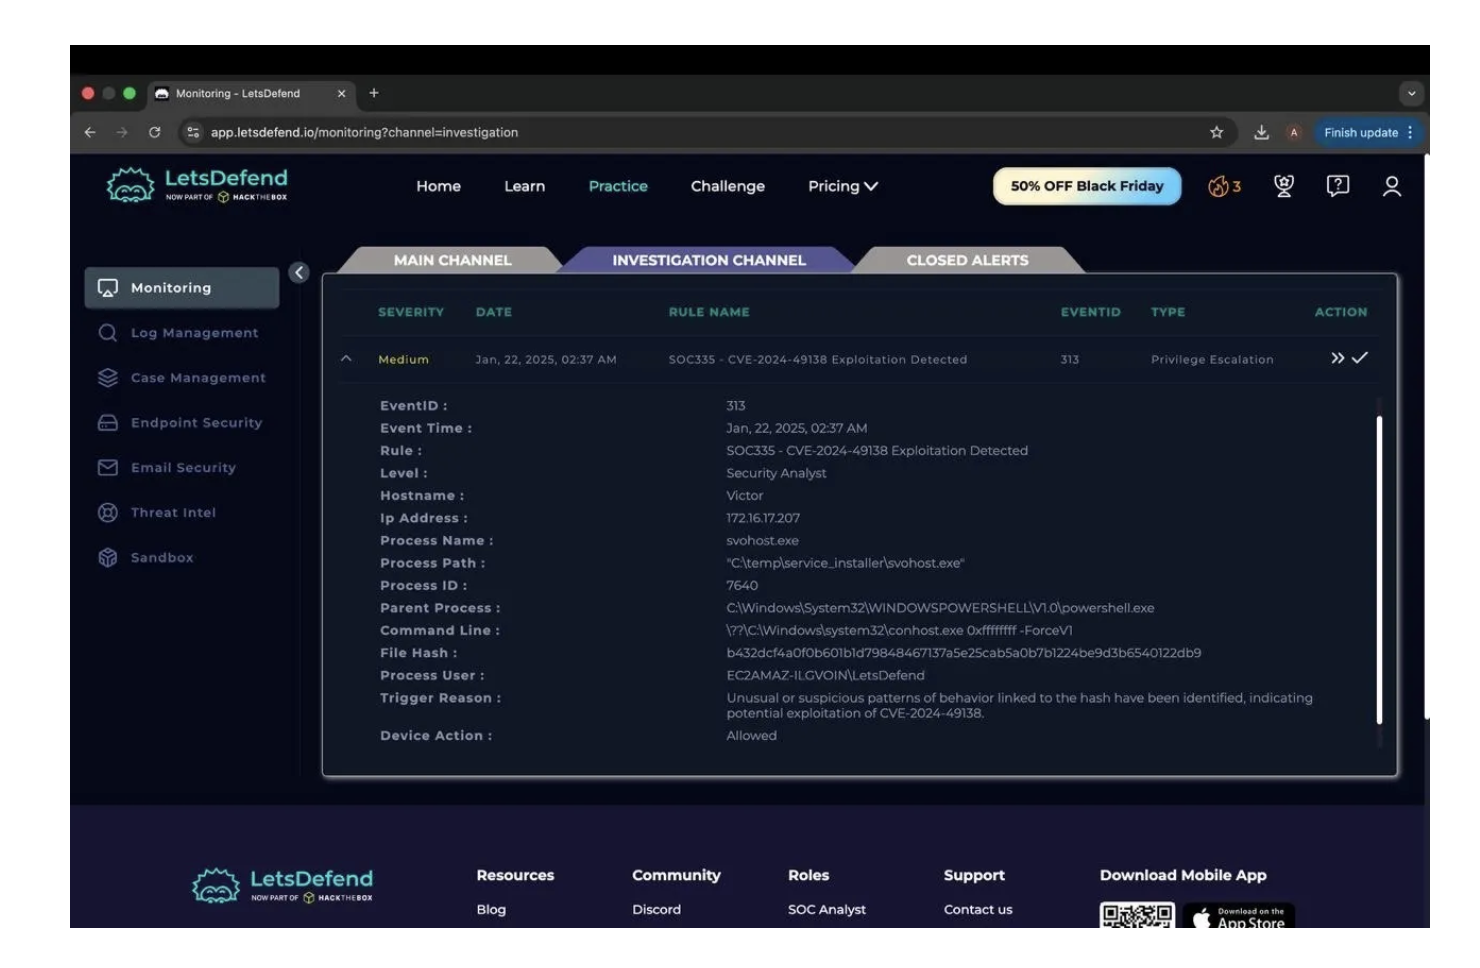
SOC investigation of CVE-2024-49138 exploitation involving brute-force activity, PowerShell execution, malicious payload analysis, privilege…

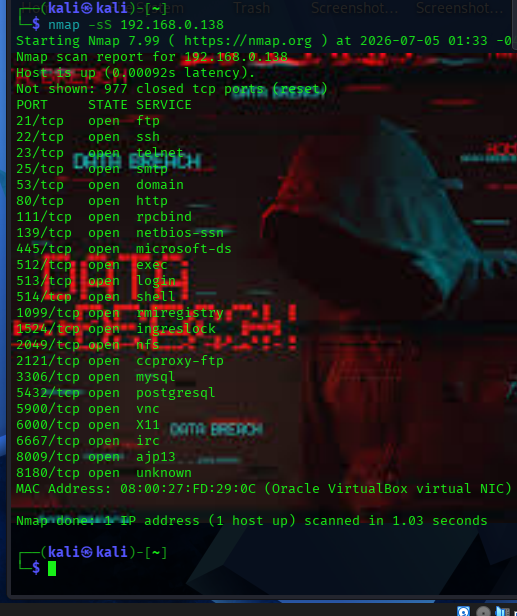
Wazuh + Suricata SOC lab detecting real exploits (CVE-2011-2523) and brute-force attacks, with custom detection rules for gaps in default IDS…

Medium-interaction SSH honeypot deployment capturing real-world brute-force traffic, malware drops, and attacker behavior. Includes TTY session…

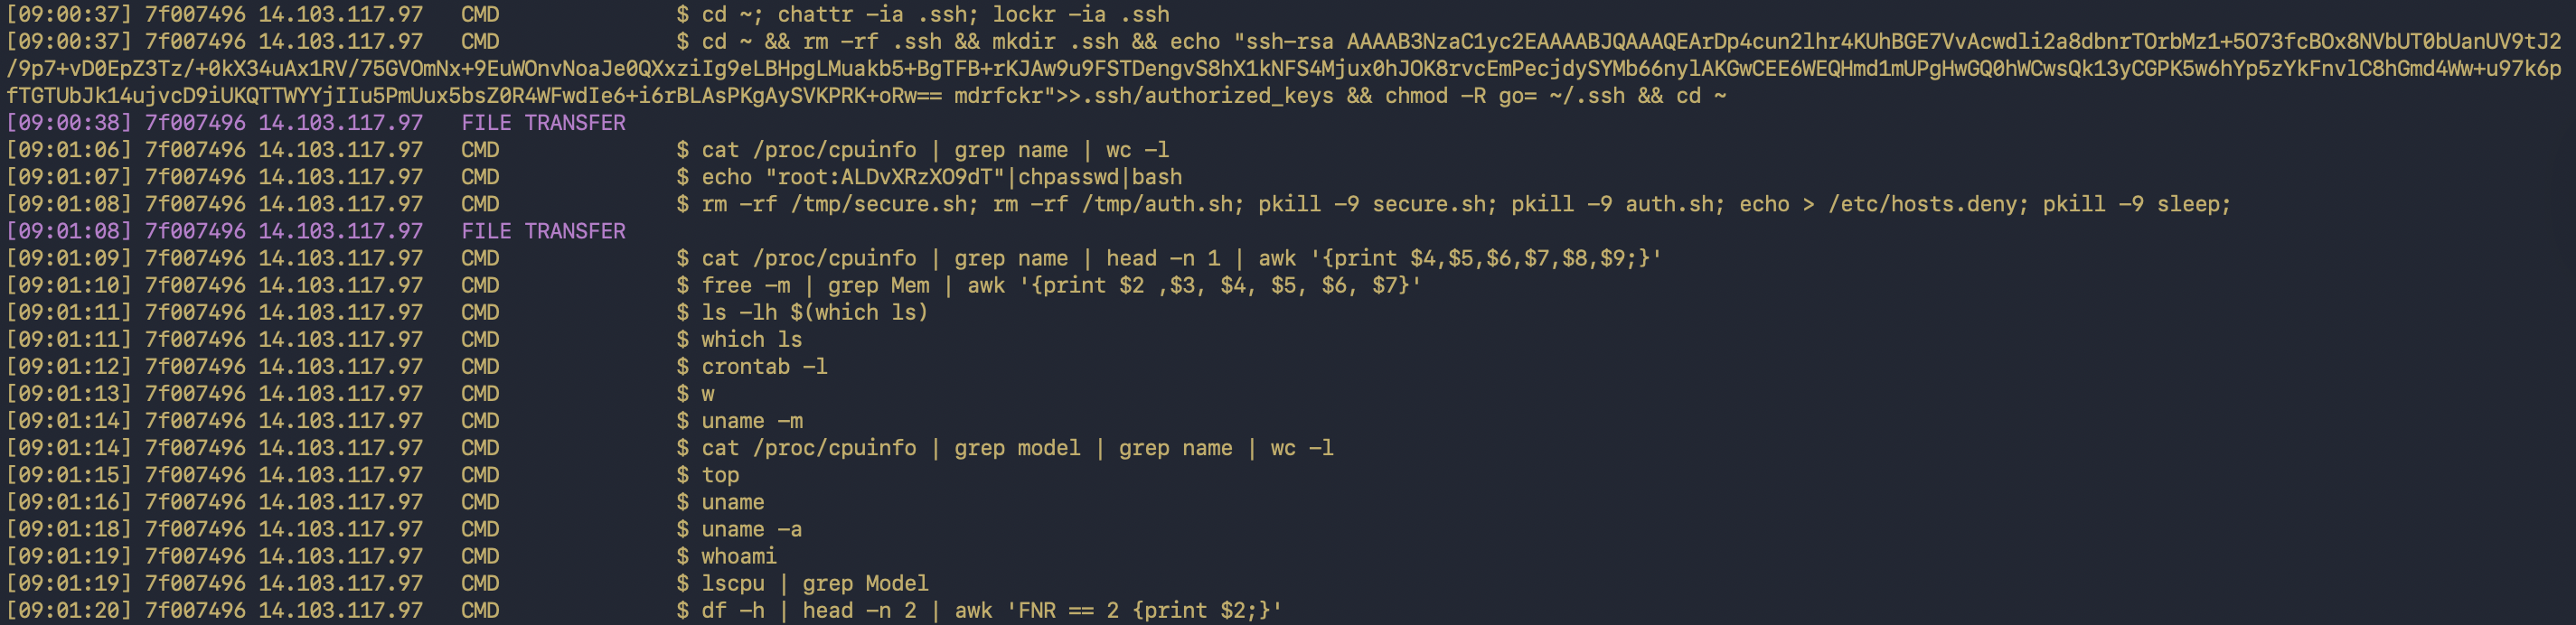
Performed a live cybersecurity assessment on a university Linux server. During analysis, active attack activity was identified, including brute-force…

Extract registry and NTDS secrets from local or remote disk images