Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
19 results
exchange_webshell_detection preview
Archived

exchange_webshell_detection

GitHubcert-lv/exchange_webshell_detection

Detect webshells dropped on Microsoft Exchange servers exploited through "proxylogon" group of vulnerabilites (CVE-2021-26855, CVE-2021-26857,…

forensicsincident-responseioc-management+3
98
5 years ago
security_monkey preview
Archived

security_monkey

GitHubnetflix/security_monkey

Security Monkey monitors AWS, GCP, OpenStack, and GitHub orgs for assets and their changes over time.

cloud-infrastructure-securitycloud-securityconfiguration-auditing+3
4.4k5 years ago
varc preview
Archived

varc

GitHubcado-security/varc

Volatile Artifact Collector collects a snapshot of volatile data from a system. It tells you what is happening on a system, and is of particular use…

cloud-securitycontainer-securitydigital-forensics+3
2541 year ago
malware-iocs preview

malware-iocs

GitHubdoctorwebltd/malware-iocs

Curated Indicators of Compromise (IOCs) from Doctor Web malware investigations, published for threat intelligence, detection engineering, and…

curated-resourcesforensicsincident-response+4
2441 month ago
Detection preview

Detection

GitHubsifalcon/detection

Curated collection of detection rules and IOCs extracted from DFIR engagements and malware analyses to support threat hunting, incident response, and…

curated-resourcesdigital-forensicsincident-response+4
243 years ago
CVE-2024-3400 preview

CVE-2024-3400

GitHubswaybs/cve-2024-3400

Python script to check Palo Alto firewalls for CVE-2024-3400 exploit attempts

exploitationincident-responseioc-management+3
22 years ago
DetectionLabELK preview

DetectionLabELK

GitHubcyberdefenders/detectionlabelk

DetectionLabELK is a fork from DetectionLab with ELK stack instead of Splunk.

configuration-auditingdefensive-toolsdigital-forensics+7
5785 years ago
sectemplates preview

sectemplates

GitHubsecuritytemplates/sectemplates

Open source templates you can use to bootstrap your security programs

configuration-auditingcurated-resourceseducation+3
9172 months ago
passivedns preview

passivedns

GitHubgamelinux/passivedns

A network sniffer that logs all DNS server replies for use in a passive DNS setup

dns-analysisforensicsincident-response+3
1.7k10 days ago
sshesame preview

sshesame

GitHubjaksi/sshesame

An easy to set up and use SSH honeypot, a fake SSH server that lets anyone in and logs their activity

defensive-toolsincident-responseinformation-gathering+4
1.8k2 years ago
CVE-2022-26134-Exploit-Detection preview

CVE-2022-26134-Exploit-Detection

GitHubma1am/cve-2022-26134-exploit-detection

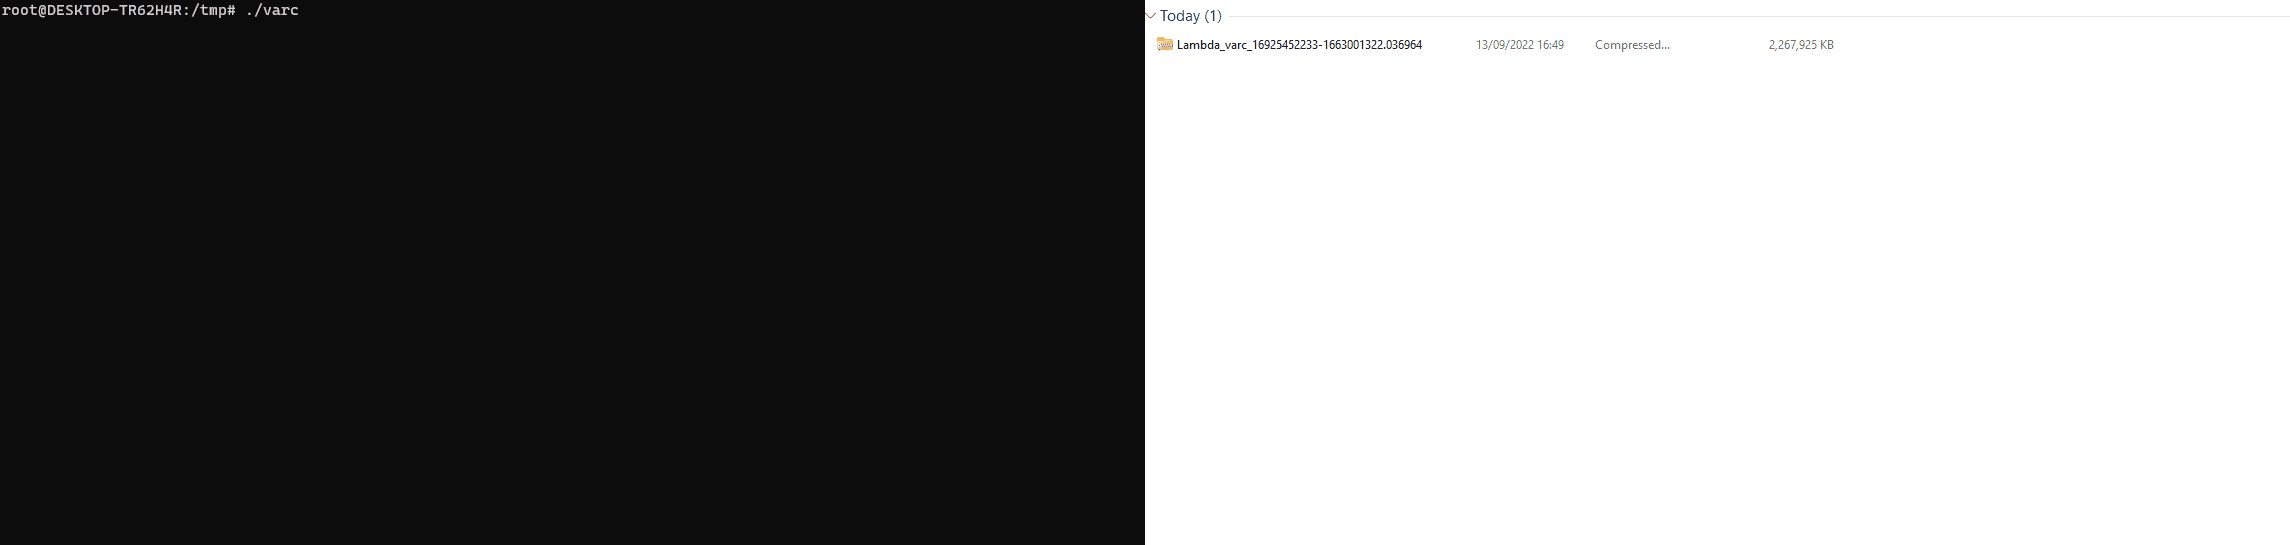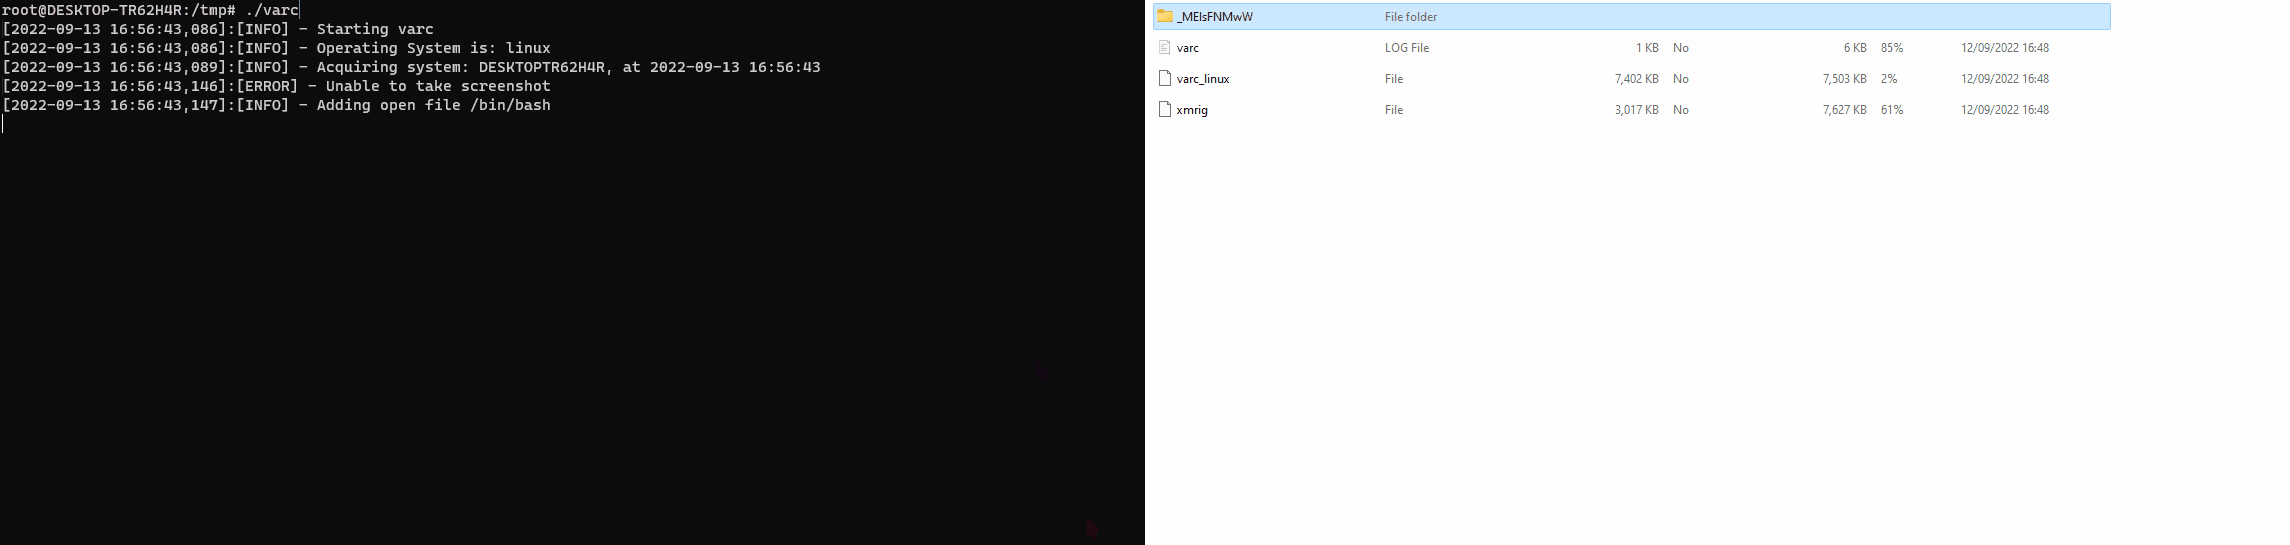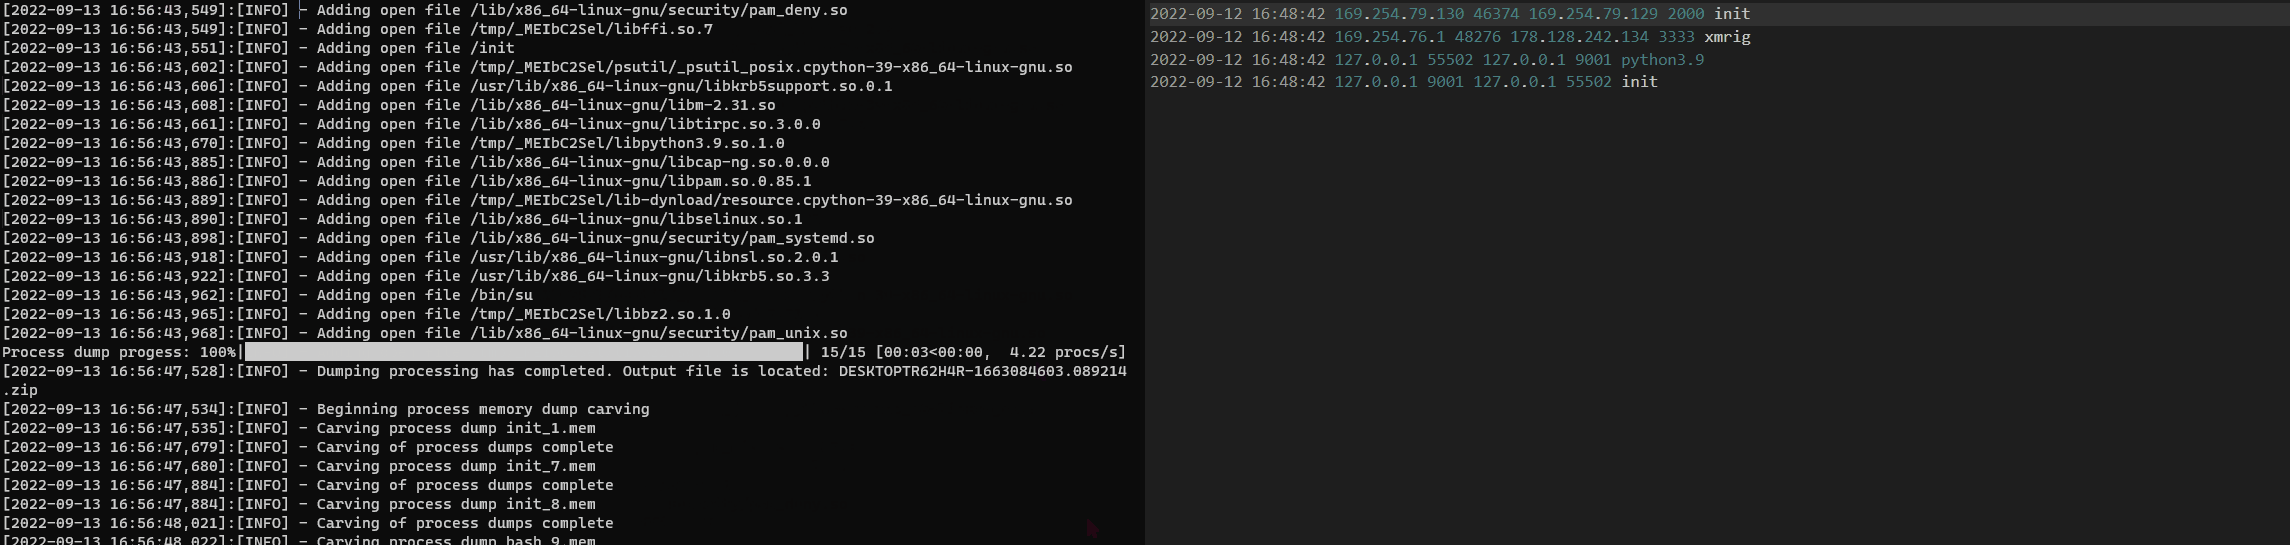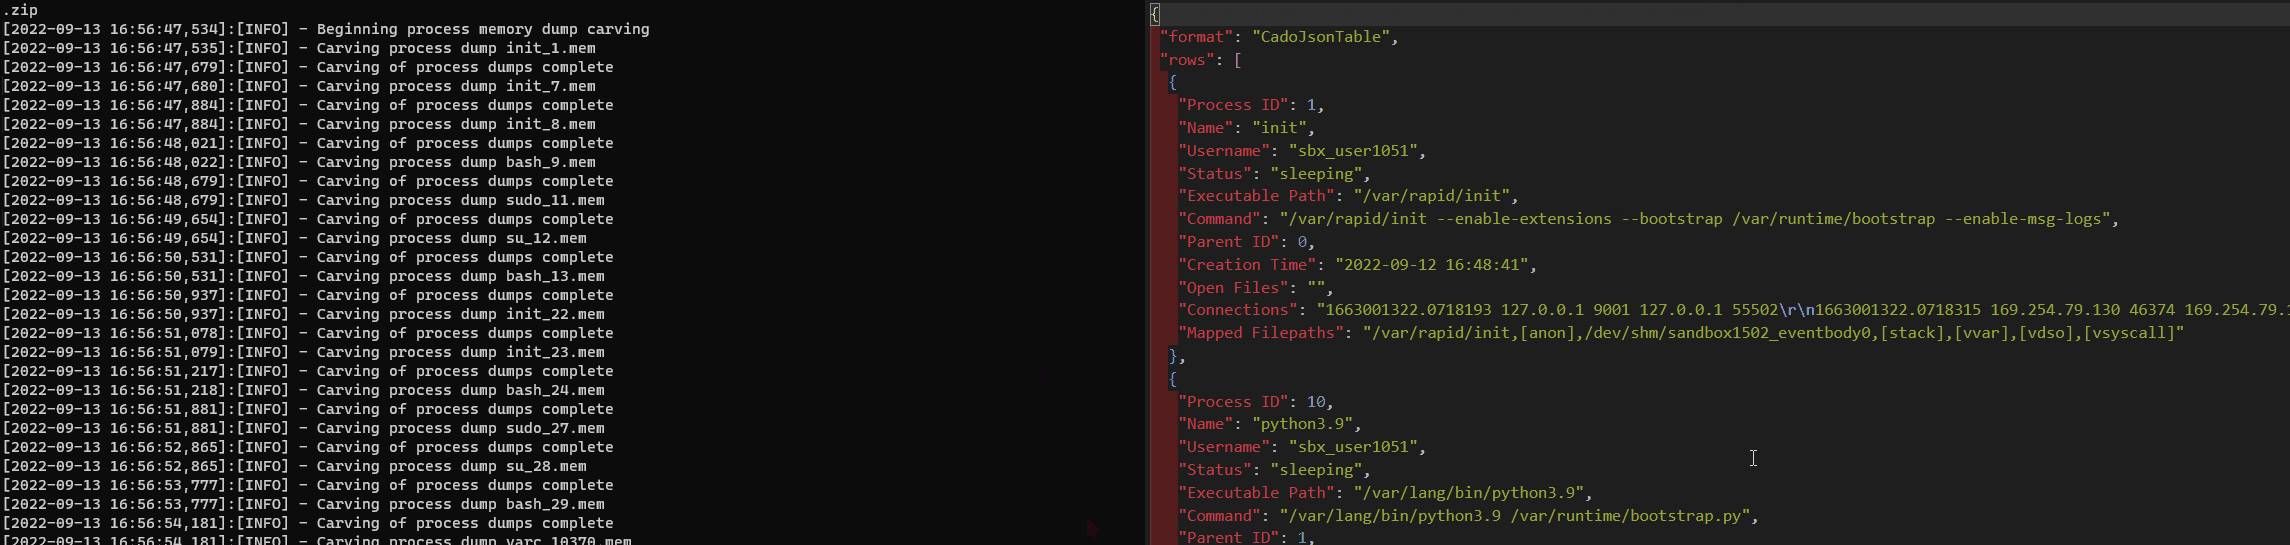
This repository contains Yara rule and the method that a security investigator may want to use for CVE-2022-26134 threat hunting on their Linux…

forensicsincident-responseioc-management+3
14 years ago
tanstack-compromise-checker preview

tanstack-compromise-checker

GitHubry-allan/tanstack-compromise-checker

Detects CVE-2026-45321 (TanStack supply chain compromise) and Mini Shai-Hulud worm artifacts. Scans node_modules, lockfiles, persistence hooks…

command-and-controlforensicsincident-response+6
5 months ago
FLAIR preview

FLAIR

GitHubwithsecurelabs/flair

Lightweight batch script for semi-automated acquisition of key forensic artefacts from Windows hosts, using only native OS tools to support incident…

digital-forensicsforensicsincident-response+2
165 years ago
dfirtriage preview

dfirtriage

GitHubtravisfoley/dfirtriage

Digital forensic acquisition tool for Windows based incident response.

digital-forensicsforensicsincident-response+1
3482 years ago
UninstalledAppCanary preview

UninstalledAppCanary

GitHubnccgroup/uninstalledappcanary

A Canary which fires when uninstalled

defensive-toolsincident-responseintrusion-detection
345 years ago
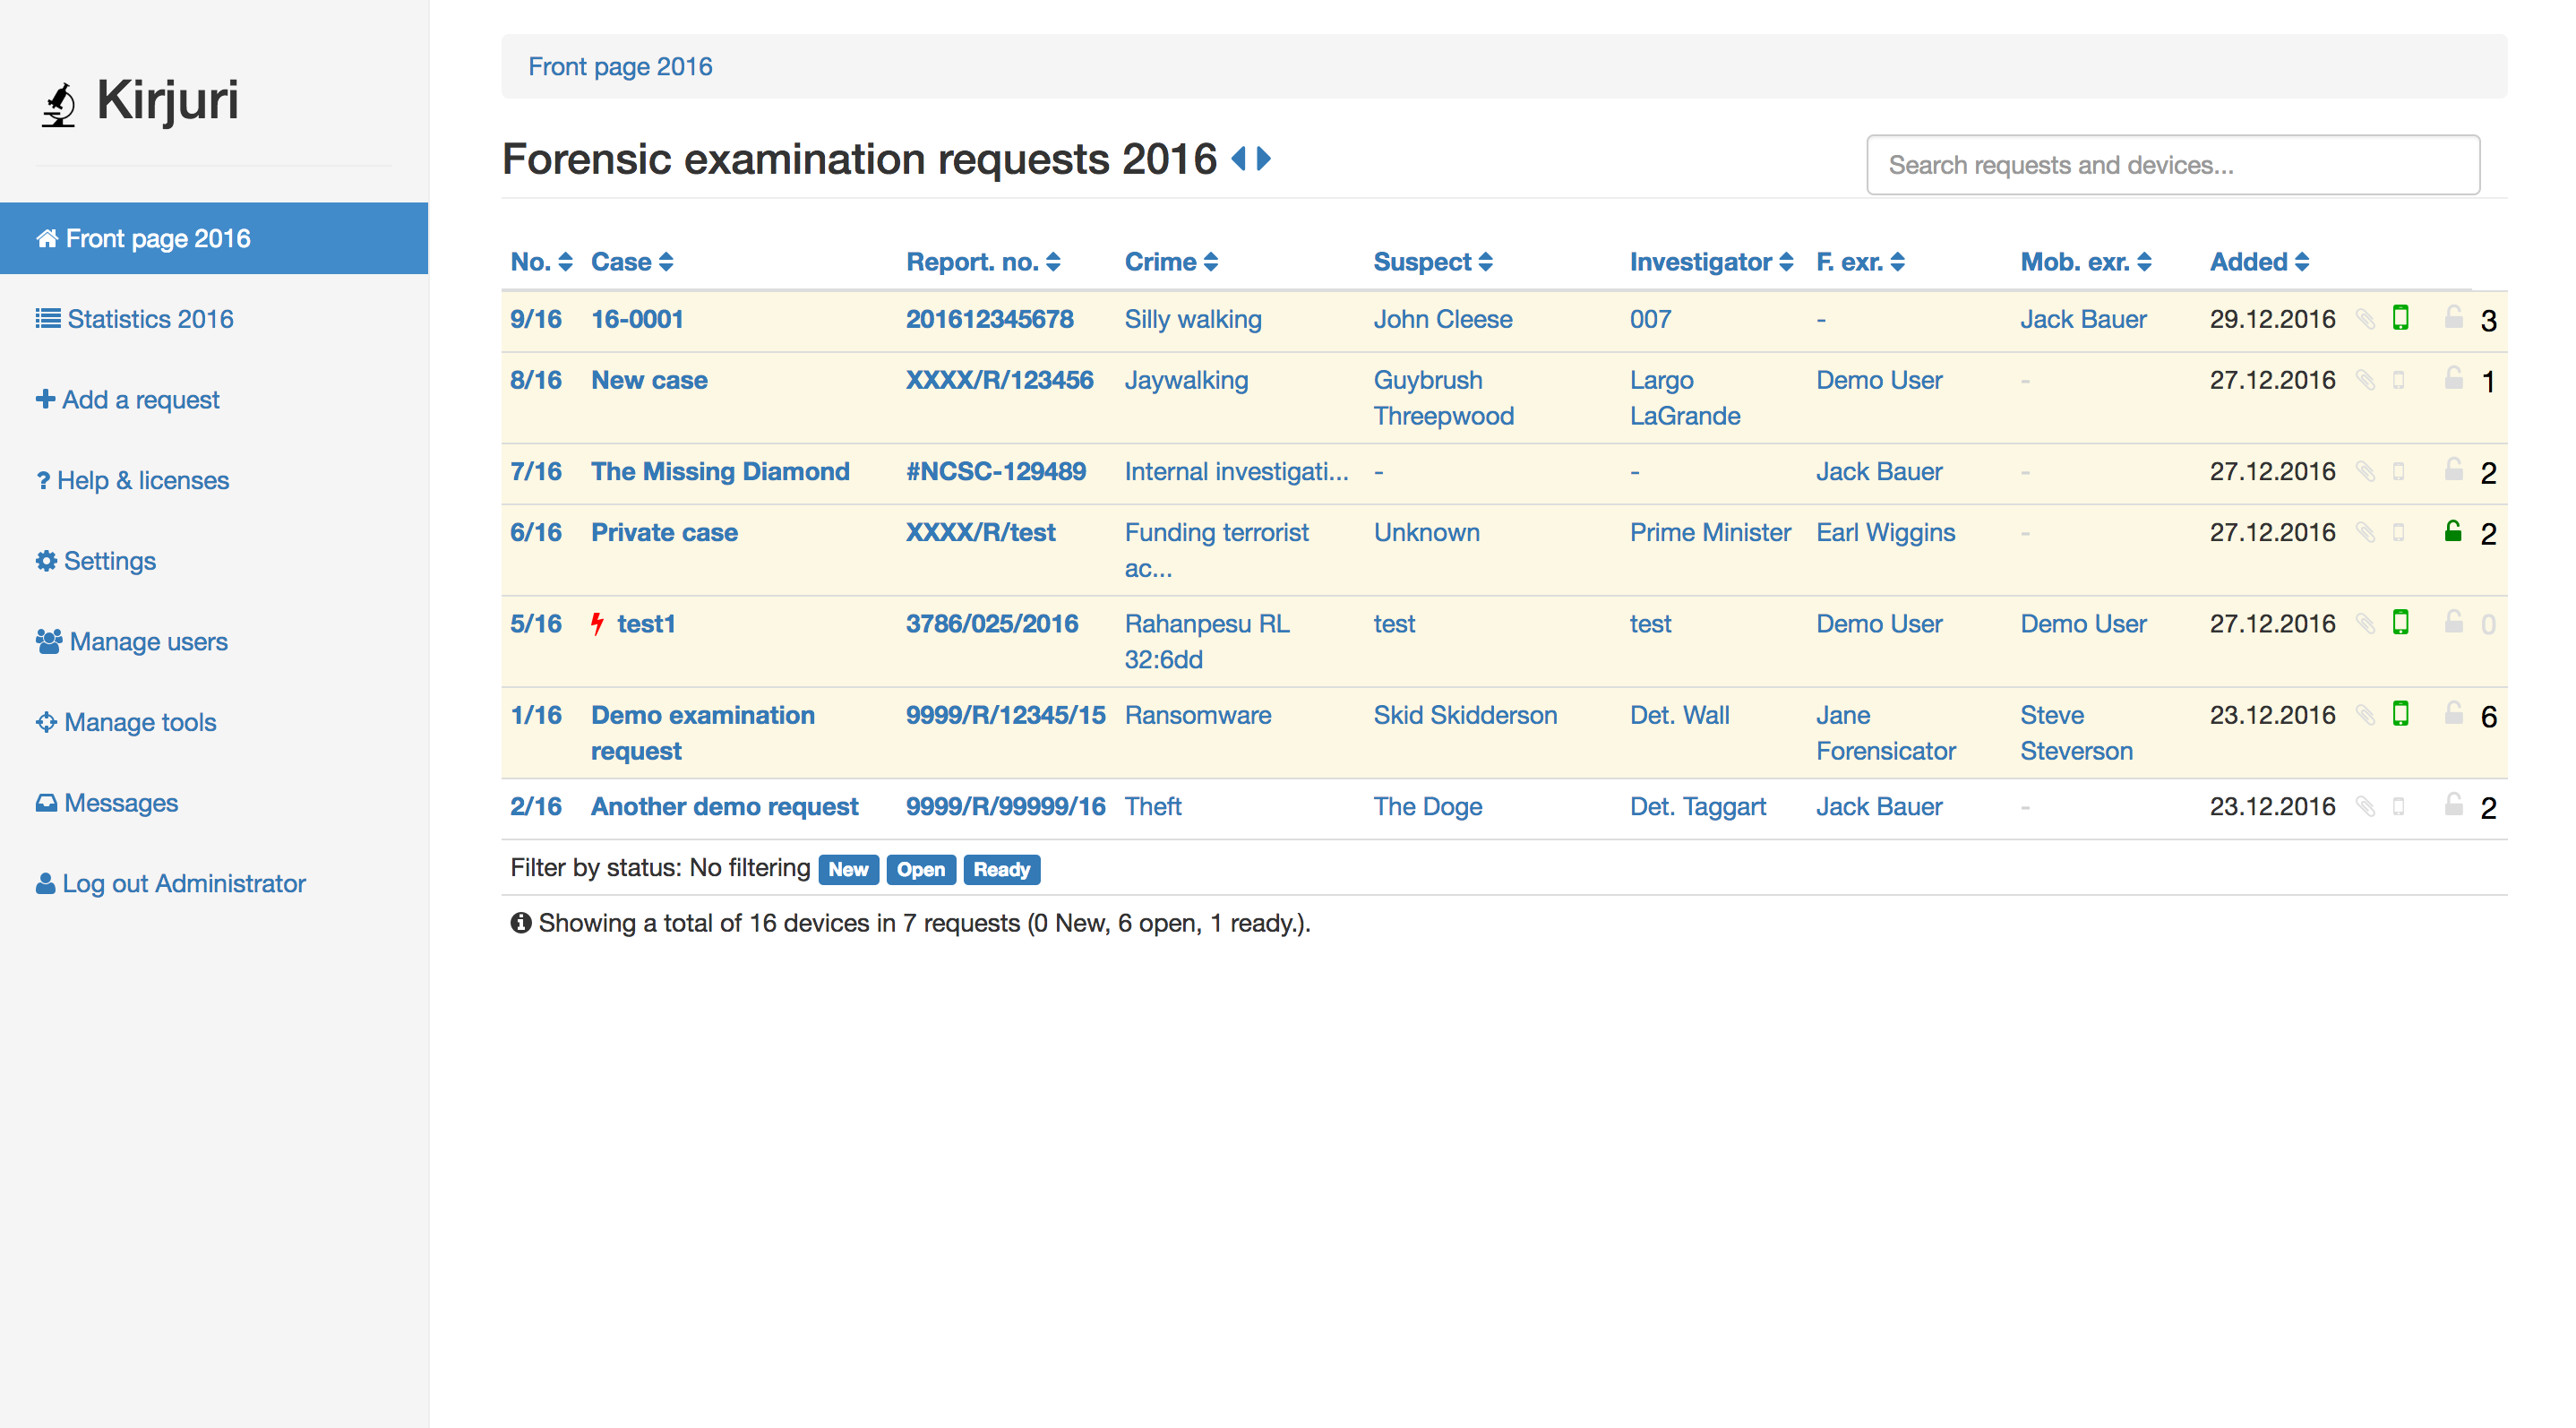
kirjuri preview
Archived

kirjuri

GitHubanttikurittu/kirjuri

Kirjuri is a web application for managing cases and physical forensic evidence items.

digital-forensicsforensicsincident-response
1095 months ago
IRM preview

IRM

GitHubcertsocietegenerale/irm

Incident Response Methodologies 2022

curated-resourceseducationincident-response
1.1k1 year ago
LSMS preview

LSMS

GitHubsqall01/lsms

Linux Security and Monitoring Scripts

defensive-toolsforensicsincident-response+2
3311 year ago
Previous12Next