
honeyLambda
 0x4d31/honeylambda
honeyλ - a simple, serverless application designed to create and monitor fake HTTP endpoints (i.e. URL honeytokens) automatically, on top of AWS…
cloud-securitydefensive-toolsincident-response+2
525
0x4d31/honeylambdahoneyλ - a simple, serverless application designed to create and monitor fake HTTP endpoints (i.e. URL honeytokens) automatically, on top of AWS…
 invoke-ir/ace
Automated, Collection, and Enrichment Platform
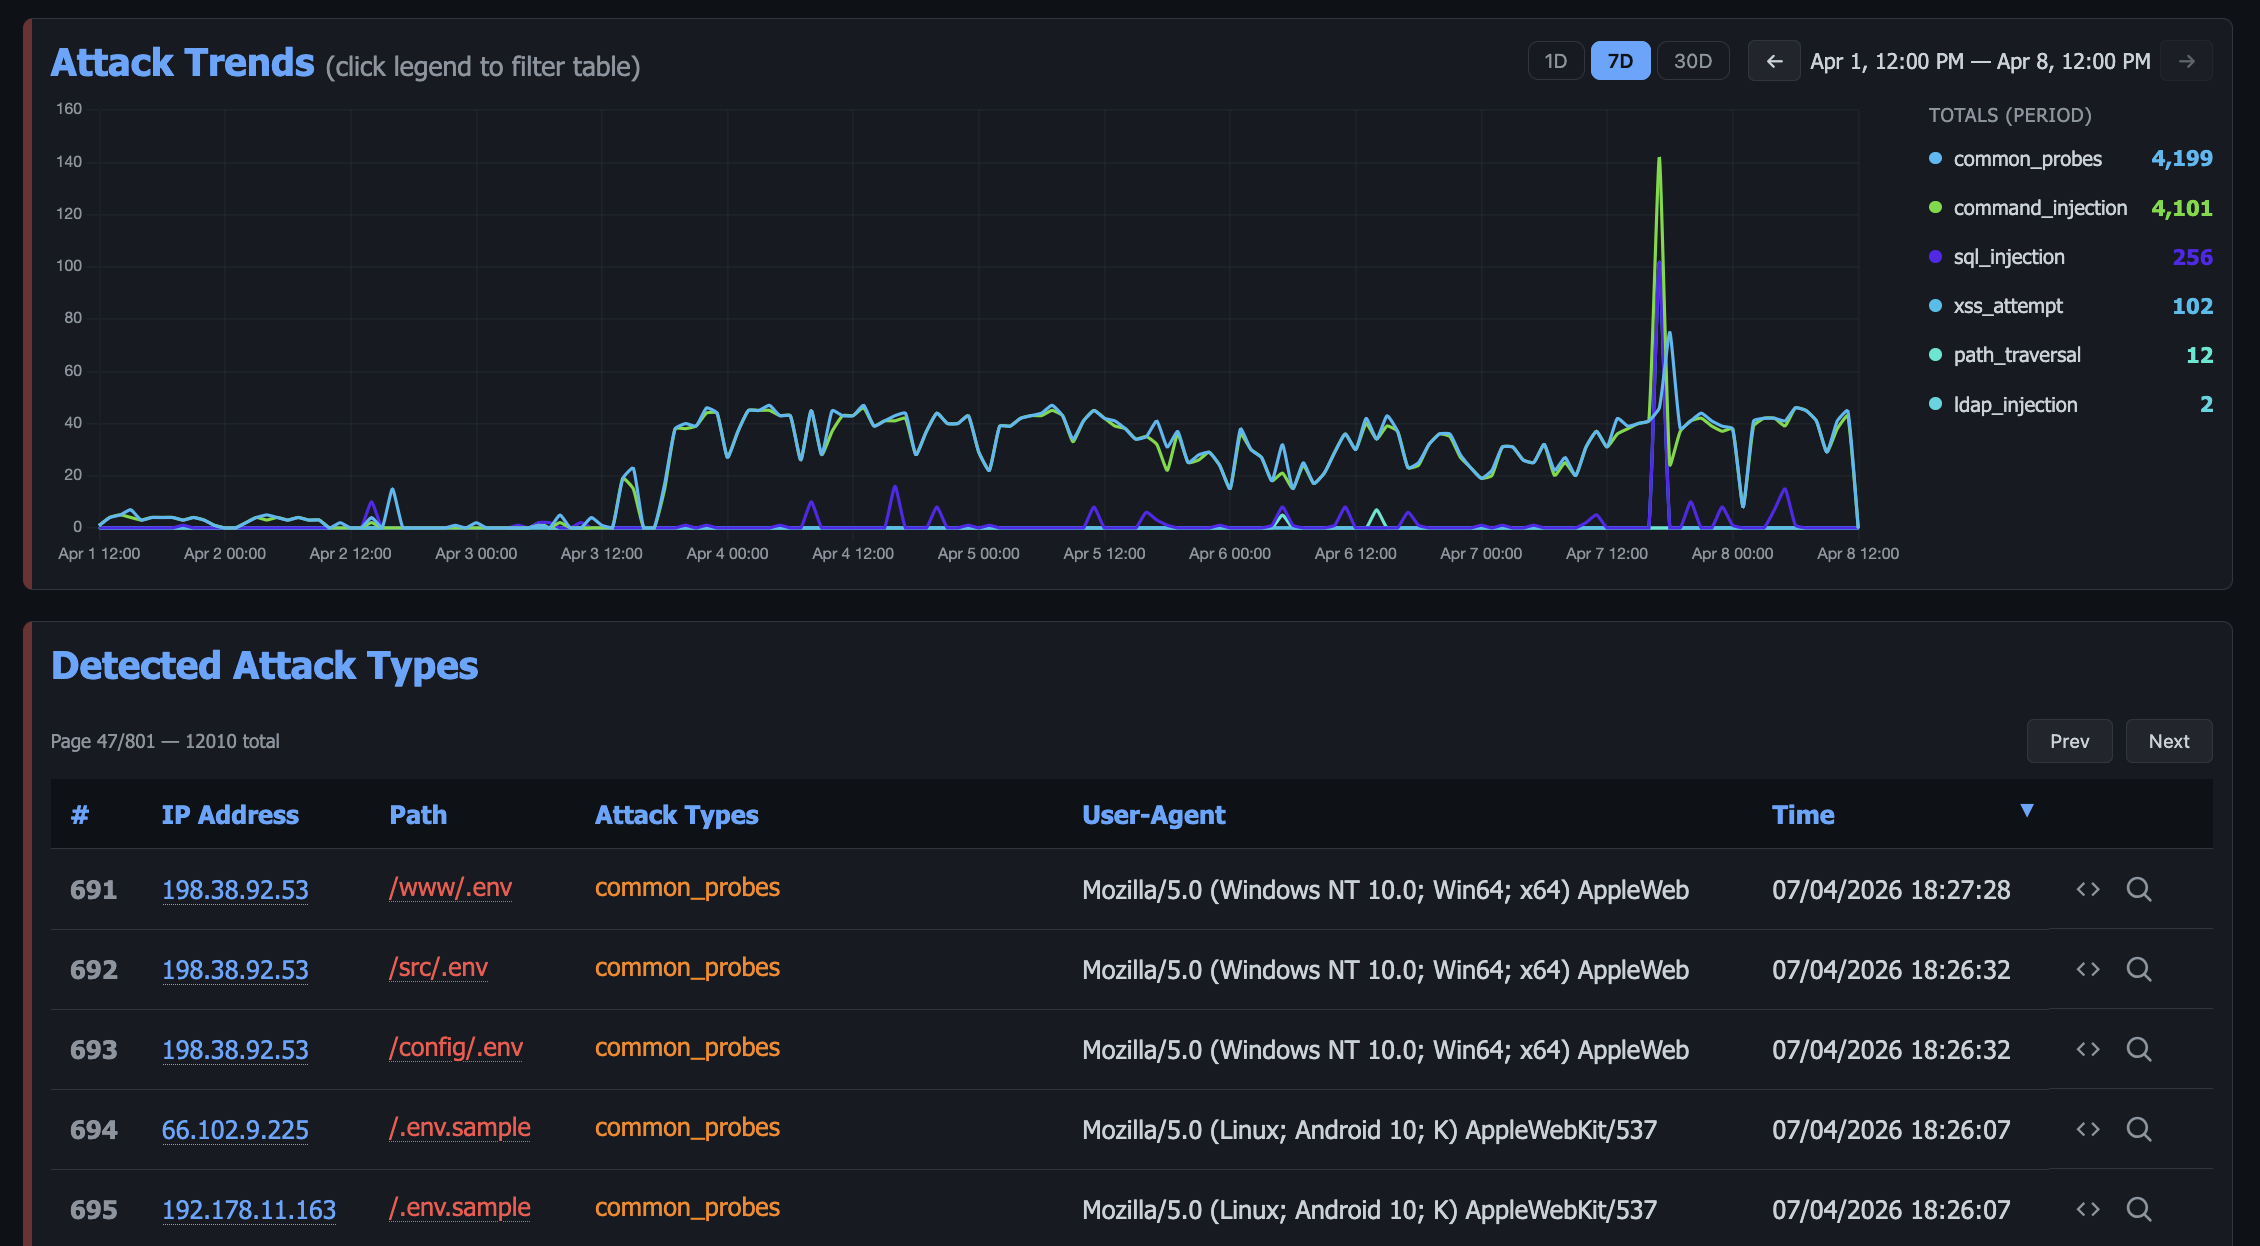 blessedrebus/krawl
Krawl is a customizable, lightweight, cloud-native web deception server and anti-crawler that creates fake web applications with low-hanging…
 swimlane/soc-faker
A python package for use in generating fake data for SOC and security automation.
 serpilrivas/log4shell-homework9
Log4Shell (CVE-2021-44228) exploit demo for SEAS 8405. Includes a vulnerable Spring Boot app, fake LDAP server, Docker setup, MITRE mapping, incident…
 mrk336/kernel-chaos-weaponizing-cve-2025-62215-for-system-privilege-escalation
Hands‑on analysis of CVE‑2025‑62215, a Windows Kernel race condition exploited in the wild. Demonstrates privilege escalation to SYSTEM, detection…
 gosecure/pyrdp
RDP monster-in-the-middle (mitm) and library for Python with the ability to watch connections live or after the fact
 karmanyat28/multi-stage-exploitation-and-detection-engineering-analysis-of-cve-2023-34362-in-moveit-transfer
This repository contains an academic and technical analysis of CVE-2023-34362, a critical SQL injection vulnerability affecting the MOVEit Transfer…
 grizzzer/cve-2026-42978-poc-research
CVE-2026-42978 — Use-After-Free race condition in Windows Push Notifications (WpnService). Patch diff, root cause analysis, TOCTOU lab, Sysmon/ETW…
 v-pun215/tourmaline
Reverse engineering notes, deobfuscated source, IOCs, and YARA rules for the Tourmaline ClickFix Python RAT, covering its DNS tunnel and blockchain…
 lukeslp/redtail-ioc
IOCs and a read-only triage checklist from a real Linux root compromise: RedTail miner, XorDDoS persistence, MoneroOcean miner, DirtyFrag LPE…
 bushidouk/ransomware-tool-matrix
A resource containing all the tools each ransomware gangs uses
 otrf/set-auditrule
Useful access control entries (ACE) on system access control list (SACL) of securable objects to find potential adversarial activity
 arch1m3d/miniplasma-detection
Sigma detection rule for MiniPlasma (CVE-2020-17103)