

Live-Forensicator
 johnng007/live-forensicator
Cross-platform incident response and live forensics toolkit with built-in detection, structured analysis, and report generation — designed for fast,…
incident-response
johnng007/live-forensicatorCross-platform incident response and live forensics toolkit with built-in detection, structured analysis, and report generation — designed for fast,…
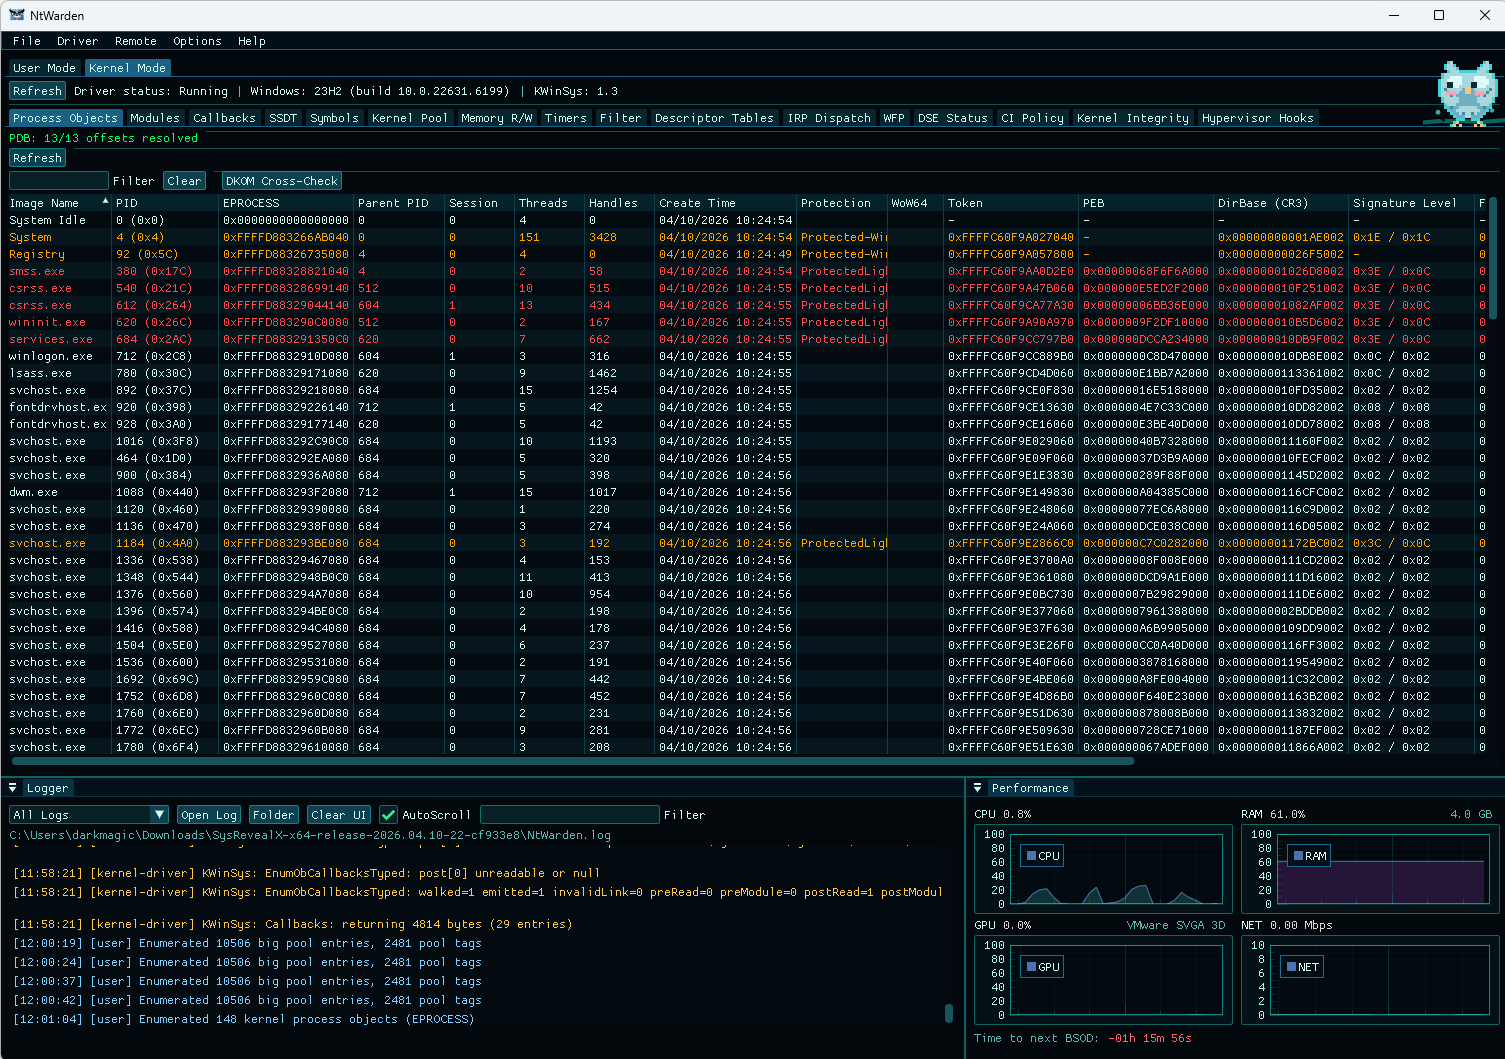 mrt4ntr4/ntwarden
Windows Analysis and Research Toolkit
 forensicmatt/rswindowsthingies
Rust-based Windows forensic toolkit for real-time MFT monitoring, event log streaming, and channel enumeration, enabling live system analysis and…
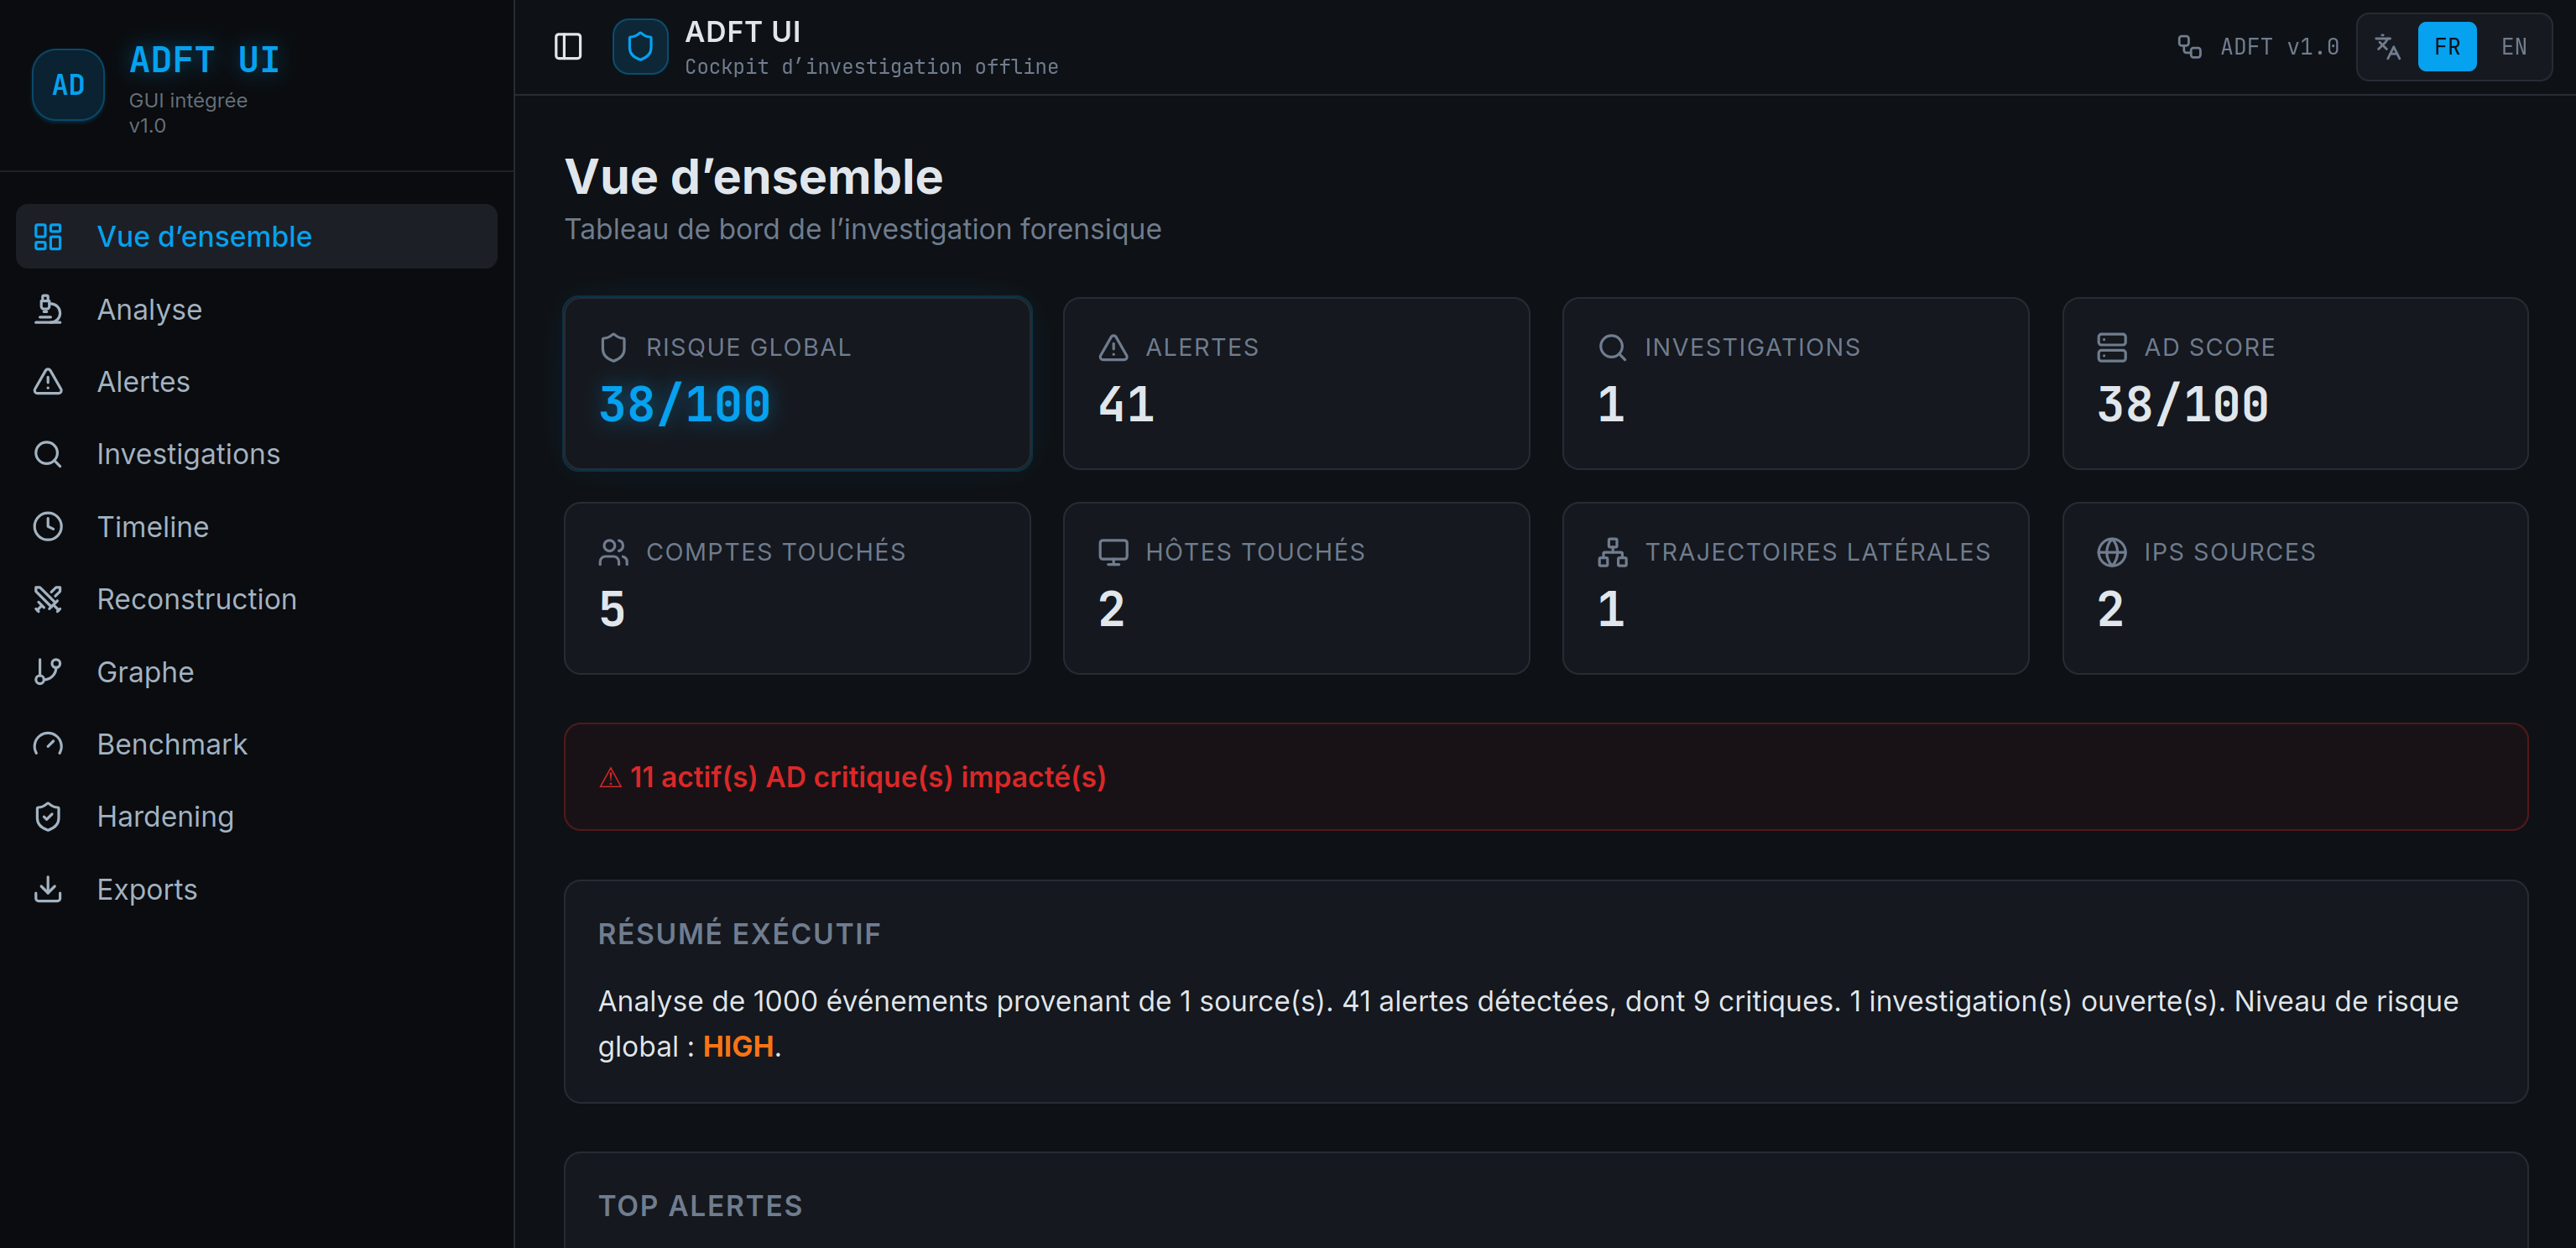 kjean13/adft
Active Directory Forensic Toolkit : Detect & reconstruct AD attacks from Windows event logs (EVTX)
 kfallahi/underlaycopy
PowerShell toolkit that extracts locked Windows files (SAM, SYSTEM, NTDS, ...) using MFT parsing and raw disk reads
 dsnezhkov/racketeer
Agent-based ransomware simulation toolkit for controlled detection testing across Windows endpoints and network assets, with a cross-platform…
 creamyg31337/ncentral-compromise-ioc-triage
Read-only N-able N-central CVE-2026-18556/CVE-2026-18577 post-exploitation IoC hunter for Windows endpoints
 osbornepro/btps-secpack
PowerShell-based security toolkit for small-to-medium enterprises, providing automated alerts, Active Directory hardening, Windows Event Forwarding,…
 rails/rails-forensics-cve-2026-66066
Forensic toolkit and agent skills for investigating Rails Active Storage/libvips CVE-2026-66066: detects crafted blob indicators, exposure windows,…
 bert-janp/incident-response-powershell
PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…
 warpedatom/offsetinspect
PowerShell toolkit for AMSI/Defender detection-boundary analysis and static malware triage maps byte offsets to detection triggers, plus YARA,…
 daryllundy/cve-2025-32711
PowerShell-based detection and remediation toolkit for CVE-2025-32711 (EchoLeak), a critical zero-click AI command injection vulnerability in…
 cristianzsh/forensictools
Collection of forensic tools
 rushyo/vindicatetool
LLMNR/NBNS/mDNS Spoofing Detection Toolkit
 virologi-info/papercut-toolkit
#PaperCut CVE-2026-81578 + CVE-2026-82078 Defense Toolkit 2 3 A **defensive** toolkit to check and understand exposure to the chained
 bluefire-redteam-cybersecurity/bluefire-sharepoint-cve-2025-53770
Automated detection, assessment, and remediation toolkit for SharePoint CVE-2025-53770 (CVSS 9.8). Includes PowerShell scripts to verify patch…
 zenzue/cve-2025-50154
PowerShell toolkit to audit, harden, and hunt for insecure NTLM/SMB usage, addressing CVE-2025-50154 credential leak risks with event log analysis…
 jchable/miasma-toolkit
Detection & remediation toolkit for the Miasma / Shai-Hulud worm and CVE-2026-35603 (AI-agent/IDE config injection)