
detectree
 withsecurelabs/detectree
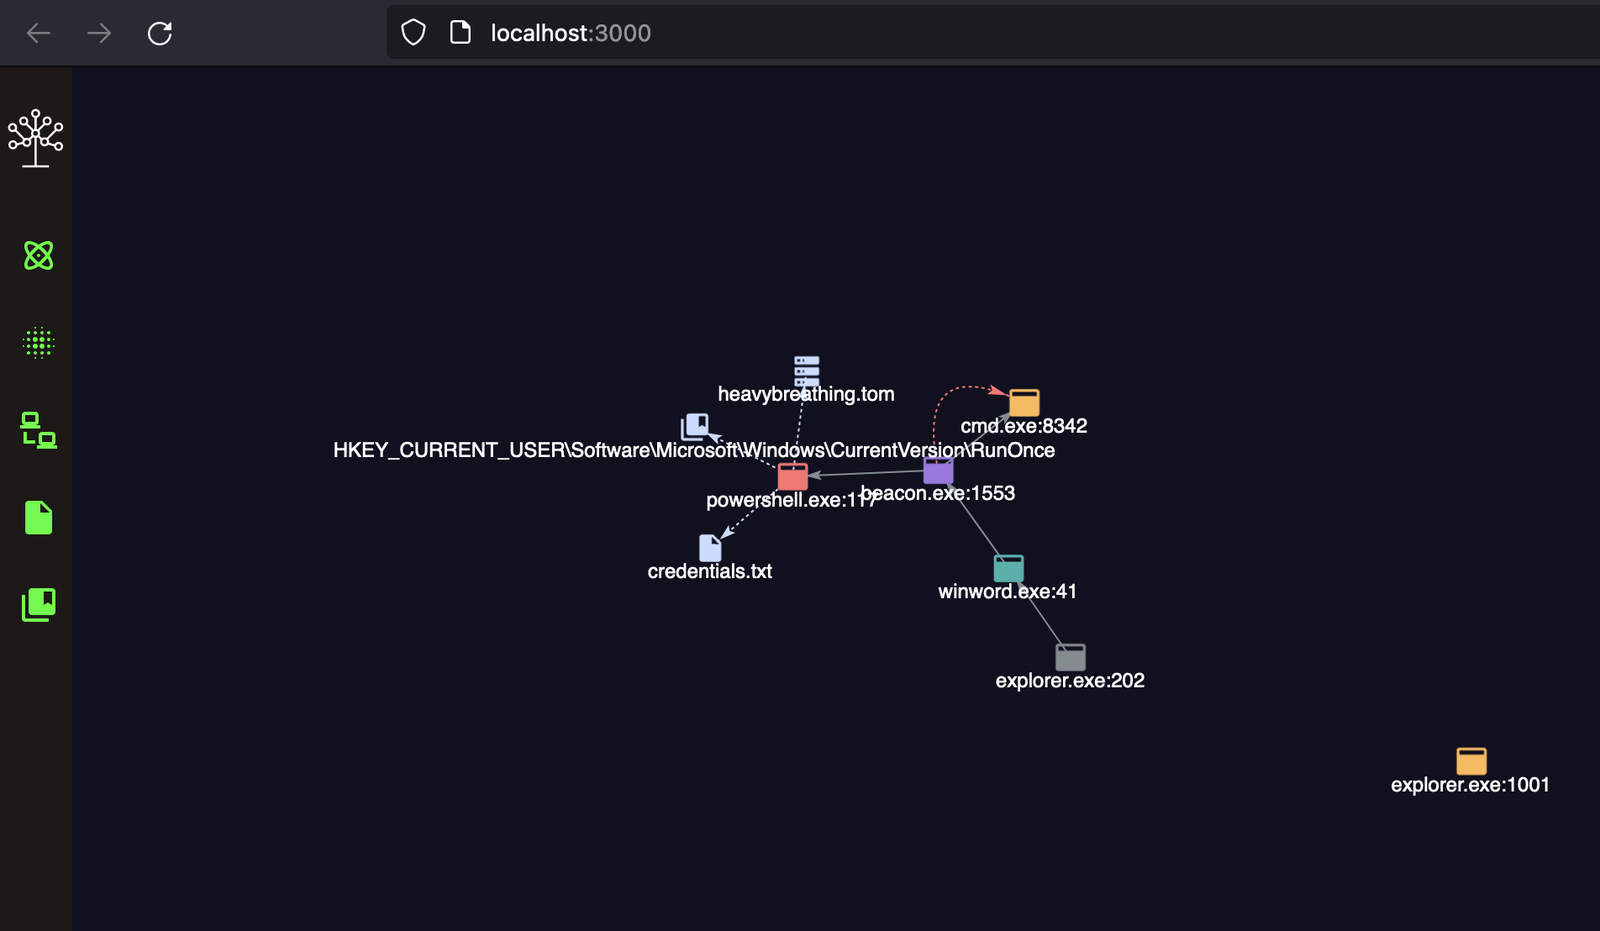
Interactive data visualization tool for blue teams to analyze detection data, understand relationships, reduce alert fatigue, and improve incident…
defensive-toolsincident-responselog-analysis+1
126
withsecurelabs/detectreeInteractive data visualization tool for blue teams to analyze detection data, understand relationships, reduce alert fatigue, and improve incident…
 letsdefendio/simple-live-data-collection
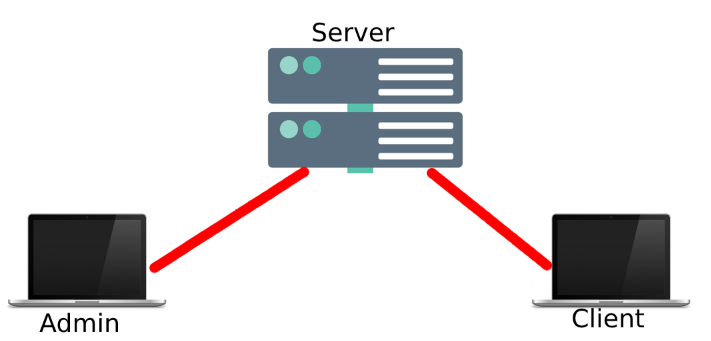
Client-server tool for live data collection during incident response. Admin sends requests to clients to gather system information for forensic…
 yampelo/beagle
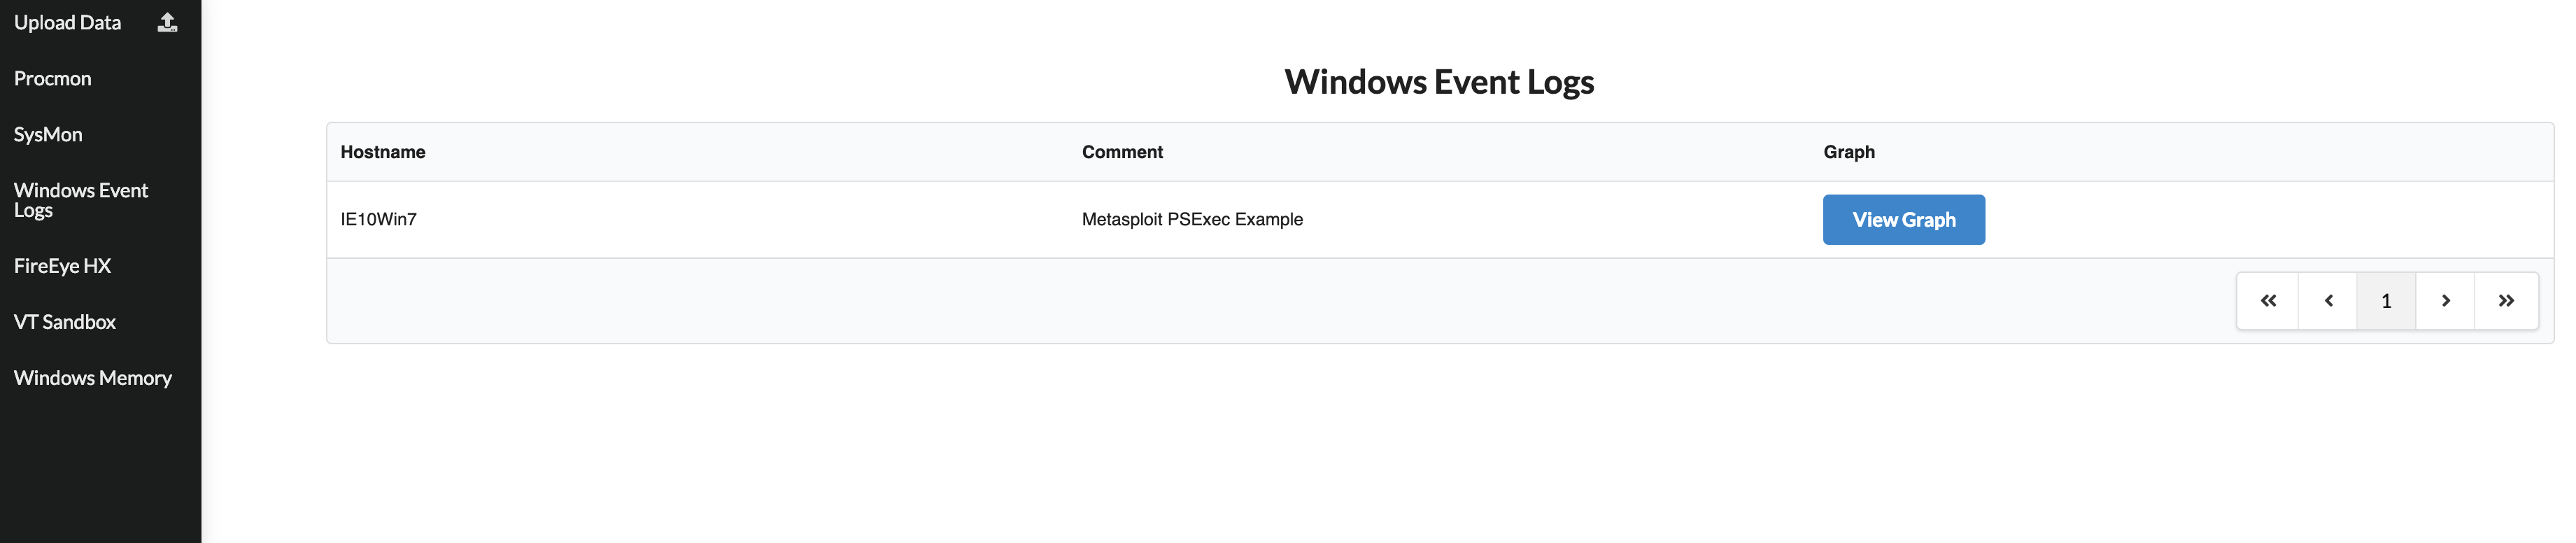
Beagle is an incident response and digital forensics tool which transforms security logs and data into graphs.
 neo23x0/mongobleed-detector
Detection Script for MongoBleed Exploitation
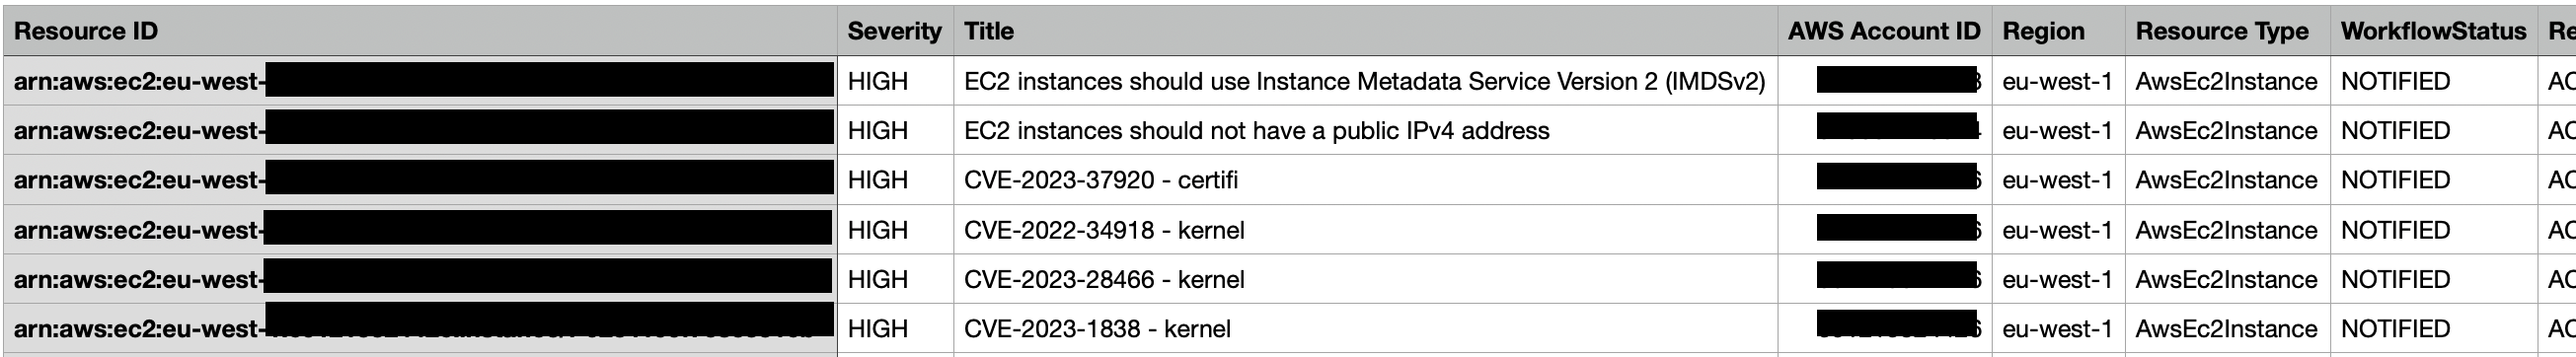 gabrielsoltz/metahub
Automated security findings enrichment and impact evaluation tool for AWS. Enriches vulnerability data with resource context, associations, and tags…
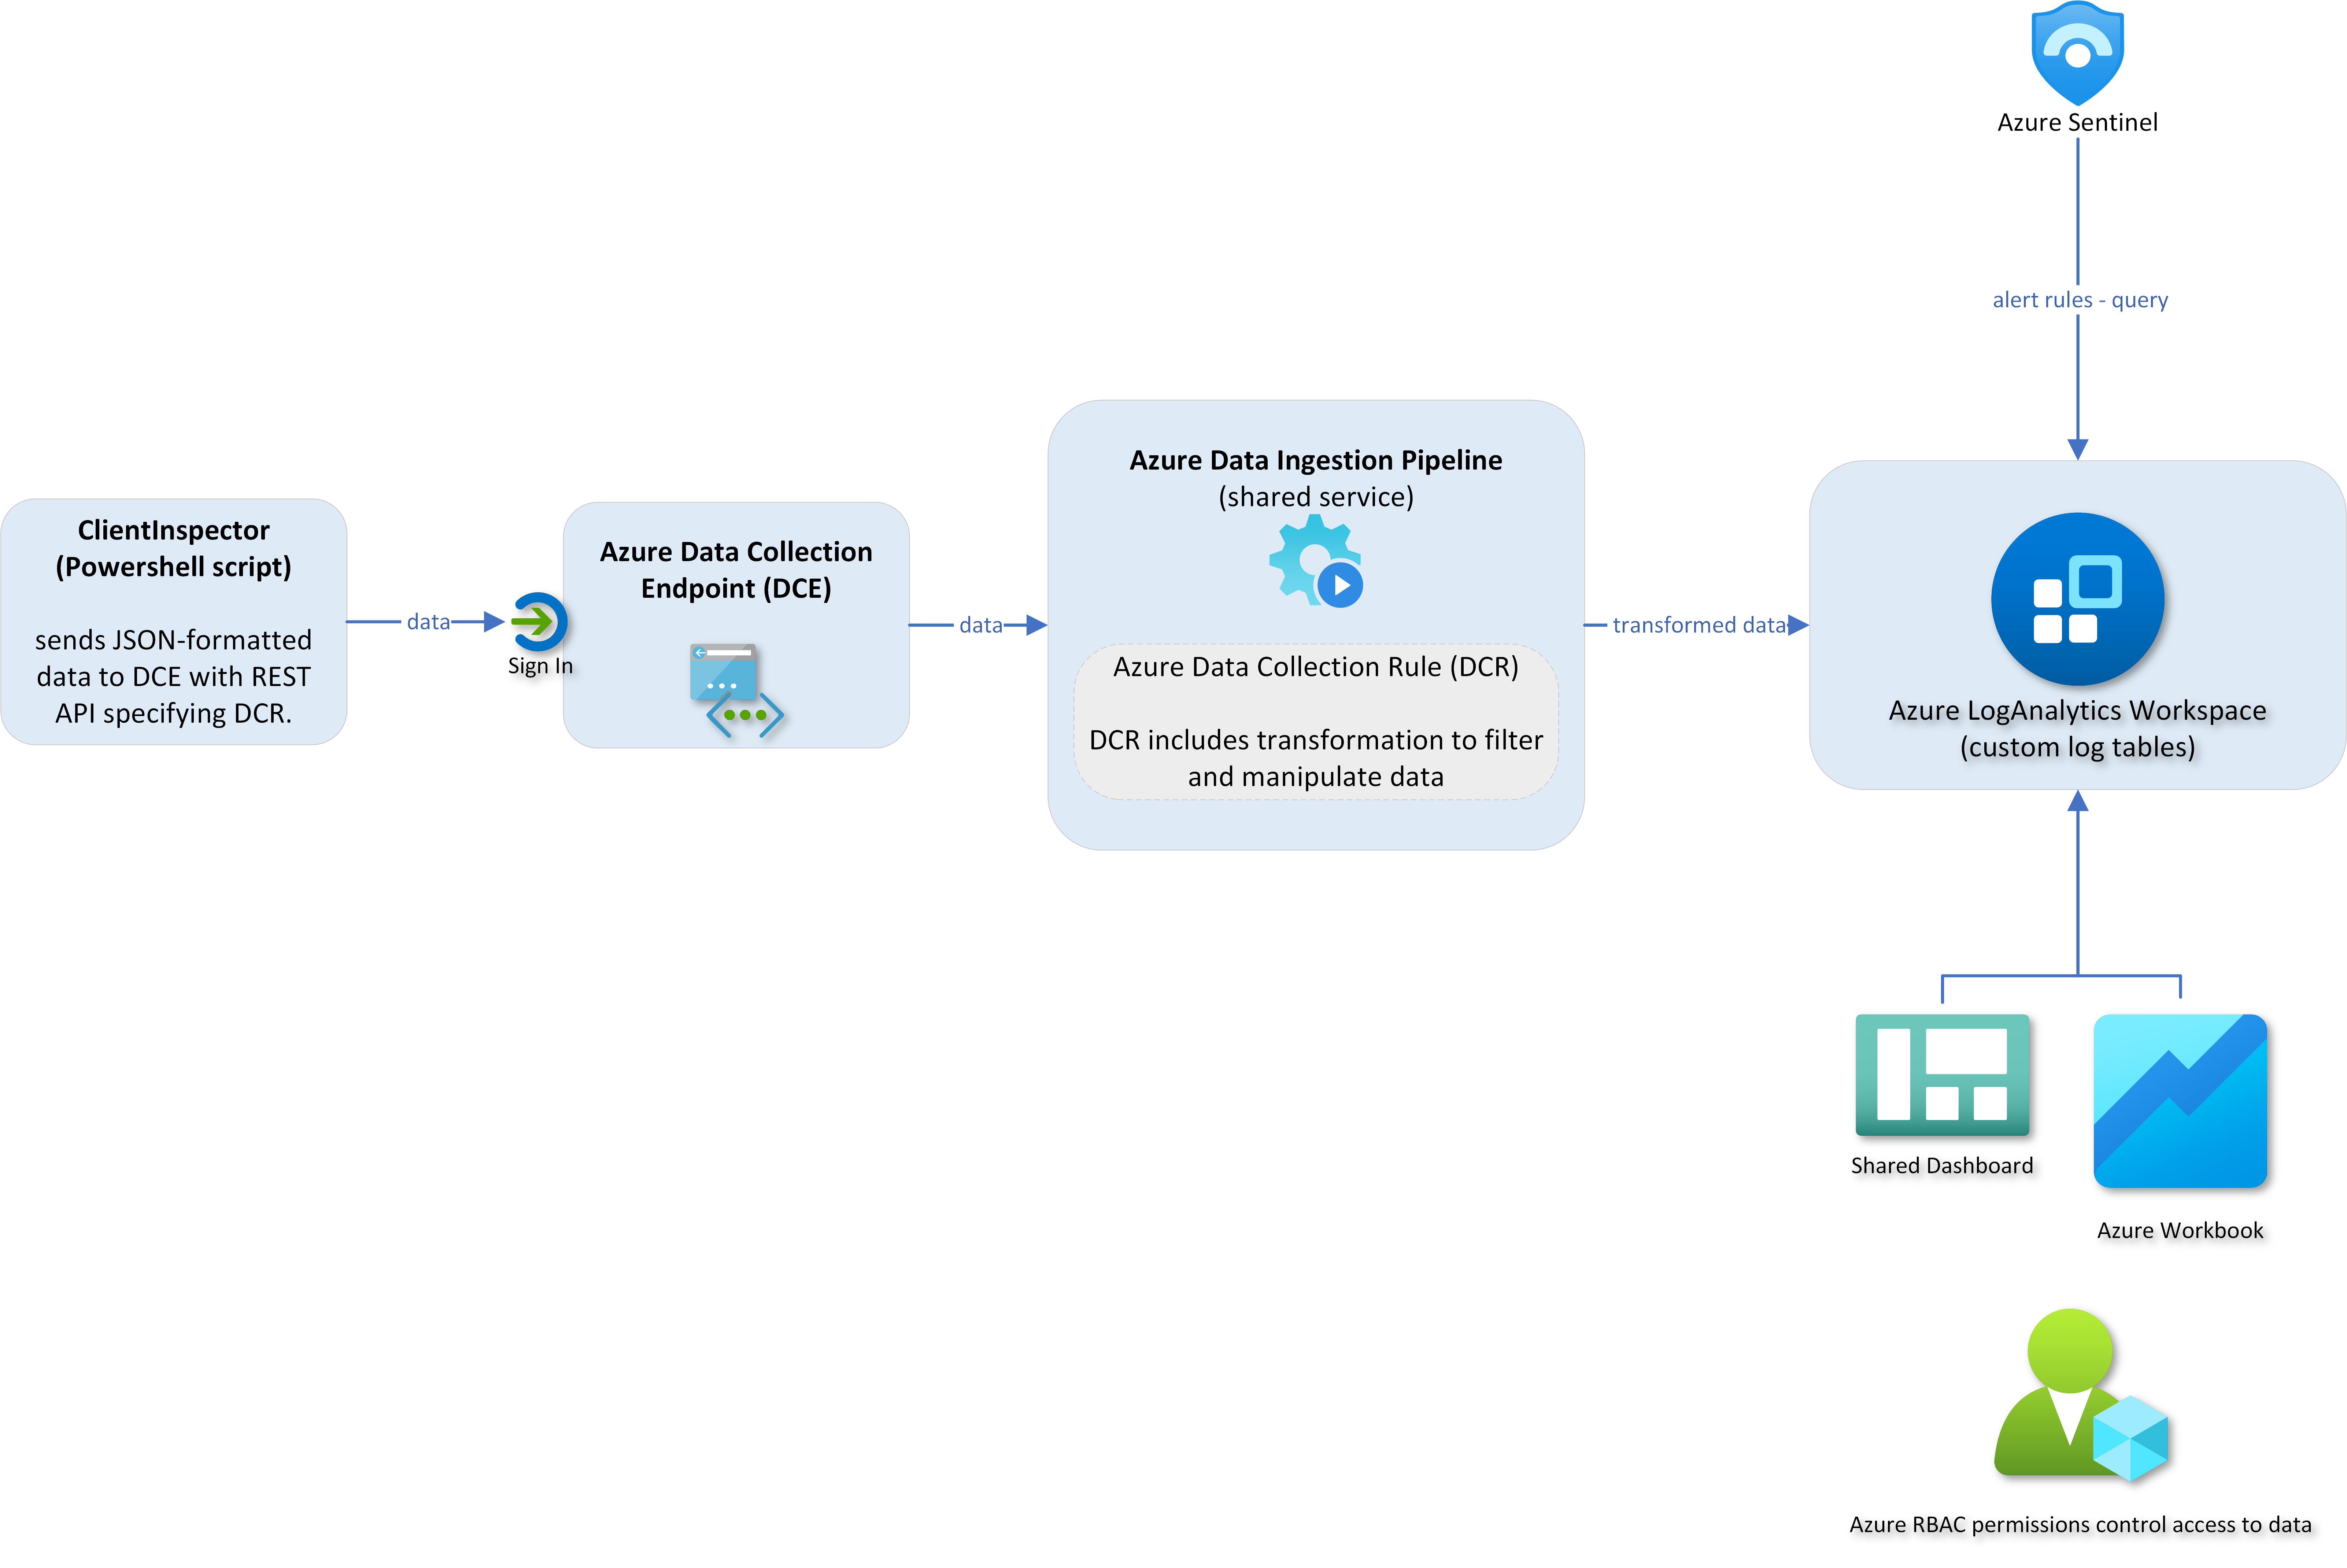 knudsenmorten/clientinspectorv2
Azure-based client inventory and drift detection tool that collects Windows configuration data (antivirus, patching, Bitlocker) into LogAnalytics for…
 st2labs/sipi
Simple IP Information Tools for Reputation Data Analysis
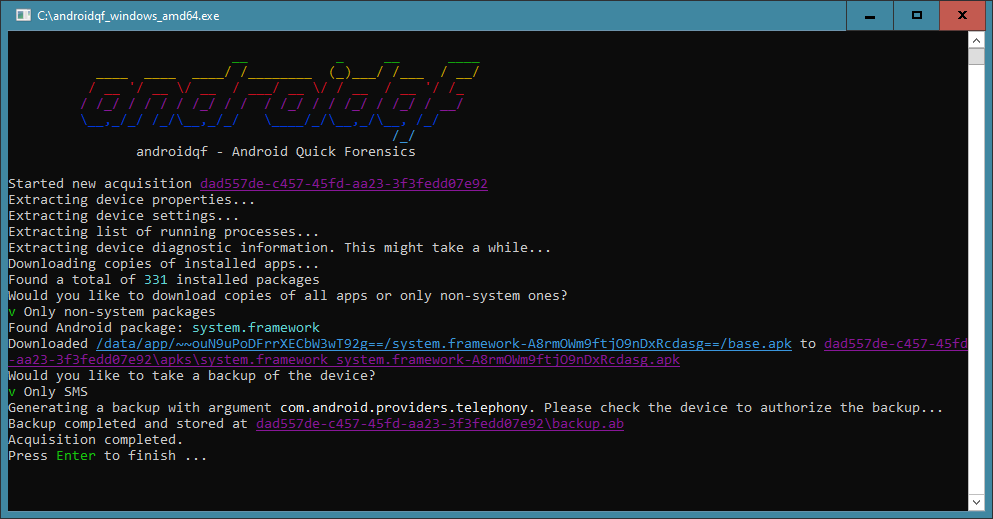 botherder/androidqf
Portable forensic acquisition tool for Android devices that collects relevant data via USB debugging to identify potential spyware or compromise…
 mvt-project/androidqf
androidqf (Android Quick Forensics) helps quickly gathering forensic evidence from Android devices, in order to identify potential traces of…
 invictus-ir/microsoft-extractor-suite
A PowerShell module for acquisition of data from Microsoft 365 and Azure for Incident Response and Cyber Security purposes.
 adamwhitehat/judge-jury-and-executable
A file system forensics analysis scanner and threat hunting tool. Scans file systems at the MFT and OS level and stores data in SQL, SQLite or CSV.…
 viralmaniar/ddwpasterecon
DDWPasteRecon tool will help you identify code leak, sensitive files, plaintext passwords, password hashes. It also allow member of SOC & Blue Team…
 wheezysec/cve-2021-44228-kusto
Kusto query-based detection and analysis tool for CVE-2021-44228 (Log4Shell) vulnerability, enabling rapid log hunting and exploitation…
 spamscanner/spamscanner
Spam Scanner is a Node.js anti-spam, email filtering, and phishing prevention tool and service. Built for @ladjs, @forwardemail, @cabinjs, @breejs,…
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
 jipegit/osxauditor
OS X Auditor is a free Mac OS X computer forensics tool
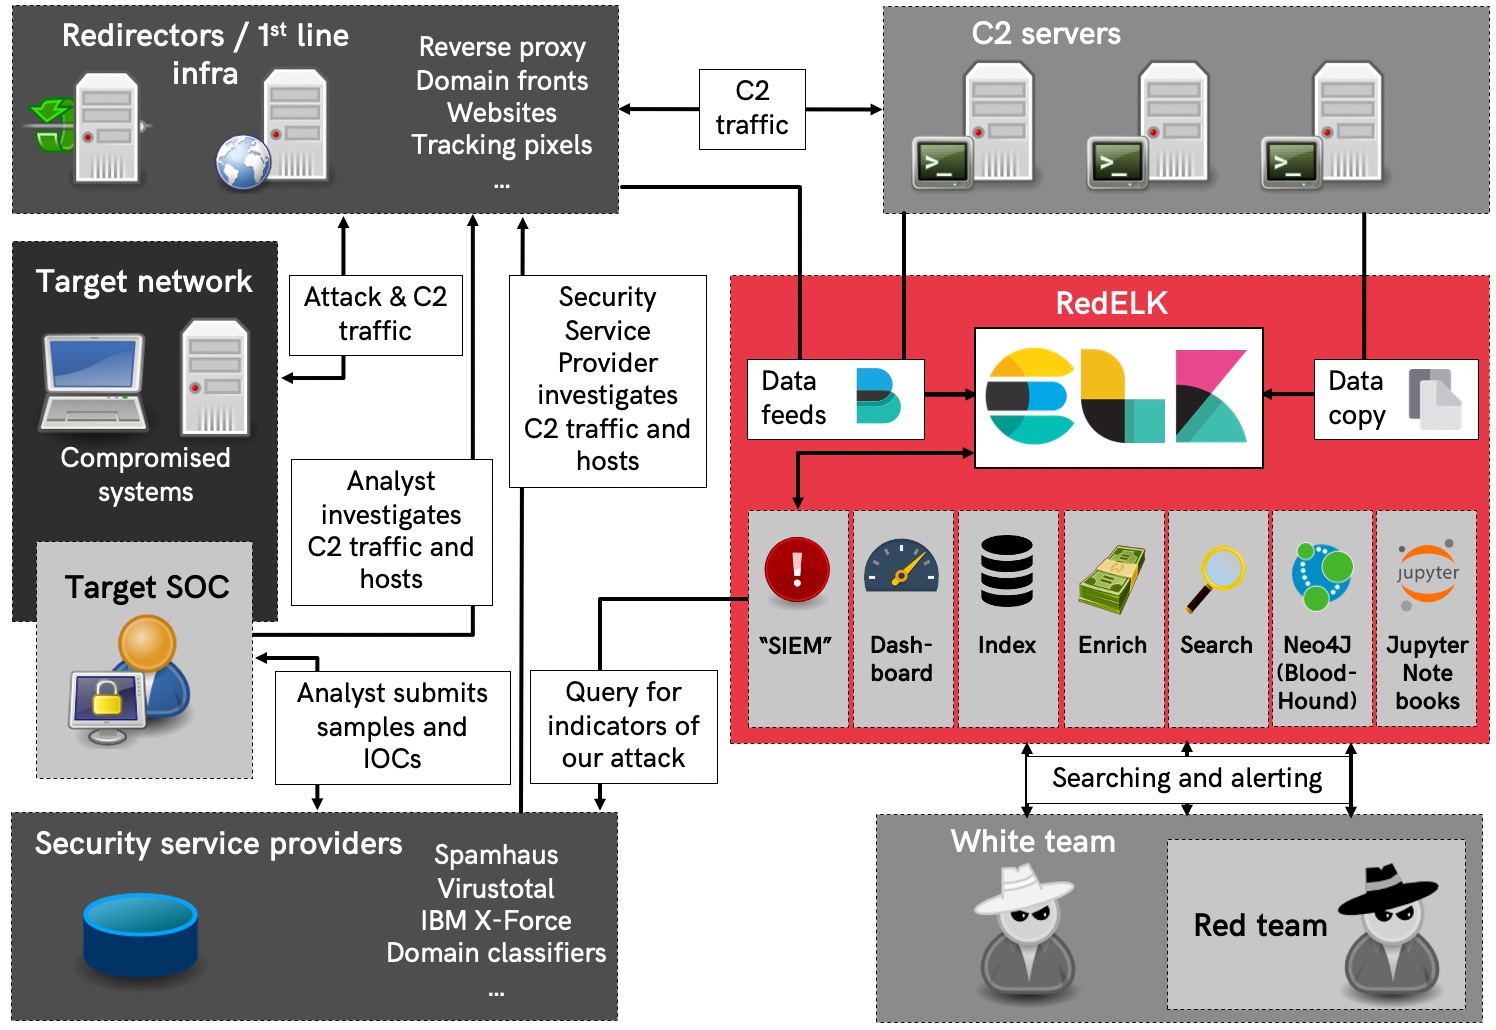 outflanknl/redelk
Red Team's SIEM - tool for Red Teams used for tracking and alarming about Blue Team activities as well as better usability in long term operations.
 sekoialab/fastir_collector
Live Windows forensic acquisition tool that collects system artefacts (registry, memory, disk, files) into CSV/JSON for early compromise detection…