
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
32 results
watcher preview

watcher

GitHubthemoonsir/watcher

Detection reverse shell and kill it before trying shell.
binary-analysisdefensive-toolsincident-response+5
27 months ago
mimicry preview

mimicry

GitHubchaitin/mimicry

Active deception tool that transparently migrates attackers from real targets to honeypots during exploitation and post-exploitation, supporting…
defensive-toolsincident-responsered-teaming+1
626 months ago
mediator preview

mediator

GitHublawndoc/mediator

An extensible, end-to-end encrypted reverse shell that works across networks without port forwarding.
command-and-controlencryption-decryption-toolsincident-response+5
1002 years ago
BerrySentinel preview

BerrySentinel

GitHubdereeqw/berrysentinel

Berry Sentinel v5.0 — Advanced behavioral C2 and reverse shell detector for Linux/Windows/Unix systems. Features real-time connection analysis,…
anomaly-detectioncommand-and-controldefensive-tools+8
136 months ago
CVE-2026-58048-PoC-Exploit preview

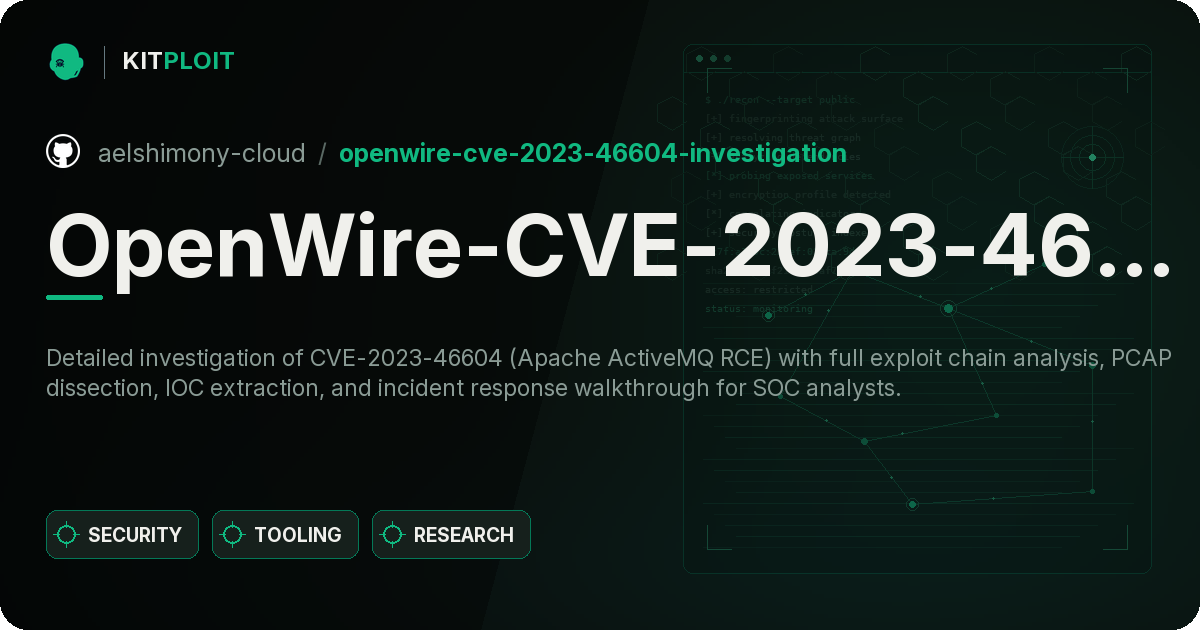
CVE-2026-58048-PoC-Exploit

GitHubtc4dy/cve-2026-58048-poc-exploit

👾 CVE-2026-58048 – cPanel Root SQL Execution Toolkit (CVSS 9.4) | Full Red/Blue Team Toolkit suite for unpatched cPanel & WHM 11.x. 2 tools: Safe…
database-securityexploitationincident-response+7
51 month ago
OpenWire-CVE-2023-46604-Investigation preview

OpenWire-CVE-2023-46604-Investigation

GitHubaelshimony-cloud/openwire-cve-2023-46604-investigation

Incident response walkthrough analyzing CVE-2023-46604 exploitation of Apache ActiveMQ via OpenWire, including PCAP analysis, IOC identification, and…
command-and-controldigital-forensicsexploitation+7
3 months ago
CVE-2024-3094-XZ-Backdoor-Detector preview

CVE-2024-3094-XZ-Backdoor-Detector

GitHubdevjanger/cve-2024-3094-xz-backdoor-detector

Shell script to detect the CVE-2024-3094 backdoor in XZ Utils by checking for malicious code in liblzma build artifacts and identifying affected…
forensicsincident-responsemalware-analysis+3
2 years ago
ToolShell-CVE-2025-53770-SharePoint-Exploit-Lab-LetsDefend preview

ToolShell-CVE-2025-53770-SharePoint-Exploit-Lab-LetsDefend

GitHubcyprianatsyor/toolshell-cve-2025-53770-sharepoint-exploit-lab-letsdefend

Step-by-step walkthrough of exploiting CVE-2025-53770 (ToolShell) in a LetsDefend lab, covering RCE, web shell deployment, and incident response…

command-and-controlctfdigital-forensics+9
1 year ago
PortGuard preview

PortGuard

GitLabk3rnix/portguard

USB port access control tool for Debian with whitelist management, automatic background scanning daemon, and CLI interface to block or allow USB…
configuration-auditingdefensive-toolshardware-iot-security+3
28 months ago
Estudo-de-Caso-CVE-2026-31431-CopyFail preview

Estudo-de-Caso-CVE-2026-31431-CopyFail

GitHubpedro-lucas-melo/estudo-de-caso-cve-2026-31431-copyfail

🔐 Estudo de caso completo do CVE-2026-31431 (CopyFail) — vulnerabilidade crítica de escalada de privilégio no kernel Linux. Inclui análise técnica,…
curated-resourceseducationexploitation+3
4 months ago
CVE-2026-31431_je_sappelle_RoOt preview

CVE-2026-31431_je_sappelle_RoOt

GitHubsbeteta42/cve-2026-31431_je_sappelle_root

CVE-2026-31431 - Guide de Remédiation et Mesures de Protection

configuration-auditingcurated-resourceseducation+2
14 months ago
uac preview

uac

GitHubtclahr/uac

Portable, dependency-free incident response tool that automates forensic artifact collection from Unix-like systems, including memory acquisition,…

digital-forensicsforensicsincident-response+3
1.5k16 days ago
agentsh preview

agentsh

GitHubcanyonroad/agentsh

Execution-Layer Security (ELS) for AI agents — policy-enforced shell with audit.
ai-securityauthentication-authorizationcloud-security+7
38610 days ago
oversight preview

oversight

GitHubrakosn1cek/oversight

A lightweight security auditor and sandbox for shell scripts. Oversight combines a Static Analysis engine (Rust) with Dynamic Enforcement (Linux…
code-analysisdevsecopsdynamic-analysis-sandboxing+7
392 months ago
macOSTriageCollectionScript preview

macOSTriageCollectionScript

GitHubwithsecurelabs/macostriagecollectionscript

Collects comprehensive triage data from macOS for incident response, including system logs, file listings, browser data, shell history, and…
digital-forensicsforensicsincident-response+2
315 years ago
larac2shell preview

larac2shell

GitHubakefallonitis/larac2shell

Cross-platform interactive shell for Microsoft Defender for Endpoint Live Response
authenticationcommand-and-controlincident-response+6
165 months ago
CVE-2025-49706-SharePoint-Spoofing-Vulnerability-Under-Active-Exploitation preview

CVE-2025-49706-SharePoint-Spoofing-Vulnerability-Under-Active-Exploitation

GitHubadityabhatt3010/cve-2025-49706-sharepoint-spoofing-vulnerability-under-active-exploitation

A deep dive into CVE-2025-49706 — the SharePoint spoofing flaw now exploited in the wild for stealthy web shell deployment and privilege escalation.

educationexploitationincident-response+6
171 year ago
tanstack-compromise-checker preview

tanstack-compromise-checker

GitHubfabriziosalmi/tanstack-compromise-checker

Shell script to detect TanStack npm supply chain attack indicators (CVE-2026-45321 / GHSA-g7cv-rxg3-hmpx)

container-securitydevsecopsforensics+7
28 days ago
Previous12Next