

ThreatLens
 abdaullahag/threatlens
Python CLI tool for rapid IOC analysis (IPs, Domains, CVEs) using 6 free Threat Intel APIs. Outputs: Color-coded Excel, JSON, CSV. Uses: VT, Shodan,…
defensive-toolsincident-responseinformation-gathering+7
25
abdaullahag/threatlensPython CLI tool for rapid IOC analysis (IPs, Domains, CVEs) using 6 free Threat Intel APIs. Outputs: Color-coded Excel, JSON, CSV. Uses: VT, Shodan,…
 viralmaniar/ddwpasterecon
DDWPasteRecon tool will help you identify code leak, sensitive files, plaintext passwords, password hashes. It also allow member of SOC & Blue Team…

 dtact/divd-2021-00038--log4j-scanner
Recursive vulnerability scanner for Log4j CVEs in archives and Docker images. Detects JndiLookup.class and vulnerable versions via SHA256 hashes,…
 mubix/cve-2021-44228-log4shell-hashes
Hashes for vulnerable LOG4J versions
 sandflysecurity/sandfly-entropyscan
Entropy scanner for Linux to detect packed or encrypted binaries related to malware. Finds malicious files and Linux processes and gives output with…
 threathunters-io/qlog
ETW-based Windows process creation logger that enriches events with file hashes, signatures, and parent process details, outputting to Windows…
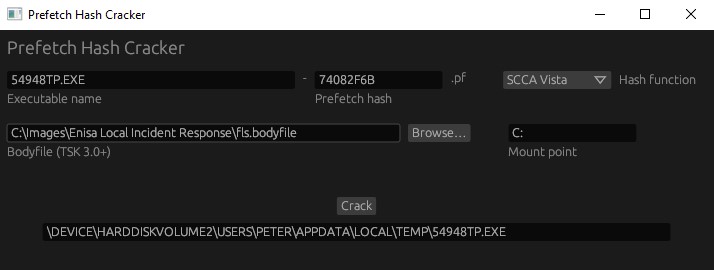 harelsegev/prefetch-hash-cracker
Brute-force tool that recovers full executable paths from Windows prefetch hashes using bodyfiles, supporting XP, Vista, and 2008 hash functions for…
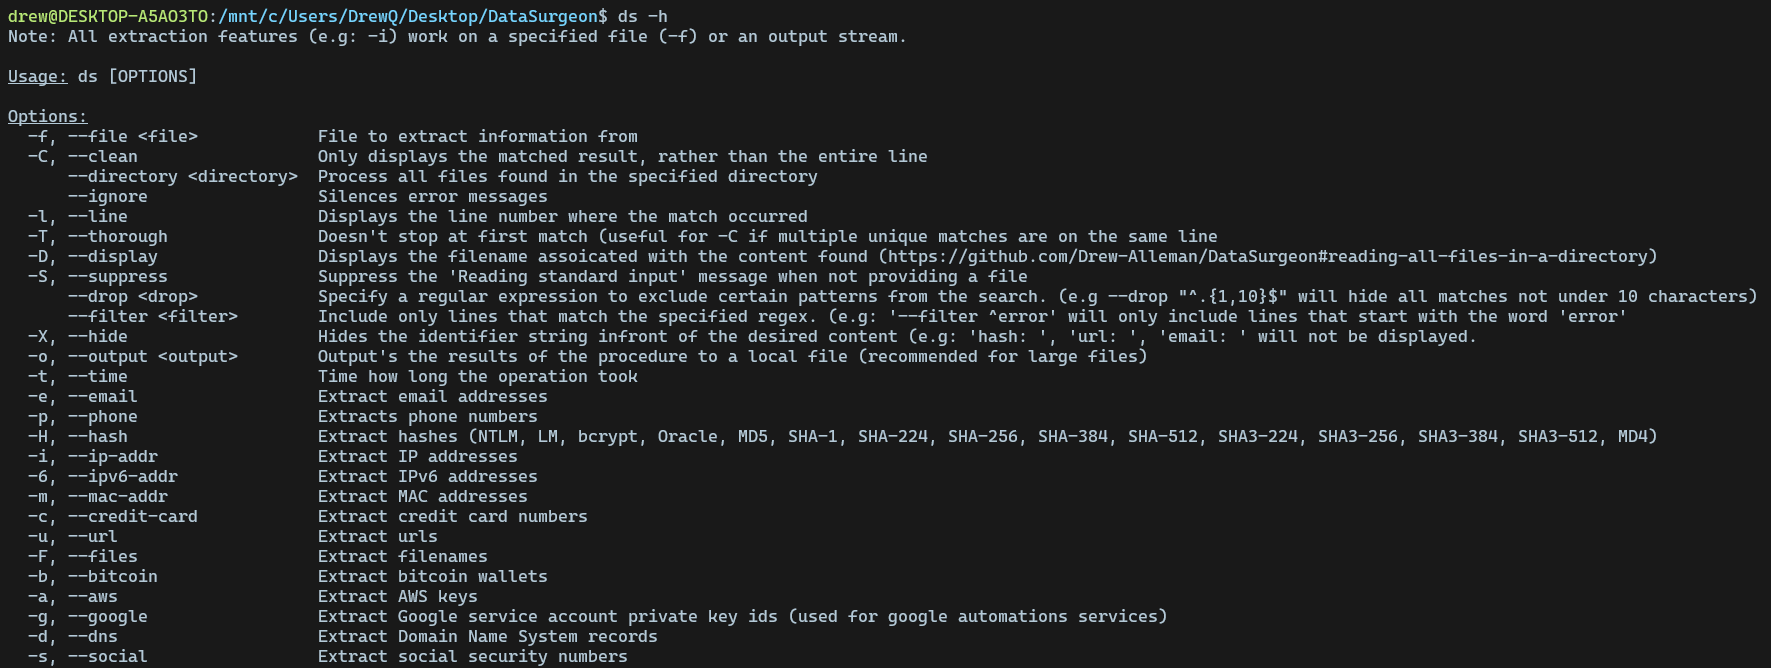 drew-alleman/datasurgeon
Quickly Extracts IP's, Email Addresses, Hashes, Files, Credit Cards, Social Security Numbers and a lot More From Text
 google/hashr
Builds forensic file hash sets from disk images, packages, and archives across GCP, AWS, and local sources, with deduplication and PostgreSQL/Spanner…
 sleuthkit/sleuthkit
Forensic library and CLI toolkit for analyzing disk and file system images, recovering deleted data, generating timelines, and validating evidence…
 dave_m/clamtk
An easy to use, light-weight, on-demand virus scanner for Linux systems. For additional help, see the <a…
 iomoath/filewatchtower
FWT is a security analysis and file monitoring tool that utilizes Sysmon events.
 withsecurelabs/shadowhammer
Batch-mode checker for Shadowhammer malware indicators, scanning local or provided MAC addresses against known malicious hashes, with offline support…
 securest8/npm-incident-response
Scanner for the keyv/cacheable supply-chain attack: detects compromised npm packages, verifies payload hashes, and finds persistence implants in repo…
 occamsec/log4j-checker
Bash and PowerShell scripts to scan a local filesystem for Log4j .jar files which could be vulnerable to CVE-2021-44228 aka Log4Shell.
 password123456/malwarescanner
Hash-based malware scanner for incident response. Scans files recursively using known malware hashes, supports multithreading, extension filtering,…
 executemalware/malware-iocs
Curated collection of indicators of compromise extracted from real-world malware investigations, including hashes, domains, and IPs for threat…