
five-nights-at-follina-s
 jeffreybxu/five-nights-at-follina-s
A Fullstack Academy Cybersecurity project examining the full cycle of the Follina (CVE-2022-30190) vulnerability, from exploit to detection and…
defensive-toolseducationexploitation+4
2
jeffreybxu/five-nights-at-follina-sA Fullstack Academy Cybersecurity project examining the full cycle of the Follina (CVE-2022-30190) vulnerability, from exploit to detection and…
 muhammad-ali007/outlookntlm_cve-2023-23397
Exploit for CVE-2023-23397 Outlook NTLM hash leak via malicious calendar invitations. Includes PowerShell weaponization, Responder integration, and…
 insomnisec/detections-cve-2026-31431
Detection rules, YARA signatures, auditd/Wazuh rules, and MISP event templates for CVE-2026-31431 Linux kernel LPE vulnerability (Copy Fail).…
 execution-py/cve-2026-9055
Defensive analysis of CVE-2026-9055, an unauthenticated privilege escalation in Amelia WordPress booking plugin. Provides root cause breakdown,…
 sentinel-aidefense/cve-2026-21509
CVE-2026-21509 Research writeup
 dtact/divd-2021-00038--log4j-scanner
Recursive vulnerability scanner for Log4j CVEs in archives and Docker images. Detects JndiLookup.class and vulnerable versions via SHA256 hashes,…
 gyaansastra/cve-2022-30190
Comprehensive analysis of CVE-2022-30190 (Follina MSDT vulnerability) with IOCs, detection rules for SIEMs/EDR, YARA signatures, mitigation scripts,…
 quantumworld-dpdns-io/cve-2026-42945
Full CVE-2026-42945 research repository with heap buffer overflow analysis, RCE exploit (heap spray + Feng Shui), detection scripts, and patching…
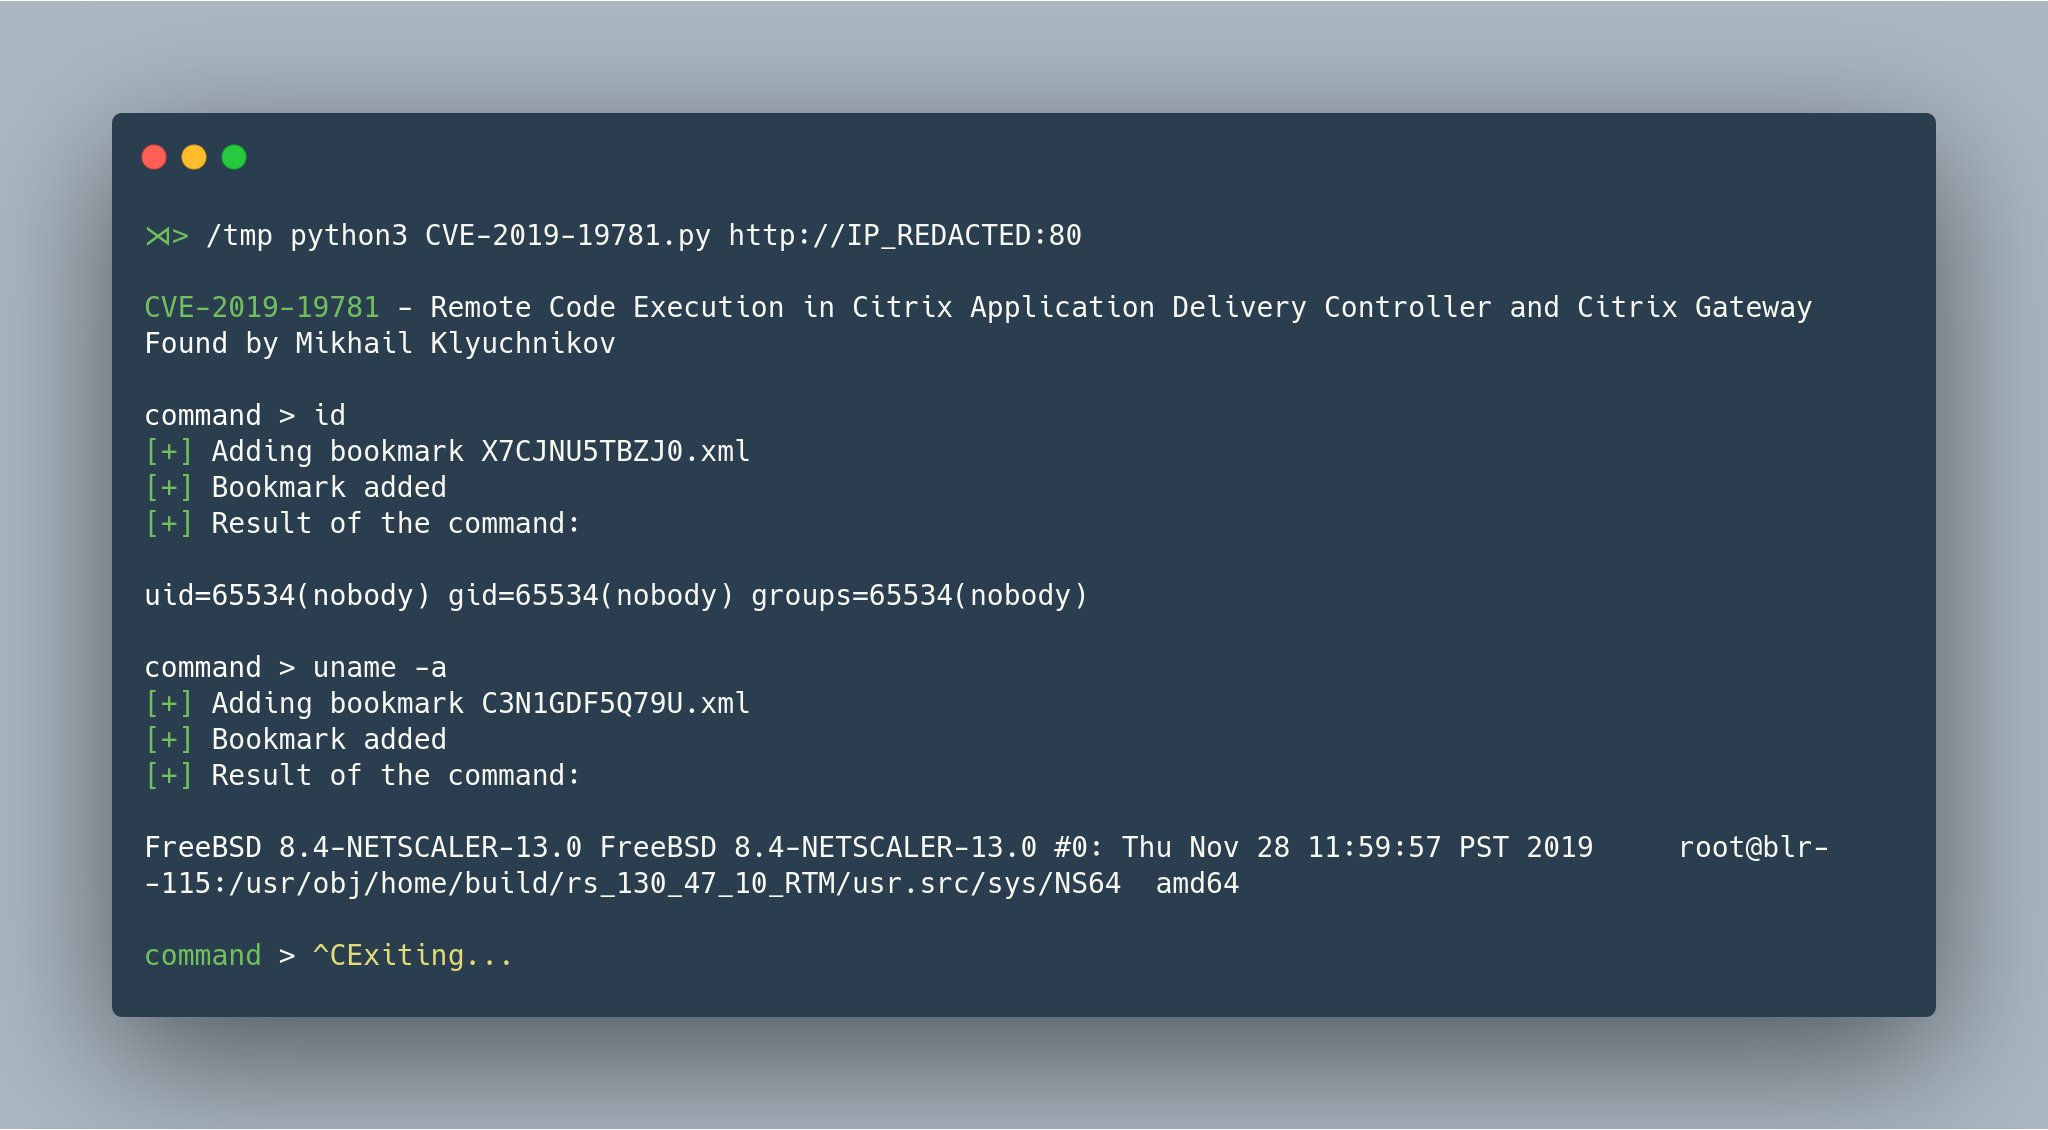 mpgn/cve-2019-19781
CVE-2019-19781 - Remote Code Execution on Citrix ADC Netscaler exploit
 corelight/cve-2022-26809
Zeek package detecting CVE-2022-26809 remote code execution attempts and successful exploitation over DCE/RPC, generating actionable exploit attempt…
 liamromanis101/cve-2026-31431-copy-fail---vulnerability-detection-script
Detection script for CVE-2026-31431 (Copy Fail) that checks kernel version, patch presence, kernel configs, AF_ALG socket availability, setuid…
 corelight/cve-2021-42292
Zeek package detecting CVE-2021-42292 Microsoft Excel local privilege escalation exploit via network traffic analysis of spreadsheet downloads.
 corelight/cve-2021-38647
CVE-2021-38647 AKA "OMIGOD" vulnerability in Windows OMI
 onapsis/onapsis-mandiant-cve-2025-31324-vuln-compromise-assessment
CVE-2025-31324 & CVE-2025-42999 vulnerability and compromise assessment tool
 kuniyal08/dirty-frag-cve-2026-43284
A report on Dirty Frag, which is a Linux Local Privilege Escalation (LPE) vulnerability chain that allows an unprivileged user to gain root access
 hkenzokimura/cve-2025-31324
Proof-of-concept exploit for CVE-2025-31324, an unauthenticated file upload in SAP NetWeaver Visual Composer, with detection guidance, MITRE mapping,…
 muhammad-ali007/follina_msdt_cve-2022-30190
Educational exploit for CVE-2022-30190 (Follina) demonstrating MSDT remote code execution via malicious Office documents, with detection and…
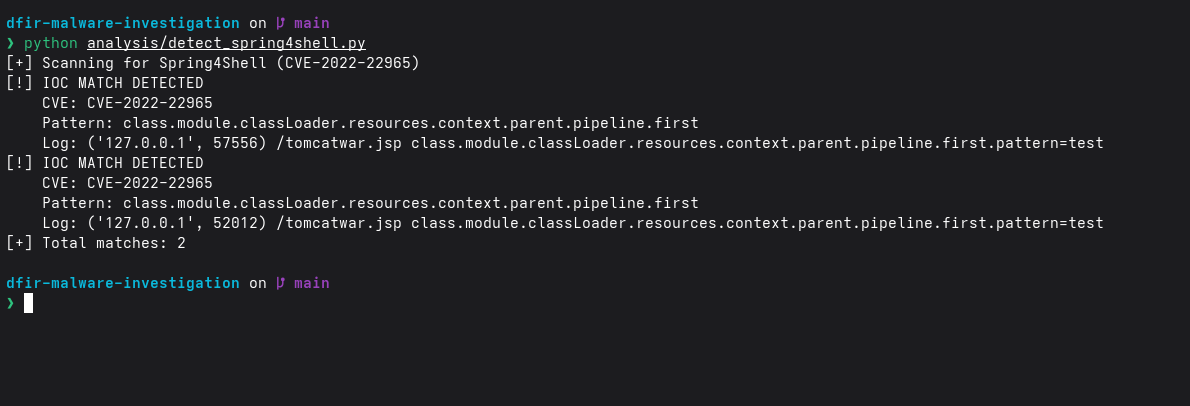 suyash-r-k/dfir-malware-investigation
Spring4Shell (CVE-2022-22965) DFIR lab with exploit simulation, Python WAF, IOC-based detection, and PCAP analysis.