Certighost-CVE-2026-54121

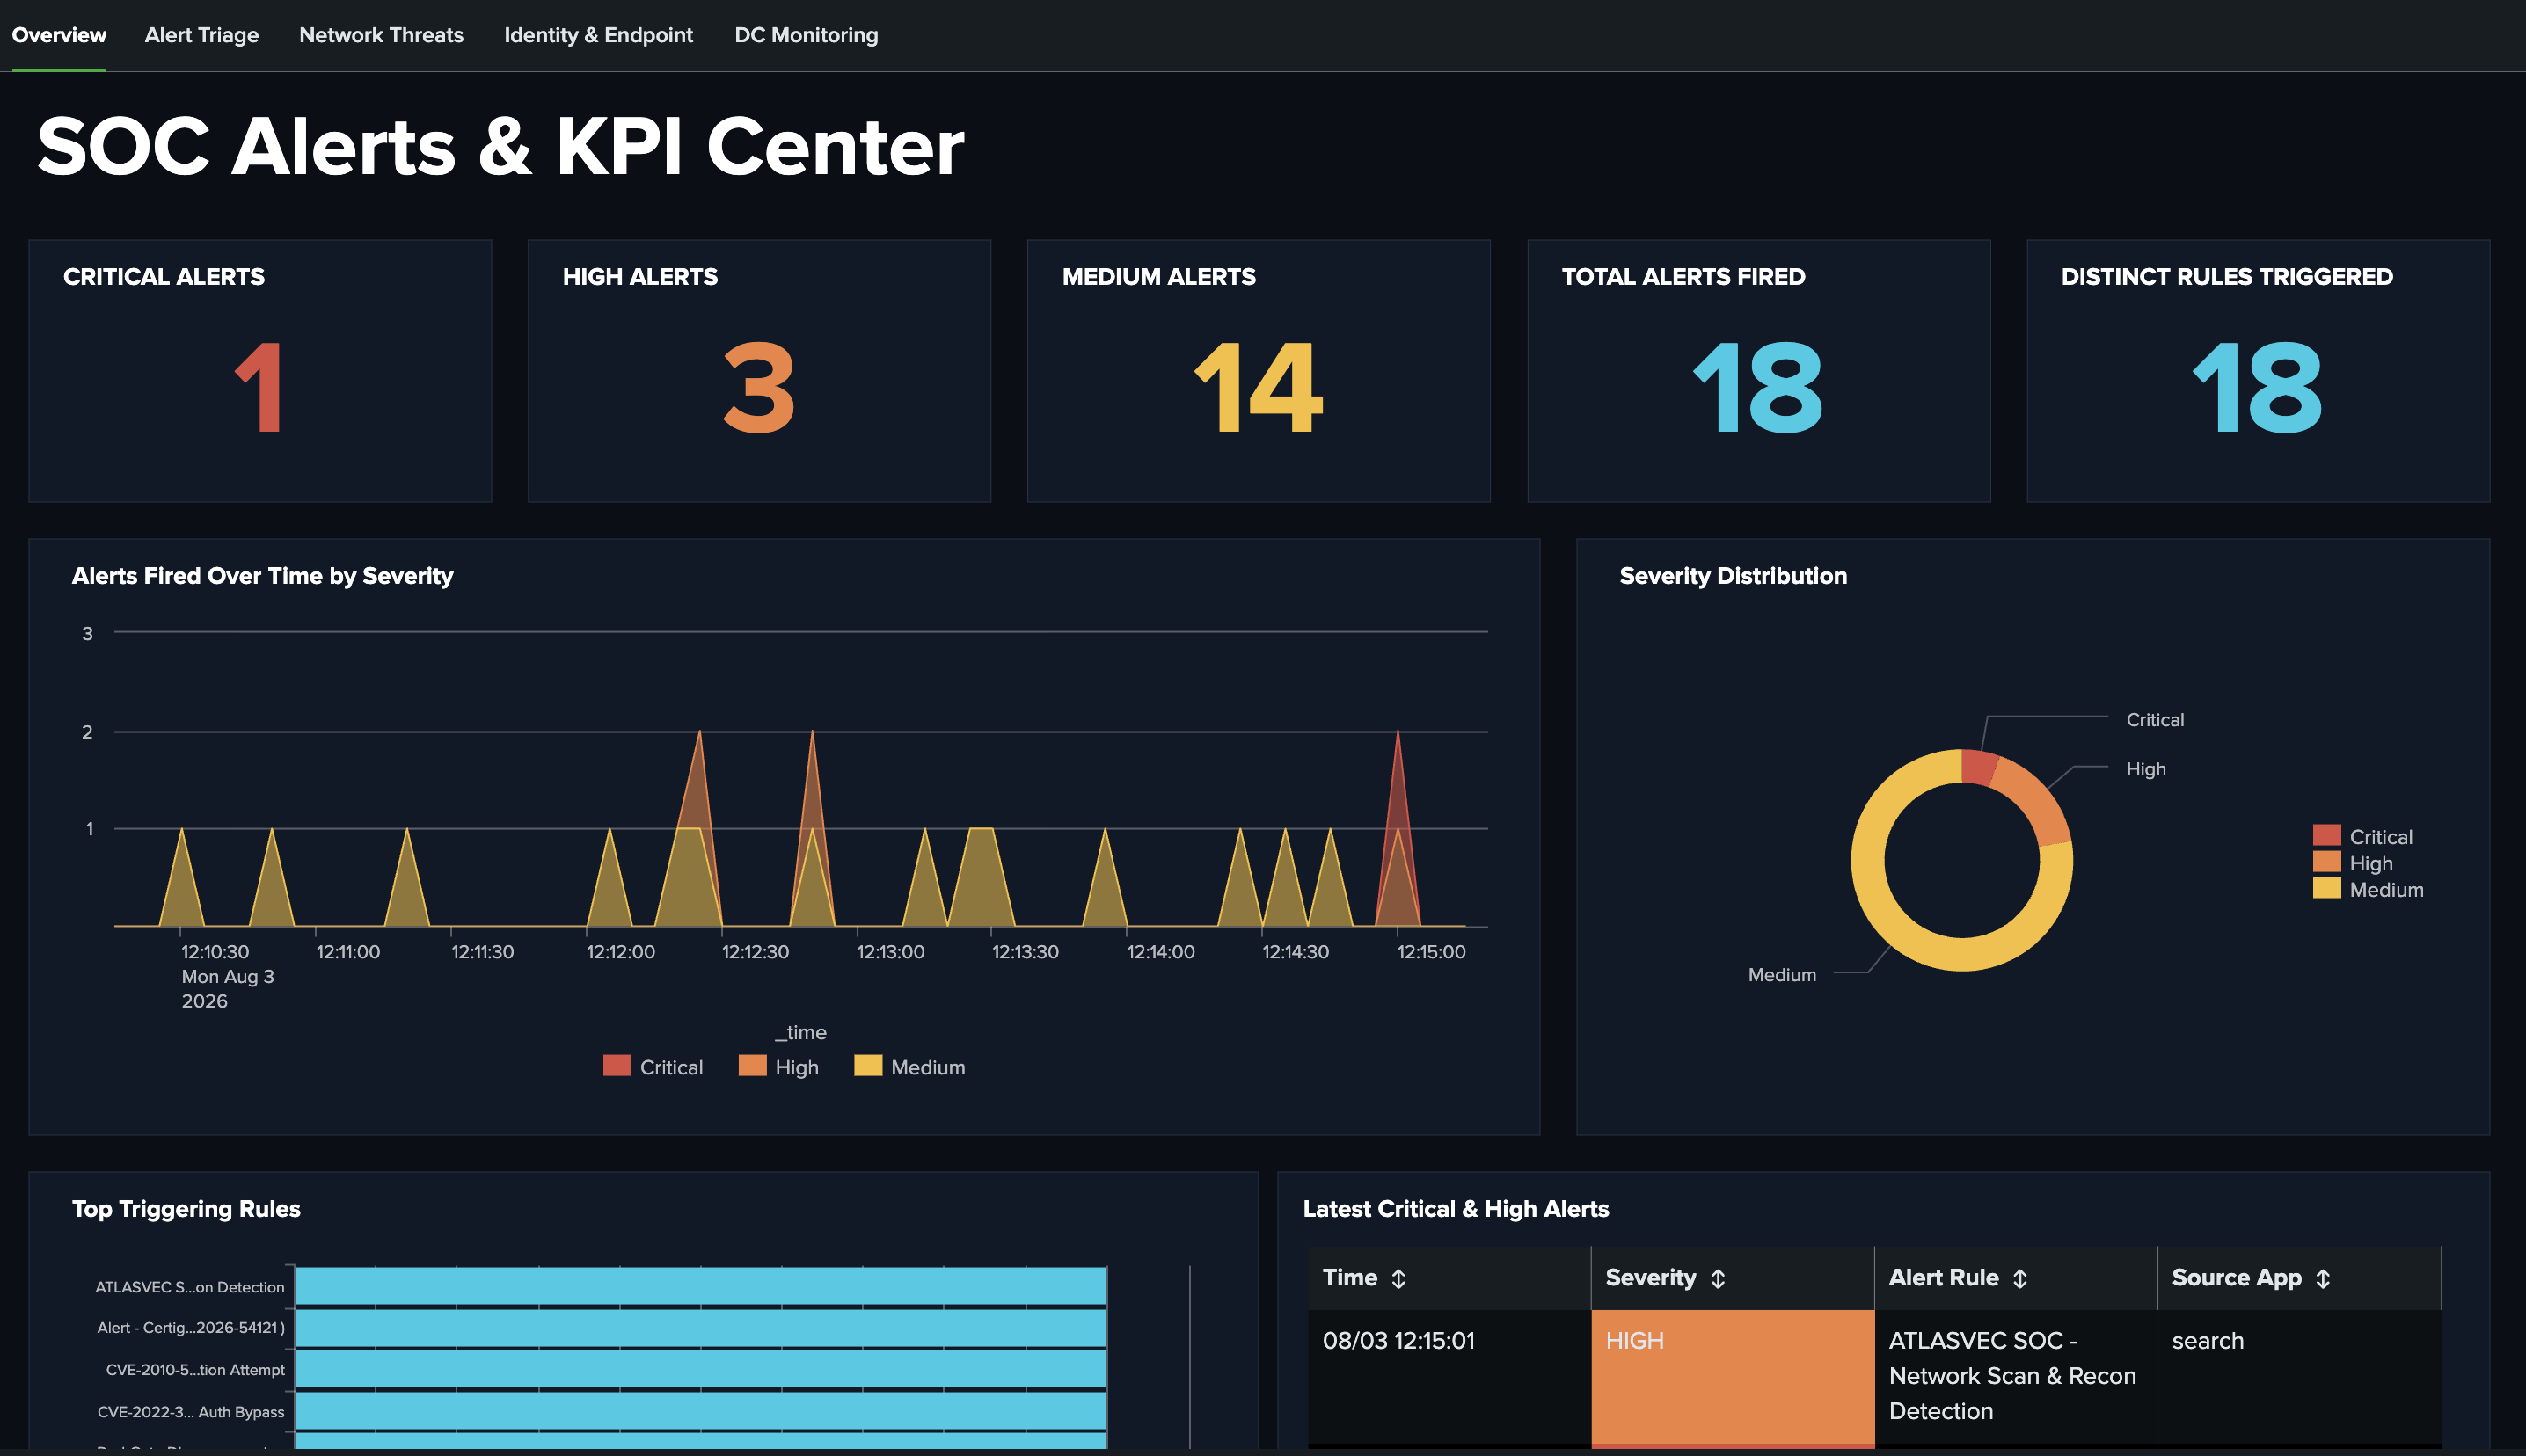
Splunk detection writeup for CVE-2026-54121 (CertiGhost): AD CS certificate chase abuse leading to full domain compromise. Lab-validated detection,…

Splunk detection writeup for CVE-2026-54121 (CertiGhost): AD CS certificate chase abuse leading to full domain compromise. Lab-validated detection,…

AI-powered threat intelligence platform for automated CVE/ransomware monitoring, domain surveillance, data leak detection, and incident response with…

Collects and analyzes AD and Azure AD authentication logs to detect lateral movement attacks using graph-based anomaly detection, visualizing…

Sanitised Windows security lab demonstrating Active Directory administration, host and network detection, and layered mitigation of CVE-2021-34527.

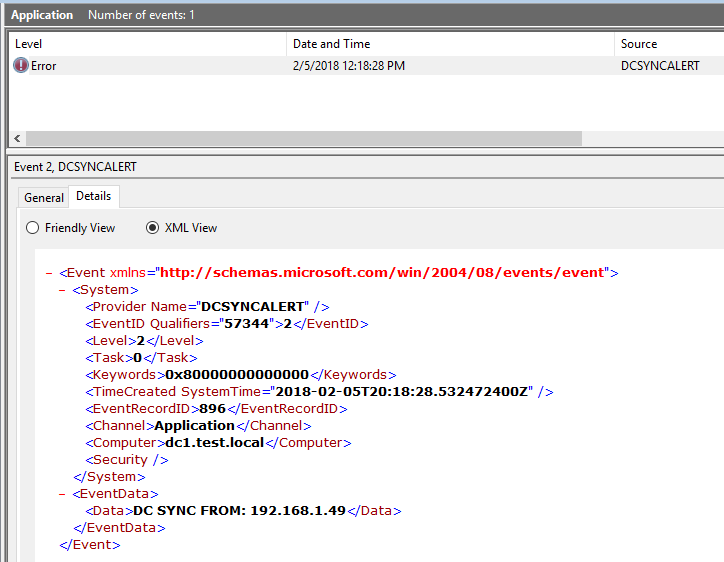
Monitors for DCSYNC and DCSHADOW attacks and create custom Windows Events for these events.

A repository of sysmon configuration modules

Tools for hunting for threats.

Docker configuration to quickly setup your own Canarytokens.

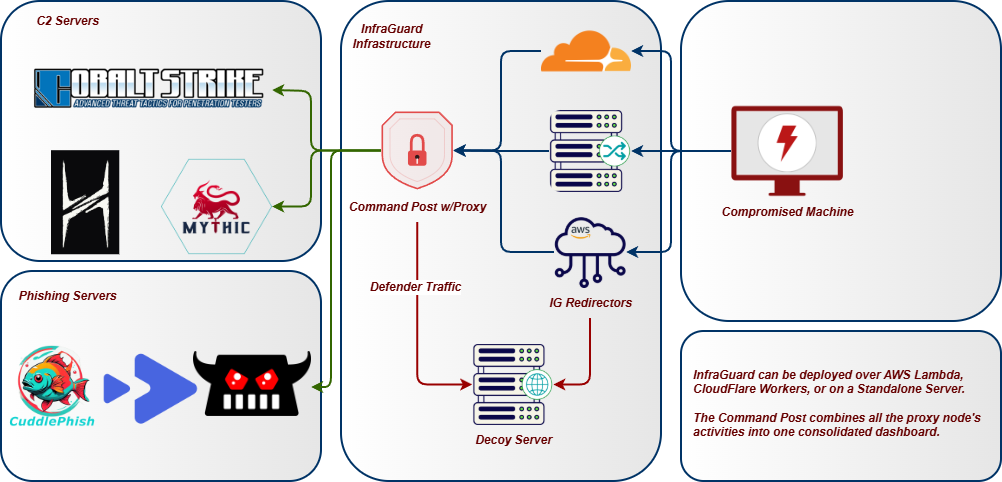
InfraGuard is a Command & Control Redirection Proxy and Manager which protects your Red Team Infrastructure against threat attribution

Zero-dependency Windows EDR utility that detects and mitigates unauthorized LSASS memory access, handle duplication, and LOLBin credential dumping in…

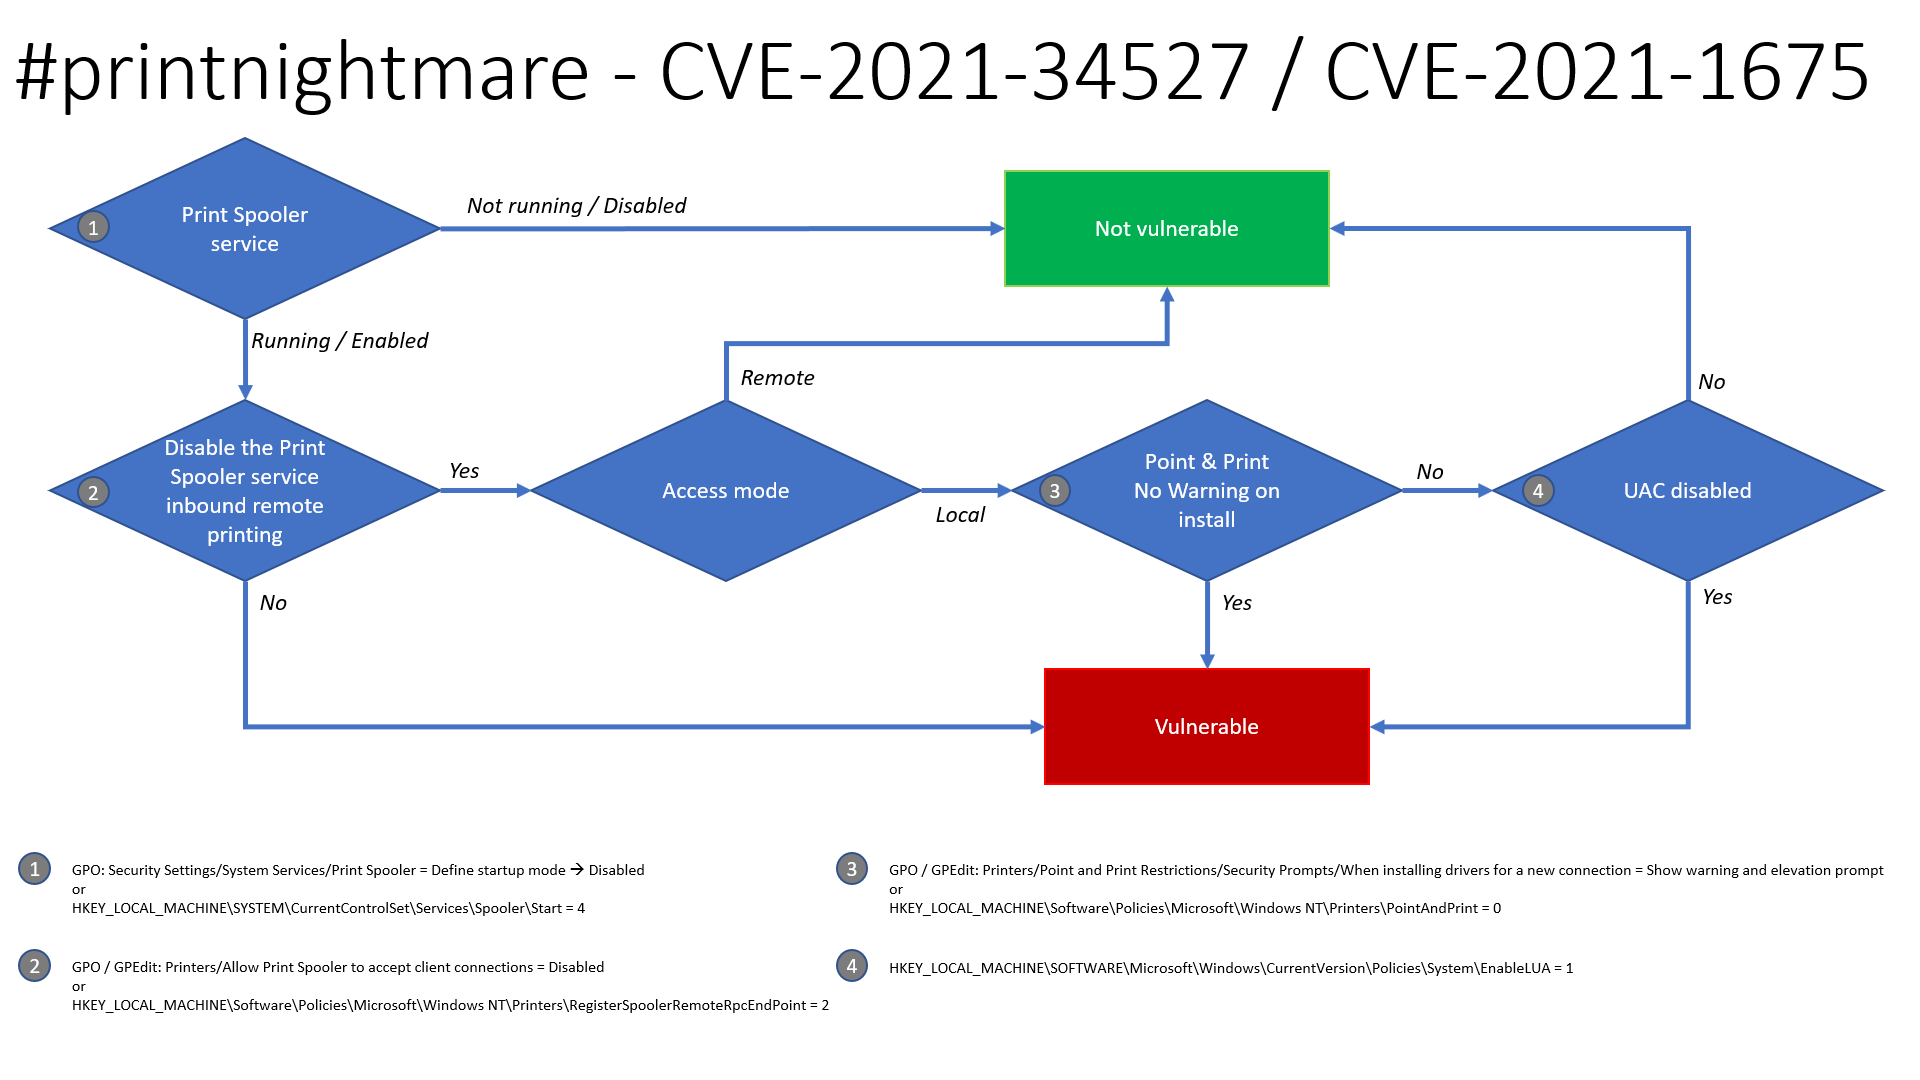
CVE-2021-1675 Detection Info

Blue Team detection lab created with Terraform and Ansible in Azure.

Detection scripts, patch checker & hardening guide for CVE-2026-44963 (Veeam B&R RCE)

Proof-of-concept exploit for CVE-2026-73570, an unauthenticated OS command injection in Zimbra Collaboration Suite via zimbra-snmp log injection,…

This repository contains a full blue-team malware analysis of a real malicious DOCX exploiting CVE-2017-0199. The lab includes sandbox execution,…

Simulated exploitation and mitigation of CVE-2025-54918 (Windows NTLM flaw). Includes detection scripts, Ansible patching, and CI/CD hardening.…

Technical write-up and analysis of PrintNightmare (CVE-2021-1675 / CVE-2021-34527), covering RCE/LPE exploitation, detection via Windows event logs,…

Splunk SIEM lab simulating and detecting CVE-2021-34527 (PrintNightmare) exploitation using Sysmon, Windows Event logs, and custom SPL detection…