
BruteRatel-DetectionTools
 immersive-labs-sec/bruteratel-detectiontools
A collection of Tools and Rules for decoding Brute Ratel C4 badgers
command-and-controldefensive-toolsincident-response+3
67
immersive-labs-sec/bruteratel-detectiontoolsA collection of Tools and Rules for decoding Brute Ratel C4 badgers
 volatilityfoundation/volatility
An advanced memory forensics framework
 cristianzsh/forensictools
Collection of forensic tools
 a-poc/blueteam-tools
Tools and Techniques for Blue Team / Incident Response
 fabacab/awesome-cybersecurity-blueteam
:computer:🛡️ A curated collection of awesome resources, tools, and other shiny things for cybersecurity blue teams.
 invoke-ir/ace
Automated, Collection, and Enrichment Platform
 horrister/moveit-transfer-cve-2023-34362
Curated vulnerability research repository with in-depth writeups, PoC scripts, and IOC detection tools for real-world security incidents like…
 synacktiv/veeam-velociraptor
Proof-of-concept Velociraptor artifacts pack to showcase a remote Veeam forensics pipeline.
 withsecurelabs/linuxcatscale
Incident Response collection and processing scripts with automated reporting scripts
 meirwah/awesome-incident-response
Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…
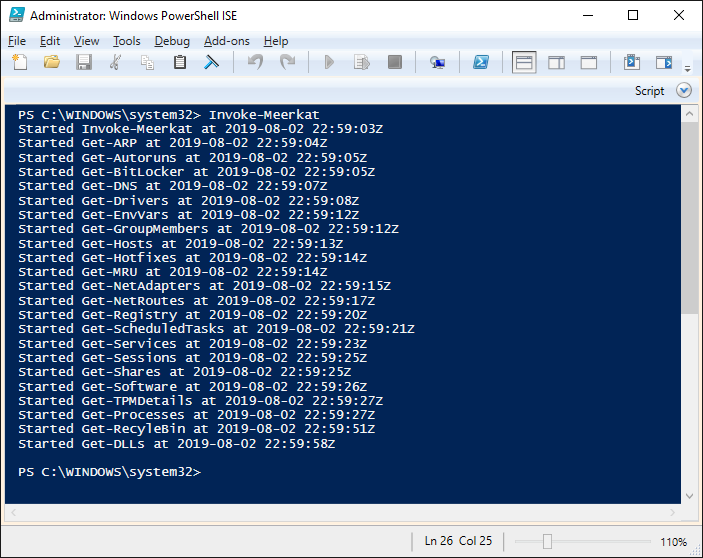 tonyphipps/meerkat
A collection of PowerShell modules designed for artifact gathering and reconnaisance of Windows-based endpoints.
 executemalware/malware-iocs
Curated collection of indicators of compromise extracted from real-world malware investigations, including hashes, domains, and IPs for threat…
 bartblaze/yara-rules
Collection of private Yara rules.
 tsale/awesome-dfir-skills
A curated collection of DFIR skills and workflows for InfoSec practitioners.
 bushidouk/breach-report-collection
A collection of companies that disclose adversary TTPs after they have been breached
 lethal-forensics/macos-collector
macos-collector - Automated Collection of macOS Forensic Artifacts for DFIR
 sifalcon/detection
Curated collection of detection rules and IOCs extracted from DFIR engagements and malware analyses to support threat hunting, incident response, and…
 fastfire/ioc_attack_esxi_feb_2023
Collection of IoCs available and related to attacks on ESXi infrastructures that occurred as of Friday February 3, 2023.