

 trailofbits/mquire
Zero-dependency Linux memory forensics, leveraging kernel-embedded BTF and kallsyms for type-aware memory analysis without external debug info.
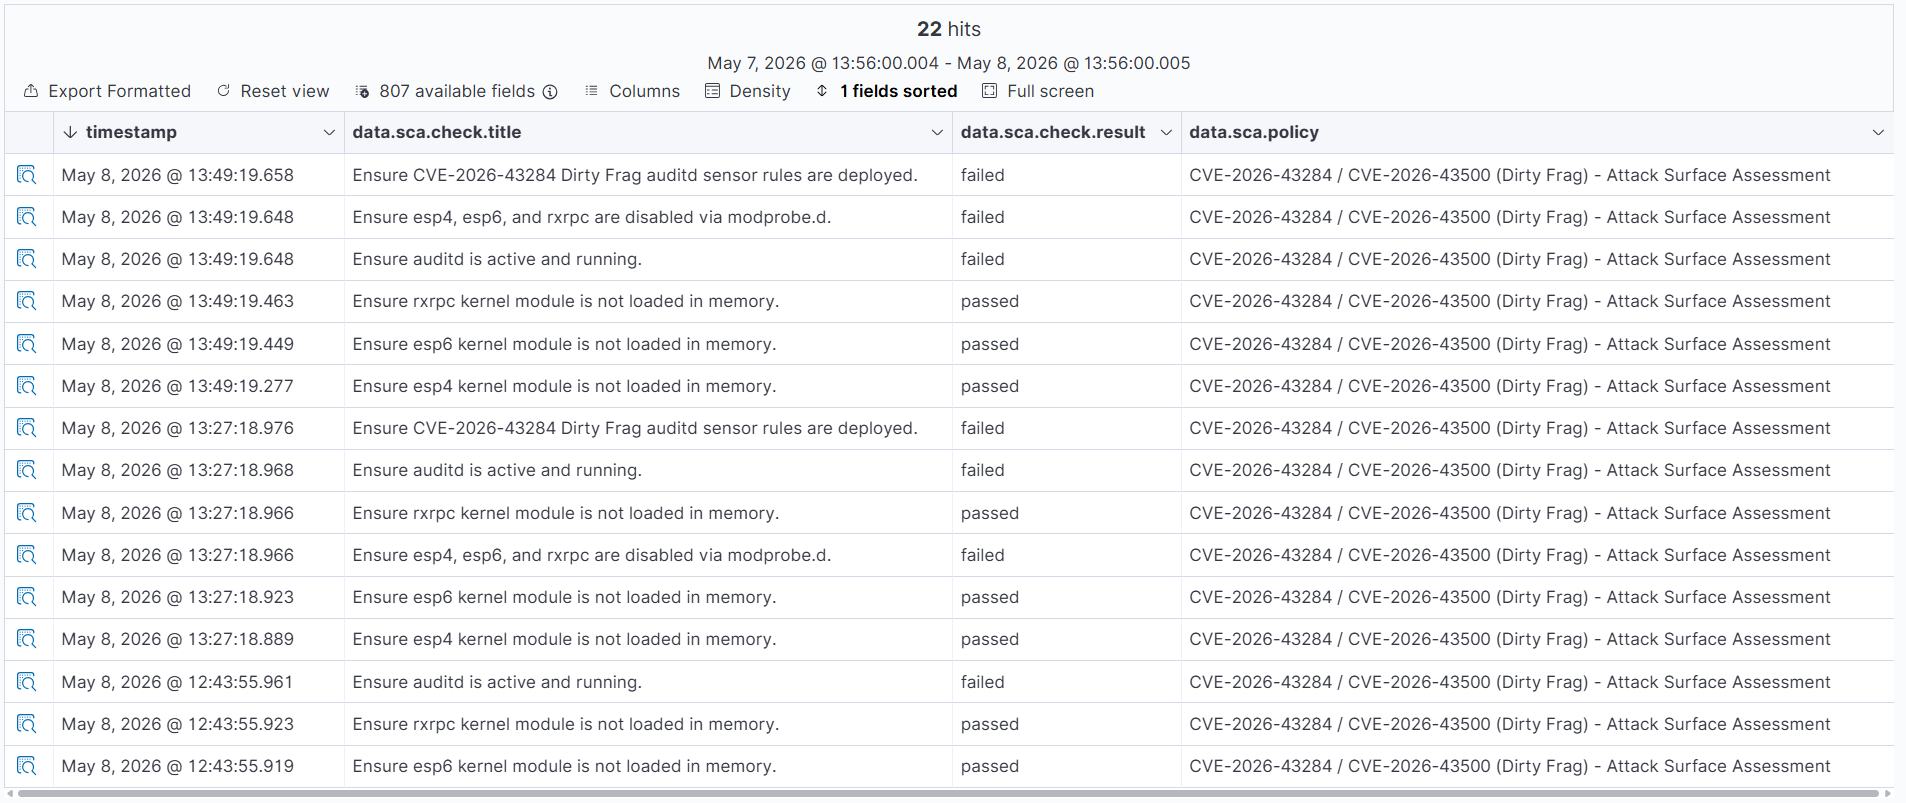 mym0us3r/dirty-frag-detection-with-wazuh-4.14.4
Wazuh 4.14.4 detection rules for CVE-2026-43284 / CVE-2026-43500 (Dirty Frag) - Linux Local Privilege Escalation via page cache write
 gosecure/pyrdp
RDP monster-in-the-middle (mitm) and library for Python with the ability to watch connections live or after the fact
 wmal/linux-kodachi
Hardened Debian-based privacy OS with pre-integrated anonymity stack (Tor, VPN, DNSCrypt), anti-forensic tooling, SOC security center, and standalone…
 securityjoes/masterparser
MasterParser is a powerful DFIR tool designed for analyzing and parsing Linux logs
 buter-chkalova/rvbbit-arsenal
Offensive & defensive Linux kernel security research focused on rootkit behavior, observable artifacts and detection.
 sumidcyber/zeroscout
🦅 ZeroScout: The Autonomous Local & Cloud Threat Hunter. Visualize attacks in a live War Room, identify APT groups via Genetic Analysis, and…
 go-lanz/persistnux
Bash-based Linux persistence detection tool for DFIR investigations. Scans 15+ persistence mechanisms (systemd, cron, kernel modules, SSH,…
 sobri3195/pegasus-malware-scan
Multi-layered malware scanner combining hash-based verification, behavioral analysis, and sandbox execution for threat detection, incident response,…
 kuniyal08/dirty-frag-cve-2026-43284
A report on Dirty Frag, which is a Linux Local Privilege Escalation (LPE) vulnerability chain that allows an unprivileged user to gain root access
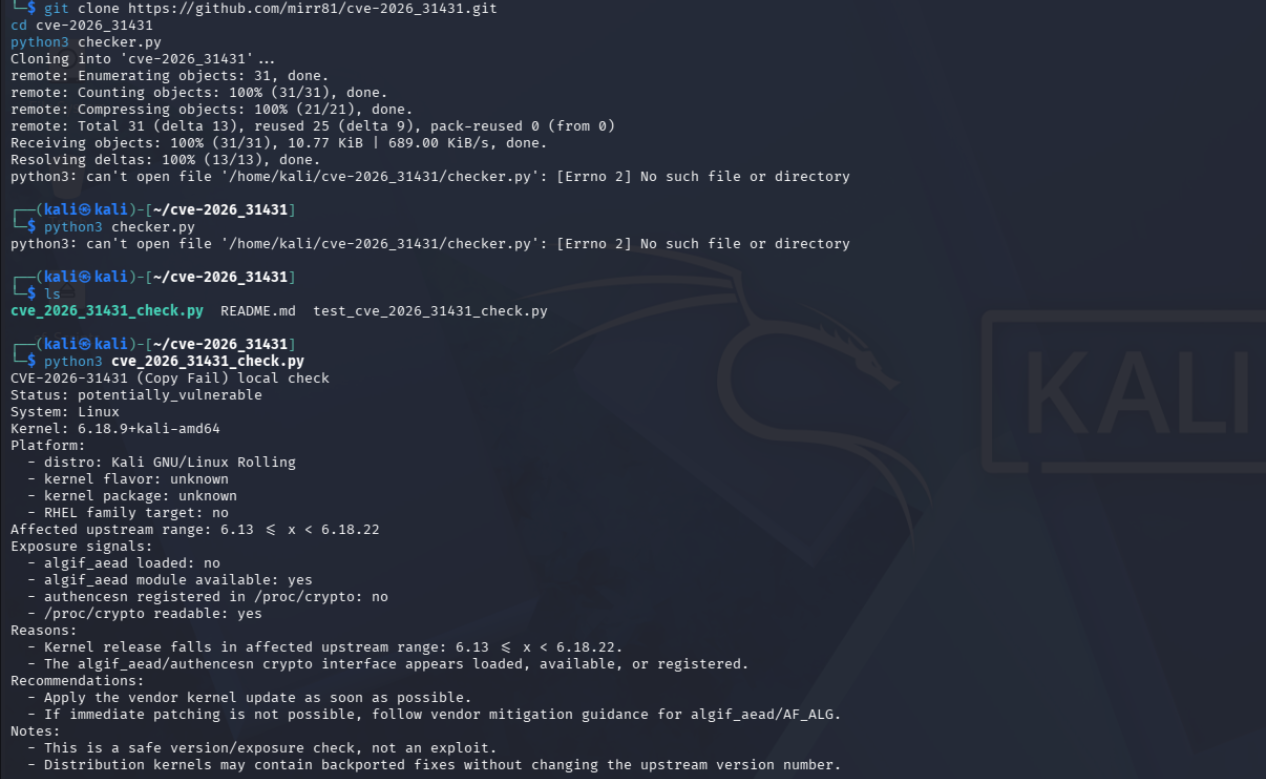 kuniyal08/copy-fail-cve-2026-31431-lab
Reproduced the fileless LPE CVE‑2026‑31431 (“Copy Fail”) on Kali Linux, then built auditd, Sigma & YARA detections to catch this stealthy kernel…
 jihwan77/linux-kernel-copy-fail-cve-2026-31431-
Analysis and mitigation of Linux kernel Copy Fail (CVE-2026-31431) vulnerability exploiting AF_ALG/splice page cache mutation, with PoC checker,…
 insomnisec/detections-cve-2026-31431
Detection rules, YARA signatures, auditd/Wazuh rules, and MISP event templates for CVE-2026-31431 Linux kernel LPE vulnerability (Copy Fail).…
 nicholasc03/dns-poisoning-triage-lab
Forensic triage of DNS cache poisoning in legacy hardware. Includes PCAP analysis of 839-byte unsolicited record injections, CVE-2025-40778 mapping,…
 nnatsopoulos/xz-backdoor-research
CVE-2024-3094 XZ Utils backdoor research - attack surface visualiser, system vulnerability checker, and general Linux CVE assessment tool
 rippsec/cve-2026-31431-copy-fail
Comprehensive analysis of CVE-2026-31431, a Linux kernel LPE, including exploit methodology, detection scripts, YARA rules, auditd and Falco…
 vishvacyber/detection-tool-kit-for-cve-2026-31431
Layered detection toolkit for CVE-2026-31431 (Copy Fail) Linux kernel LPE. Provides eBPF, auditd, Sigma rules, page-cache diff, and IOC guides for…