
Honeypot-Project
 owasp/honeypot-project
Deploy web honeypots to capture emerging attack data, analyze ModSecurity audit logs via ELK, and share threat intelligence with MISP for…
defensive-toolseducationincident-response+5
109
owasp/honeypot-projectDeploy web honeypots to capture emerging attack data, analyze ModSecurity audit logs via ELK, and share threat intelligence with MISP for…
 blessedrebus/krawl
Krawl is a customizable, lightweight, cloud-native web deception server and anti-crawler that creates fake web applications with low-hanging…
 0x4d31/galah
Galah: An LLM-powered web honeypot.
 chaitin/mimicry
Active deception tool that transparently migrates attackers from real targets to honeypots during exploitation and post-exploitation, supporting…
 cymmetria/micros_honeypot
MICROS Honeypot is a low interaction honeypot to detect CVE-2018-2636 in the Oracle Hospitality Simphony component of Oracle Hospitality Applications…
 patrowl/patrowlmanager
PatrOwl - Open Source, Smart and Scalable Security Operations Orchestration Platform
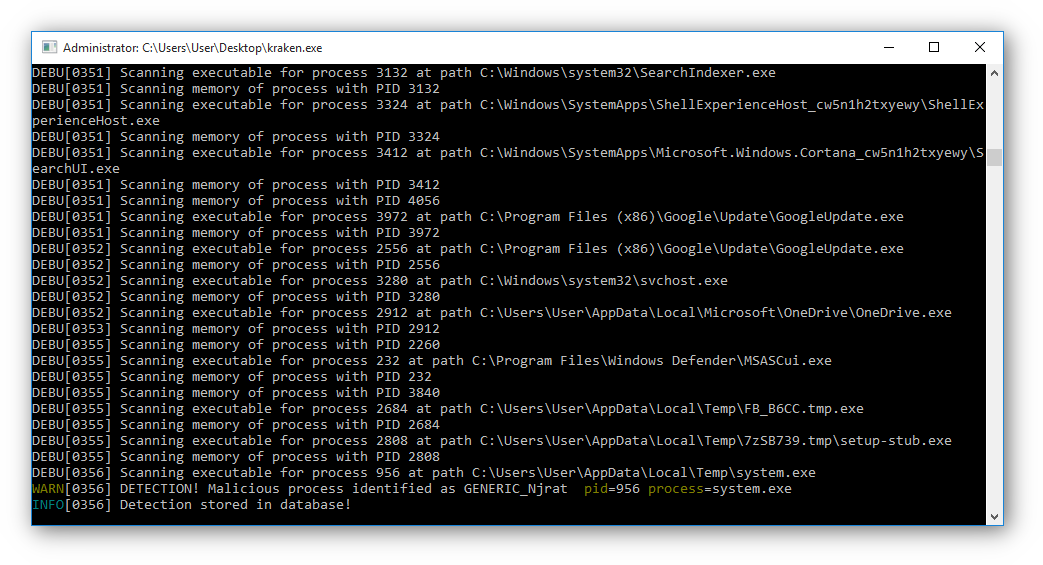 botherder/kraken
Cross-platform Yara scanner written in Go
 malwaretech/citrixhoneypot
Detect and log CVE-2019-19781 scan and exploitation attempts.
 airbus-cert/cve-2024-4040
Scanner for CVE-2024-4040
 wortell/cve-2020-0618
CVE-2020-0618 Honeypot
 zerozenxlabs/cve-2025-61882-oracle-ebs
Operational exploit for CVE-2025-61882 in Oracle E-Business Suite, with research artifacts for defensive validation, detection engineering, incident…
 qingtengyun/cve-2021-44228-qingteng-patch
Hotpatch tool for CVE-2021-44228 (Log4Shell) that uses JVM Instrumentation API to fix JndiLookup::lookup() in running Java processes without restart.…
 emrekybs/nginxhunter
Analyzes Nginx access logs to detect SQL injection, scanner tools, webshells, and exploitation attempts, aiding system administrators in server…
 anoxhunterdump-ctrl/cve-2026-103752-authorizer-privilege-escalation
Defensive analysis, patch breakdown, and passive detection scanner for CVE-2026-103752 (WordPress Authorizer Plugin <= 3.15.3).
 dabbleam/cve-2026-31431-mitigation
eBPF-based daemon to mitigate CVE-2026-31431 on systems where `algif_aead` is built into the kernel, without a reboot!
 kaleth4/cve-2026-64638
Technical analysis and defensive mitigation for a WordPress Core pre-auth XSS-to-RCE chain, including sanitizer bypass, DOM clobbering, JSONP abuse,…
 brets0150/stickyexim
Exim Honey Pot for CVE-2019-10149 exploit attempts.
 sonicwave21/follina-cve-2022-30190-unofficial-patch
An Unofficial Patch Follina CVE-2022-30190 (patch) by micrisoft Guidelines.