
C2-detection-manjusaka
 corelight/c2-detection-manjusaka
Detection of Manjusaka C2 framework
command-and-controlincident-responseintrusion-detection+3
corelight/c2-detection-manjusakaDetection of Manjusaka C2 framework
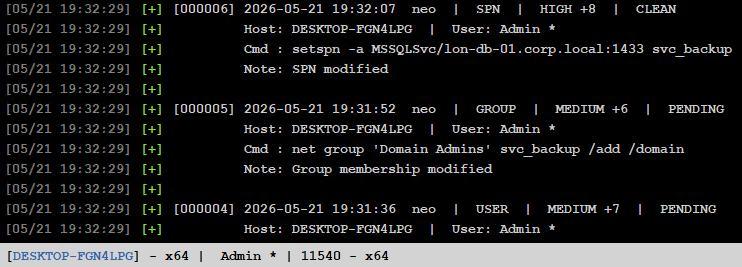 shellkraft/ledger
An aggressor script that tracks operational changes made during a red team engagement. Gives you a full audit trail of what was changed and what…
 nivdolgin/cve-2018-13379
Hunting CVE-2018-13379
 3lp4tr0n/beaconhunter
Detect and respond to Cobalt Strike beacons using ETW.
 duyduongduyduong/cve-2021-36934-dll-hijacking-dfir-investigation
DFIR investigation resources for CVE-2021-36934, covering DLL hijacking, privilege-escalation detection, and forensic analysis of affected Windows…
 sentinelblue/cve-2022-29072
** DISPUTED ** 7-Zip through 21.07 on Windows allows privilege escalation and command execution when a file with the .7z extension is dragged to the…
 n3tsurge/cve-2021-36934
Detection and Mitigation script for CVE-2021-36934 (HiveNightmare aka. SeriousSam)
 arch1m3d/miniplasma-detection
Sigma detection rule for MiniPlasma (CVE-2020-17103)
 vorkampfer/copyfail2_electric_boogaloo_fix
A temporary mitigation against copy_fail variant (copyfail2_electric_boogaloo) - Unprivileged Linux LPE via xfrm ESP-in-UDP MSG_SPLICE_PAGES no-COW…
 fox-it/dissect.cobaltstrike
Python library for dissecting and parsing Cobalt Strike related data such as Beacon payloads and Malleable C2 Profiles
 facebookincubator/ttpforge
The TTPForge is a Cybersecurity Framework for developing, automating, and executing attacker Tactics, Techniques, and Procedures (TTPs).
 malwaretech/hiddendesktop
Create and enumerate hidden desktops.
 withsecurelabs/ppid-spoofing
Scripts for performing and detecting parent PID spoofing
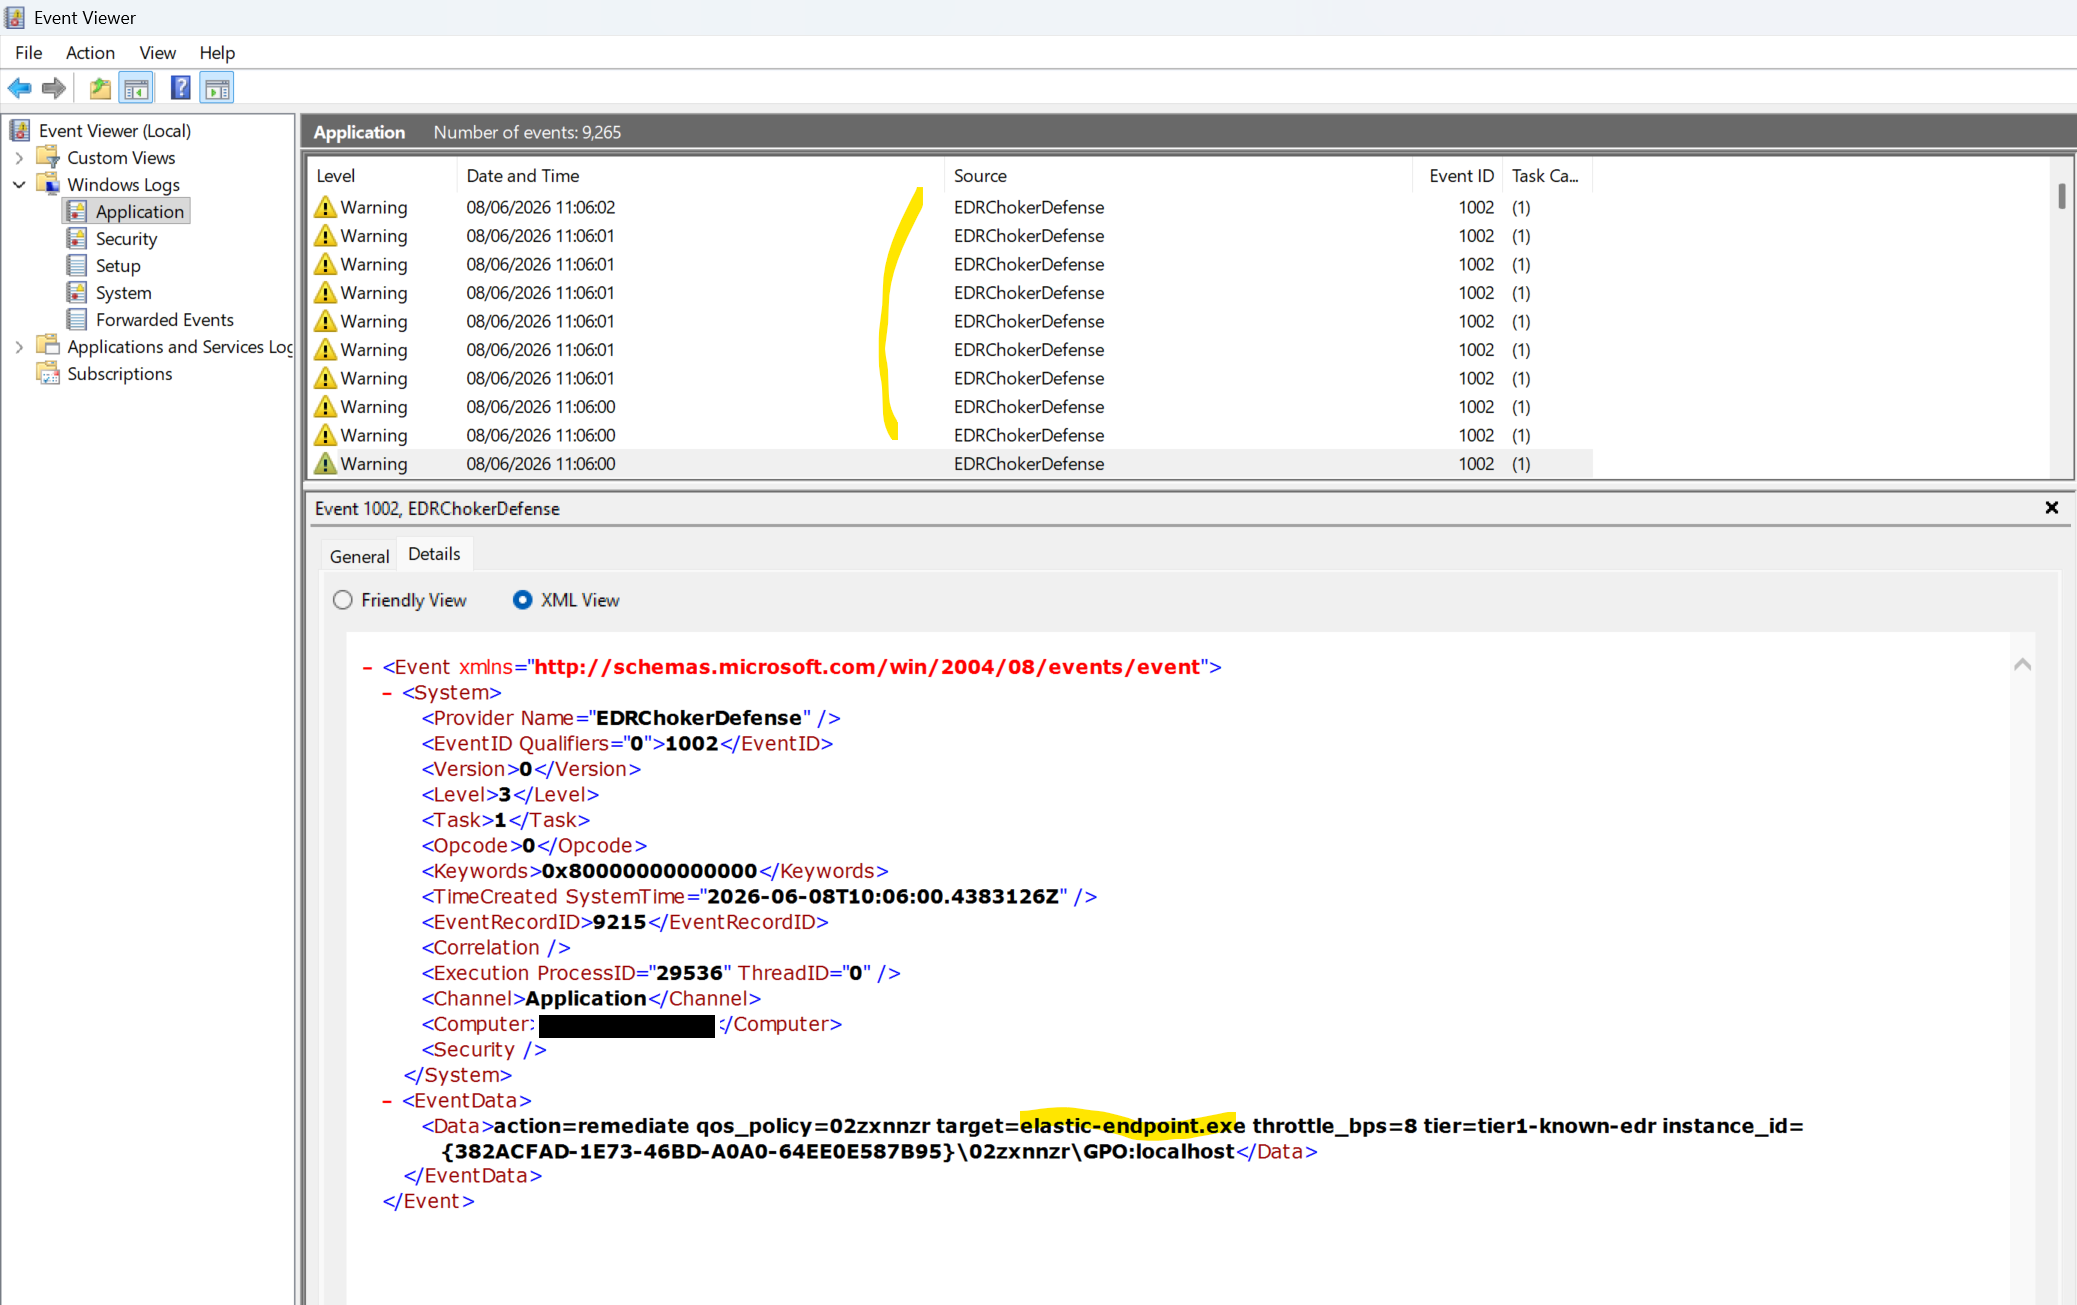 sbousseaden/edrunchoker
EDRUnChoker - fileless WMI defense that removes EDRChoker QoS throttling policies
 qingtengyun/cve-2021-44228-qingteng-online-patch
Hot-patch CVE-2021-44228 by exploiting the vulnerability itself.
 phantomiman/7-zip.chm-mitigation
7-Zip CVE-2022-29072 Mitigation - CHM file - This script detects if the .chm file exists and removes it.
 notitssixtyn3in/cve-2025-4162027
Security advisory detailing a critical authentication vulnerability in Copilot where user IDs are switched, enabling unauthorized account access and…