
CloudGrappler
 permiso-io-tools/cloudgrappler
Query high-fidelity cloud detections for known threat actors across AWS, Azure, and GCP using CloudTrail logs and custom threat intelligence rules.
cloud-securitydefensive-toolsincident-response+2
267
permiso-io-tools/cloudgrapplerQuery high-fidelity cloud detections for known threat actors across AWS, Azure, and GCP using CloudTrail logs and custom threat intelligence rules.
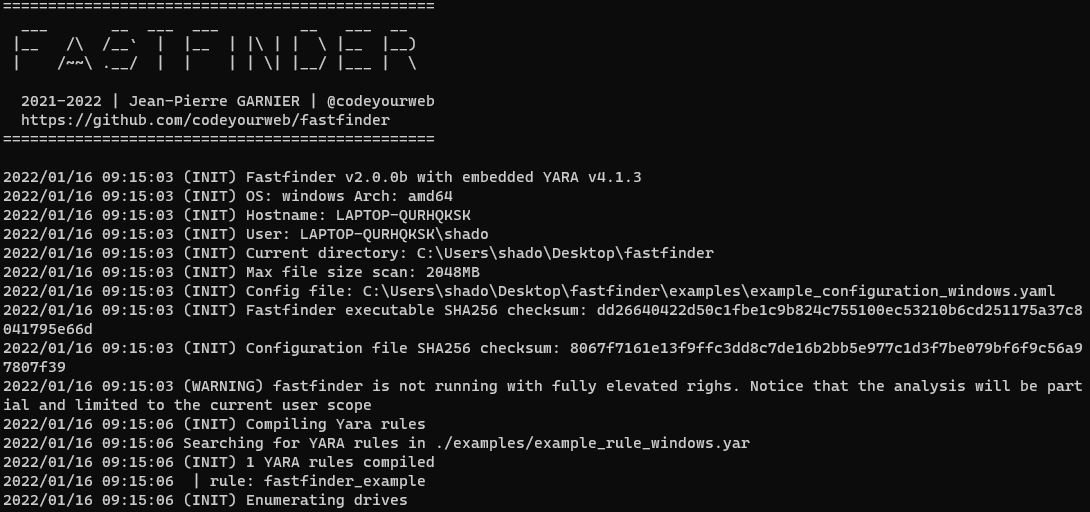 codeyourweb/fastfinder
Incident Response - Fast suspicious file finder
 tclahr/uac
Portable, dependency-free incident response tool that automates forensic artifact collection from Unix-like systems, including memory acquisition,…
 idaholab/malcolm
Malcolm is a powerful, easily deployable network traffic analysis tool suite for full packet capture artifacts (PCAP files), Zeek logs and Suricata…
 zdhenard42/soc-multitool
A powerful and user-friendly browser extension that streamlines investigations for security professionals.
 inverse-inc/packetfence
PacketFence is a fully supported, trusted, Free and Open Source network access control (NAC) solution. Boasting an impressive feature set including a…
 wecooperate/imonitorsdk
The world's most powerful System Activity Monitor Engine · 一款功能强大的终端行为采集防御开发套件 ~ 旨在帮助EDR、零信任、数据安全、审计管控等终端安全软件可以快速实现产品功能,…
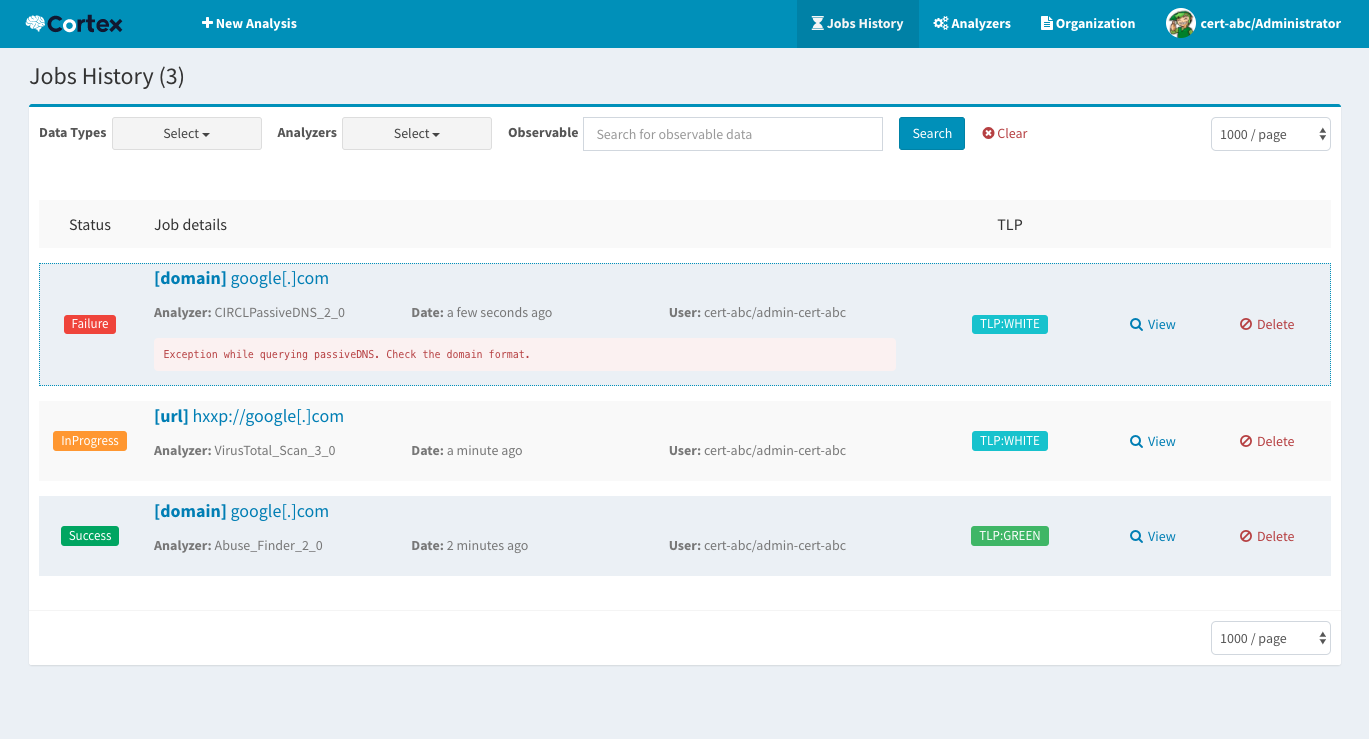 thehive-project/cortex
Cortex: a Powerful Observable Analysis and Active Response Engine
 winsiderss/systeminformer
Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
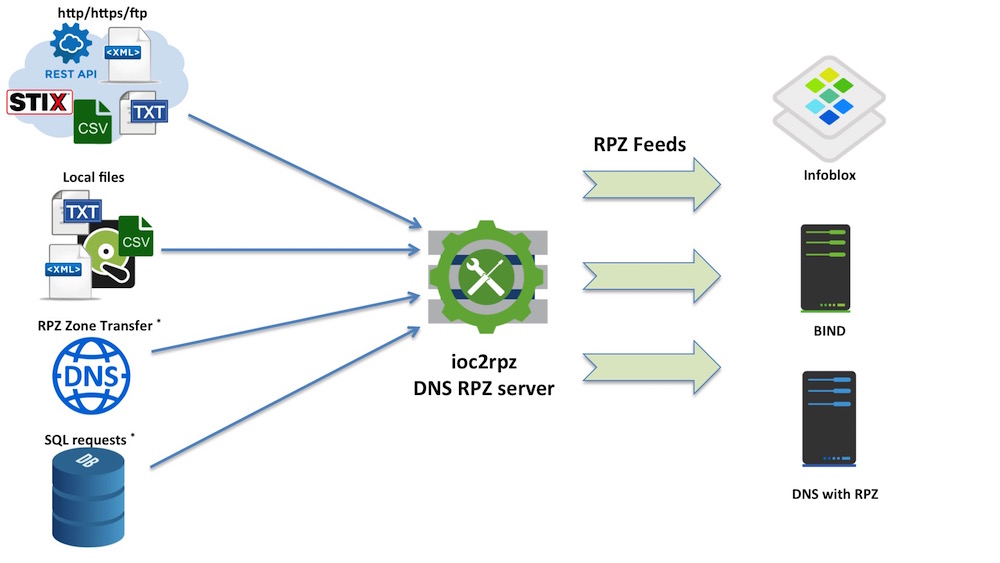 homas/ioc2rpz
ioc2rpz is a place where threat intelligence meets DNS.
 vineet7800/cpanel-malware-cleaner-cve-2026
Detects and removes malware, botnets, and webshells from cPanel servers, mitigating CVE-2026-41940 and related RCE vulnerabilities with one-command…
 neo23x0/loki
IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…
 password123456/malwarescanner
Hash-based malware scanner for incident response. Scans files recursively using known malware hashes, supports multithreading, extension filtering,…
 codeshield-security/log4jshell-bytecode-detector
Local Bytecode Scanner for the Log4JShell Vulnerability (CVE-2021-44228)
 perplexityai/bumblebee
Read-only developer endpoint scanner for on-disk package, extension, and developer-tool metadata, built to check exposure to known software…
 sandflysecurity/sandfly-entropyscan
Entropy scanner for Linux to detect packed or encrypted binaries related to malware. Finds malicious files and Linux processes and gives output with…
 fox-it/citrix-netscaler-triage
Forensic triage toolkit for Citrix NetScaler devices, featuring a Dissect-based IOC scanner for webshells, timestomping, and suspicious binaries,…
 dave_m/clamtk
An easy to use, light-weight, on-demand virus scanner for Linux systems. For additional help, see the <a…