
MacOSThreatTrack
 ab2pentest/macosthreattrack
Bash tool used for proactive detection of malicious activity on macOS systems.
digital-forensicsincident-responseinformation-gathering+1
40
ab2pentest/macosthreattrackBash tool used for proactive detection of malicious activity on macOS systems.
 t0pcyber/hawk
Powershell Based tool for gathering information related to O365 intrusions and potential Breaches
 tclahr/uac
Portable, dependency-free incident response tool that automates forensic artifact collection from Unix-like systems, including memory acquisition,…
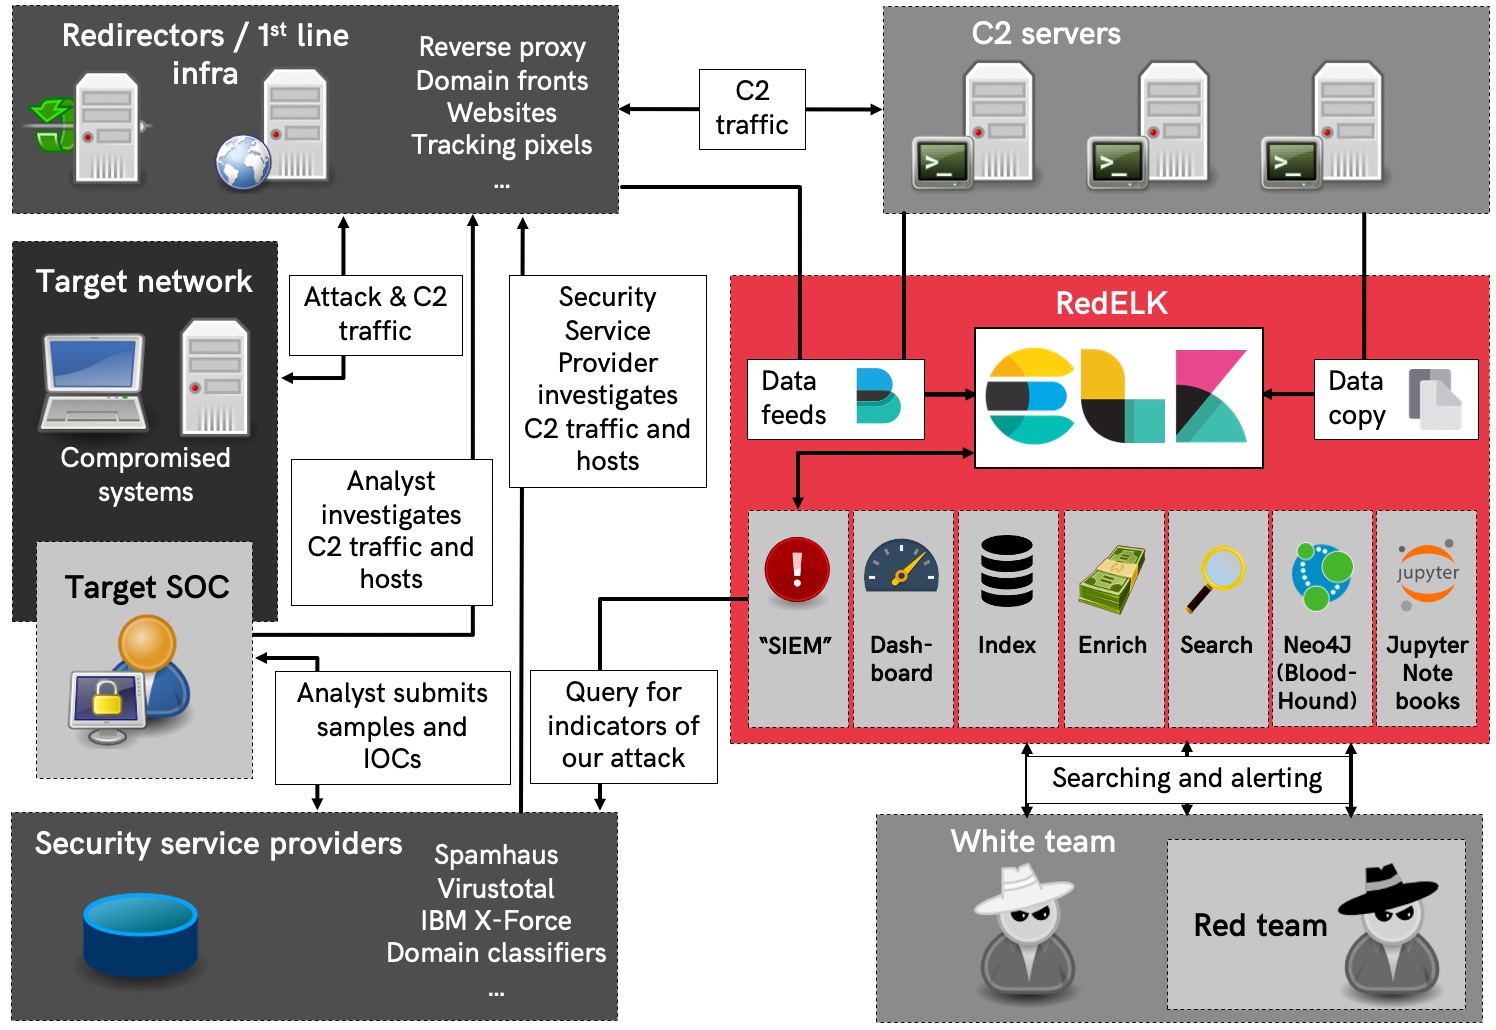 outflanknl/redelk
Red Team's SIEM - tool for Red Teams used for tracking and alarming about Blue Team activities as well as better usability in long term operations.
 adrecon/adrecon
PowerShell tool that extracts Active Directory artifacts via LDAP or ADWS and generates Excel reports for auditing, DFIR, and penetration testing.
 viralmaniar/remote-desktop-caching-
This tool allows one to recover old RDP (mstsc) session information in the form of broken PNG files. These PNG files allows Red Team member to…
 abdulrhmanalfaifi/fennec
Artifact collection tool for *nix systems
 zomato/vinifera
A GitHub recon/monitoring tool for finding internal leaks belonging to your organisation.
 st2labs/sipi
Simple IP Information Tools for Reputation Data Analysis
 abdaullahag/threatlens
Python CLI tool for rapid IOC analysis (IPs, Domains, CVEs) using 6 free Threat Intel APIs. Outputs: Color-coded Excel, JSON, CSV. Uses: VT, Shodan,…
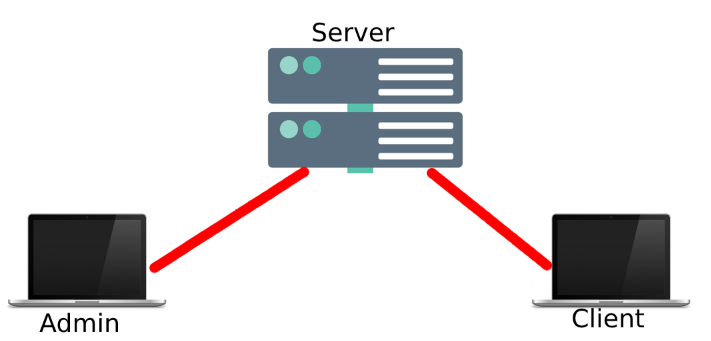 letsdefendio/simple-live-data-collection
Client-server tool for live data collection during incident response. Admin sends requests to clients to gather system information for forensic…
 emrekybs/bluefish
Automation tool designed to simplify the analysis of PCAP (Packet Capture) files
 nccgroup/impossibletravelloganalysis
Basic log analysis tool to detect impossible travel via IP address geographic information
 gamelinux/passivedns
A network sniffer that logs all DNS server replies for use in a passive DNS setup
 invictus-ir/microsoft-extractor-suite
A PowerShell module for acquisition of data from Microsoft 365 and Azure for Incident Response and Cyber Security purposes.
 zdhenard42/soc-multitool
A powerful and user-friendly browser extension that streamlines investigations for security professionals.
 sap8899/reportly
AzureAD/EntraID user activity reporter for blue teams. Input a suspicious user and time frame to receive a detailed report of user info, actions, and…
 rushyo/vindicatetool
LLMNR/NBNS/mDNS Spoofing Detection Toolkit