
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
38 results
Live-Forensicator preview

Live-Forensicator

GitHubjohnng007/live-forensicator

Cross-platform incident response and live forensics toolkit with built-in detection, structured analysis, and report generation — designed for fast,…
incident-response
63314 days ago
RsWindowsThingies preview

RsWindowsThingies

GitHubforensicmatt/rswindowsthingies

Rust-based Windows forensic toolkit for real-time MFT monitoring, event log streaming, and channel enumeration, enabling live system analysis and…
digital-forensicsincident-responselog-analysis
236 years ago
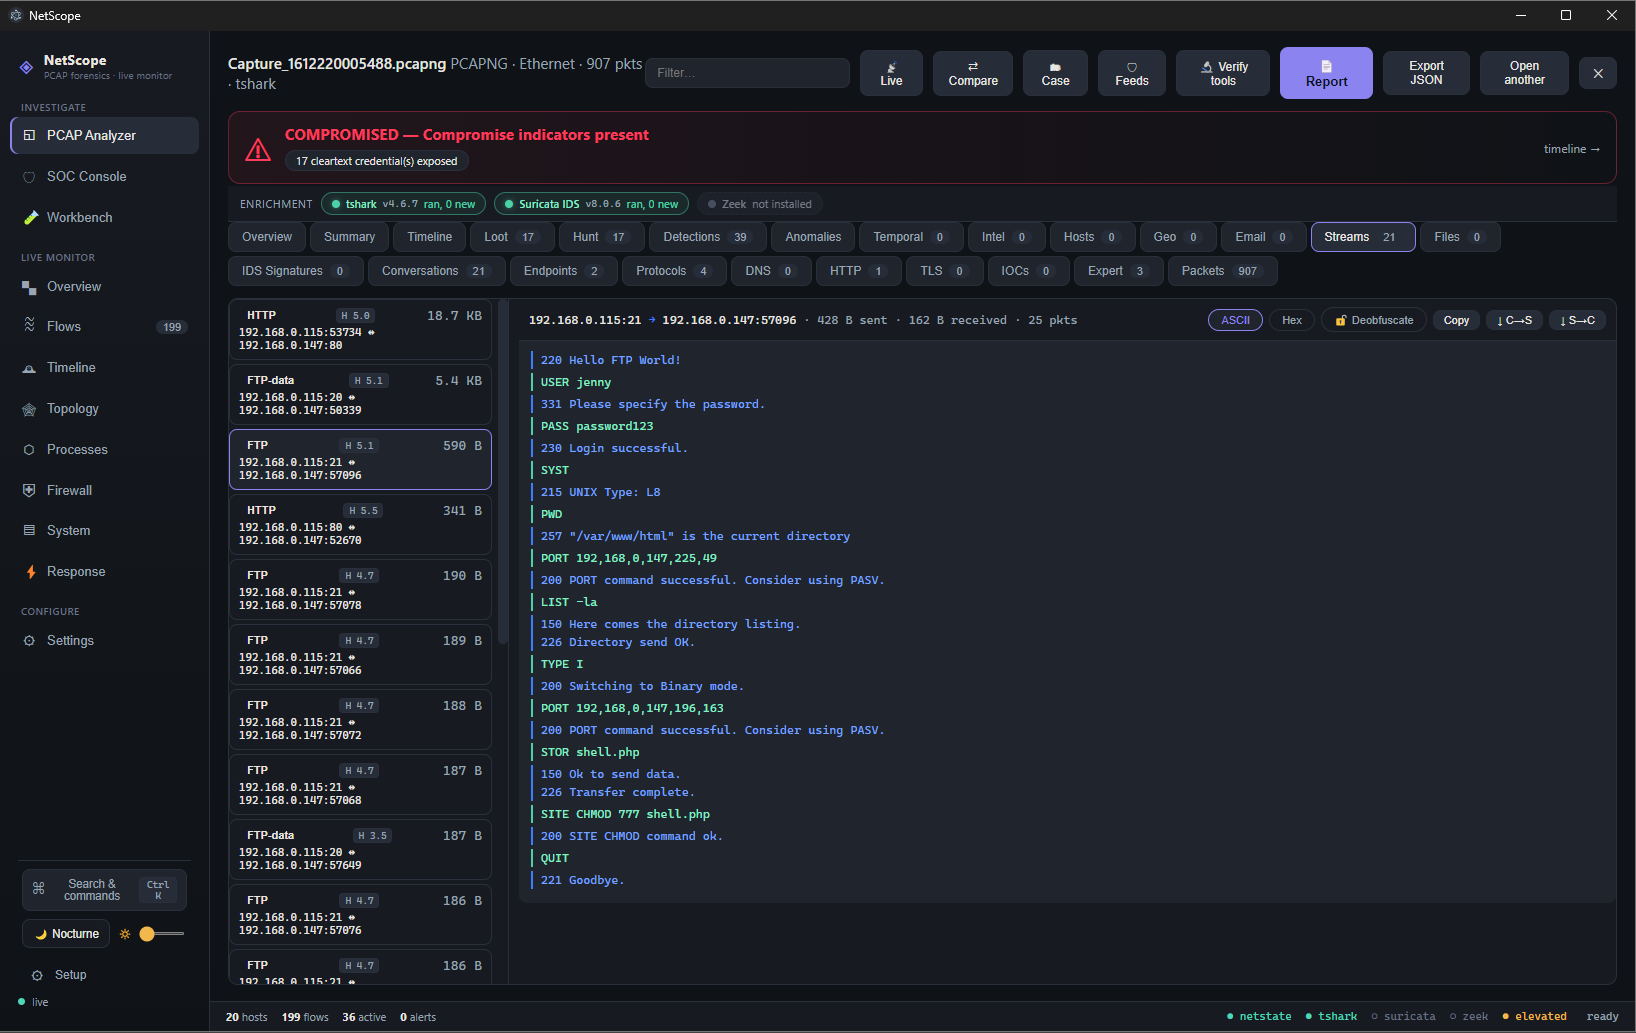
NetScope preview

NetScope

GitHubspectralzero/netscope

Offline-first network investigation and response platform for Windows. Turns a pcap or live capture into a full forensic verdict — attack story,…
anomaly-detectiondigital-forensicsincident-response+5
31 month ago
larac2shell preview

larac2shell

GitHubakefallonitis/larac2shell

Cross-platform interactive shell for Microsoft Defender for Endpoint Live Response
authenticationcommand-and-controlincident-response+6
165 months ago
ToolShell-CVE-2025-53770-SharePoint-Exploit-Lab-LetsDefend preview

ToolShell-CVE-2025-53770-SharePoint-Exploit-Lab-LetsDefend

GitHubcyprianatsyor/toolshell-cve-2025-53770-sharepoint-exploit-lab-letsdefend

Step-by-step walkthrough of exploiting CVE-2025-53770 (ToolShell) in a LetsDefend lab, covering RCE, web shell deployment, and incident response…
command-and-controlctfdigital-forensics+9
1 year ago
Fastir_Collector preview

Fastir_Collector

GitHubsekoialab/fastir_collector

Live Windows forensic acquisition tool that collects system artefacts (registry, memory, disk, files) into CSV/JSON for early compromise detection…

digital-forensicsdisk-forensicsforensics+3
5215 years ago
aether preview

aether

GitHub0xsp-srd/aether

Windows memory-forensics and threat hunting tool that scans live process memory for malicious patterns, injection techniques, and reflectively loaded…

binary-analysiscommand-and-controldigital-forensics+7
672 months ago
Incident-Response-Powershell preview

Incident-Response-Powershell

GitHubbert-janp/incident-response-powershell

PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…
digital-forensicsdisk-forensicsforensics+6
8164 months ago
Filedumper preview

Filedumper

GitHubseyyidkadir/filedumper

Windows memory forensics tool for dumping files from process memory regions, searching byte patterns (PDF, JPG, SWF), and performing live process…
data-recoverydigital-forensicsforensics+3
18 months ago
pyrdp preview

pyrdp

GitHubgosecure/pyrdp

RDP monster-in-the-middle (mitm) and library for Python with the ability to watch connections live or after the fact
ctfeducationexploitation+9
1.8k4 months ago
openclaw-dashboard preview

openclaw-dashboard

GitHubtugcantopaloglu/openclaw-dashboard

🔐 Secure, real-time monitoring dashboard for OpenClaw AI agents. Auth, TOTP MFA, cost tracking, live feed, memory browser and more.
api-securityauthenticationcloud-security+7
7016 months ago
CVE-2026-93616_Checks preview

CVE-2026-93616_Checks

GitHubwadesweaponshed/cve-2026-93616_checks

Shell and SmartDashboard scripts that check Check Point management servers for indicators of compromise tied to CVE-2026-93616, including rogue…
defensive-toolsincident-responseinformation-gathering+3
3 days ago
shadow-fleet-tracker-light preview

shadow-fleet-tracker-light

GitHubformerlab/shadow-fleet-tracker-light

Open source Baltic Sea shadow fleet tracker. 1200+ vessels, live AIS, cable proximity alerts. No cloud, no subscription, runs locally
data-exfiltrationdigital-forensicsdns-analysis+9
444 months ago
pacmap preview

pacmap

GitHubm0vi0/pacmap

Graph-first network traffic visualizer for live capture and PCAP replay with checkpoint diffing, path tracing, and Wireshark-style display filters…
dns-analysisforensicsincident-response+4
1320 days ago
RemotePSpy preview

RemotePSpy

GitHubwithsecurelabs/remotepspy

Live monitoring tool for remote PowerShell sessions using ETW to capture and decode WinRM/PSRP protocol, providing command execution traces and…

defensive-toolsdigital-forensicsincident-response+3
196 years ago
ZeroScout preview

ZeroScout

GitHubsumidcyber/zeroscout

🦅 ZeroScout: The Autonomous Local & Cloud Threat Hunter. Visualize attacks in a live War Room, identify APT groups via Genetic Analysis, and…
defensive-toolsdigital-forensicseducation+7
129 months ago
netsentryx preview

netsentryx

GitHubaman-sharma-dev/netsentryx

An event-driven network monitoring platform that performs live packet capture (Npcap), low-latency traffic analytics, and unsupervised threat…

anomaly-detectioncloud-securitydefensive-tools+6
1 month ago
awesome-incident-response preview

awesome-incident-response

GitHubmeirwah/awesome-incident-response

Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…

curated-resourcesdigital-forensicsdisk-forensics+9
9.4k2 months ago
Previous123Next