
xz-cve-2024-3094
 hackura/xz-cve-2024-3094
Python demo simulating CVE-2024-3094: a supply chain backdoor in XZ Utils with a trigger-based stealth activation.
digital-forensicseducationforensics+6
hackura/xz-cve-2024-3094Python demo simulating CVE-2024-3094: a supply chain backdoor in XZ Utils with a trigger-based stealth activation.
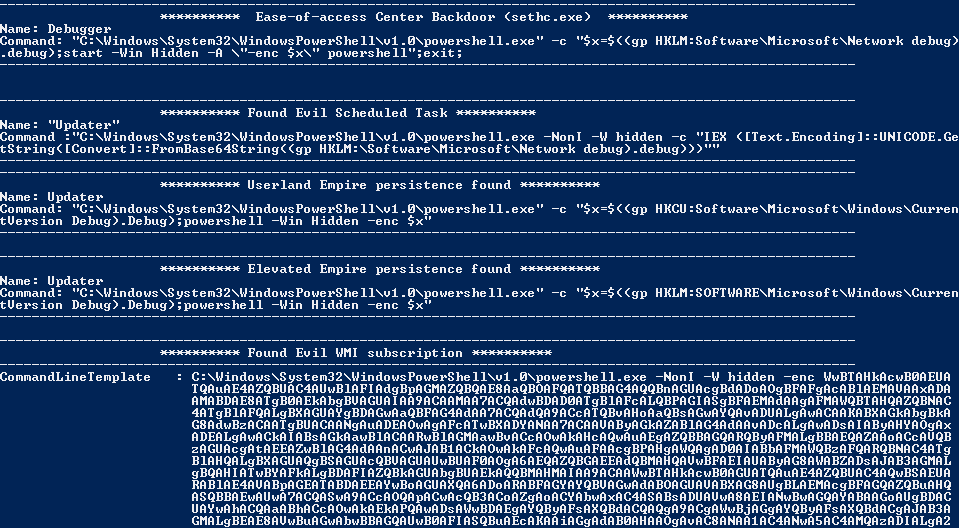 n00py/norknork
Powershell Empire Persistence finder
 lockness-ko/xz-vulnerable-honeypot
An ssh honeypot with the XZ backdoor. CVE-2024-3094
 24owais/threat-intel-cve-2024-3094
Threat intelligence report analyzing the xz-utils backdoor vulnerability (CVE-2024-3094)
 chaitin/mimicry
Active deception tool that transparently migrates attackers from real targets to honeypots during exploitation and post-exploitation, supporting…
 ngvcanh/cve-2025-55182-attack-analysis
Real-world attack analysis of CVE-2025-55182 (React2Shell) - React Server Components RCE vulnerability
 last-byte/persistencesniper
Powershell module that can be used by Blue Teams, Incident Responders and System Administrators to hunt persistences implanted in Windows machines.…
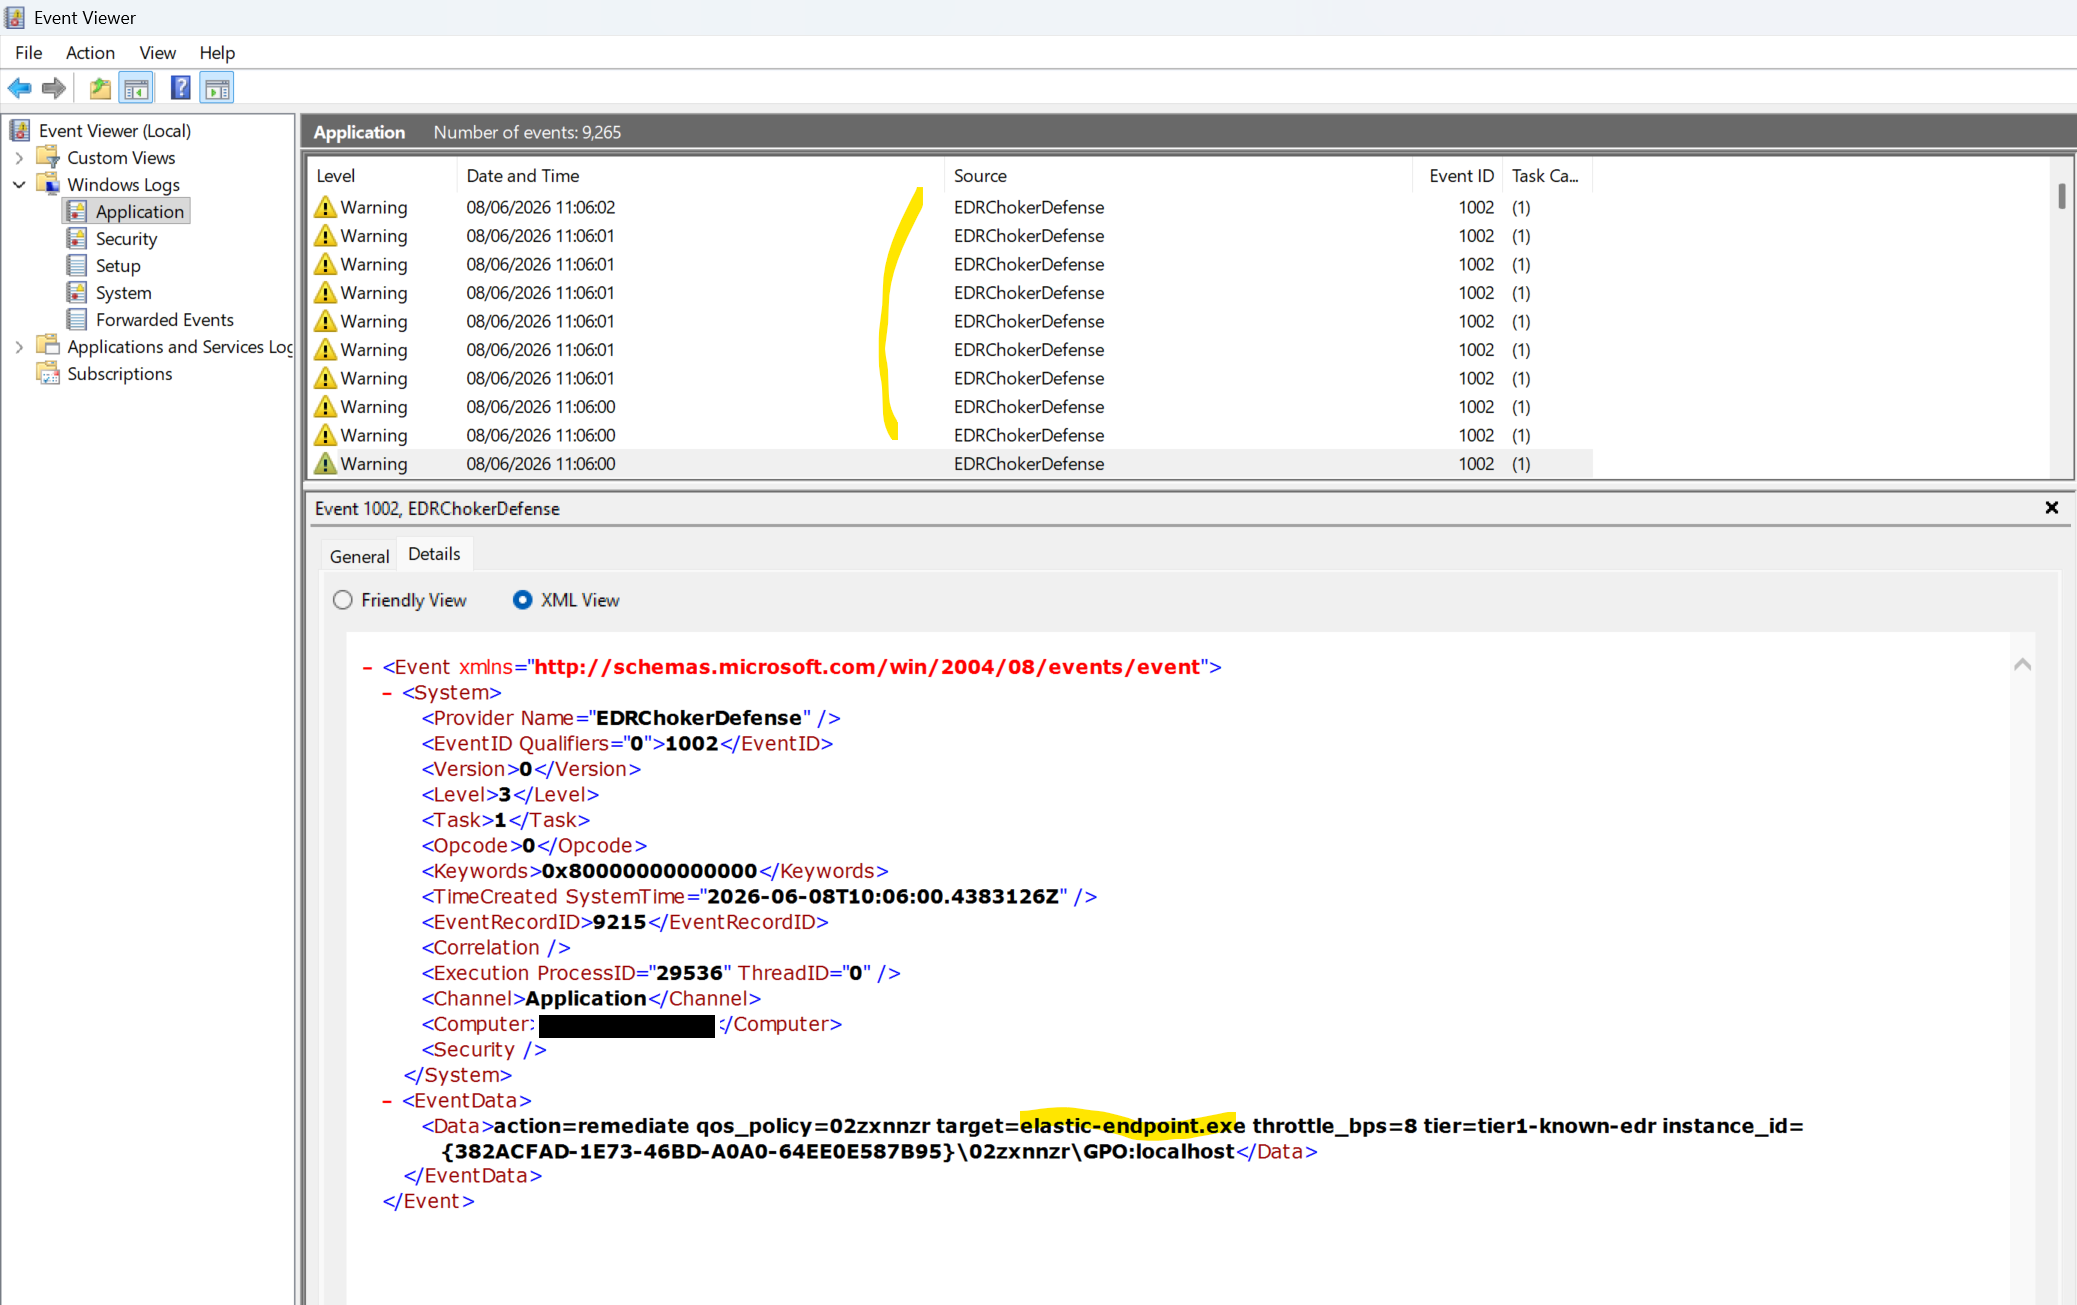 sbousseaden/edrunchoker
EDRUnChoker - fileless WMI defense that removes EDRChoker QoS throttling policies
 jfrog/cve-2024-3094-tools
Shell-based scanner to detect the XZ Backdoor (CVE-2024-3094) vulnerability in files and directories, enabling rapid identification and mitigation of…
 mr-r3b00t/cve-2021-44228
PowerShell-based backdoor detection tool for VMware Horizon connection servers, targeting CVE-2021-44228. Includes canary with optional submission…
 michel-dv/xz-utils-backdoor-case-study
Technical case study of the XZ Utils backdoor (CVE-2024-3094), covering supply-chain trust abuse, malicious release artifacts, build-stage injection,…
 kaminaduck/ansible-cve-2024-3094
Ansible playbooks designed to check and remediate CVE-2024-3094 (XZ Backdoor)
 nnatsopoulos/xz-backdoor-research
CVE-2024-3094 XZ Utils backdoor research - attack surface visualiser, system vulnerability checker, and general Linux CVE assessment tool
 czabatta/thm-tempest
TryHackMe SOC Level 1 — Follina CVE-2022-30190, Nim C2, Chisel, PrintSpoofer, backdoor accounts
 nitinsukthe-g/openvas-vulnerability-assessment-incident-response
Performed a Full & Fast vulnerability assessment using OpenVAS against Metasploitable2, identified the critical vsftpd Backdoor vulnerability…
 m1lo25/cs50finalproject
Investigation into the XZ Utils backdoor (CVE-2024-3094): chronology, attack chain, risk to SSH, and supply-chain insights. Includes slides, sources,…
 devjanger/cve-2024-3094-xz-backdoor-detector
Shell script to detect the CVE-2024-3094 backdoor in XZ Utils by checking for malicious code in liblzma build artifacts and identifying affected…
 juul/xz-backdoor-scan
Scan for files containing the signature from the `xz` backdoor (CVE-2024-3094)