
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
126 results
misp-objects preview

misp-objects

GitHubmisp/misp-objects

Curated JSON object templates that define MISP attributes and relationship types for structured threat intelligence sharing and interoperable IOC…

curated-resourcesincident-responseioc-management+3
111
4 days ago
CIRTKit preview

CIRTKit

GitHubopensourcesec/cirtkit

Tools for the Computer Incident Response Team :computer:

digital-forensicsforensicsincident-response+2
1529 years ago
ransomware-simulator preview

ransomware-simulator

GitHubnccgroup/ransomware-simulator

NCC Group Ransomware Simulator
defensive-toolseducationincident-response+3
6910 years ago
Vidar-Stealer-Reverse-Engineering preview

Vidar-Stealer-Reverse-Engineering

GitHubkaandemir993/vidar-stealer-reverse-engineering

"In-depth reverse engineering analysis of Vidar Stealer 2.0 covering Task Scheduler tampering (1999 timestamps), Explorer.exe process hollowing, and…
binary-analysiseducationforensics+7
23 months ago
wazuhlabproject preview

wazuhlabproject

GitHubswastiksagar/wazuhlabproject

Hands-on Wazuh SIEM/XDR home lab covering OVA deployment, agent enrollment, file integrity monitoring, VirusTotal malware detection, and MITRE ATT&CK…
configuration-auditingdefensive-toolsdigital-forensics+7
33 months ago
CVE-2022-22965-Spring4Shell-Security-Operations-Analysis preview

CVE-2022-22965-Spring4Shell-Security-Operations-Analysis

GitHubshakur1314/cve-2022-22965-spring4shell-security-operations-analysis

A comprehensive Security Operations Centre (SOC) incident response simulation demonstrating threat detection, triage, analysis, and mitigation of the…
educationincident-responselog-analysis+3
8 months ago
cve-mcp-server preview

cve-mcp-server

GitHubmukul975/cve-mcp-server

Production-grade MCP server giving Claude 27 security intelligence tools across 21 APIs — CVE lookup, EPSS scoring, CISA KEV, MITRE ATT&CK, Shodan,…

api-securitydevsecopsincident-response+6
1.1k4 months ago
Data-Shield_IPv4_Blocklist preview

Data-Shield_IPv4_Blocklist

GitHubduggytuxy/data-shield_ipv4_blocklist

Curated IPv4 blocklist of malicious addresses, refreshed every 6 hours for firewall and WAF ingestion, with split lists and CTI-ready formats for…
defensive-toolsincident-responseinformation-gathering+5
6236h 12m ago
intelmq preview

intelmq

GitHubcerttools/intelmq

IntelMQ is a solution for IT security teams for collecting and processing security feeds using a message queuing protocol.
incident-responseinformation-gatheringintrusion-detection+6
1.1k6 months ago
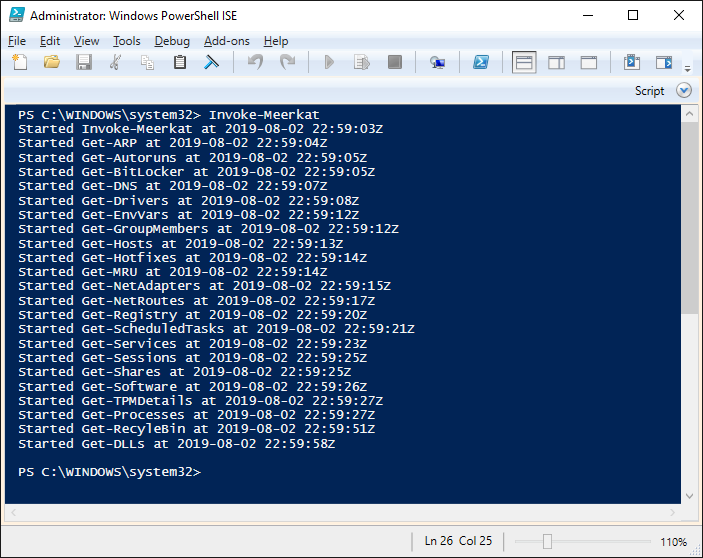
Meerkat preview

Meerkat

GitHubtonyphipps/meerkat

A collection of PowerShell modules designed for artifact gathering and reconnaisance of Windows-based endpoints.
digital-forensicsforensicsincident-response+2
4831 year ago
rastrea2r preview

rastrea2r

GitHubrastrea2r/rastrea2r

Collecting & Hunting for IOCs with gusto and style
digital-forensicsforensicsincident-response+6
23822 days ago
pockint preview

pockint

GitHubedoardogerosa/pockint

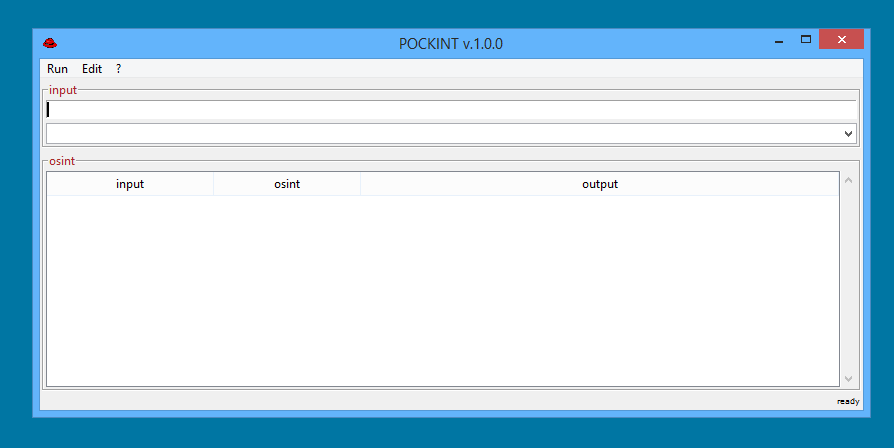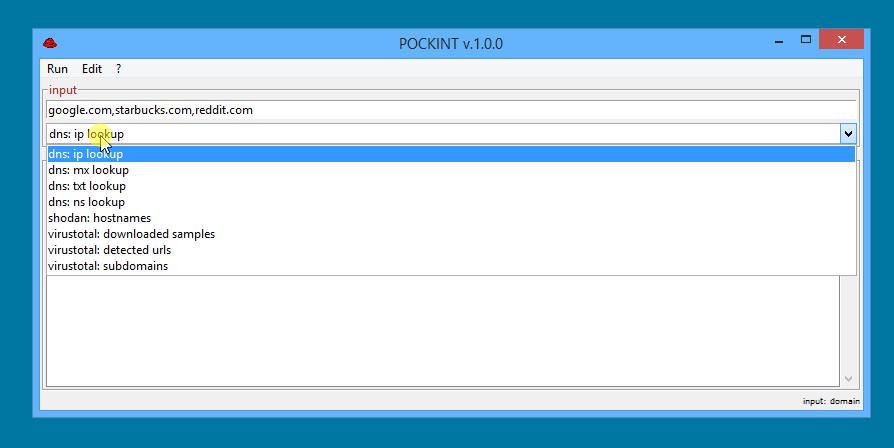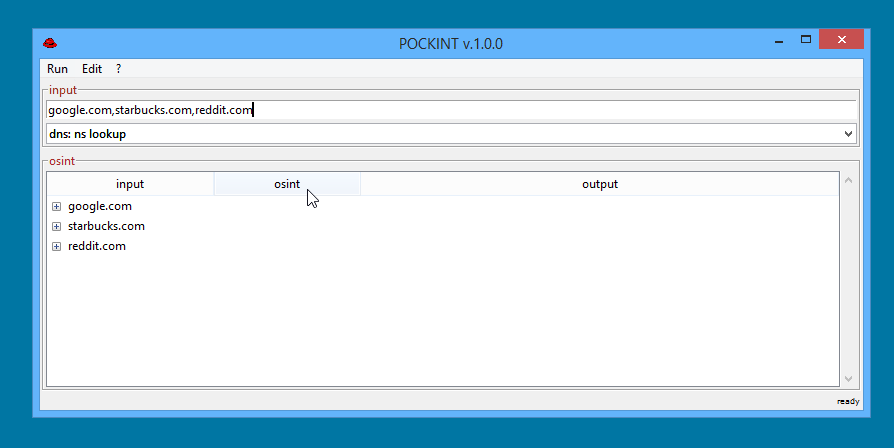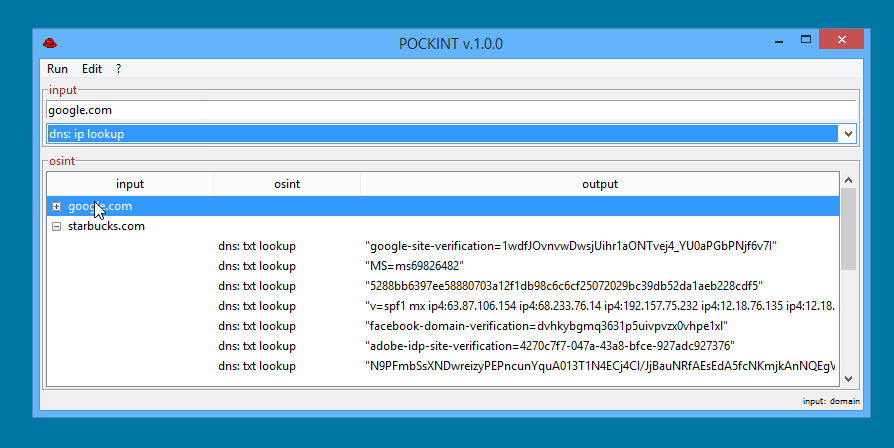
A portable OSINT Swiss Army Knife for DFIR/OSINT professionals 🕵️ 🕵️ 🕵️
digital-forensicsdns-analysisincident-response+5
2853 years ago
Credential-Hunting preview

Credential-Hunting

GitHubnecr00/credential-hunting

CredsHunter - Credential Hunting scripts for Windows and Linux OS

forensicsincident-responseinformation-gathering+7
1692 months ago
honeypot-data preview

honeypot-data

GitHub0x4d31/honeypot-data

Public honeypot datasets and observation reports with HTTP/TLS fingerprint data (JA3/JA4), pseudonymized source IPs, and exploitation attempt…

incident-responseinformation-gatheringioc-management+4
448 days ago
ThreatIntel-Aggregator preview

ThreatIntel-Aggregator

GitHubethan-andrews/threatintel-aggregator

Self-hosted threat intelligence platform — feed aggregation, AI triage, MITRE ATT&CK coverage, and Sentinel-integrated detection engineering. Runs…

ai-securitydefensive-toolsincident-response+7
601 month ago
shomon preview

shomon

GitHubkaansk/shomon

Shodan Monitoring integration for TheHive.
incident-responseinformation-gatheringosint+1
1304 years ago
gargamel preview

gargamel

GitHublifars/gargamel

A forensic evidence acquirer

digital-forensicsforensicsincident-response+3
865 years ago
gundog preview

gundog

GitHubjangeisbauer/gundog

gundog - guided hunting in Microsoft Defender

incident-responseinformation-gatheringlog-analysis+2
535 years ago
Previous1234567Next