
volatility-plugins
 withsecurelabs/volatility-plugins
Volatility plugins for memory forensics, including detection of Gargoyle memory scanning evasion techniques.
digital-forensicsforensicsincident-response+2
11
withsecurelabs/volatility-pluginsVolatility plugins for memory forensics, including detection of Gargoyle memory scanning evasion techniques.
 pugazhendii22/keepass-exfil-forensics
Network forensics writeup + tooling for a TryHackMe DFIR challenge: reverses a hex→Base64→XOR exfiltration chain from PCAP traffic, then recovers a…
 helpsystems/embarcadero-workaround
This is a workaround for CVE-2014-0993 and CVE-2014-0994 that patches on memory without the need to recompile your vulnerable software. This is not…
 areebashoaib42/keepass-cve-2023-32784-exploitation-and-defense
Exploitation and defense-in-depth mitigation strategies for the KeePass memory leakage vulnerability (CVE-2023-32784).
 adem-hosni/mappedimagesdetector
Lightweight native Windows memory scanner for AV/EDR platforms, detecting suspicious mapped images and manual DLL injection techniques by IAT thunk
 prox0959/memguard
Zero-dependency Windows EDR utility that detects and mitigates unauthorized LSASS memory access, handle duplication, and LOLBin credential dumping in…
 cado-security/rip_raw
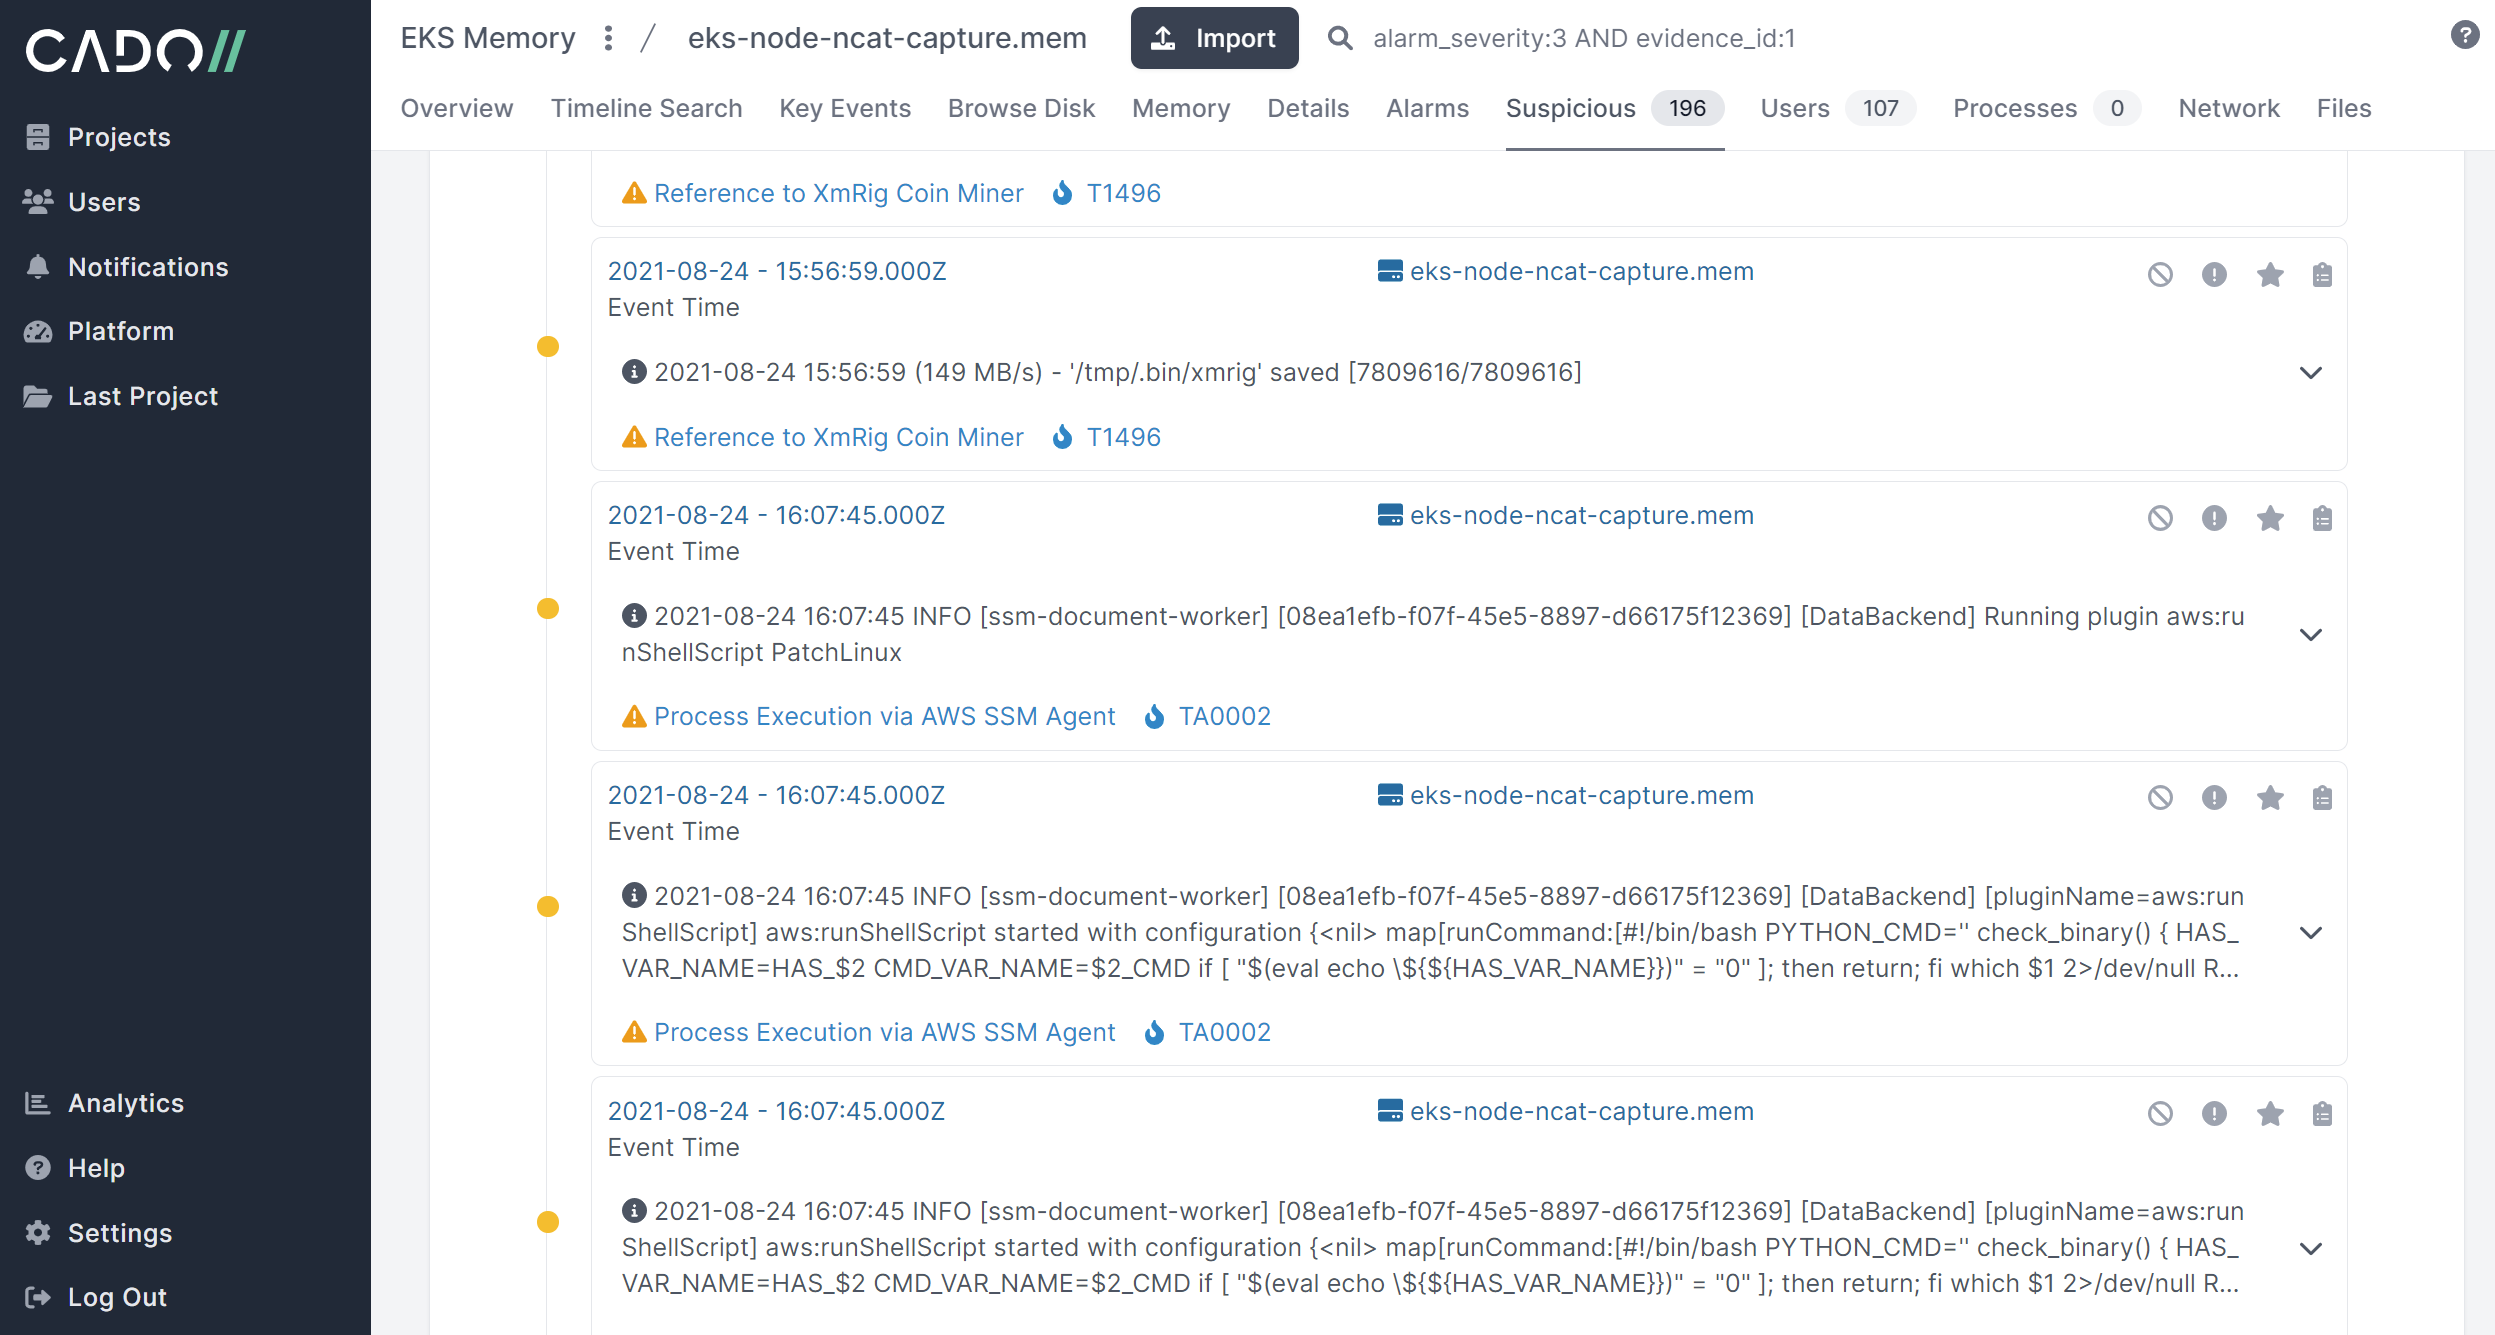
Rip Raw is a small tool to analyse the memory of compromised Linux systems.
 daddycocoaman/dumpscan
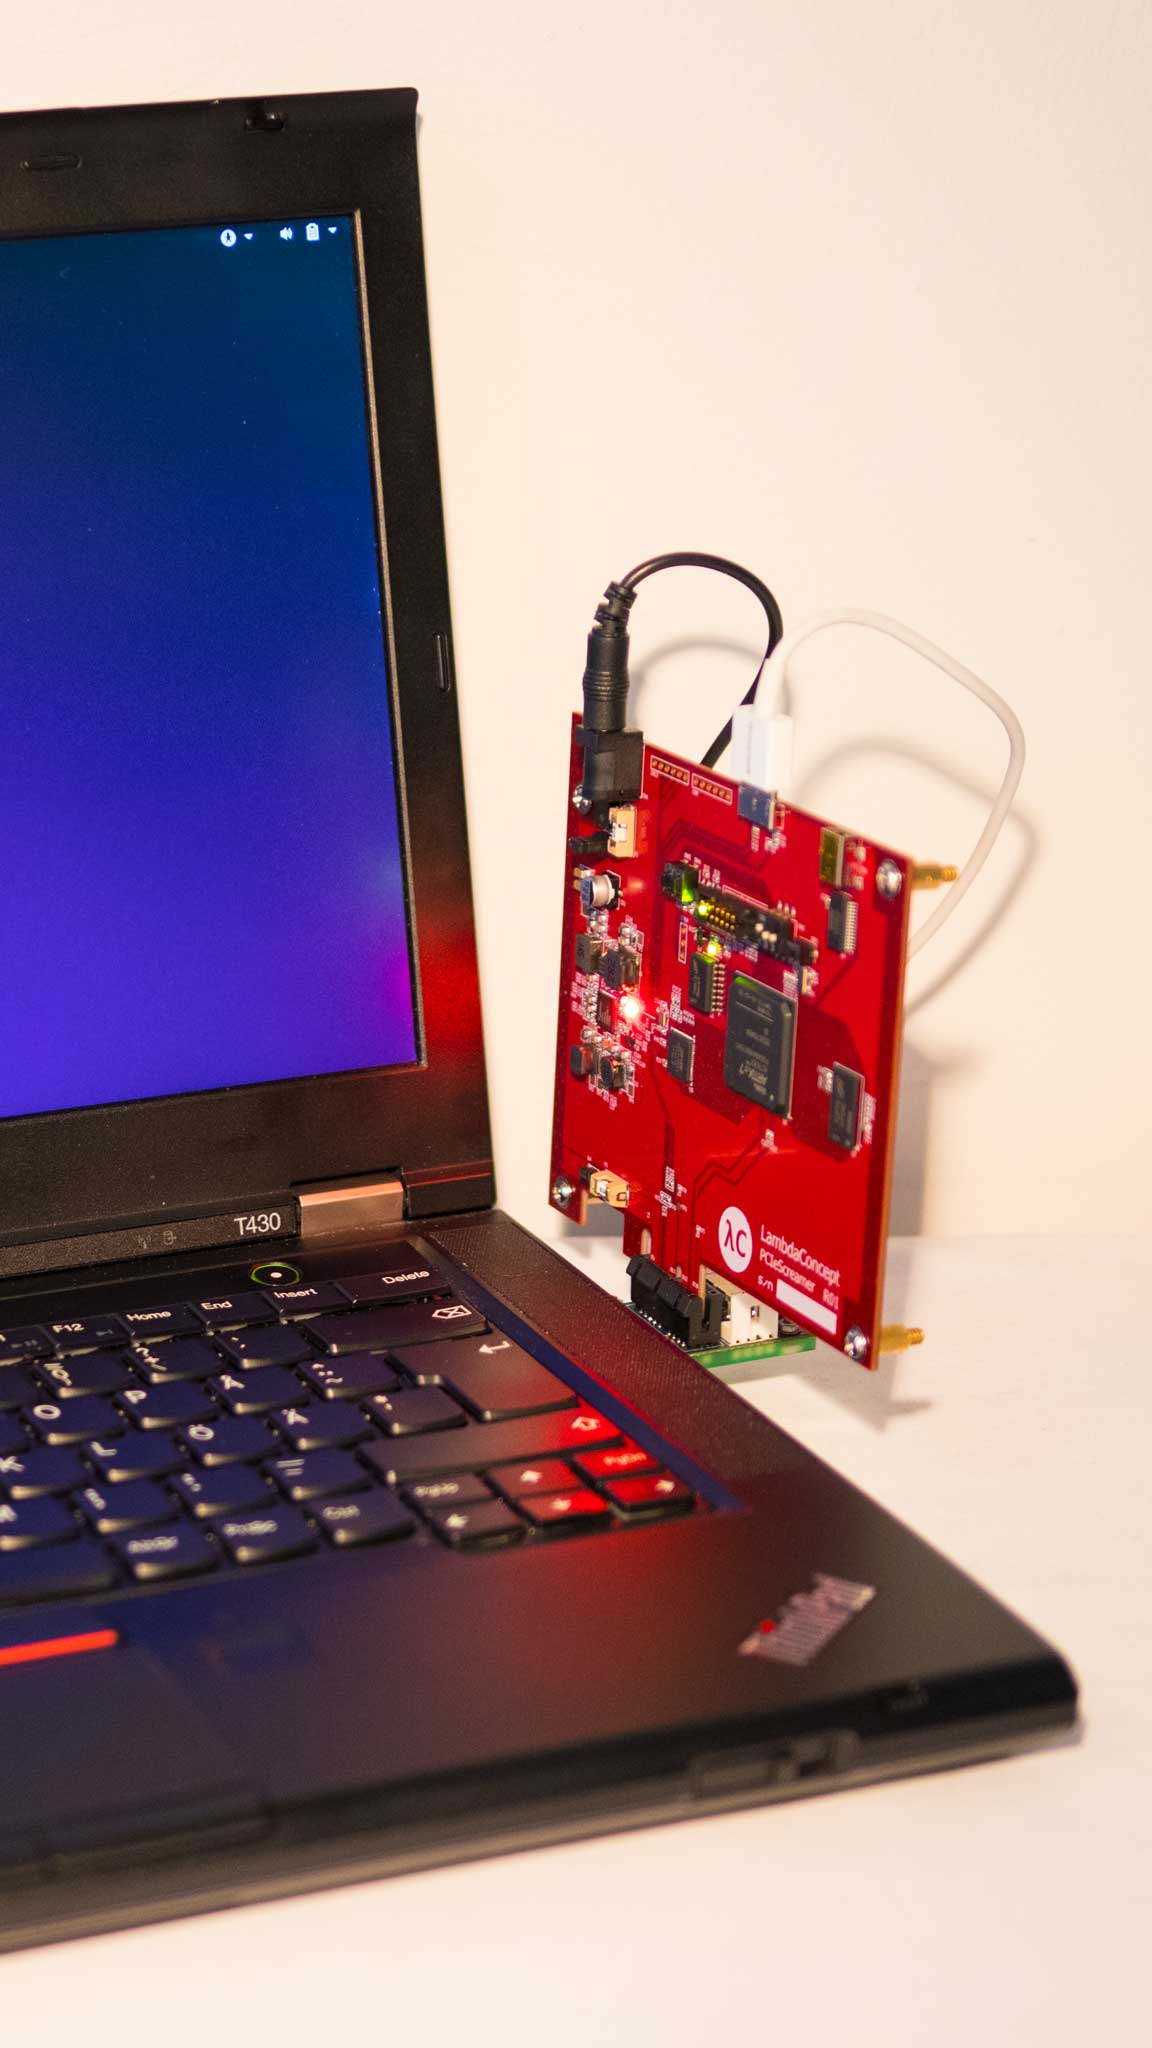
Finding secrets in kernel and user memory
 hasherezade/hollows_hunter
Scans all running processes. Recognizes and dumps a variety of potentially malicious implants (replaced/implanted PEs, shellcodes, hooks, in-memory…
 daffainfo/vol-rs
Volatility 3 ported to Rust. Same output, much faster.
 mingshenhk/citrixbleed-2-cve-2025-5777-poc-
详细讲解CitrixBleed 2 — CVE-2025-5777(越界泄漏)PoC 和检测套件
 mahradbt/copyfail-mitigation
Ansible playbooks to audit and mitigate CVE-2026-31431 ("Copy Fail"), a local privilege escalation vulnerability in the Linux kernel's `algif_aead`…
 mrk336/inside-cve-2026-20805-how-a-windows-dwm-flaw-exposed-sensitive-data
CVE‑2026‑20805: A Windows Desktop Window Manager flaw causing local information disclosure. Requires low privileges, no user interaction. Rated CVSS…
 intezer/linux-explorer
Easy-to-use live forensics toolbox for Linux endpoints