

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
84 results
honeypot-data preview

honeypot-data

GitHub0x4d31/honeypot-data

Public honeypot datasets and observation reports with HTTP/TLS fingerprint data (JA3/JA4), pseudonymized source IPs, and exploitation attempt…
incident-responseinformation-gatheringioc-management+4
44
8 days ago
FarsightAD preview

FarsightAD

GitHubqazeer/farsightad

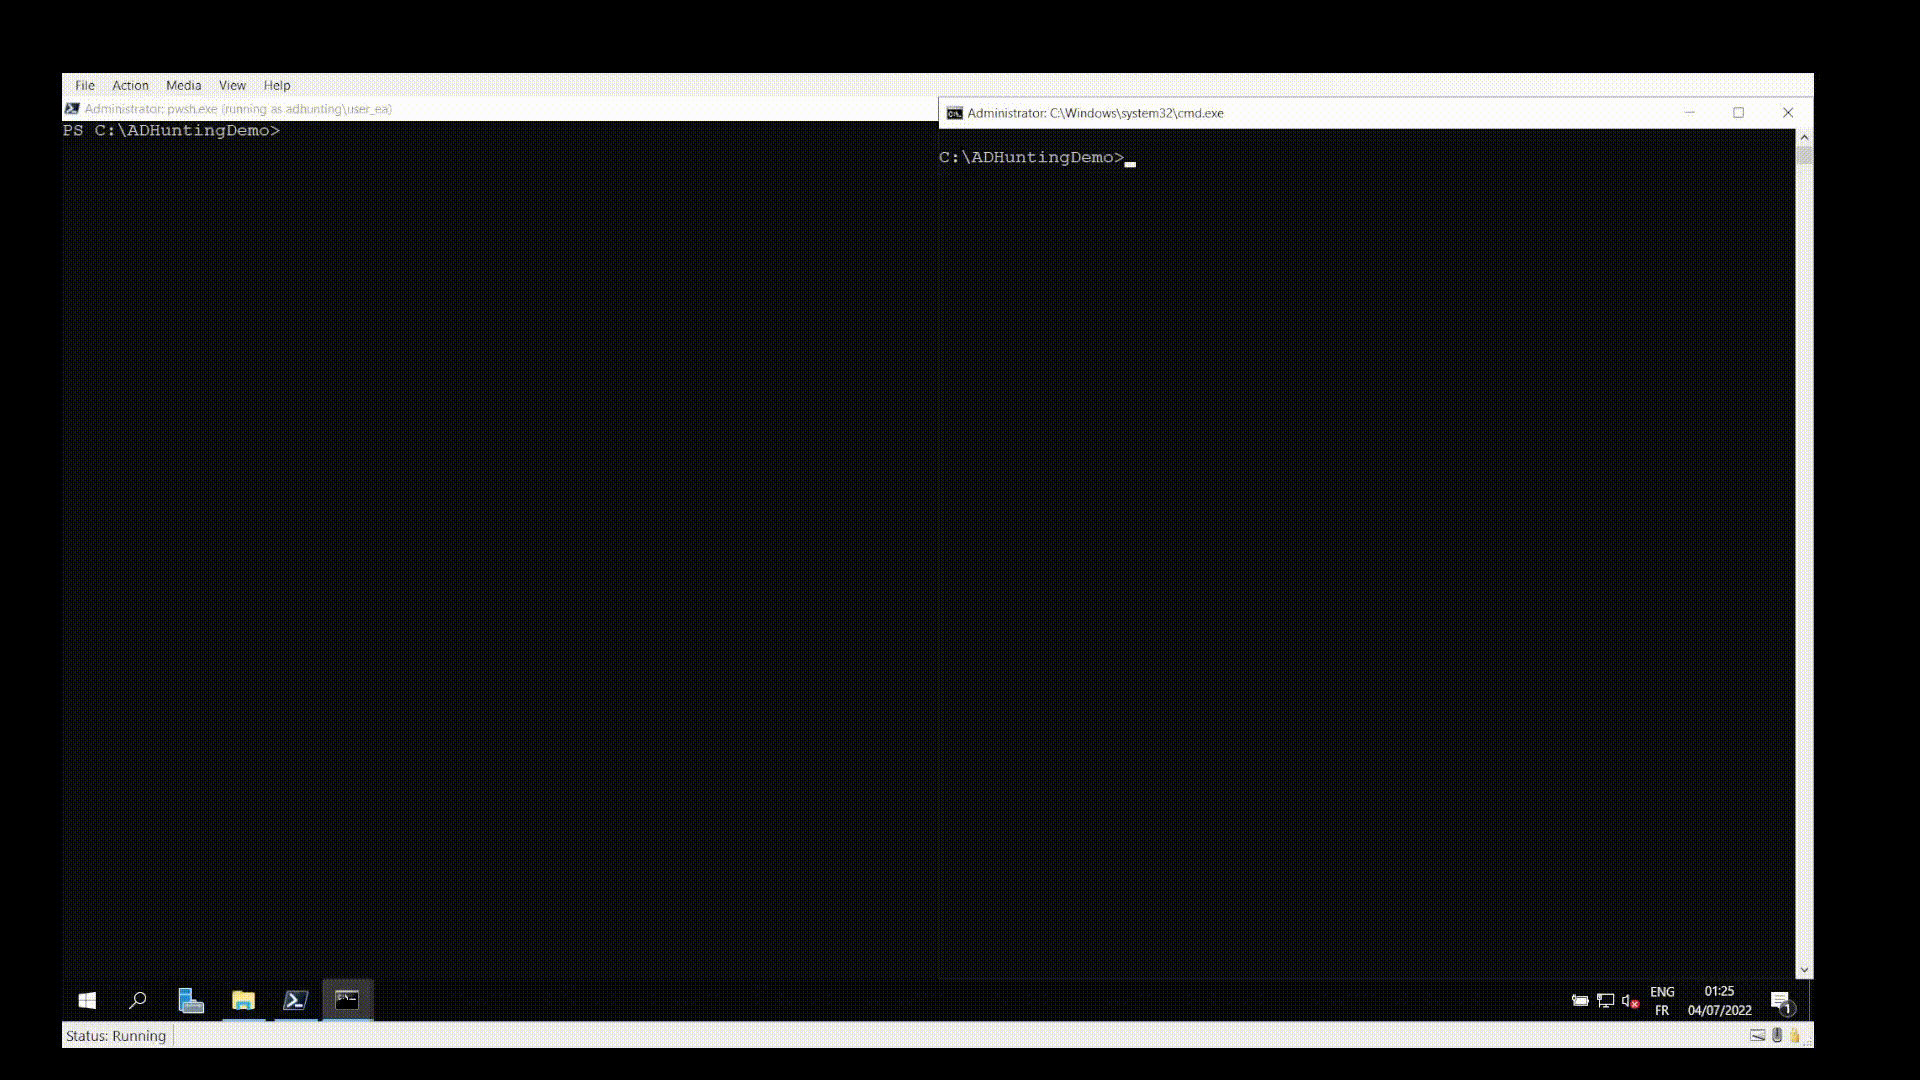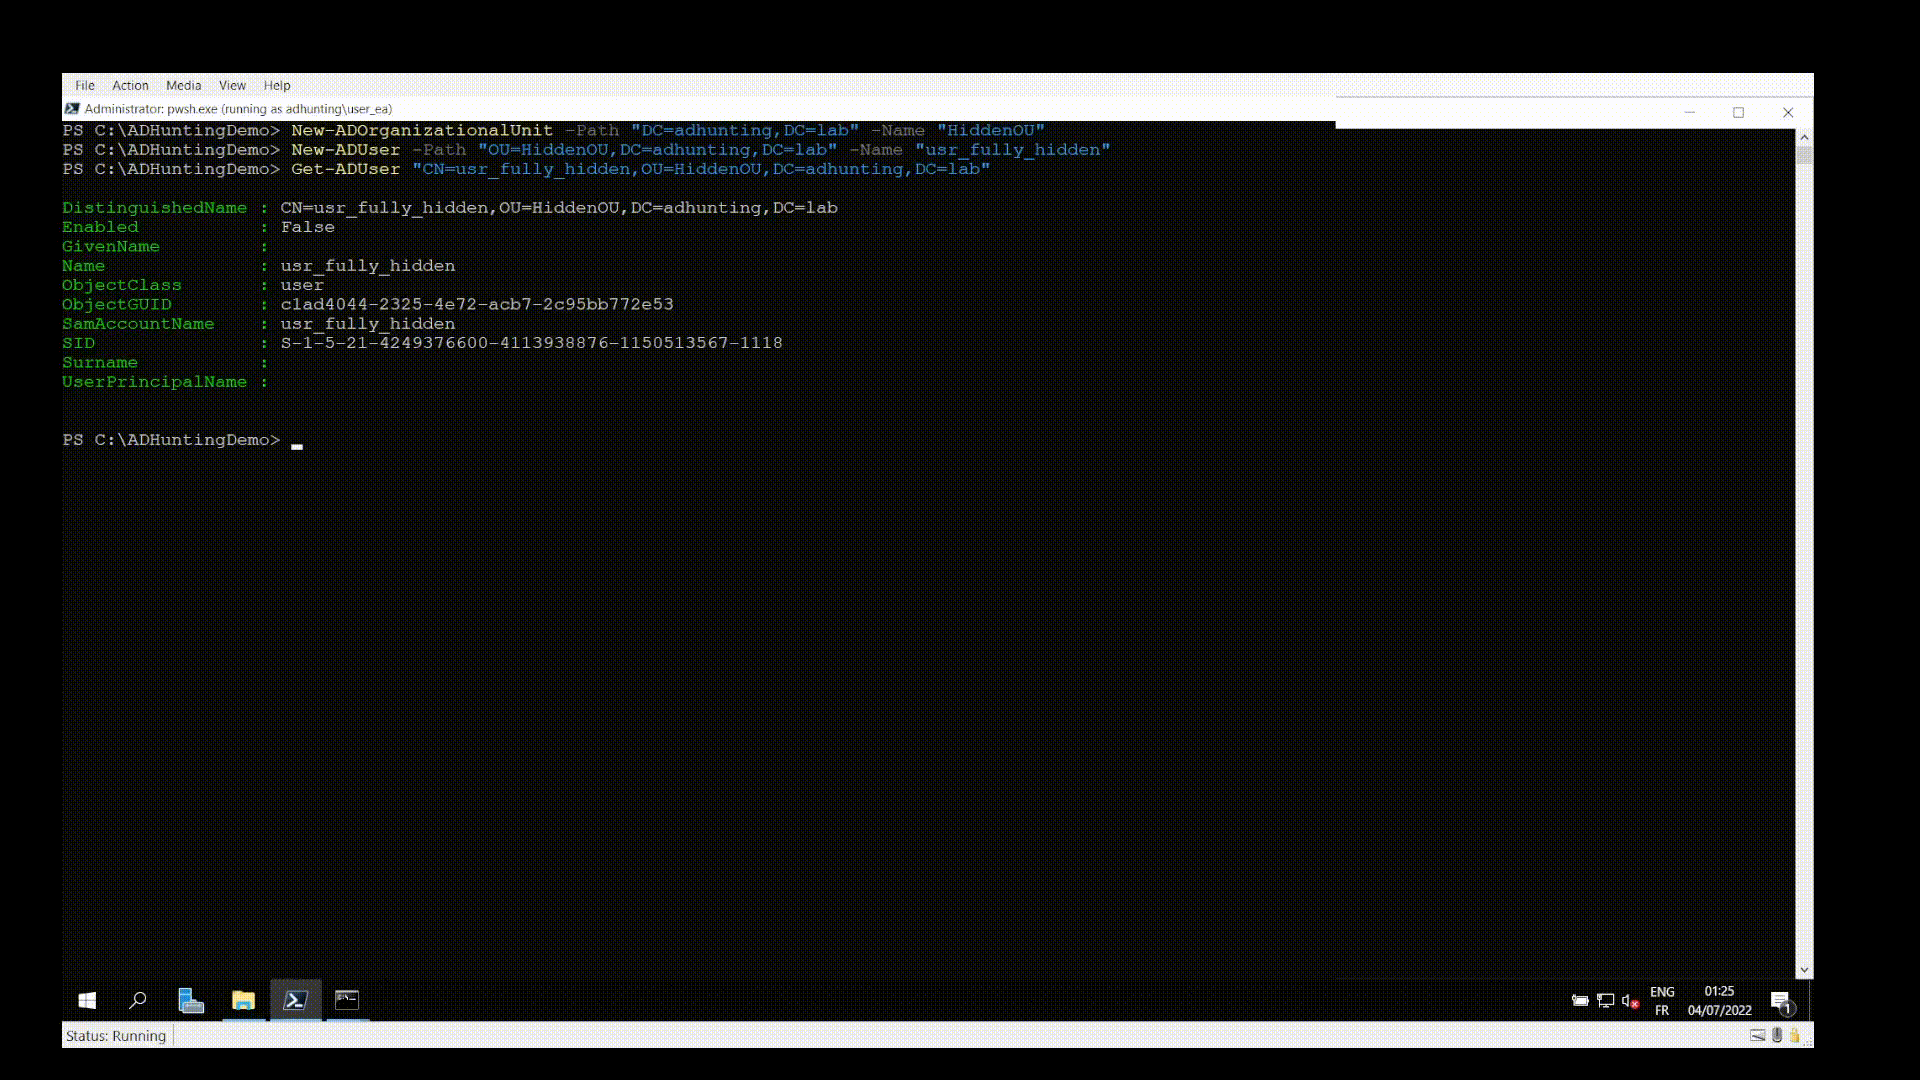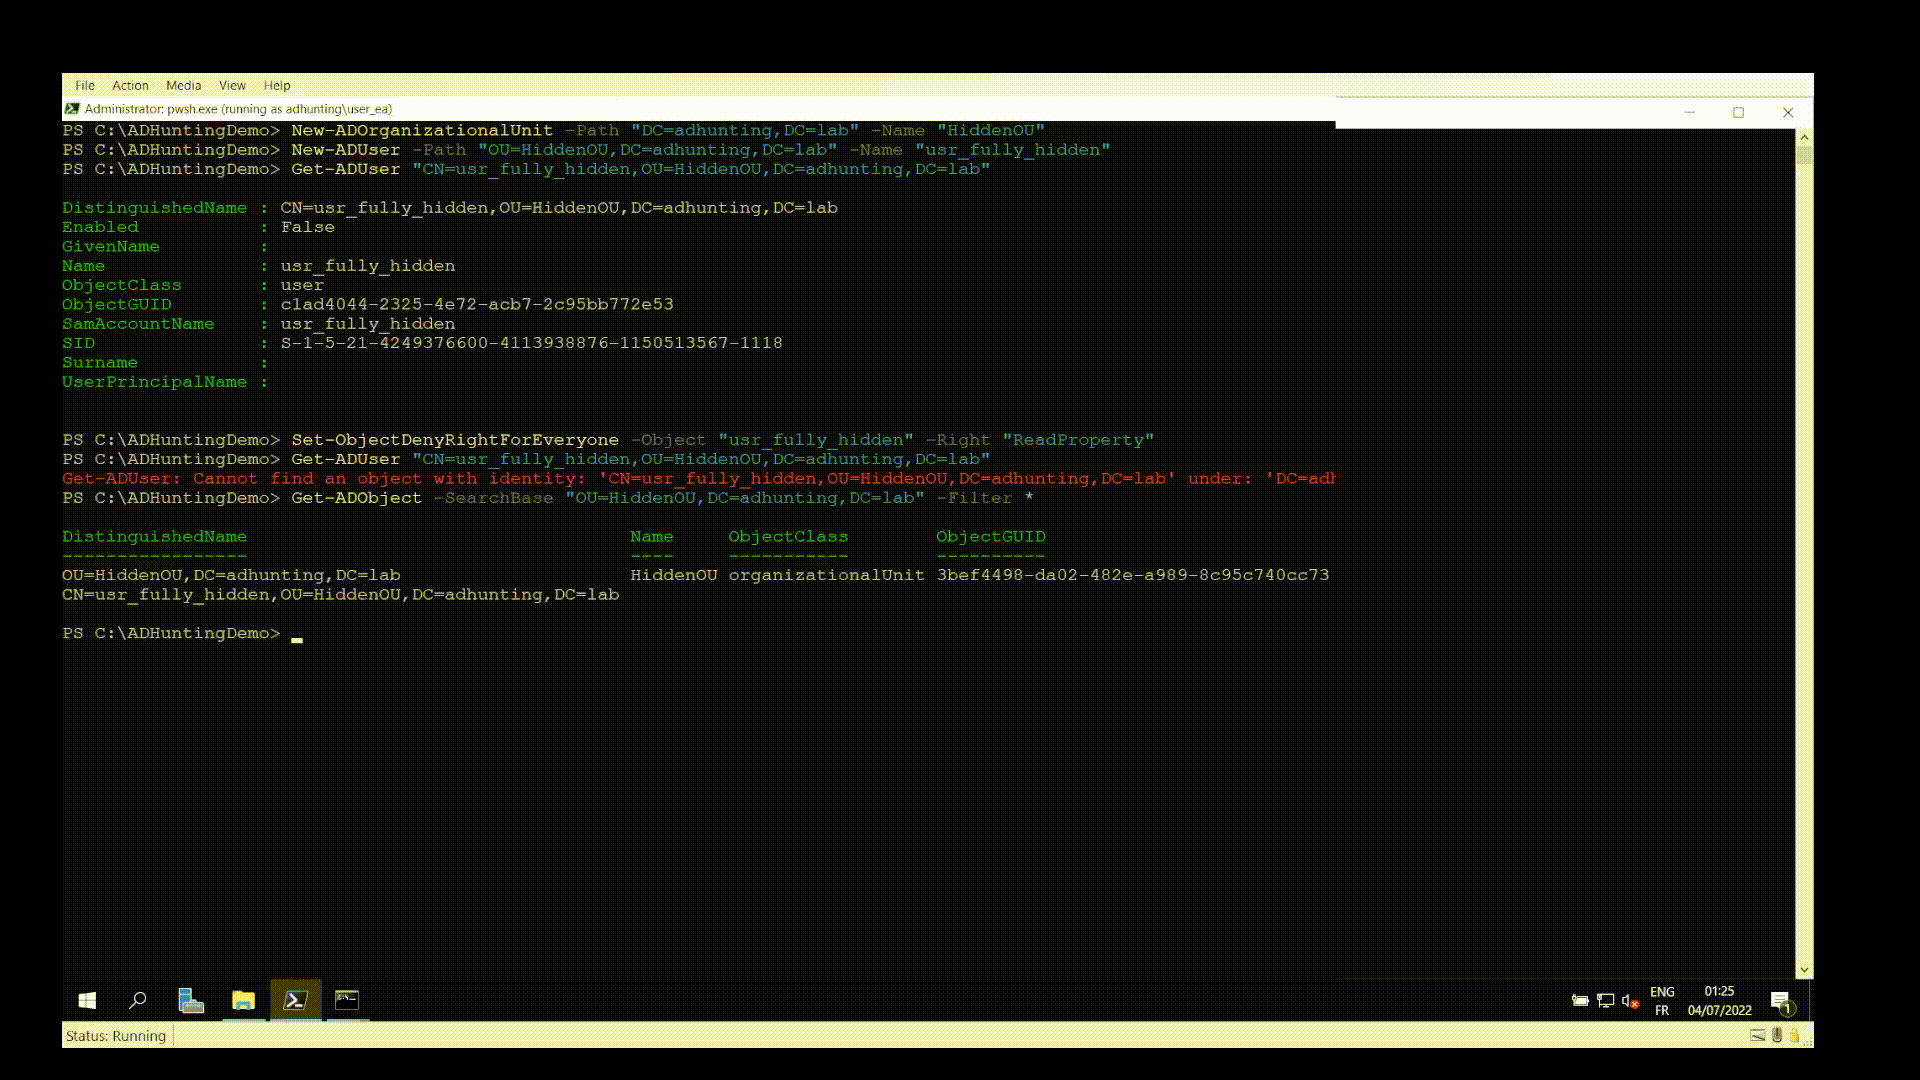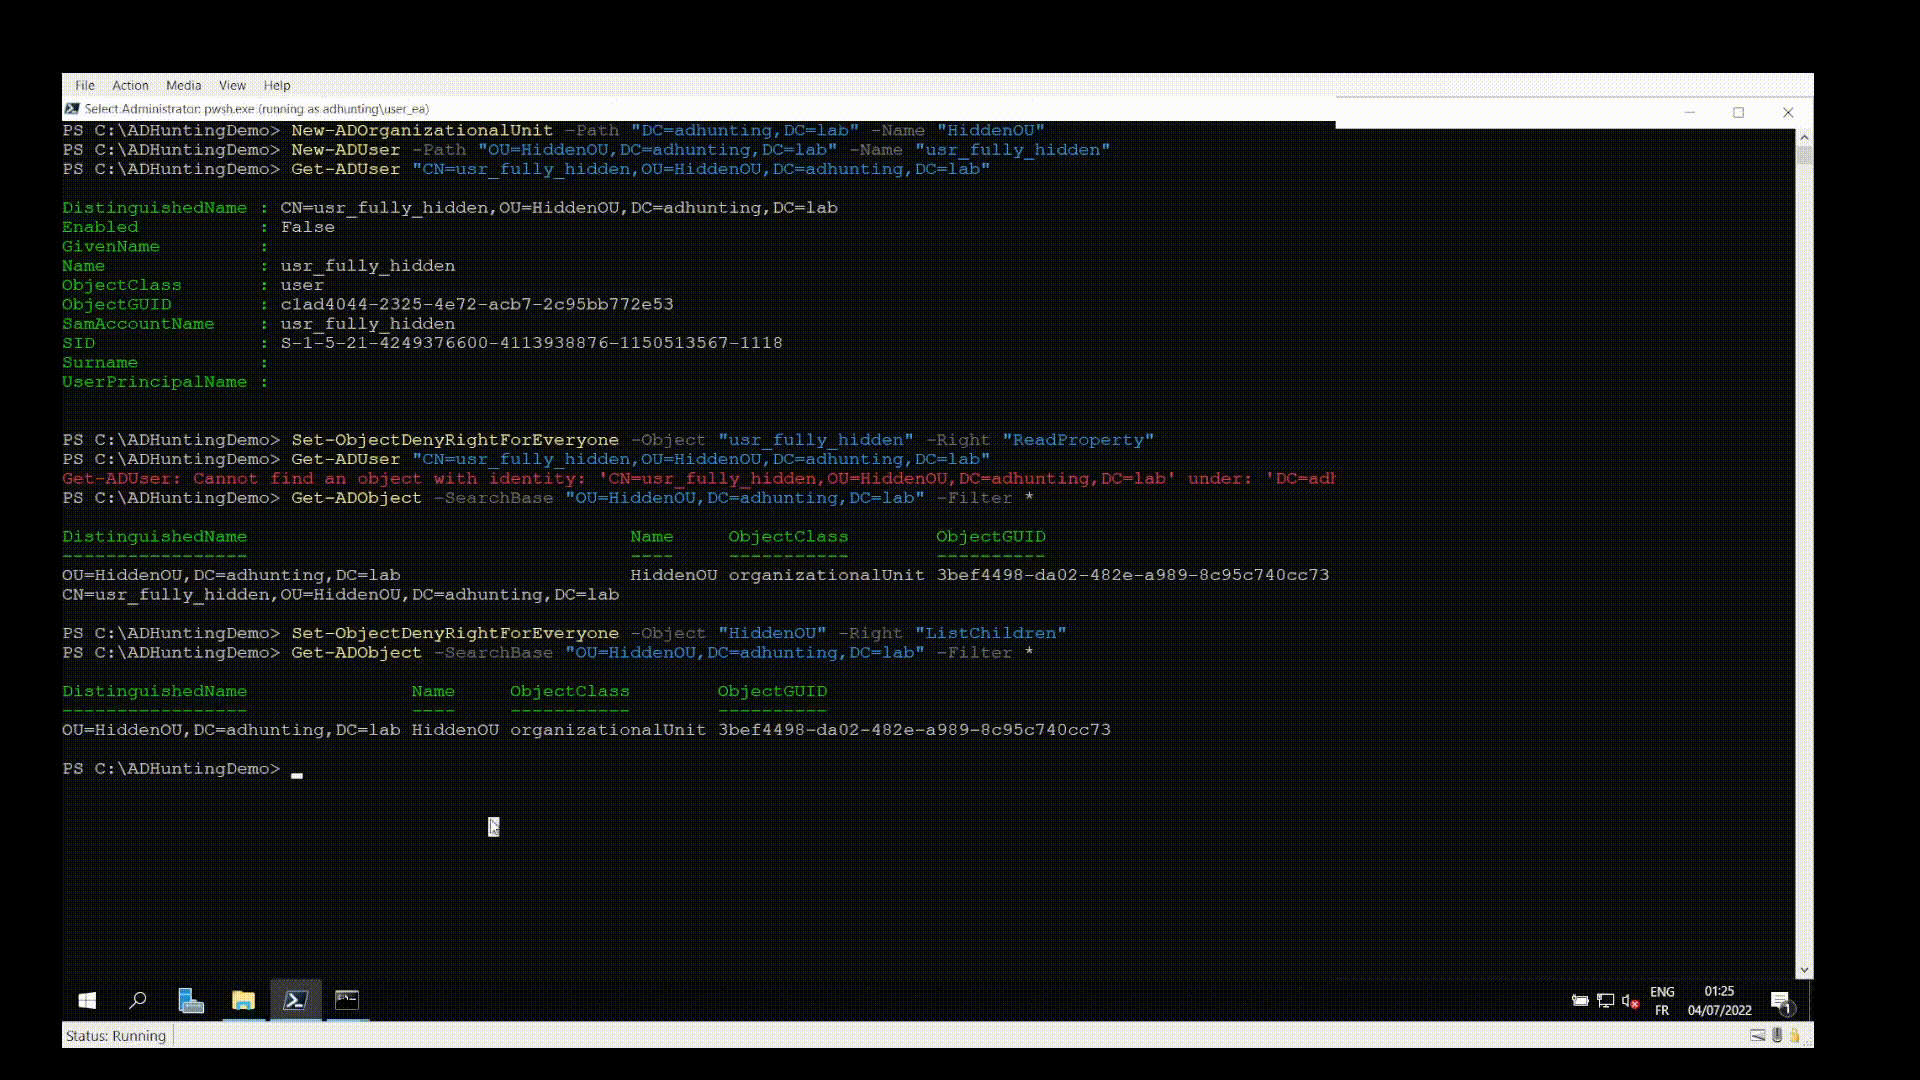
PowerShell script that aim to help uncovering (eventual) persistence mechanisms deployed by a threat actor following an Active Directory domain…

forensicsincident-responseinformation-gathering+5
989 months ago
ThreatIntel-Aggregator preview

ThreatIntel-Aggregator

GitHubethan-andrews/threatintel-aggregator

Self-hosted threat intelligence platform — feed aggregation, AI triage, MITRE ATT&CK coverage, and Sentinel-integrated detection engineering. Runs…

ai-securitydefensive-toolsincident-response+7
601 month ago
shomon preview

shomon

GitHubkaansk/shomon

Shodan Monitoring integration for TheHive.
incident-responseinformation-gatheringosint+1
1304 years ago
latma preview

latma

GitHubsilverfort-open-source/latma

Collects and analyzes AD and Azure AD authentication logs to detect lateral movement attacks using graph-based anomaly detection, visualizing…
anomaly-detectioncloud-securityincident-response+5
803 years ago
gargamel preview

gargamel

GitHublifars/gargamel

A forensic evidence acquirer

digital-forensicsforensicsincident-response+3
865 years ago
gundog preview

gundog

GitHubjangeisbauer/gundog

gundog - guided hunting in Microsoft Defender
incident-responseinformation-gatheringlog-analysis+2
535 years ago
log4shell_ioc_ips preview

log4shell_ioc_ips

GitHubhackinghippo/log4shell_ioc_ips

log4j / log4shell IoCs from multiple sources put together in one big file (IPs) more coming soon (CVE-2021-44228)
incident-responseinformation-gatheringioc-management+3
374 years ago
reportly preview

reportly

GitHubsap8899/reportly

AzureAD/EntraID user activity reporter for blue teams. Input a suspicious user and time frame to receive a detailed report of user info, actions, and…

cloud-securityidentity-access-managementincident-response+2
963 years ago
rootly-graphify-importer preview

rootly-graphify-importer

GitHubrootly-ai-labs/rootly-graphify-importer

Turn Rootly incidents, alerts, and teams into a queryable knowledge graph. Visualize service dependencies, on-call coverage gaps, and cross-incident…

incident-responseinformation-gatheringlog-analysis+1
426 months ago
ThreatLens preview

ThreatLens

GitHubabdaullahag/threatlens

Python CLI tool for rapid IOC analysis (IPs, Domains, CVEs) using 6 free Threat Intel APIs. Outputs: Color-coded Excel, JSON, CSV. Uses: VT, Shodan,…
defensive-toolsincident-responseinformation-gathering+7
266 days ago
thrunt-god preview

thrunt-god

GitHubbackbay-labs/thrunt-god

Threat hunting command system for agentic IDEs
incident-responseinformation-gatheringintrusion-detection+5
363 months ago
SessionView preview

SessionView

GitHublsecqt/sessionview

A portable C# utility for enumerating local and remote windows sessions

digital-forensicsforensicsincident-response+3
5710 months ago
SIPI preview

SIPI

GitHubst2labs/sipi

Simple IP Information Tools for Reputation Data Analysis
incident-responseinformation-gatheringosint+2
237 years ago
Simple-Live-Data-Collection preview

Simple-Live-Data-Collection

GitHubletsdefendio/simple-live-data-collection

Client-server tool for live data collection during incident response. Admin sends requests to clients to gather system information for forensic…
digital-forensicsforensicsincident-response+1
226 years ago
MacOSThreatTrack preview

MacOSThreatTrack

GitHubab2pentest/macosthreattrack

Bash tool used for proactive detection of malicious activity on macOS systems.
digital-forensicsincident-responseinformation-gathering+1
391 year ago
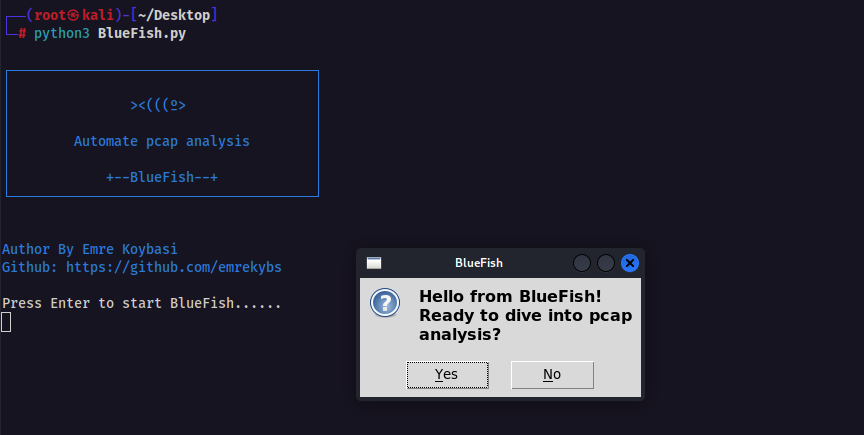
BlueFish preview

BlueFish

GitHubemrekybs/bluefish

Automation tool designed to simplify the analysis of PCAP (Packet Capture) files
forensicsincident-responseinformation-gathering+2
197 months ago
ImpossibleTravelLogAnalysis preview

ImpossibleTravelLogAnalysis

GitHubnccgroup/impossibletravelloganalysis

Basic log analysis tool to detect impossible travel via IP address geographic information

anomaly-detectionforensicsincident-response+3
207 years ago
Previous12345Next