CVE-2021-1675_CarbonBlack_HuntingQuery

CarbonBlack hunting queries to detect PrintNightmare (CVE-2021-1675) exploitation via file, module load, and process events, based on Sigma rules.

CarbonBlack hunting queries to detect PrintNightmare (CVE-2021-1675) exploitation via file, module load, and process events, based on Sigma rules.

Detailed incident response walkthrough analyzing CVE-2024-49138 exploitation on Windows, covering process tree analysis, IOC identification, and…

Shell script that monitors for a vulnerable sudo process and triggers authentication lockout to mitigate CVE-2021-3156.

Deploys an agent to fix CVE-2021-44228 (Log4j RCE vulnerability) in a running JVM process

A PowerShell module for acquisition of data from Microsoft 365 and Azure for Incident Response and Cyber Security purposes.

An agent to hotpatch the log4j RCE from CVE-2021-44228.

Enumerate various traits from Windows processes as an aid to threat hunting

the ps utility, with an eBPF twist and container context

Open-source secret scanner in Rust

Triages a suspect Windows machine in minutes. Collects processes, services, autoruns, event logs and forensic artifacts, flags attacker activity, and…

A canary designed to minimize the impact from certain Ransomware actors


Extensible MacOS system telemetry generator.

Aggregates MITRE ATT&CK, Sigma, and Atomic Red Team data into BloodHound graphs so SOC analysts can map detection coverage, identify gaps, and…

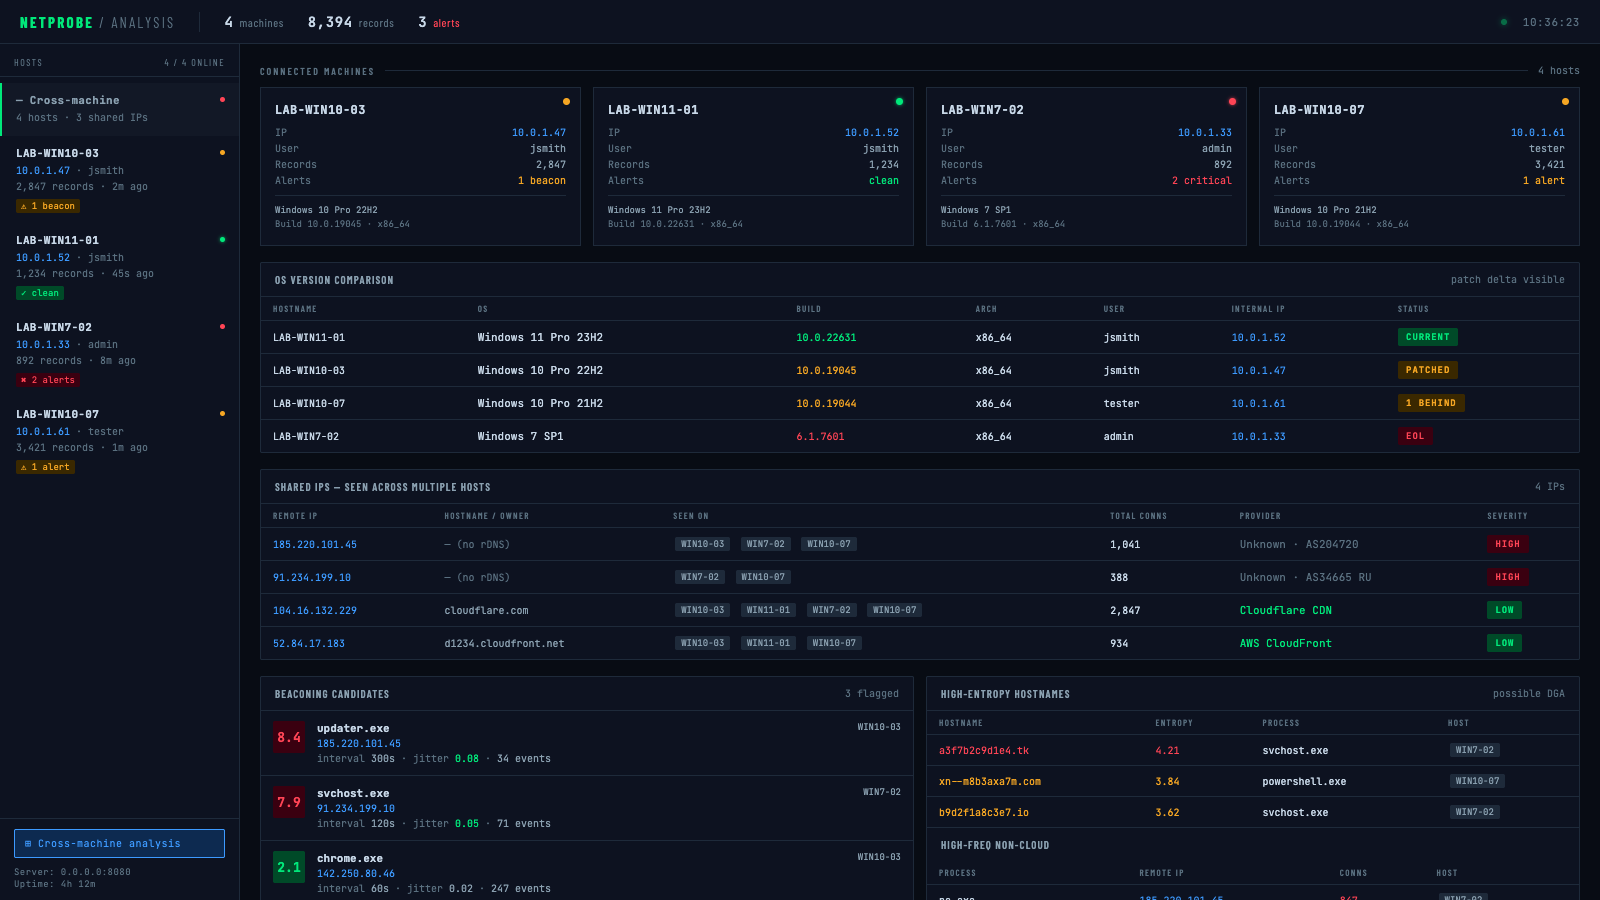
Network monitoring tool that maps process-to-network connections, identifies cloud providers, and detects beaconing activity

Easy-to-use live forensics toolbox for Linux endpoints

By Kprobe technology Open Source Host-based Intrusion Detection System(HIDS), from E_Bwill.

Kernel-Mode Rootkit Hunter