

NginxHunter
 emrekybs/nginxhunter
Analyzes Nginx access logs to detect SQL injection, scanner tools, webshells, and exploitation attempts, aiding system administrators in server…
defensive-toolsincident-responselog-analysis+2
5
emrekybs/nginxhunterAnalyzes Nginx access logs to detect SQL injection, scanner tools, webshells, and exploitation attempts, aiding system administrators in server…
 vorkampfer/copyfail2_electric_boogaloo_fix
A temporary mitigation against copy_fail variant (copyfail2_electric_boogaloo) - Unprivileged Linux LPE via xfrm ESP-in-UDP MSG_SPLICE_PAGES no-COW…
 municipalparkingservices/cve-2021-44228-scanner
Single-binary scanner for CVE-2021-44228 (Log4Shell) that detects vulnerable log4j versions in JAR/WAR/EAR files and applies mitigation patches by…
 liverwortenuresis371/copyfail-rs
Exploit and detect CVE-2026-31431 vulnerabilities using a static binary that monitors system integrity and bypasses PAM authentication.
 corretto/hotpatch-for-apache-log4j2
An agent to hotpatch the log4j RCE from CVE-2021-44228.
 mrbuglf/xz-utils_cve-2024-3094
XZ-Utils工具库恶意后门植入漏洞(CVE-2024-3094)
 tclahr/uac
Portable, dependency-free incident response tool that automates forensic artifact collection from Unix-like systems, including memory acquisition,…
 mrhackercharlie/netspecter
Real-time system monitoring tool for detecting process activity and network exposure!
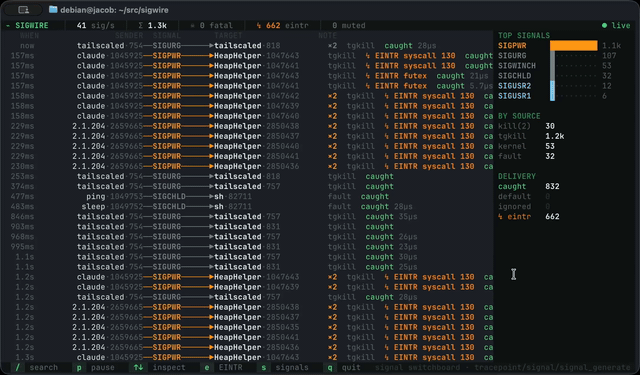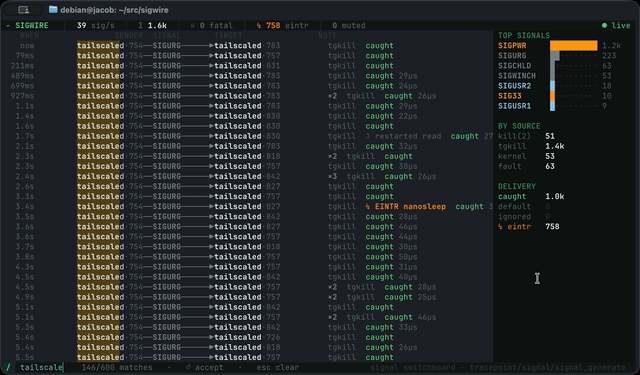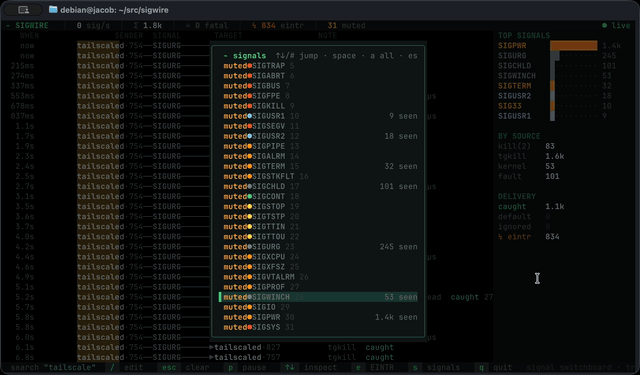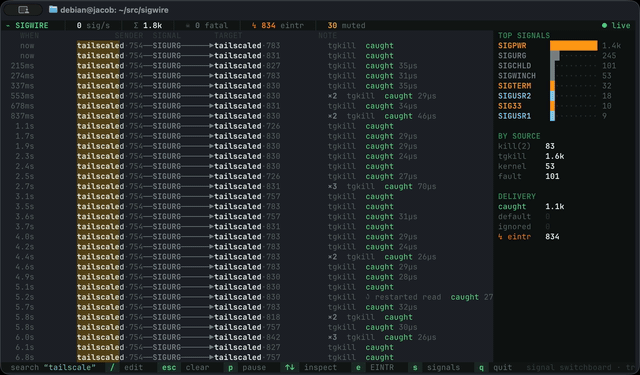 yeet-src/sigwire
Live kernel signal observability tool using eBPF tracepoints to stream every signal raised on a Linux host, showing sender, target, disposition,…
 akefallonitis/larac2shell
Cross-platform interactive shell for Microsoft Defender for Endpoint Live Response
 sonitbahl/sshintel
Self-contained SSH honeypot for capturing attacker interactions and turning them into structured security intelligence.
 wagga40/logstotal
Self-hosted multi-engine Sigma detection for event logs
 olafhartong/sysmon-modular
A repository of sysmon configuration modules
 diogo-fernan/ir-rescue
A Windows Batch script and a Unix Bash script to comprehensively collect host forensic data during incident response.
 webhosting4u/copy-fail_detect_and_mitigate_cve-2026-31431
Detects exposure to CVE-2026-31431 (Copy Fail) and optionally mitigates by disabling the vulnerable algif_aead kernel module, providing verdicts and…
 thinkst/opencanary
Low-resource honeypot that emulates common network services to detect post-breach attacker activity, with extensible protocol modules and…
 thinkst/canarytokens-docker
Docker configuration to quickly setup your own Canarytokens.
 ohmyadd/wetland
A high interaction SSH honeypot