

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
84 results
ADRecon preview

ADRecon

GitHubadrecon/adrecon

PowerShell tool that extracts Active Directory artifacts via LDAP or ADWS and generates Excel reports for auditing, DFIR, and penetration testing.
defensive-toolsdigital-forensicsincident-response+6
990
2 years ago
sshesame preview

sshesame

GitHubjaksi/sshesame

An easy to set up and use SSH honeypot, a fake SSH server that lets anyone in and logs their activity
defensive-toolsincident-responseinformation-gathering+4
1.8k2 years ago
Aurora-Incident-Response preview

Aurora-Incident-Response

GitHubcyb3rfox/aurora-incident-response

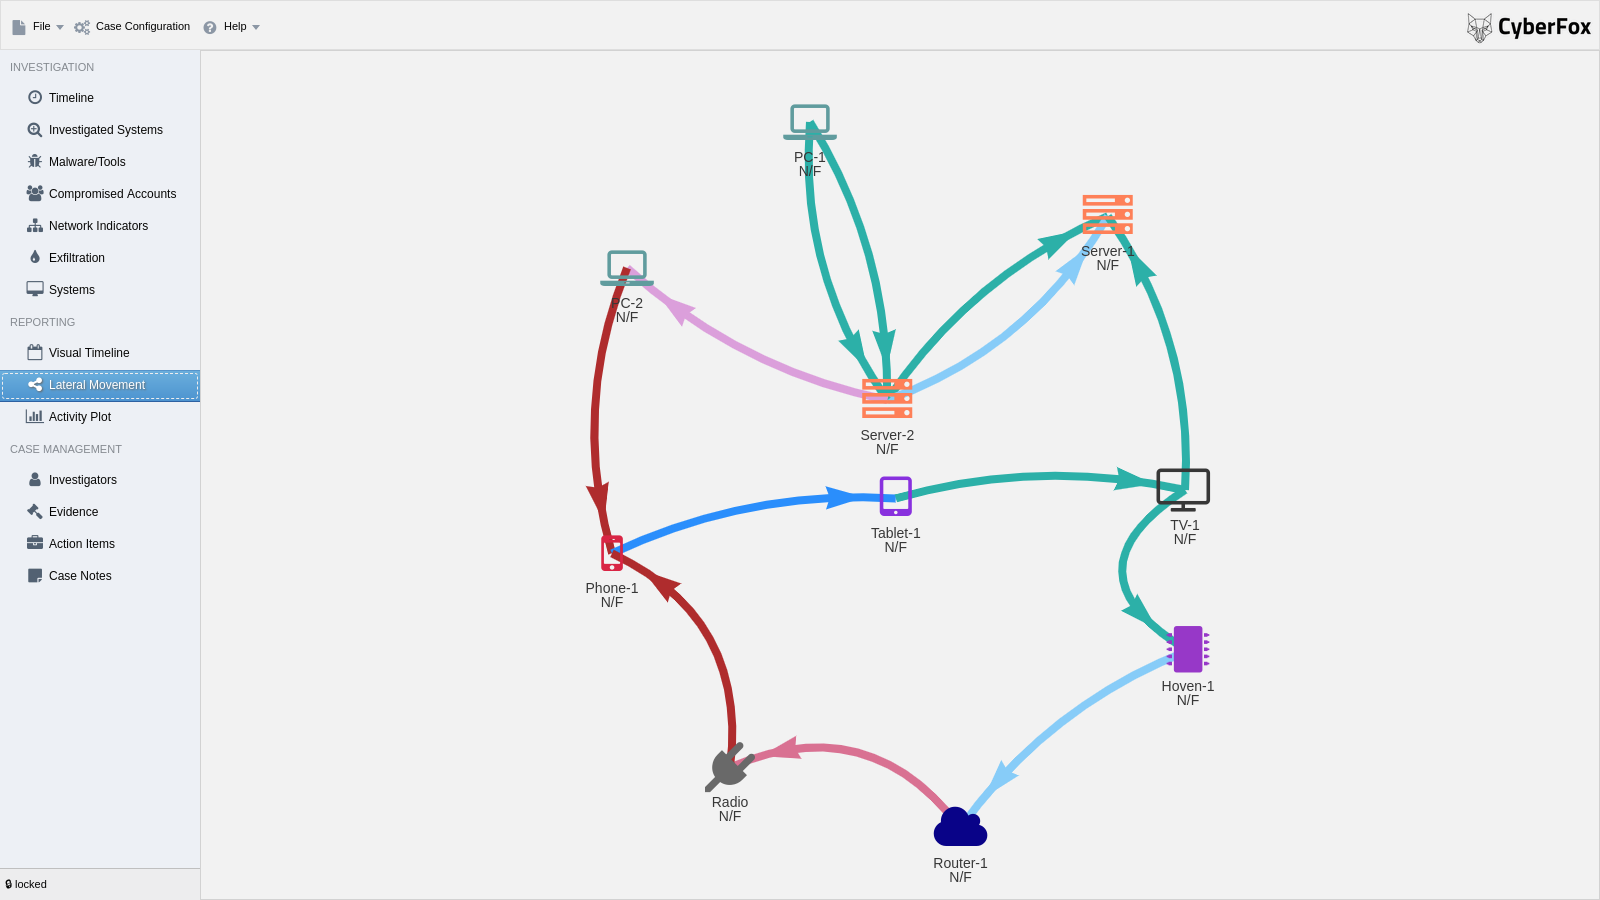
Incident Response Documentation made easy. Developed by Incident Responders for Incident Responders
digital-forensicsforensicsincident-response+3
1.1k4 years ago
Microsoft-Extractor-Suite preview

Microsoft-Extractor-Suite

GitHubinvictus-ir/microsoft-extractor-suite

A PowerShell module for acquisition of data from Microsoft 365 and Azure for Incident Response and Cyber Security purposes.
cloud-securitydigital-forensicsincident-response+3
8374 months ago
Meerkat preview

Meerkat

GitHubtonyphipps/meerkat

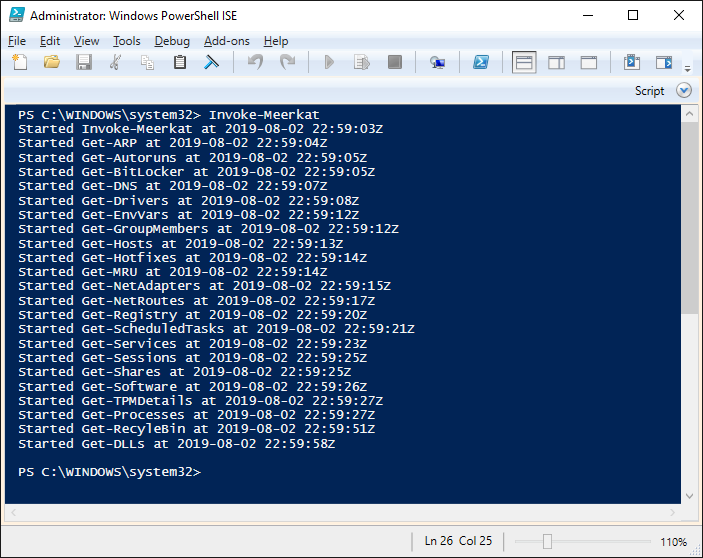
A collection of PowerShell modules designed for artifact gathering and reconnaisance of Windows-based endpoints.
digital-forensicsforensicsincident-response+2
4831 year ago
Threat-Remediation-Scripts preview

Threat-Remediation-Scripts

GitHubxephora/threat-remediation-scripts

This repository contains a list of new remediation scripts.
defensive-toolsdigital-forensicsincident-response+5
19014 days ago
AzureHunter preview

AzureHunter

GitHubdarkquasar/azurehunter

A Cloud Forensics Powershell module to run threat hunting playbooks on data from Azure and O365

cloud-securitydigital-forensicsincident-response+3
7954 years ago
Remote-Desktop-Caching- preview

Remote-Desktop-Caching-

GitHubviralmaniar/remote-desktop-caching-

This tool allows one to recover old RDP (mstsc) session information in the form of broken PNG files. These PNG files allows Red Team member to…
digital-forensicsforensicsincident-response+4
2188 years ago
Hale preview

Hale

GitHubpjlantz/hale

Botnet command & control monitor

command-and-controlincident-responseinformation-gathering+5
2024 years ago
SOC-Multitool preview

SOC-Multitool

GitHubzdhenard42/soc-multitool

A powerful and user-friendly browser extension that streamlines investigations for security professionals.
incident-responseinformation-gatheringosint+1
4201 year ago
rastrea2r preview

rastrea2r

GitHubrastrea2r/rastrea2r

Collecting & Hunting for IOCs with gusto and style
digital-forensicsforensicsincident-response+6
23822 days ago
pockint preview

pockint

GitHubedoardogerosa/pockint

A portable OSINT Swiss Army Knife for DFIR/OSINT professionals 🕵️ 🕵️ 🕵️
digital-forensicsdns-analysisincident-response+5
2853 years ago
Credential-Hunting preview

Credential-Hunting

GitHubnecr00/credential-hunting

CredsHunter - Credential Hunting scripts for Windows and Linux OS

forensicsincident-responseinformation-gathering+7
1692 months ago
CVE-2019-19781 preview

CVE-2019-19781

GitHubmpgn/cve-2019-19781

CVE-2019-19781 - Remote Code Execution on Citrix ADC Netscaler exploit

exploitationincident-responseinformation-gathering+4
1576 years ago
cve-intel preview

cve-intel

GitHubfazmin/cve-intel

Local security intelligence for CVE triage - 40 data sources and 41 tools, risk scores and an MCP server for AI agents, all in native Rust. Private…
ai-securitydevsecopsincident-response+8
13214h 5m ago
Fennec preview

Fennec

GitHubabdulrhmanalfaifi/fennec

Artifact collection tool for *nix systems
digital-forensicsforensicsincident-response+3
2202 years ago
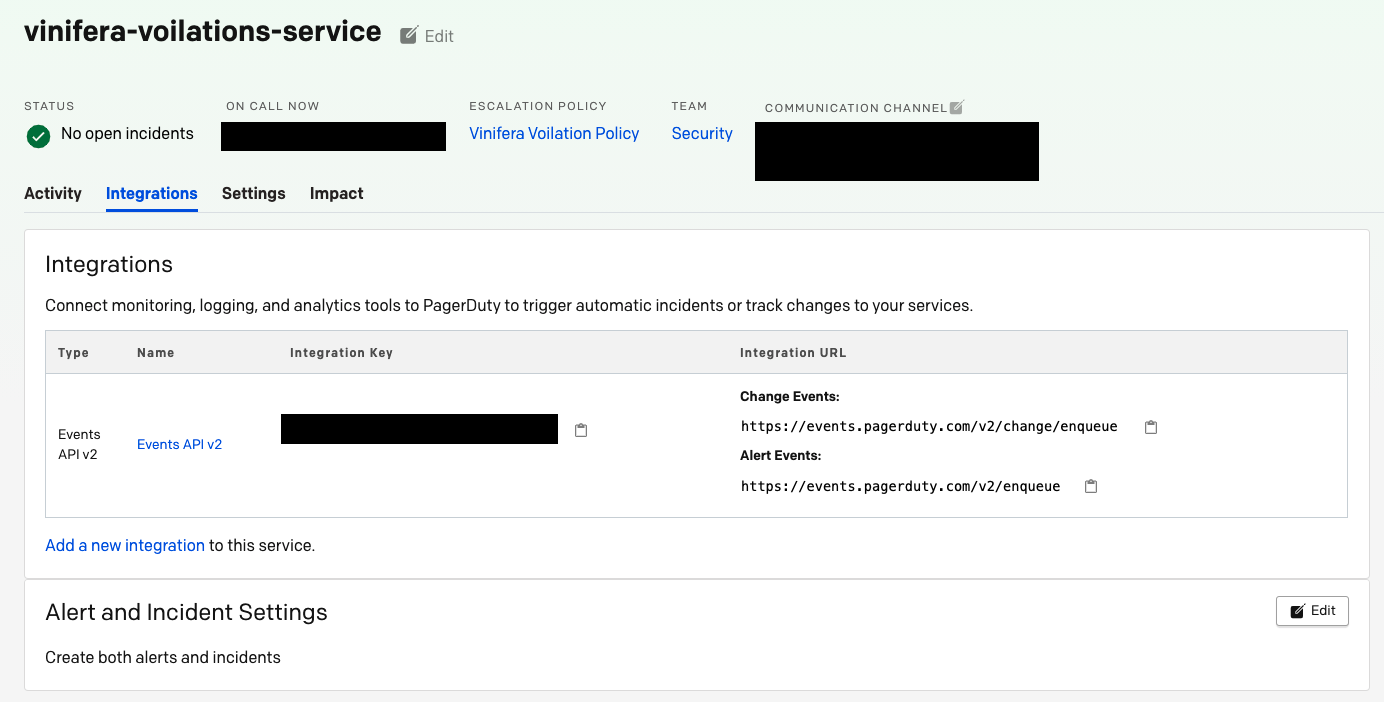
vinifera preview

vinifera

GitHubzomato/vinifera

A GitHub recon/monitoring tool for finding internal leaks belonging to your organisation.
incident-responseinformation-gatheringosint+2
942 years ago
Douglas-042 preview

Douglas-042

GitHubemrekybs/douglas-042

Triages a suspect Windows machine in minutes. Collects processes, services, autoruns, event logs and forensic artifacts, flags attacker activity, and…

forensicsincident-responseinformation-gathering+1
442 months ago
Previous12345Next