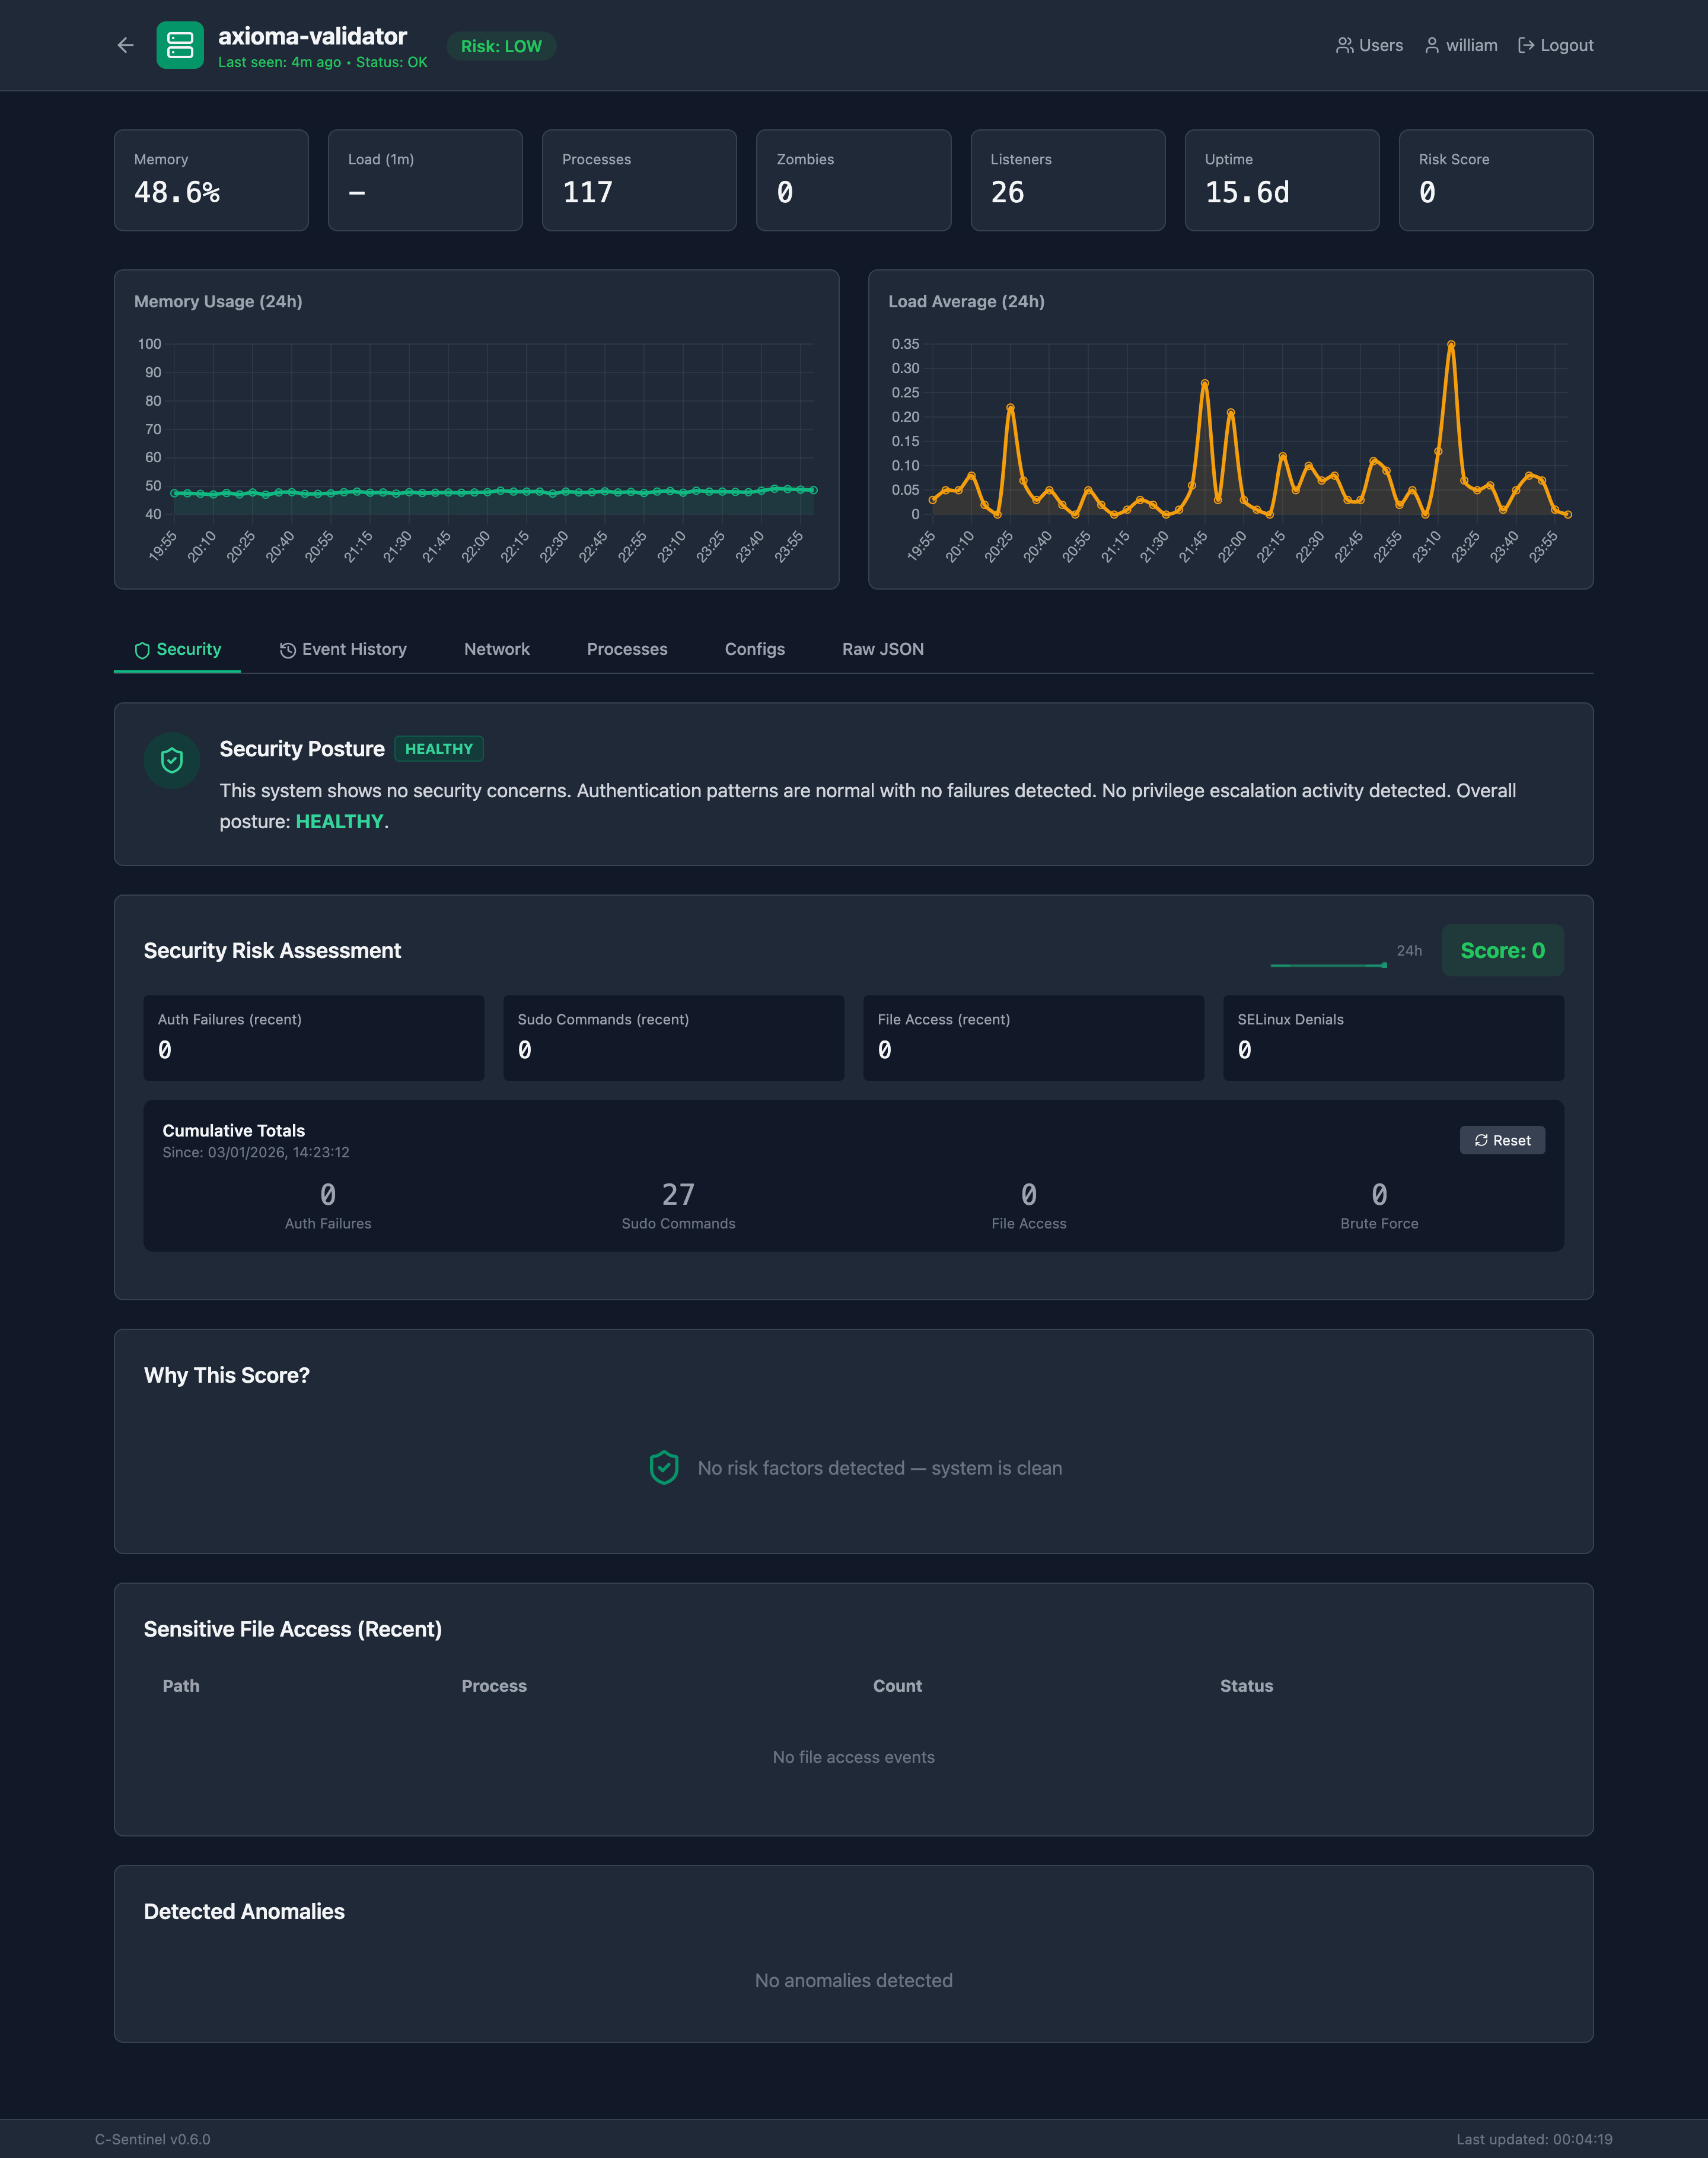
c-sentinel
 speytech/c-sentinel
Semantic Observability for UNIX Systems - A lightweight C-based system prober with AI-powered analysis
ai-securityanomaly-detectionauthentication+8
727 months ago
speytech/c-sentinelSemantic Observability for UNIX Systems - A lightweight C-based system prober with AI-powered analysis
 dereeqw/berrysentinel
Berry Sentinel v5.0 — Advanced behavioral C2 and reverse shell detector for Linux/Windows/Unix systems. Features real-time connection analysis,…
 thrandomv/cve-2026-31431-detection
Defensive detection package for CVE-2026-31431 (Linux kernel AF_ALG LPE). Sigma, Falco, auditd, KQL, and EQL rules mapped to MITRE ATT&CK…
 security-onion-solutions/security-onion
Security Onion 16.04 - Linux distro for threat hunting, enterprise security monitoring, and log management

 trustedsec/artillery
Open-source blue team tool that protects Linux and Windows systems using multiple host and network defense and detection methods.
 opensourcemalware/polinrider
Technical dossier on the DPRK-linked PolinRider supply-chain attack, documenting obfuscated JS payload injection, git history manipulation, C2…
 kadir/copy-fail-cve-2026-31431-ioc
Detection, mitigation, and IOC toolkit for Copy Fail CVE-2026-31431 Linux kernel page-cache privilege escalation
 botherder/kraken
Cross-platform Yara scanner written in Go
 mr-r3b00t/cve-2021-44228
PowerShell-based backdoor detection tool for VMware Horizon connection servers, targeting CVE-2021-44228. Includes canary with optional submission…
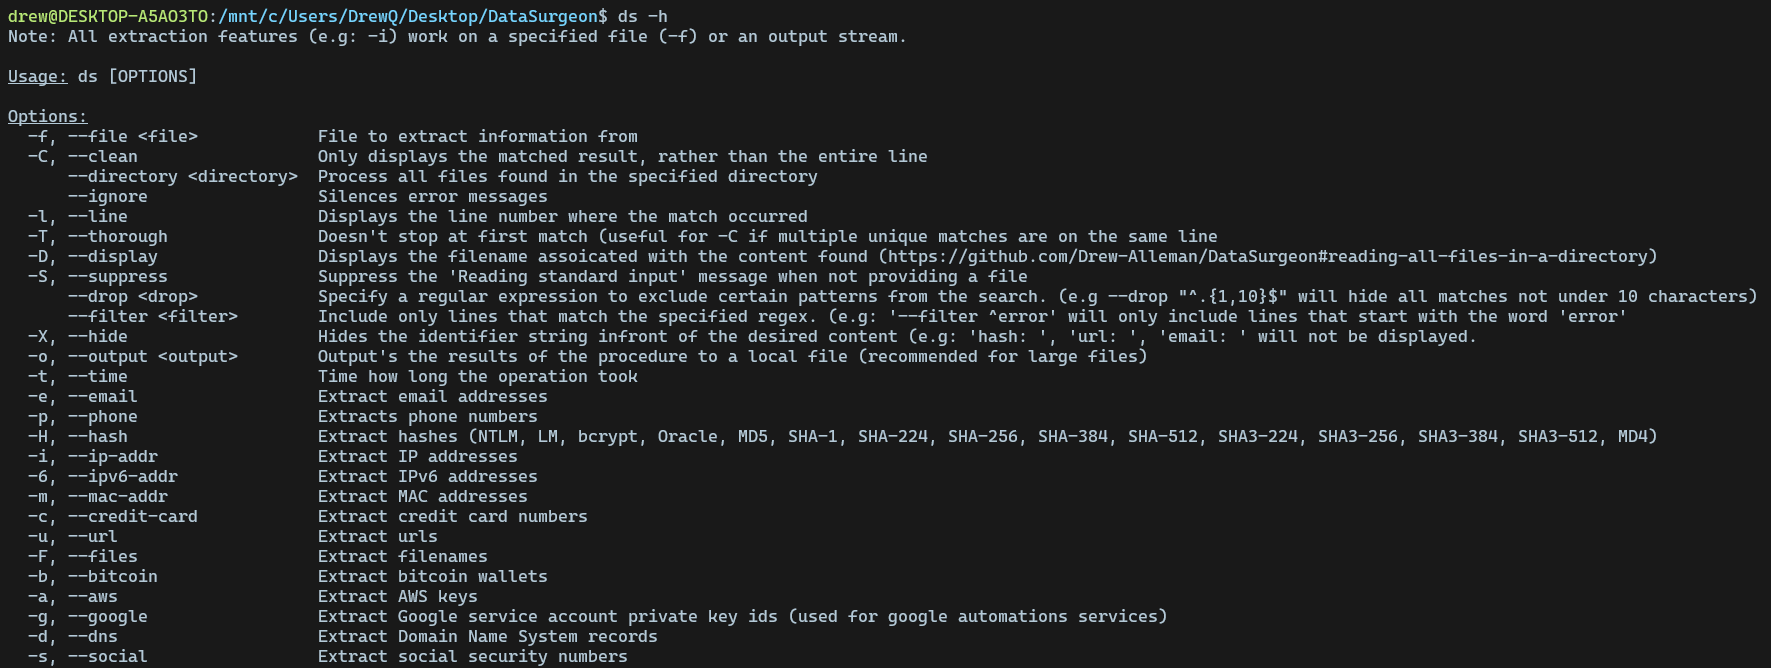 drew-alleman/datasurgeon
Quickly Extracts IP's, Email Addresses, Hashes, Files, Credit Cards, Social Security Numbers and a lot More From Text
 formerlab/shadow-fleet-tracker-light
Open source Baltic Sea shadow fleet tracker. 1200+ vessels, live AIS, cable proximity alerts. No cloud, no subscription, runs locally
 blacksnufkin/deadmanswitch
DeadManSwitch in rust with several triggers (remote local and network)

 wmal/linux-kodachi
Hardened Debian-based privacy OS with pre-integrated anonymity stack (Tor, VPN, DNSCrypt), anti-forensic tooling, SOC security center, and standalone…
 priyanshu-rawa/cybersecurity-handbook
Open-source cybersecurity knowledge base with 400+ notes, labs, and cheat sheets covering offense, defense, cryptography, cloud, and forensics.
 habibkaratas/sorry-ransomware-analysis
Sorry ransomware (.sorry) IOCs, YARA rules and forensic analysis - CVE-2026-41940 cPanel campaign